

redknife
 yukibtc/redknife
A Swiss Army knife for offensive security.
command-and-controlinformation-gatheringpenetration-testing+4
yukibtc/redknifeA Swiss Army knife for offensive security.
 ghostmanager/ghostwriter
The SpecterOps project management and reporting engine
 kr0no/bloodhound-shell
An interactive command-line shell for BloodHound API.
 absllk/hexestra
AI-native penetration testing IDE where operators and an AI agent share browser, terminals, traffic capture, shells, asset graph, tasks, and evidence…
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 nccgroup/steppingstones
Web-based red team activity logging, reporting, and situational awareness tool with Cobalt Strike and BloodHound integration.
 principlebreach/waybend
Self-hosted SSRF redirect, payload, callback, and DNS workbench
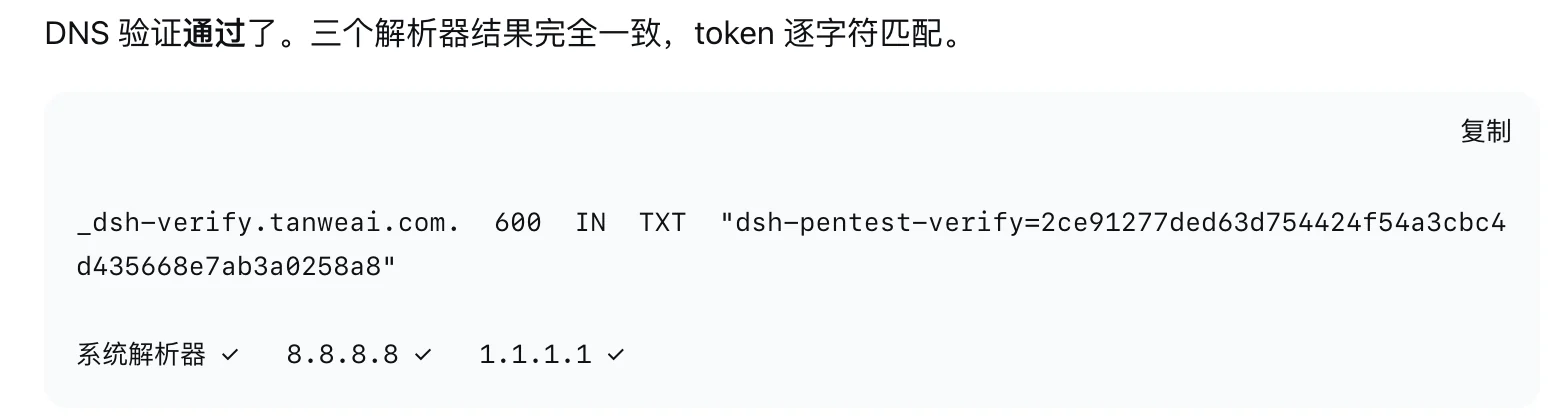 xsser/dig
macOS dig wrapper that appends spoofed local TXT records to DNS query output, designed to deceive LLM agents into performing automated penetration…
 blue0x1/nimrm
Native Nim WinRM shell with NTLM, Kerberos, file transfer, in-memory helpers, and AD/OPSEC reporting
 ghostlyrootb2h/cve-2026-82222
Exploit framework for CVE-2026-82222, an unauthenticated RCE in GiveWP WordPress plugin. Supports mass scanning, auto-detection, multi-threading,…
 maxprog-svg/cve-2026-33017
CVE-2025-62593 — Ray Unauthenticated RCE Exploit is an unauthenticated remote code execution vulnerability in the Ray distributed AI compute engine.
 atomiczsec/adrenaline
C2-agnostic BOF collection, categorized by attack chain phase. Designed to be small and modular, allowing for quick execution and automation.
 g0d150ne/xss2shell
Exploits WordPress pre-auth XSS (CVE-2026-64638) to achieve remote code execution, installing an AES-encrypted backdoor webshell with persistence,…
 netomize/http-basma
In the realm of cybersecurity, accurately identifying and characterizing web servers is crucial for threat detection, vulnerability assessment, and…
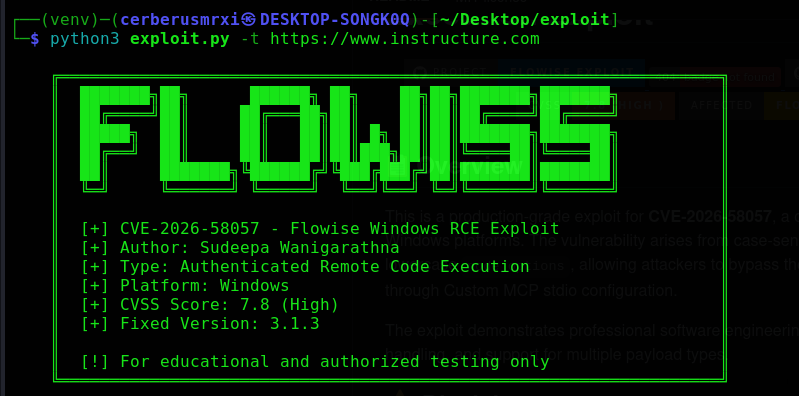 cerberusmrxi/flowise-cve-2026-58057-exploit
Flowise Windows RCE exploit for CVE-2026-58057. Bypasses environment variable validation via case-sensitive flaw. Uses node_options to inject…
 cerberusmrxi/wp-bricks-exploit-cve-2024-25600
CVE-2024-25600 - Unauthenticated RCE exploit for WordPress Bricks Builder Theme. Advanced exploitation framework with interactive shell, reverse…
 exdev994/cve-2026-4631-cockpit-rce
Unauthenticated Remote Code Execution via SSH Command-Line Argument Injection Cockpit versions 327 – 359 | CVSS 9.8 Critical | CWE-78
 shinthink/solrradar
☄️ Mass reconnaissance & exploitation framework for Apache Solr CVE-2026-44825 — Velocity template injection to RCE