wraith
 arcanum-sec/wraith
Browser-hooking framework for authorized red teams and educators. Hooks browsers via XSS, provides interactive post-exploitation control, blind-XSS…
command-and-controleducationexploitation+6
146
arcanum-sec/wraithBrowser-hooking framework for authorized red teams and educators. Hooks browsers via XSS, provides interactive post-exploitation control, blind-XSS…
 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
 activecm/rita
Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.
 s4dp4nd4/frida-c2-mcp
Agentic C2-style MCP server for Frida instrumentation on rooted Android and jailbroken iOS.
 blackcat4347/cve-2025-32433-available-for-windows
CVE-2025-32433-available-for-windows-victims
 jonstratton/selenium-node-takeover-kit
A collection of selenium tests that might aid it takeover of a selenium node
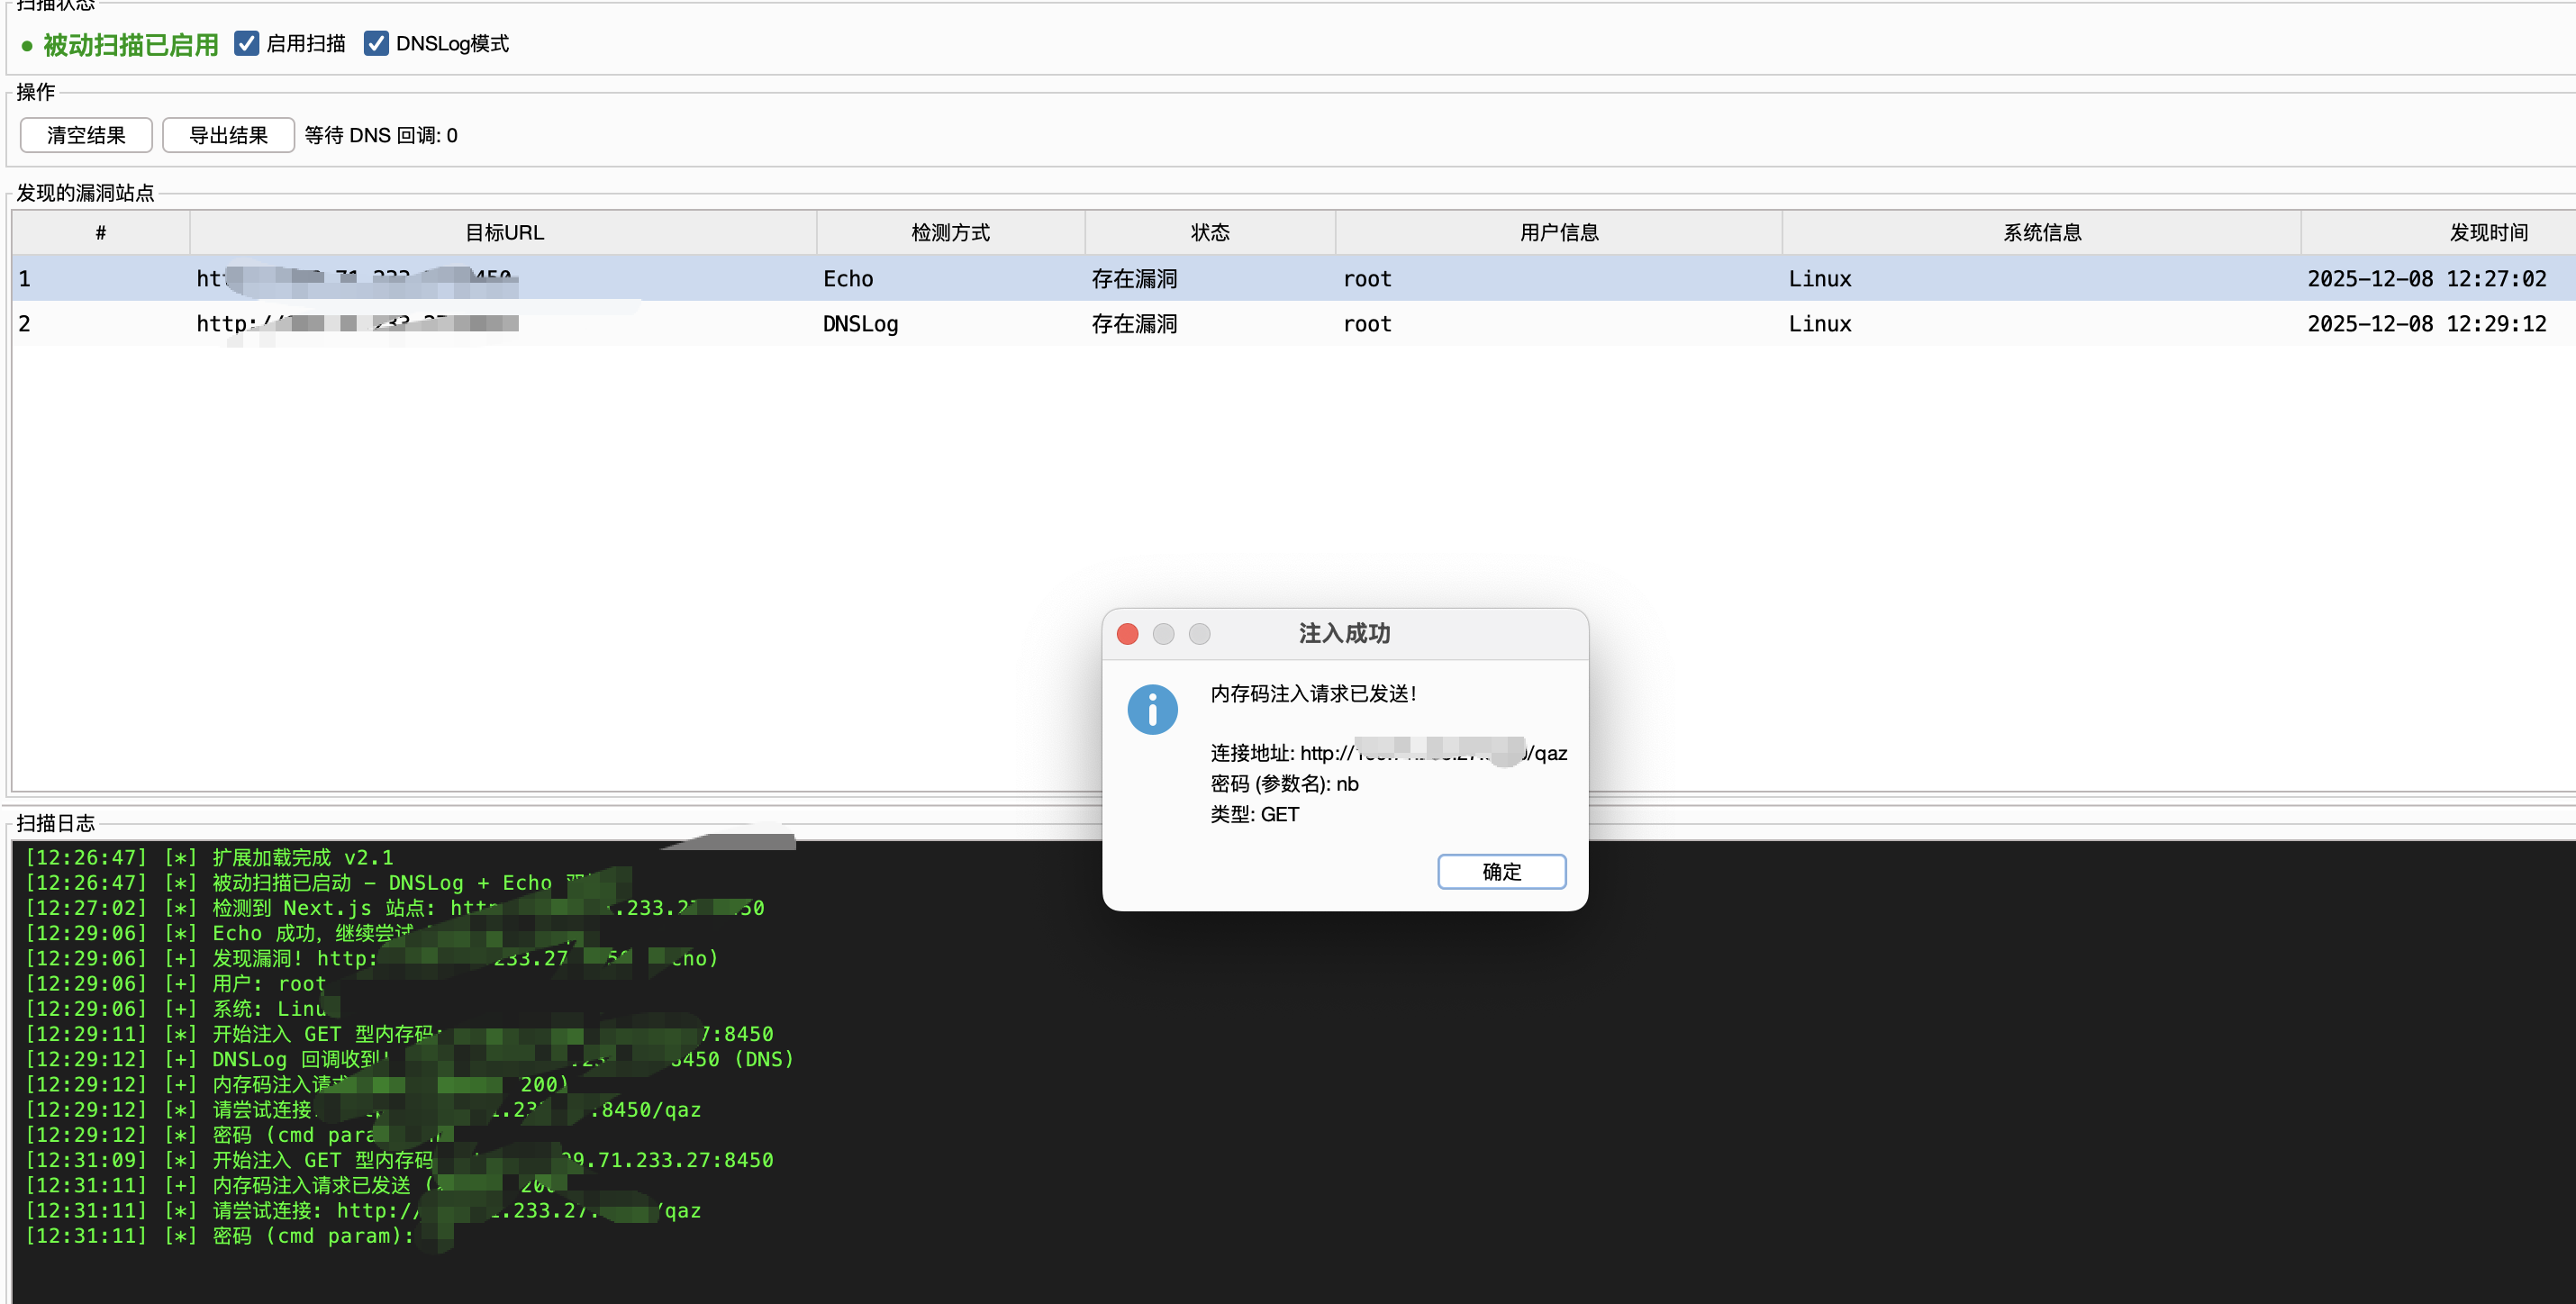 cr4at0r/next.js-rce-scanner-burpsuite-extension-
使用burp自动检测CVE-2025-55182 Next.js RCE 漏洞
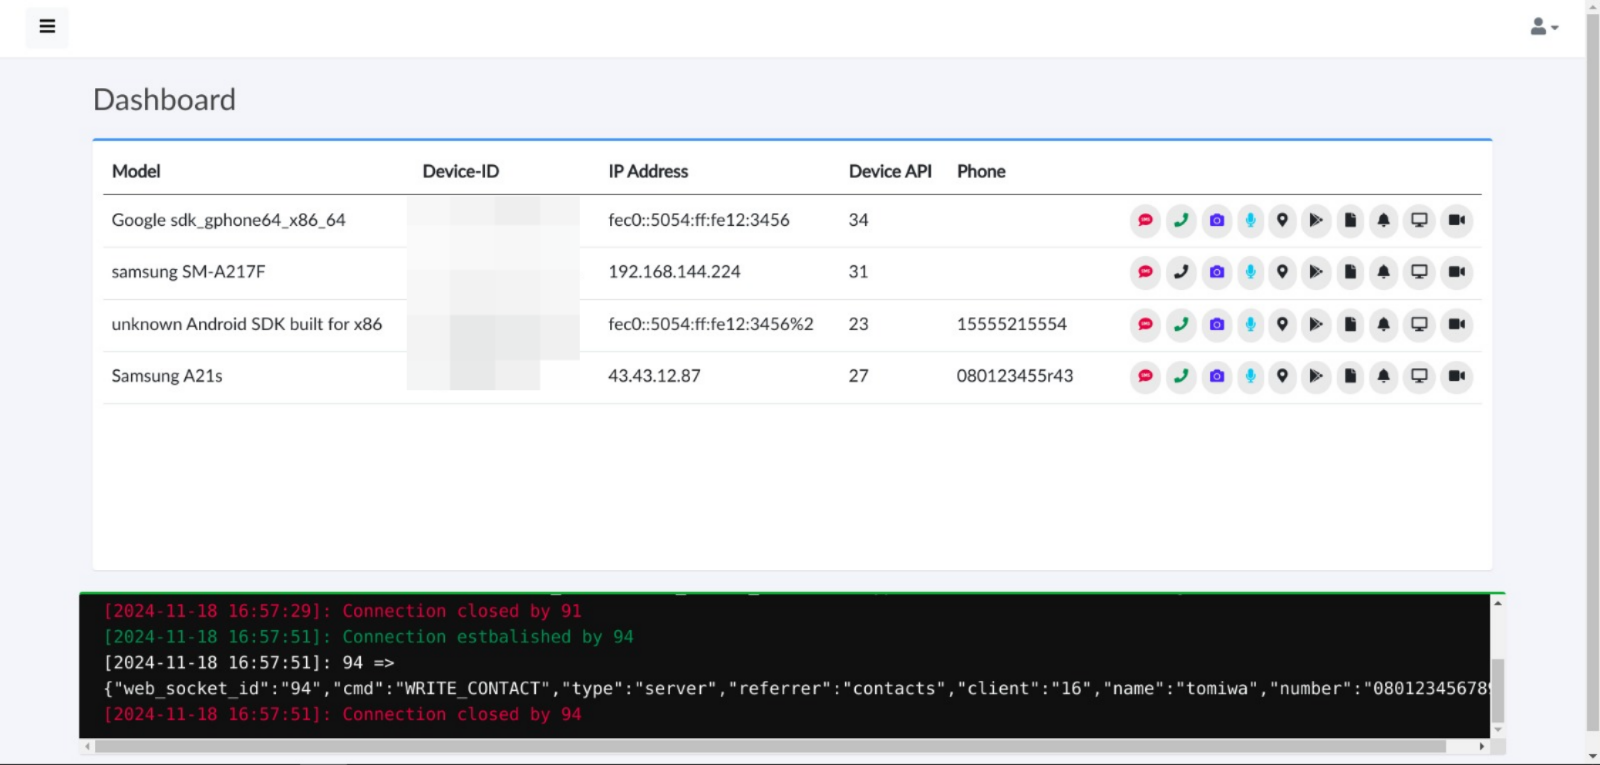 tomiwa-ot/moukthar
Android remote administration tool
 thestingr/cve-2025-25257
Public PoC for CVE-2025-25257: FortiWeb pre-auth SQLi to RCE
 ch4os1/cve-2024-4157-ssrf-rce-reverse-shell
Chaining Havoc C2 SSRF with RCE to get reverse shell on Havoc C2 Server.
 udyz/cve-2025-53770-exploit
Exploit for CVE-2025-53770, a SharePoint ViewState deserialization vulnerability, enabling remote code execution via crafted payloads.
 explxx/cve-2023-33538
Python Exploit for TP-Link TL-WR940N/TL-WR841N Command Injection Vulnerability
 tonyarris/cve-2025-24813-poc
A PoC for CVE-2025-24813
 tinashelorenzi/cve-2023-30258-magnus-billing-v7-exploit
Automated Python exploit for CVE-2023-30258, a command injection in Magnus Billing System v7. Sends crafted GET request to icepay.php to execute…
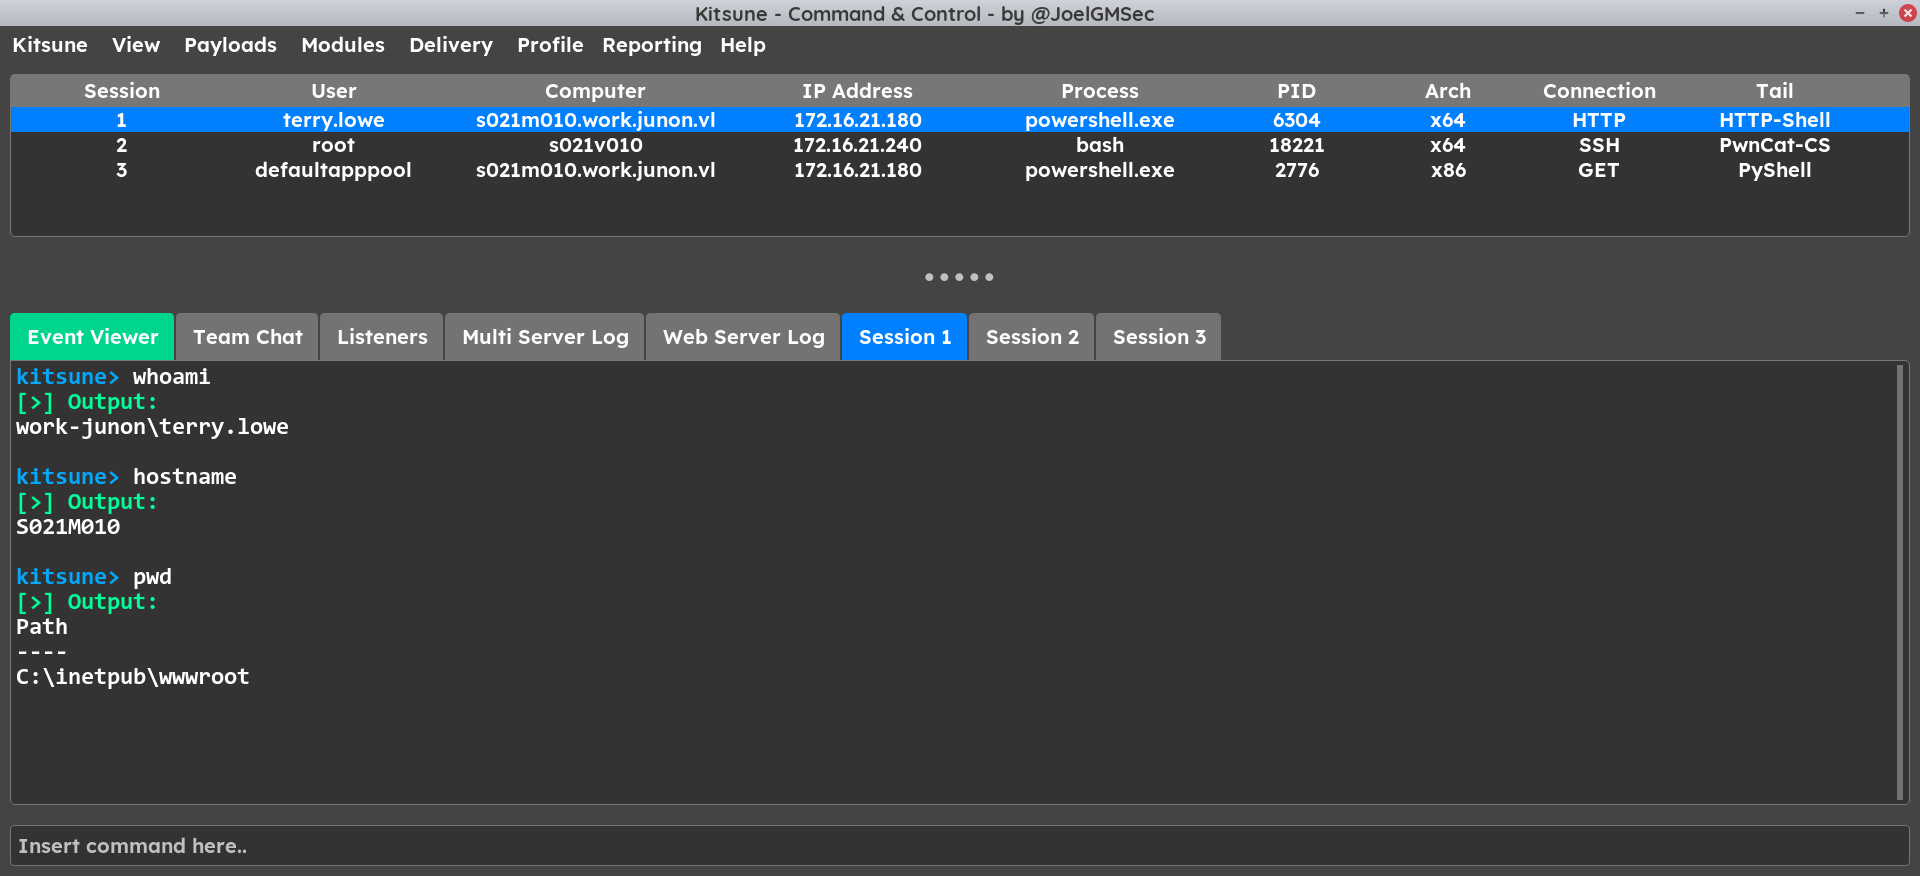 joelgmsec/kitsune
Polymorphic C2 framework with graphical interface, automatic reconnection, payload generation, and integrated hacking tools for red team operations…
 nanowraith/cve-2024-29973
Proof-of-concept exploit for CVE-2024-29973, a command injection vulnerability in Zyxel NAS devices. Executes arbitrary OS commands via a crafted…
 0xr2r/cve-2024-3400-palo-alto-os-command-injection
Proof-of-concept exploitation steps for CVE-2024-3400, demonstrating unauthenticated command injection in Palo Alto GlobalProtect via crafted cookie…