
Archived
LAZYPARIAH
 octetsplicer/lazypariah
A tool for generating reverse shell payloads on the fly.
command-and-controlctfexploitation+5
1
octetsplicer/lazypariahA tool for generating reverse shell payloads on the fly.
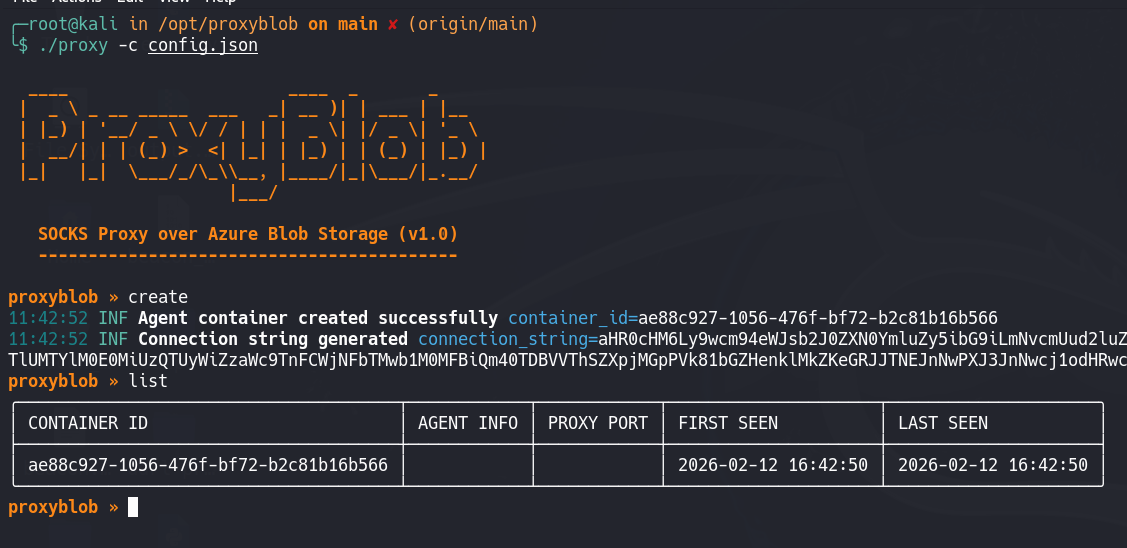 dazzyddos/clickonceblobber
Weaponize signed .NET ClickOnce applications for initial access by hijacking a dependency DLL via AppDomainManager injection and loading a C# port of…
 ic3-512/linux-root-kit
End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…
 dvkunion/cve-2025-53547-poc
CVE-2025-53547 one of poc code
 c1ph3rbyt3/cve-2022-24816
Exploit script for CVE-2022-24816 targeting GeoServer. Executes arbitrary commands on vulnerable servers via crafted HTTP requests. Includes…
 enkomio/alanframework
A C2 post-exploitation framework
 darkcodersc/sharpftpc2
A Streamlined FTP-Driven Command and Control Conduit for Interconnecting Remote Systems.
 trickster0/offensiverust
Rust Weaponization for Red Team Engagements.