

OffensivePascal-CVE-2011-2523
 mfernstrom/offensivepascal-cve-2011-2523
FreePascal implementation of the vsFTPD 2.3.4 CVE-2011-2523
command-and-controlexploitationpayload-development+3
mfernstrom/offensivepascal-cve-2011-2523FreePascal implementation of the vsFTPD 2.3.4 CVE-2011-2523
 mawk0235/cve-2024-23346
This is an exploit for CVE-2024-23346 that acts as a "terminal" (tested on chemistry.htb)
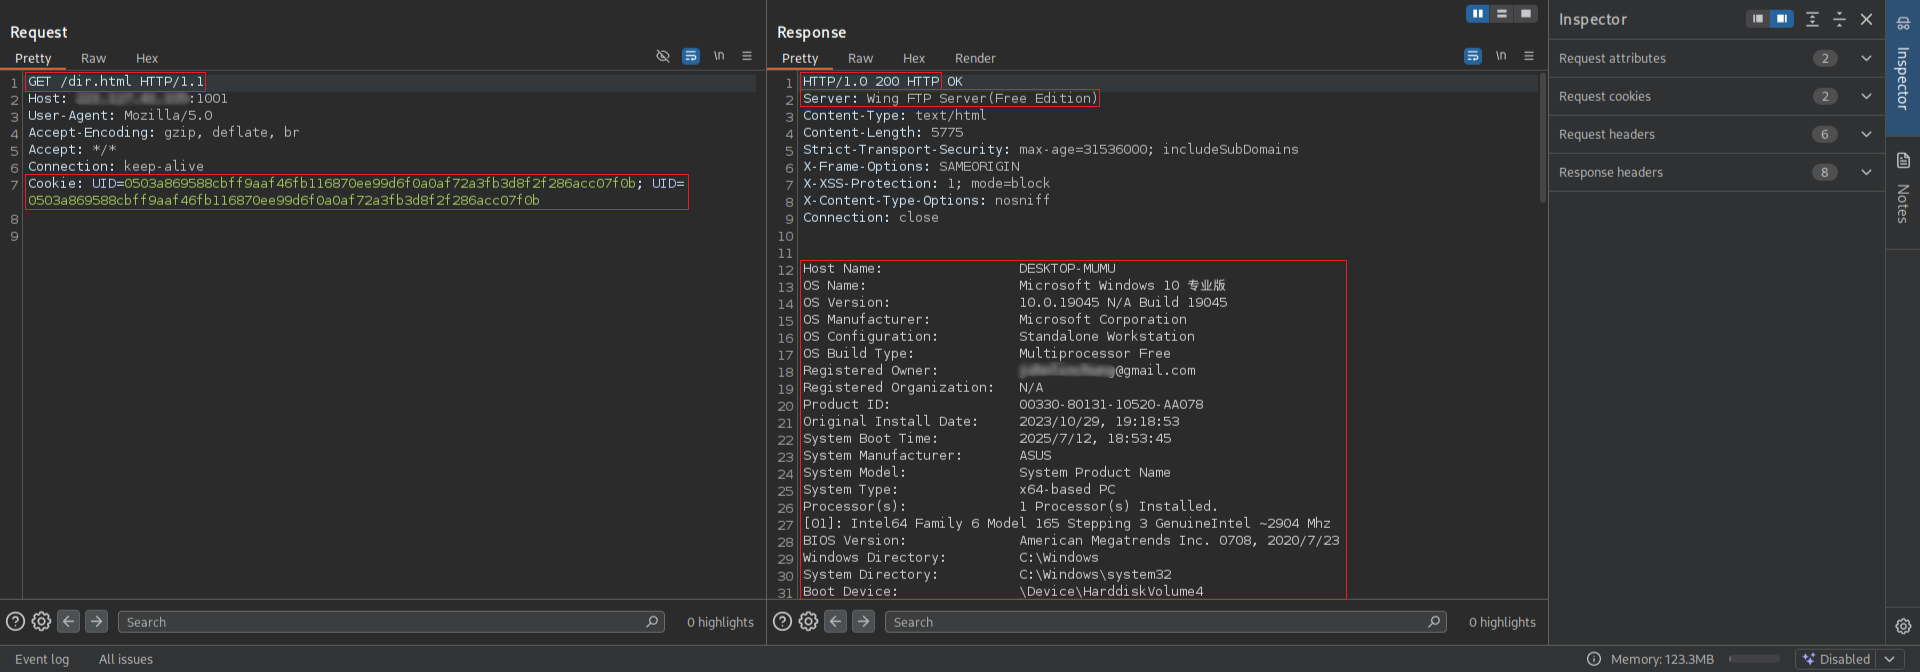 r0otk3r/cve-2025-47812
Python exploit for CVE-2025-47812, achieving remote code execution on Wing FTP Server via Lua injection in the login username parameter. Supports…
 nxvh1337/cve-2025-63406-poc
Small PoC to automate exploitation of CVE-2025-63406.
 dahalsamir/cve-2011-2523-exploit
Python exploit for vsFTPd 2.3.4 backdoor (CVE-2011-2523) that triggers a hidden shell on port 6200 via a crafted username, enabling remote command…
 josebarrios/cve-2007-2447
Remote Command Injection Vulnerability (CVE-2007-2447), allows remote attackers to execute arbitrary commands by specifying a Samba username…
 foudadev/cve-2007-2447
Educational exploit implementation for CVE-2007-2447 Samba 3.0.20-3.0.25rc username map script command execution vulnerability with Python SMB client…
 erpscanteam/cve-2018-2380
PoC of Remote Command Execution via Log injection on SAP NetWeaver AS JAVA CRM
 b33m0x00/cve-2007-2447
CVE-2007-2447 samba remote code execution
 ziemni/cve-2007-2447-in-python
Python implementation of 'Username' map script' RCE Exploit for Samba 3.0.20 < 3.0.25rc3 (CVE-2007-2447).
 wildfootw/cve-2007-2447_samba_3.0.25rc3
Exploit for Samba 3.0.0-3.0.25rc3 'Username' map script command execution vulnerability (CVE-2007-2447), enabling remote code execution.
 jonaslejon/ad-autopwn
Automated Active Directory attack chain from zero-auth to Domain Admin. Chains 25+ techniques including Kerberoast, AD CS ESC1-16, Shadow…
 ac8999/prtg-network-monitor-18.2.38---authenticated-remote-code-execution-cve-2018-9276
Python Exploit for CVE: 2018-9276
 0xkn/cve-2007-2447
Python exploit for Samba CVE-2007-2447 username map script remote command execution, delivering a reverse shell payload to a configurable remote…