
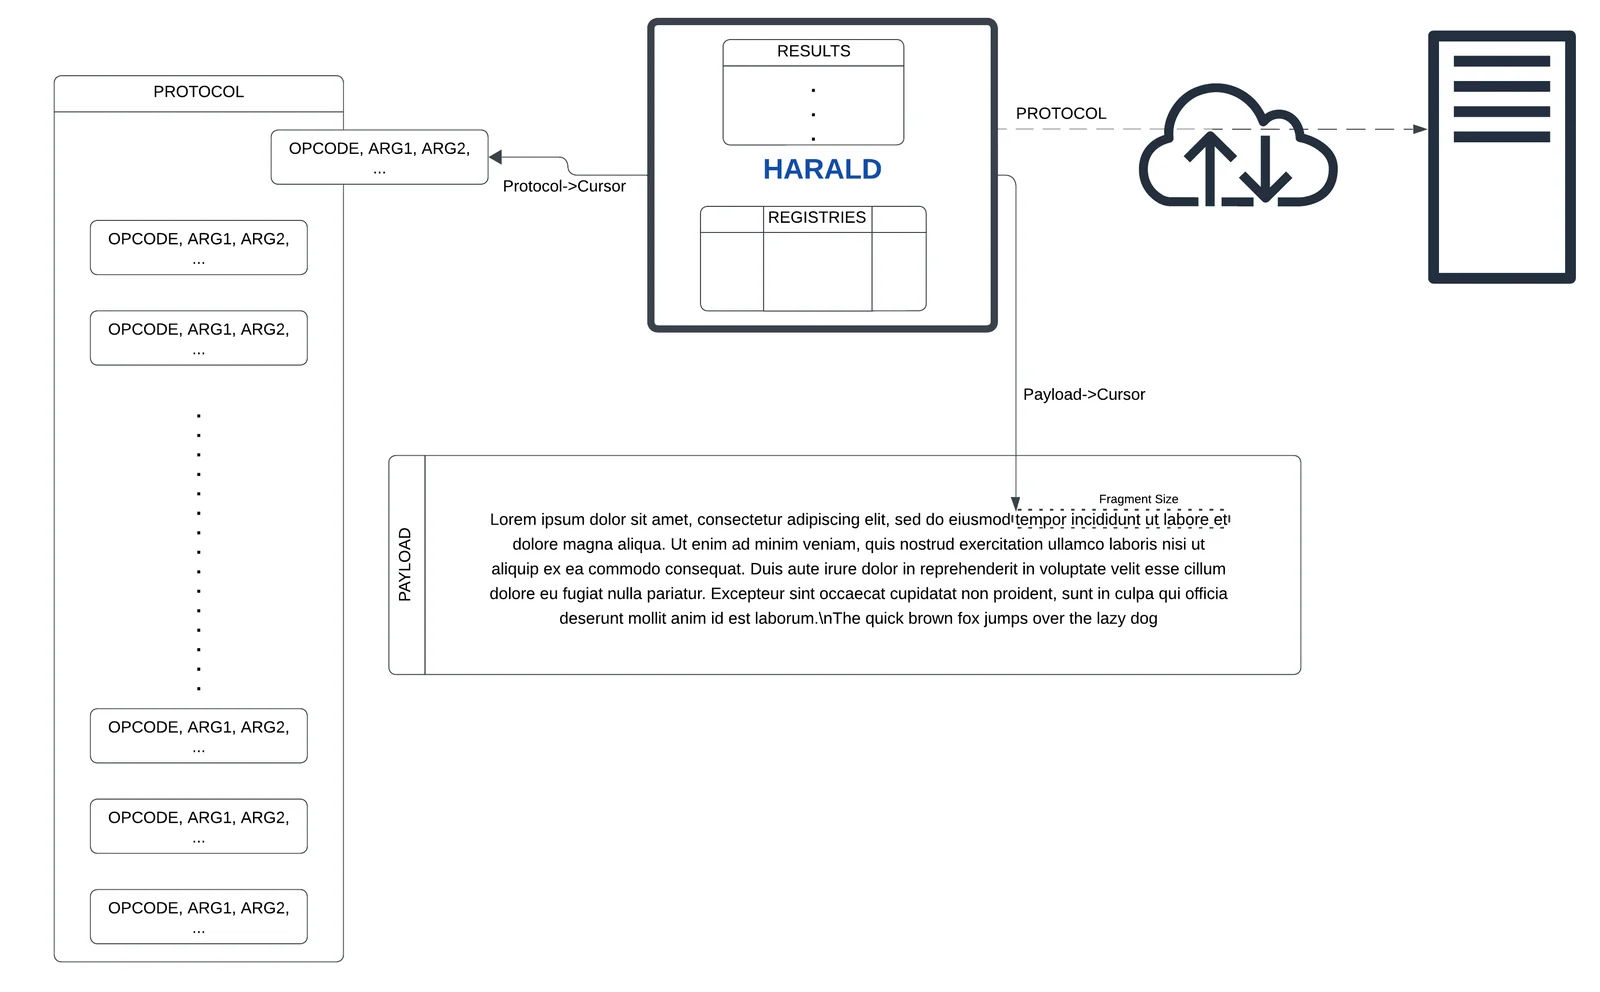
Harald
 gmh5225/harald
An in-memory minimal CPU for agnostic on-the-fly protocols creation
command-and-controlexploitationids-ips-evasion+6
gmh5225/haraldAn in-memory minimal CPU for agnostic on-the-fly protocols creation
 petitoto/chromium-exploit-dev
Toolkit to weaponize Chromium vulnerabilities into reliable, cross-platform, full-chain exploits
 d3vzer0/cnc-relay
Docker projects to retain beacon source IPs using C2 relaying infra
 dsnezhkov/octohook
Git Web Hook Tunnel for C2
 gobysec/cve-2023-28343
Altenergy Power System Control Software set_timezone RCE Vulnerability (CVE-2023-28343)
 explxx/cve-2023-33538
Python Exploit for TP-Link TL-WR940N/TL-WR841N Command Injection Vulnerability
 coolman6942o/-exploit-cve-2023-36025
Windows SmartScreen Security Feature Bypass Vulnerability
 cfielding-r7/poc-cve-2023-2868
Ruby-based proof-of-concept exploit for CVE-2023-2868 command injection in Barracuda ESG, delivering a reverse shell for targeted penetration testing.
 afifudinmtop/cve-2009-3103
Exploit for CVE-2009-3103, a Windows SMB remote code execution vulnerability, with a Python script and Metasploit handler for reverse shell.
 al1ex/cve-2020-35729
CVE-2020-35729
 node9-ai/node9-proxy
Access control for AI agents. Set what Claude Code, Codex, Gemini, Cursor and any MCP server are allowed to do, review risky actions before they run,…
 aashay221999/cve-2024-49368
Explorations of CVE-2024-49368 + Exploit Development
 4n4s4zi/cve-2025-33053_poc
POC exploit for CVE-2025-33053 (external control of file execution path in URL file)
 mythicagents/thanatos
Mythic C2 agent targeting Linux and Windows hosts written in Rust
 wkl-sec/wmiexec
Set of python scripts which perform different ways of command execution via WMI protocol.
 qmadev/tf-mythic-azure
Automatically deploying Mythic C2 in Azure using Terraform
 shiva108/pentestproxy
Scripts for: How to Build a Covert Pentesting Infrastructure Almost Free