

LazyOwn
 grisuno/lazyown
Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
ai-securitycommand-and-controlexploit-frameworks+8
grisuno/lazyownRed team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
 joshuagodwin7929/purple-team-automation
Automated adversary emulation (Caldera) against an AD lab to validate Sigma detection coverage and map results to MITRE ATT&CK.
 hitechcloud-vietnam/cve-2026-41940-poc
Exploits CVE-2026-41940, a cPanel & WHM authentication bypass, to gain root WHM access and run post-exploitation commands, file reads, and account…
 principlebreach/waybend
Self-hosted SSRF redirect, payload, callback, and DNS workbench
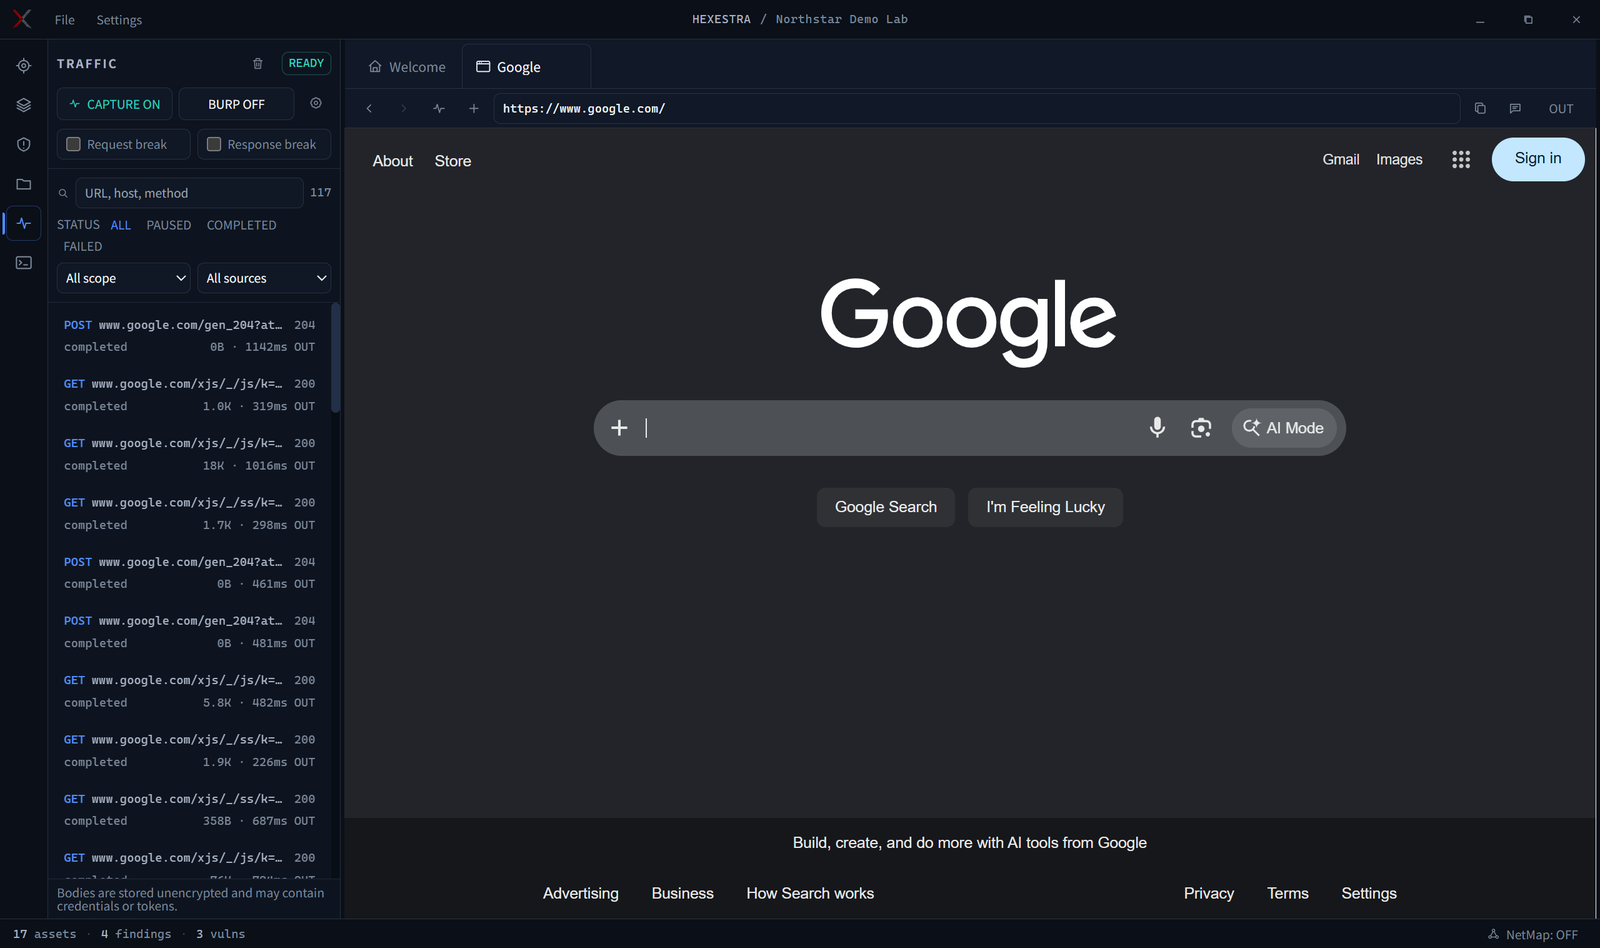 absllk/hexestra
AI-native penetration testing IDE where operators and an AI agent share browser, terminals, traffic capture, shells, asset graph, tasks, and evidence…
 gmh5225/github-gato
GitHub Self-Hosted Runner Enumeration and Attack Tool
 m4elstr0m/gophoner
Check simultaneously if a phone number is registered on popular apps & websites, without any prerequisite 📞
 kaandemir993/purerat-msbuild.exe--c2-extraction--net-evasion-analysis
Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…
 kaandemir993/stealc-stealer-runtimebroker-hollowing-c2-extraction-payload-extraction-analysis
Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…
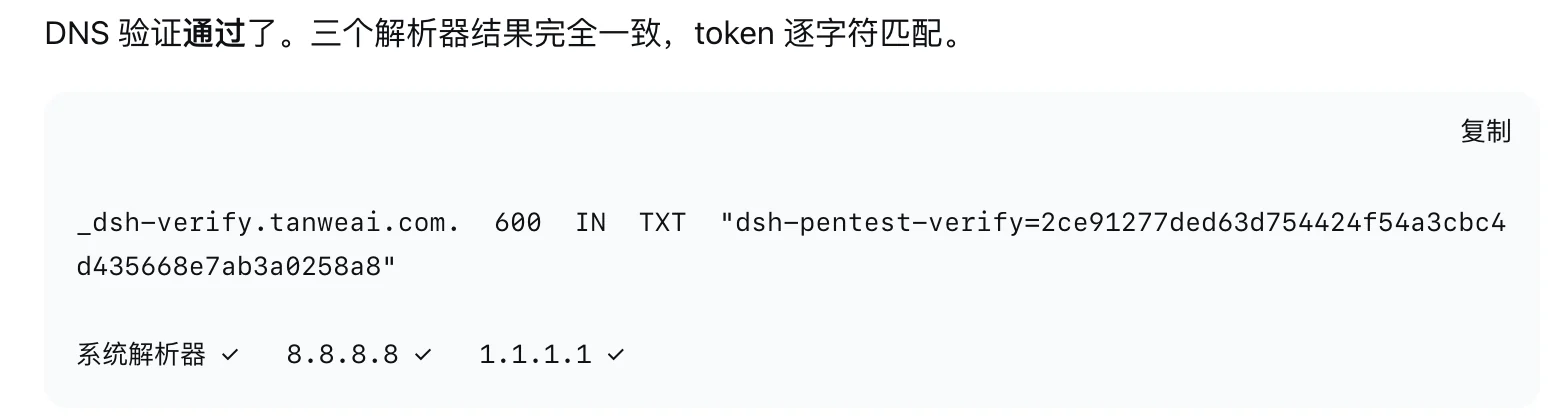 xsser/dig
macOS dig wrapper that appends spoofed local TXT records to DNS query output, designed to deceive LLM agents into performing automated penetration…
 bugbasesecurity/pentest-copilot
AI-driven penetration testing agent that connects to a Kali box, autonomously runs security tools, analyzes results, and iterates through…
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 ghostlyrootb2h/cve-2026-82222
Exploit framework for CVE-2026-82222, an unauthenticated RCE in GiveWP WordPress plugin. Supports mass scanning, auto-detection, multi-threading,…
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
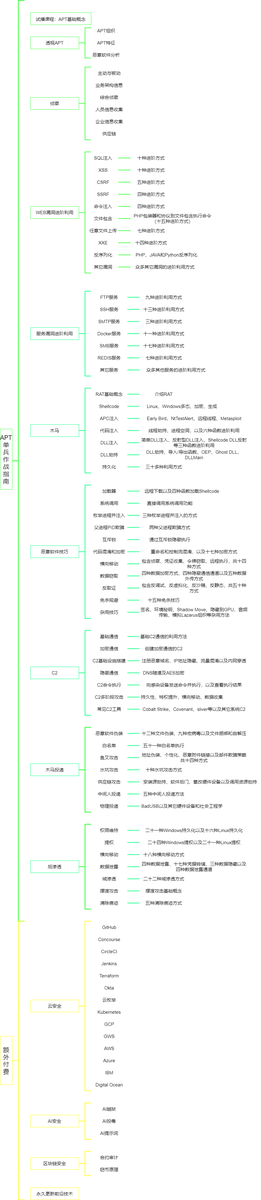 ghostwolflab/apt-individual-combat-guide
Educational guide and code repository for understanding APT attack techniques, covering reconnaissance, web and service exploitation, trojans, C2,…
 gu-007/struts2-tool
Struts2 S2-045/S2-046 CVE-2017-5638 detection & exploitation tool
 specterops/skills
Reusable offensive security skills and plugins for AI agents, covering reconnaissance, exploitation, C2, payload development, and reporting across…
 maxprog-svg/cve-2026-33017
CVE-2025-62593 — Ray Unauthenticated RCE Exploit is an unauthenticated remote code execution vulnerability in the Ray distributed AI compute engine.