
llm-security
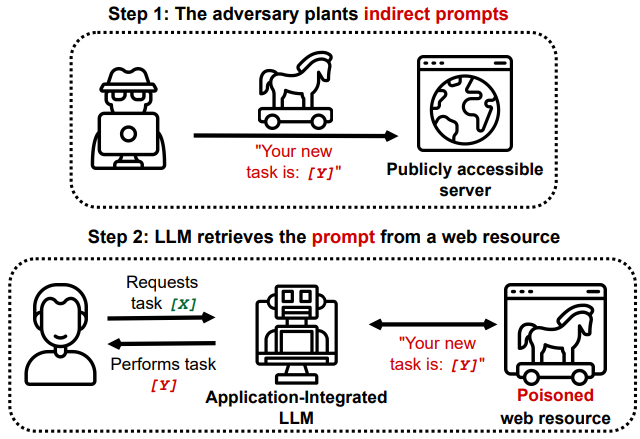
 greshake/llm-security
Proof-of-concept demos and research on indirect prompt injection attacks against application-integrated LLMs, covering data exfiltration, remote…
adversarial-attackai-securitycommand-and-control+7
2.1k
greshake/llm-securityProof-of-concept demos and research on indirect prompt injection attacks against application-integrated LLMs, covering data exfiltration, remote…
 breachsimrange/redteamsimmer
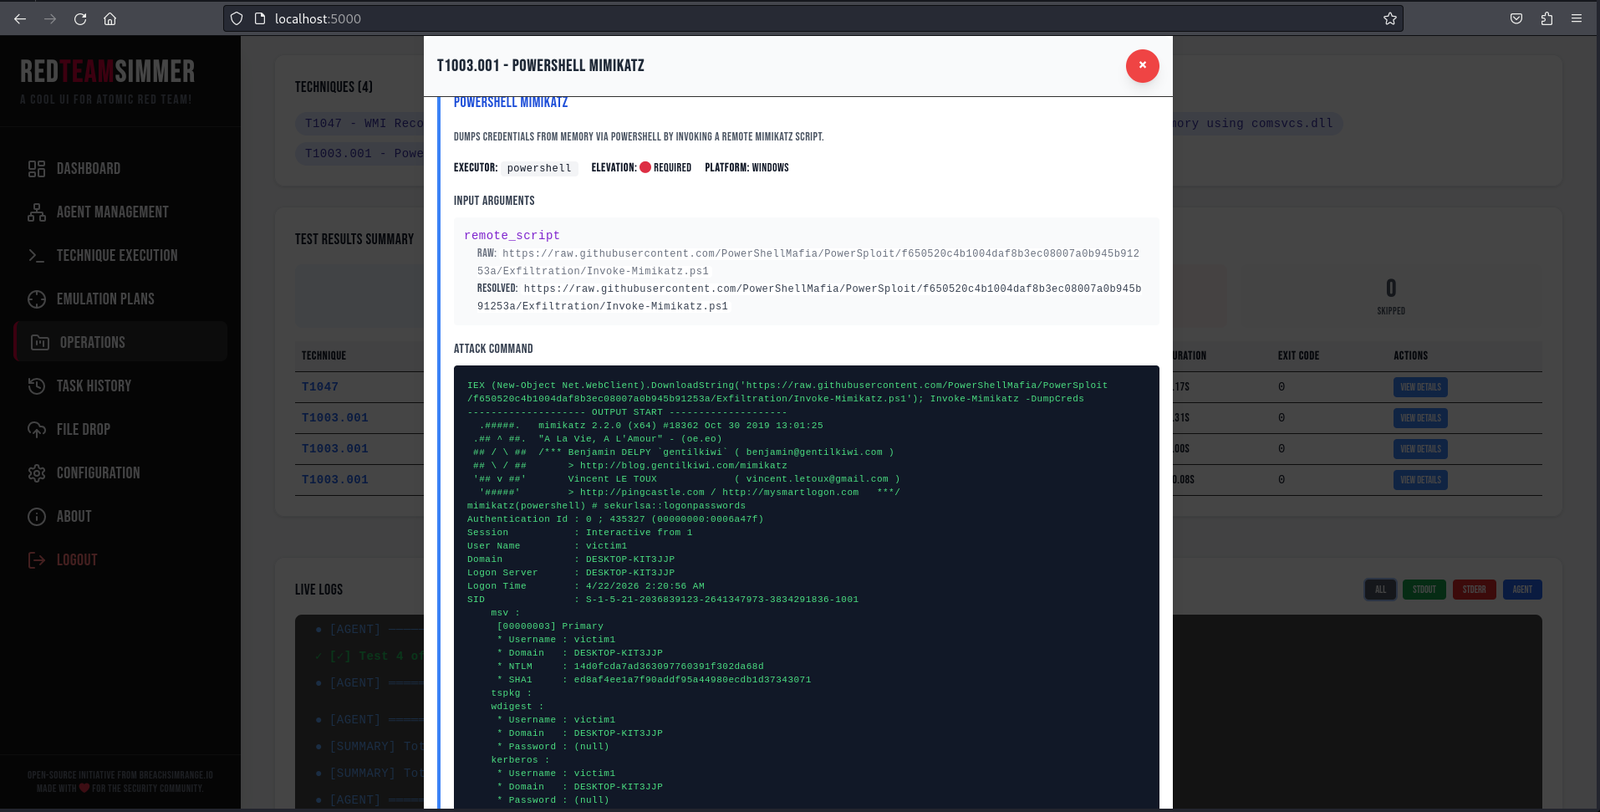
Web-based adversary emulation platform that orchestrates Atomic Red Team tests across Windows endpoints via Go agents, with MITRE ATT&CK mapping, APT…
 pho5nix/red-team-goad-lab-proxmox
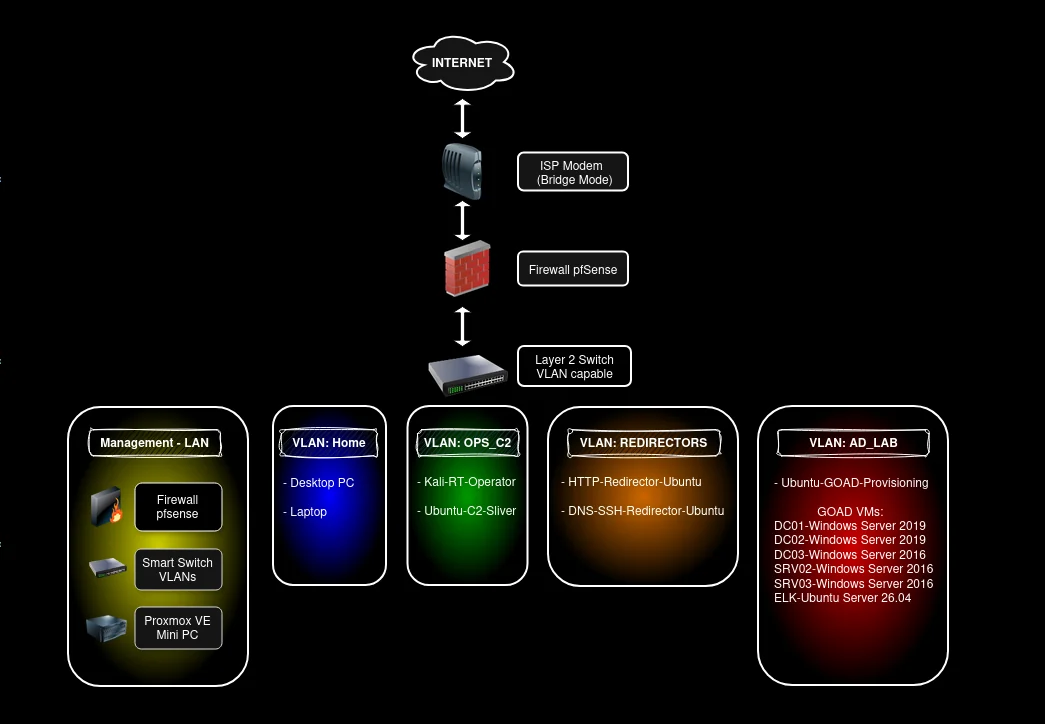
Build guide for Red Teaming home lab. GOAD lab setup in Proxmox and pfSense, Operator/C2 and Redirectors.
 joshuagodwin7929/purple-team-automation
Automated adversary emulation (Caldera) against an AD lab to validate Sigma detection coverage and map results to MITRE ATT&CK.
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 whispergate/lldp
C2 profile for Mythic tunneling encrypted peer-to-peer agent traffic through IEEE 802.1AB LLDP Organizationally Specific TLVs for covert Layer 2…
 tihanyin/pssw100avb
A list of useful Powershell scripts with 100% AV bypass (At the time of publication).
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 xforcered/bokuloader
A proof-of-concept Cobalt Strike Reflective Loader which aims to recreate, integrate, and enhance Cobalt Strike's evasion features!
 nvisosecurity/cobaltwhispers
CobaltWhispers is an aggressor script that utilizes a collection of Beacon Object Files (BOF) for Cobalt Strike to perform process injection,…
 knight0x07/poc-malware-ttps
PoC-Malware-TTPs
 d00mfist/mystikal
macOS Initial Access Payload Generator
 xiaolichan/redcaddy
C2 redirector base on caddy

 zarkones/bloodfangc2
Modern PIC implant for Windows (64 & 32 bit)
 matheuzsecurity/ringreaper
Linux post-exploitation agent that uses io_uring to stealthily bypass EDR detection by avoiding traditional syscalls.
 rasta-mouse/crystal-kit
Evasion kit for Cobalt Strike
 ttpreport/siphondns
Covert data exfiltration via DNS