CVE-2026-58457
 j4ck3lsyn-gen2/cve-2026-58457
PoC tools for CVE-2026-58457: Unauthenticated OS Command Injection leading to remote root on Shenzhen Aitemi M300 Wi-Fi Repeater (MT02). Includes…
command-and-controleducationexploitation+7
3
j4ck3lsyn-gen2/cve-2026-58457PoC tools for CVE-2026-58457: Unauthenticated OS Command Injection leading to remote root on Shenzhen Aitemi M300 Wi-Fi Repeater (MT02). Includes…
 joshuavanderpoll/cve-2025-66398
CVE-2025-66398 — Signal K Server ≤ 2.18.0 RCE PoC
 dereeqw/netspy
NetSpyC2 – Python C2 Server with RSA Key Exchange and AES-GCM Encrypted Sessions
 0zetrium0/cve-2025-69212_poc
This repository contains a PoC exploit for CVE-2025-69212.
 ustayready/python-pentesting
Just a repo of random Python scripts to get pentesters started with the Python language on engagements.
 undeadsec/socialfish
Modern dynamic phishing toolkit for authorized red team exercises. Clones login pages, captures credentials, cookies, and 2FA codes with a live…
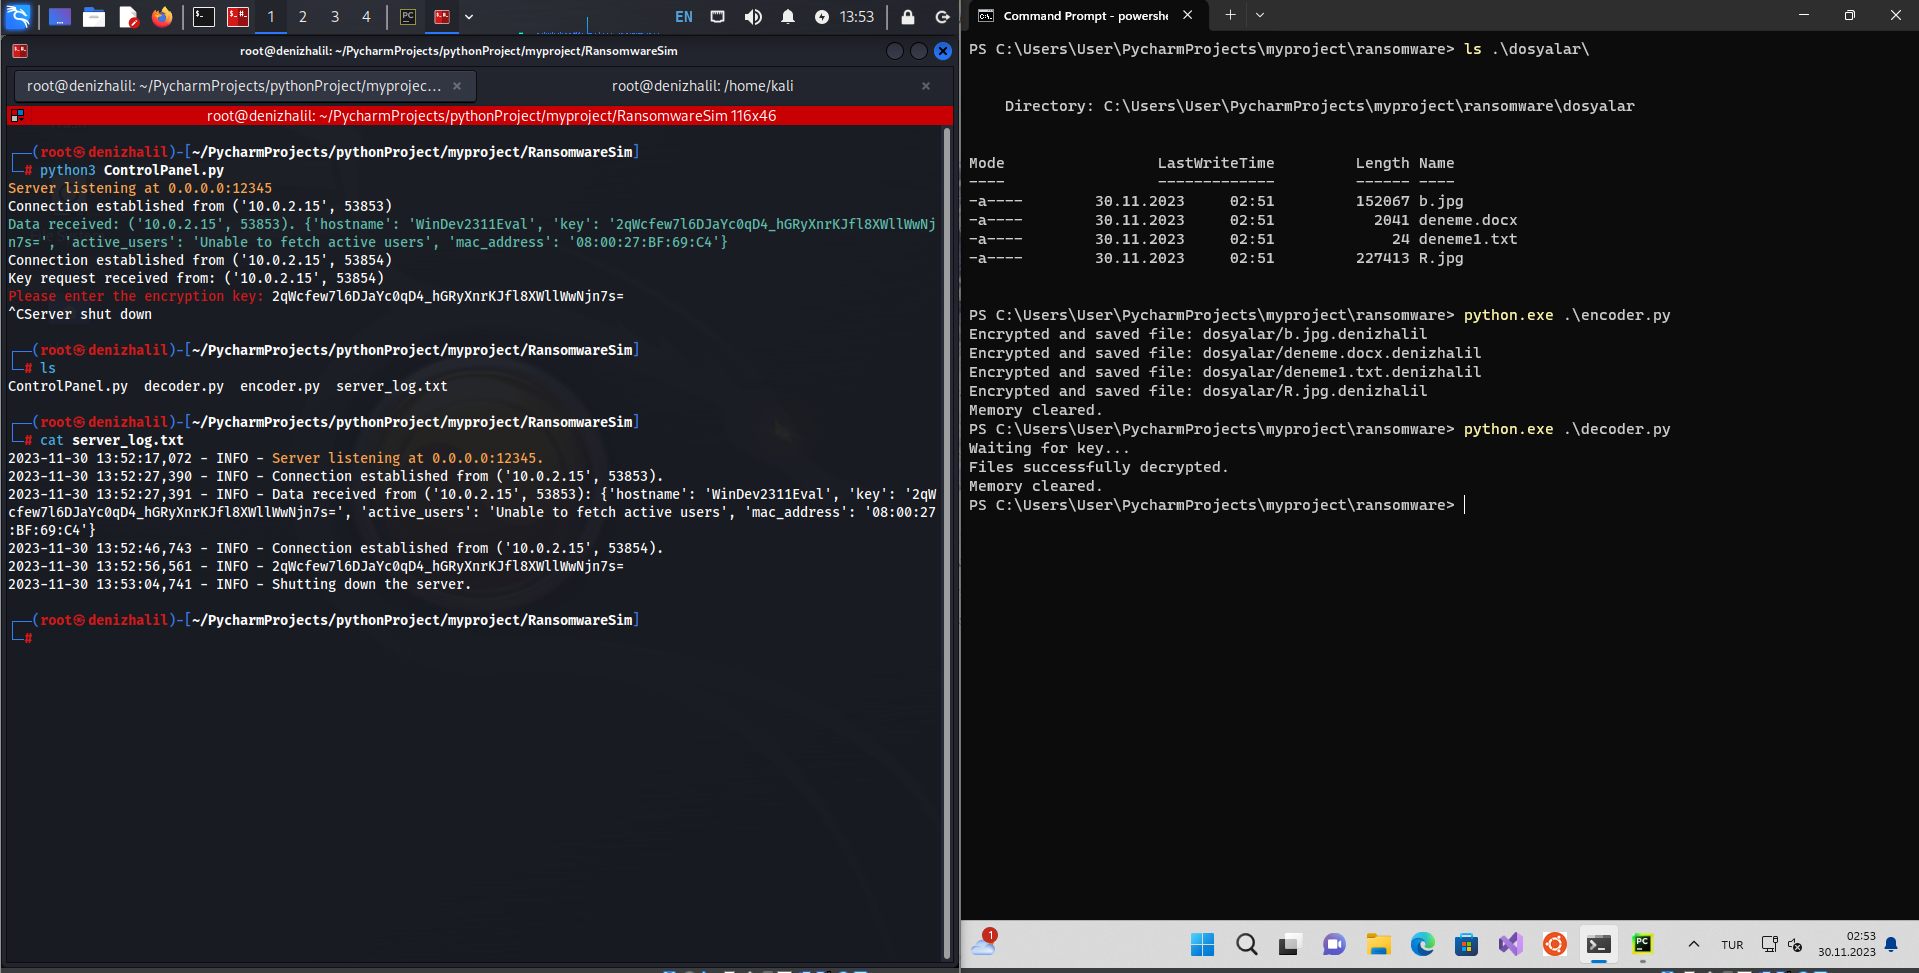 halildeniz/ransomwaresim
Educational ransomware simulator demonstrating file encryption, C2 communication, and decryption for cybersecurity training and malware analysis.
 enelg52/kittystager
KittyStager is a simple stage 0 C2. It is made of a web server to host the shellcode and an implant, called kitten. The purpose of this project is to…