external-c2-experiments

Go external C2 module for go-exploit that catches reverse SSH shells, providing a server listener and payload client for integrating custom C2…

Go external C2 module for go-exploit that catches reverse SSH shells, providing a server listener and payload client for integrating custom C2…

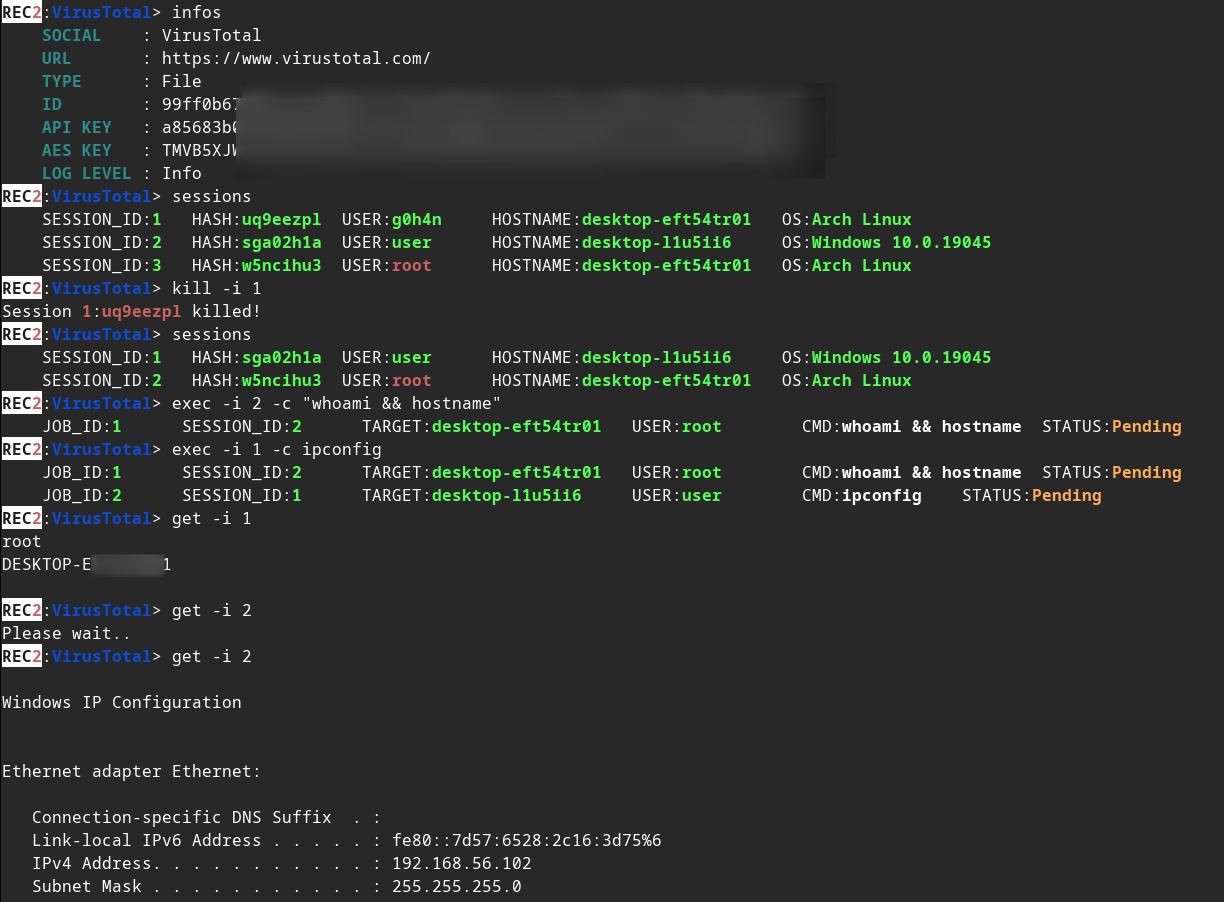
REC2 (Rusty External Command and Control) is client and server tool allowing auditor to execute command from VirusTotal and Mastodon APIs written in…

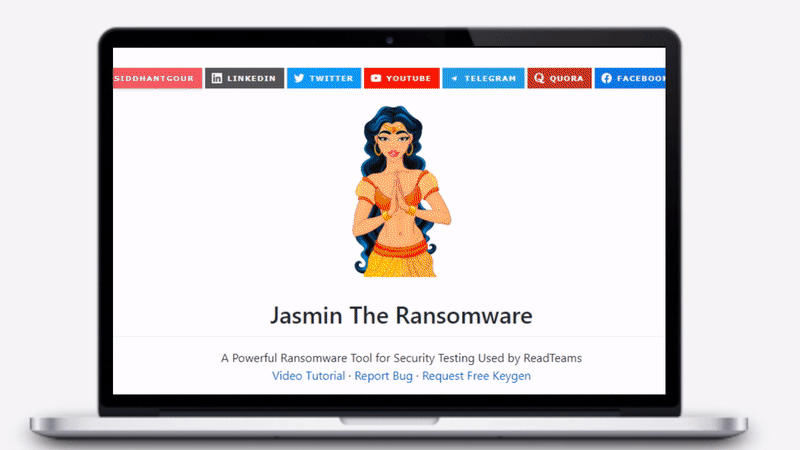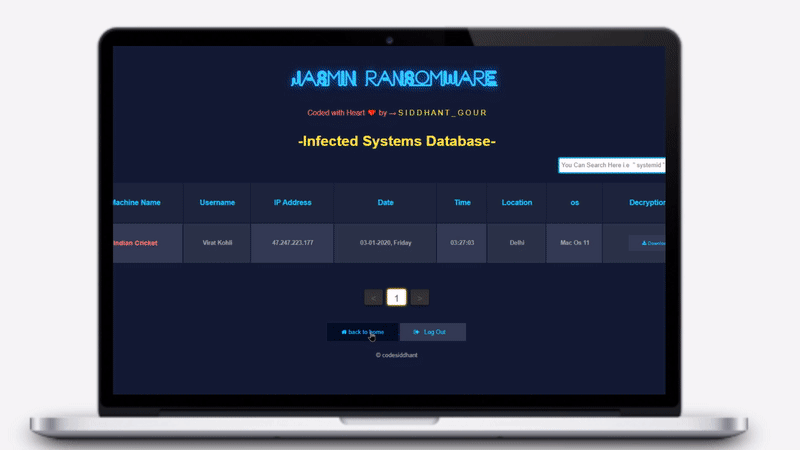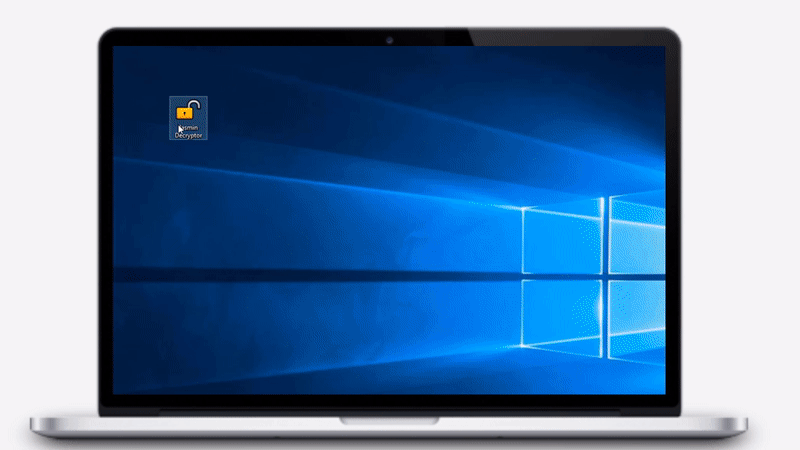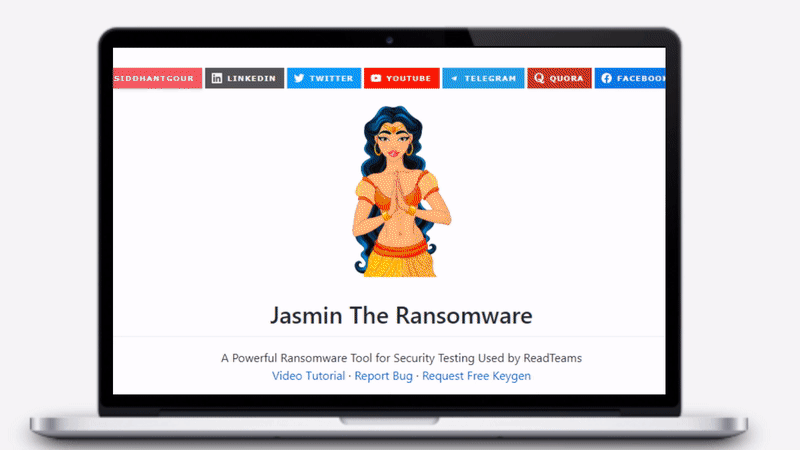
Jasmin Ransomware is an advanced red team tool (WannaCry Clone) used for simulating real ransomware attacks. Jasmin helps security researchers to…

Voron messenger crypto/protocol library (X3DH-lite + Double Ratchet, group sender-keys, onion transport) — external review requested

Docker projects to retain beacon source IPs using C2 relaying infra

External C2 Using IE COM Objects

POC for Cobalt Strike external C2

Aggressor Script, Kits, Malleable C2 Profiles, External C2 and so on

A library for integrating communication channels with the Cobalt Strike External C2 server

Python api for usage with cobalt strike's External C2 specification

Python api for usage with cobalt strike's External C2 specification

CobaltStrike External C2 for Websockets

Lightweight PowerShell-based exploit for CVE-2023-3519, enabling remote code execution without external dependencies like NMAP or Python.

Fawkes is a golang Mythic C2 Agent exclusively written by AI.

POC exploit for CVE-2025-33053 (external control of file execution path in URL file)

PoC and technical write-up for CVE-2025-43920, a remote command injection in GNU Mailman 2.1.39's external archiver allowing unauthenticated code…

Proof-of-concept for CVE-2026-4480, a Samba print job name command injection vulnerability. Demonstrates exploitation via malicious print job names…

Cooolis-ms是一个包含了Metasploit Payload Loader、Cobalt Strike External C2 Loader、Reflective DLL injection的代码执行工具,它的定位在于能够在静态查杀上规避一些我们将要执行且含有特征的代码,帮助红队人员更方便快…