mythic_telegram_profile

Mythic C2 profile that tunnels Athena and Apollo agent traffic through Telegram bot-to-bot messages, bridging encrypted payloads to Mythic via its…

Mythic C2 profile that tunnels Athena and Apollo agent traffic through Telegram bot-to-bot messages, bridging encrypted payloads to Mythic via its…

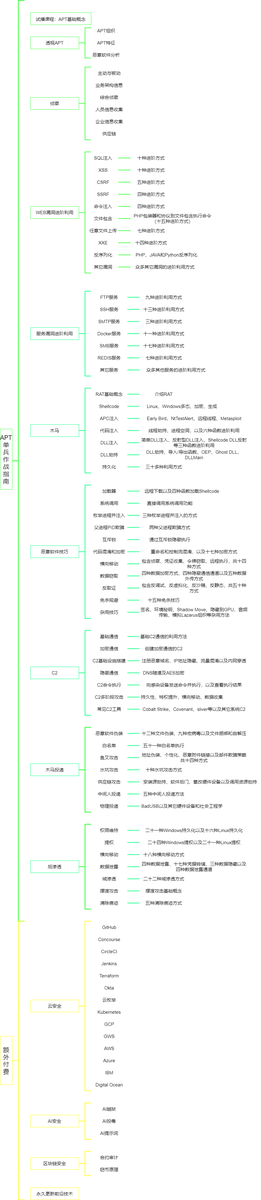
Educational guide and code repository for understanding APT attack techniques, covering reconnaissance, web and service exploitation, trojans, C2,…

Sliver HTTP(S) C2 PNG bomb DoS exploit — GHSA-663m-7x7m-g4fw (CVE-2026-77622)

CVE-2026-32941 PoC - Sliver Remote OOM

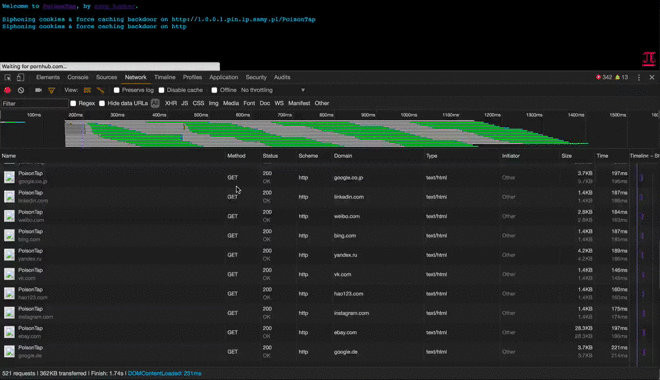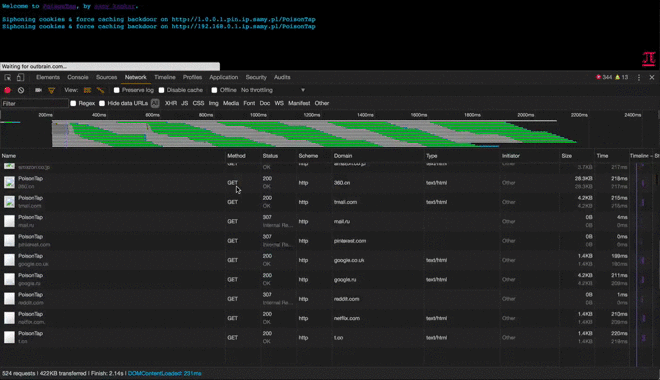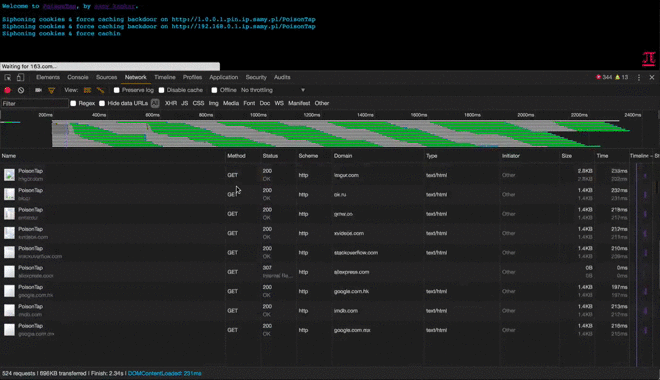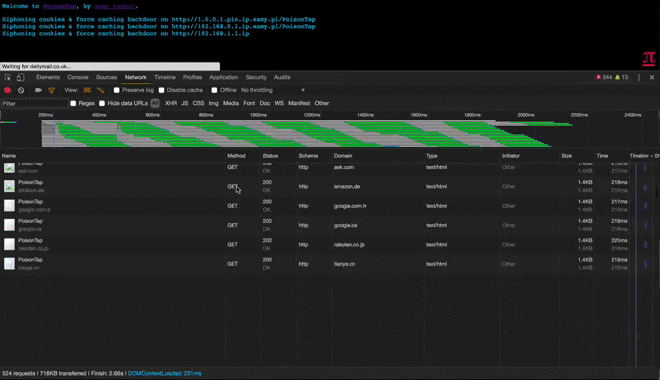
Exploits locked/password protected computers over USB, drops persistent WebSocket-based backdoor, exposes internal router, and siphons cookies using…

Proof-of-concept backdoor for SCCM Management Point using rogue COM service for persistent remote command execution as SYSTEM.

Penetration testing framework with AI-driven decision engine

Remote Administration Toolkit (or Trojan) for POSiX (Linux/Unix) system working as a Web Service

Adaptix C2 service plugin that drives LitterBox payload analysis from the operator UI.

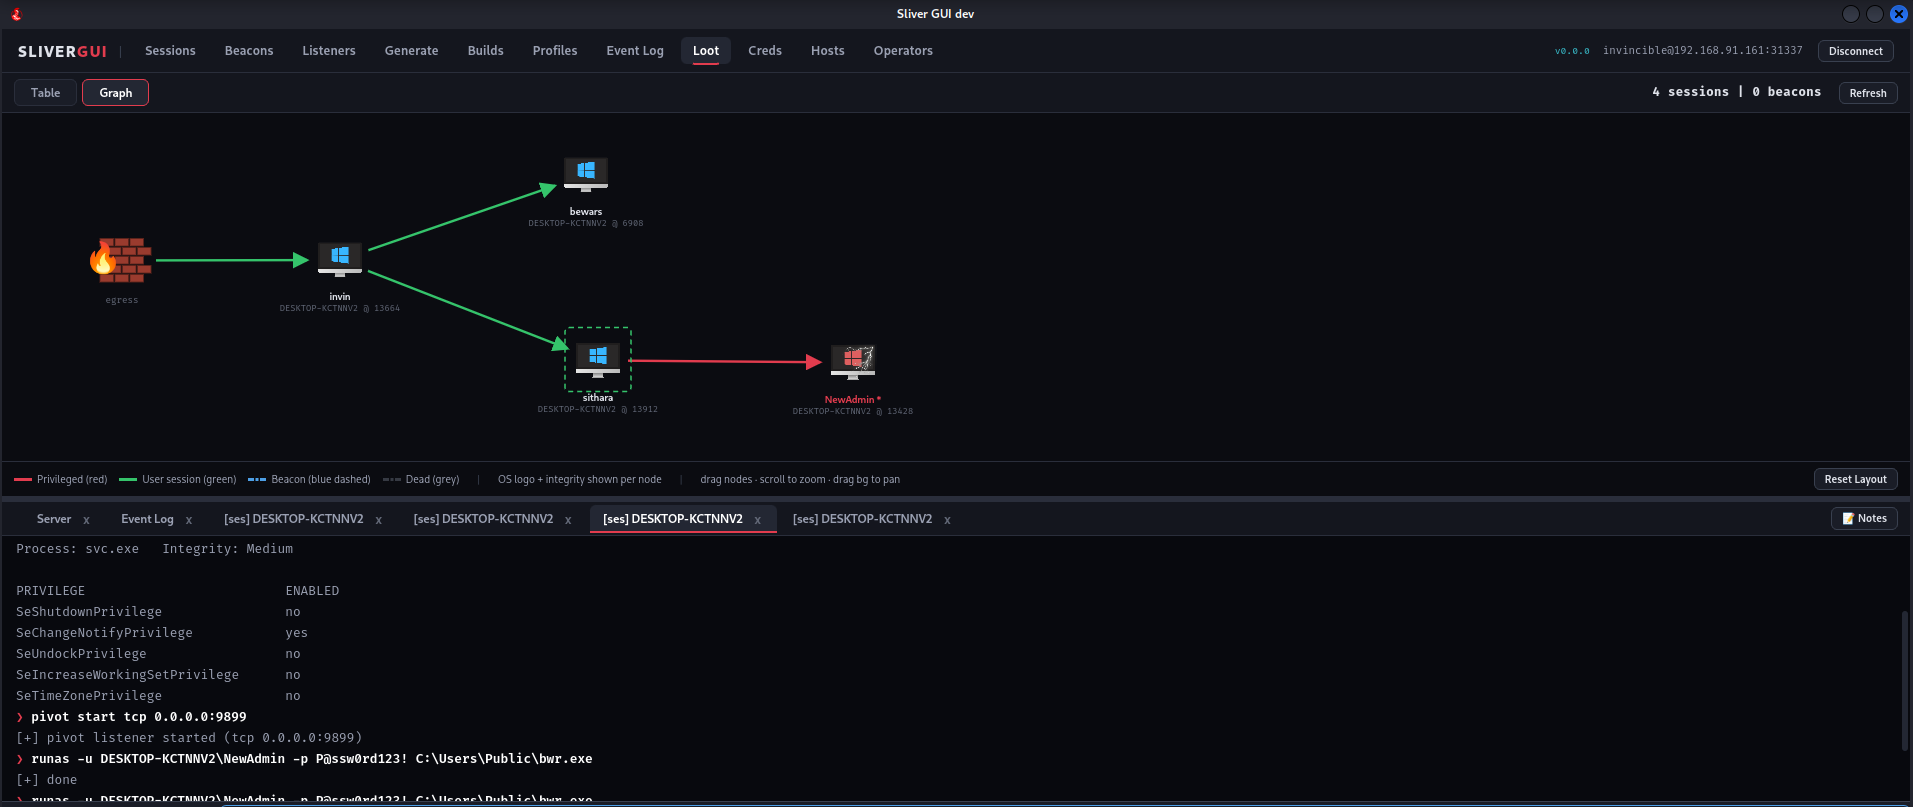
A desktop operator console for Sliver C2, built with Wails. Provides a native, lightweight GUI interface for Sliver by directly interfacing with its…


Shadow Workers is a free and open source C2 and proxy designed for penetration testers to help in the exploitation of XSS and malicious Service…

Script that exploits the vulnerability that allows establishing a backdoor in the UnrealIRCd service with CVE-2010-2075

Remote Command Execution into shell from a vulnerable exim service.

FreePascal implementation of the UnrealIRCD CVE-2010-2075

CVE-2025-60021

CVE-2025-64155-hunter

Comodo