
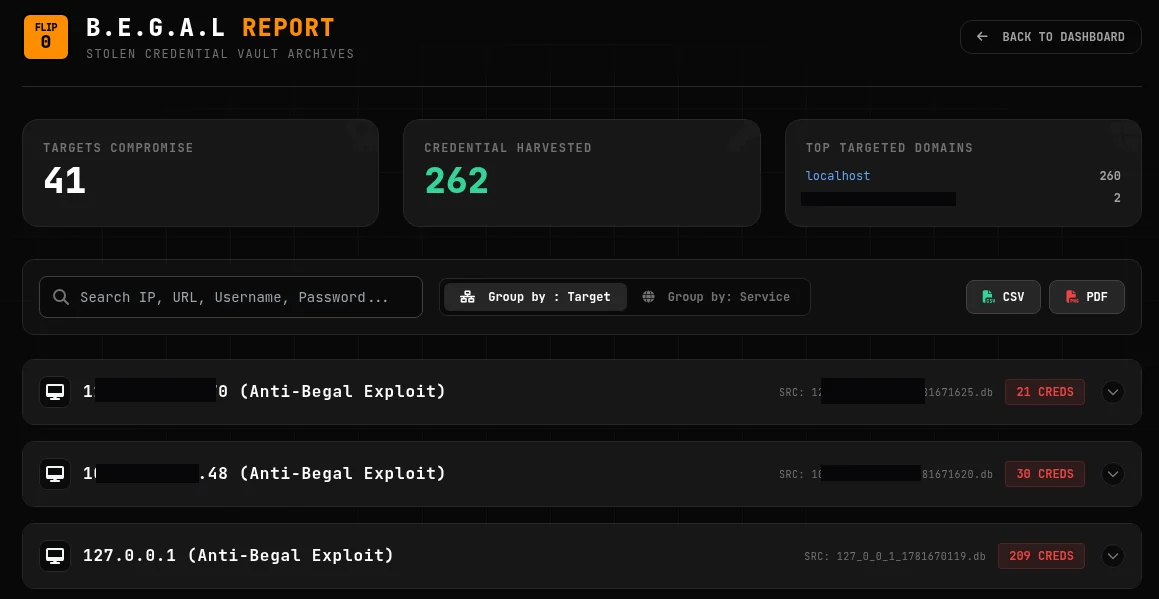
anti-begal.py
 xsanflip/anti-begal.py
Python script that exploits a resource-exhaustion flaw in the B.E.G.A.L C2 collector endpoint, flooding it with spoofed XOR/Base64 payloads to…
command-and-controldefensive-toolsexploitation+5
xsanflip/anti-begal.pyPython script that exploits a resource-exhaustion flaw in the B.E.G.A.L C2 collector endpoint, flooding it with spoofed XOR/Base64 payloads to…
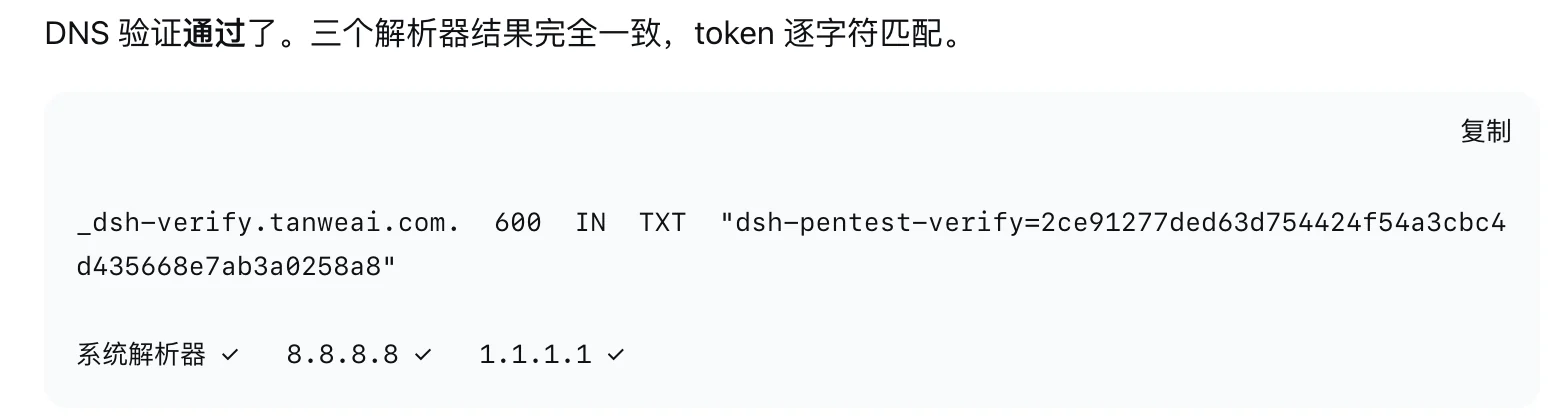 xsser/dig
macOS dig wrapper that appends spoofed local TXT records to DNS query output, designed to deceive LLM agents into performing automated penetration…
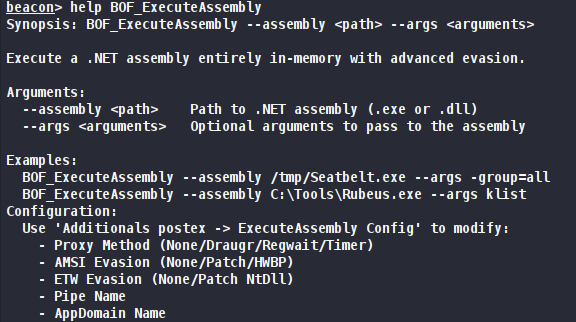 ntdallas/bof_executeassembly
Beacon Object File for Cobalt Strike that executes .NET assemblies in beacon with evasion techniques.
 amaranese/cve-2021-34527
PowerShell exploit for CVE-2021-34527 (PrintNightmare) enabling remote code execution via Windows Print Spooler.
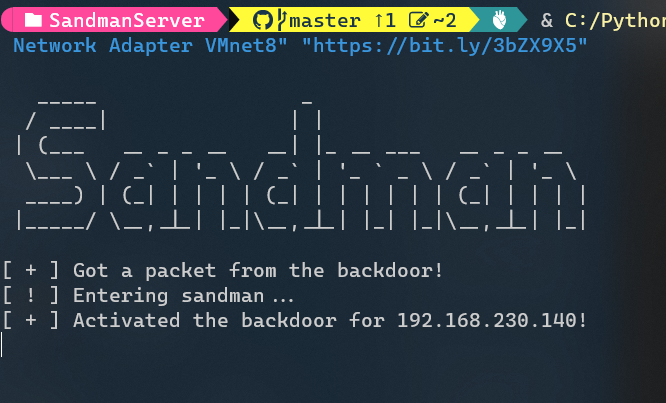 idov31/sandman
NTP-based backdoor for hardened networks, delivering and executing arbitrary shellcode via spoofed NTP traffic with optional persistence as a Windows…