
Hale
 pjlantz/hale
Botnet command & control monitor
command-and-controlincident-responseinformation-gathering+5
pjlantz/haleBotnet command & control monitor
 lazarusreborn/docx-exploit-2021
This docx exploit uses res files inside Microsoft .docx file to execute malicious files. This exploit is related to CVE-2021-40444
 jacobmisirian/dbltekgoippwn
Tool to check if an IP of a DblTek GoIP is vulnerable to a challenge-response login system, send SMS messages from the system, execute remote…
 watersalesman/aura-botnet
A super portable botnet framework with a Django-based C2 server. The client is written in C++, with alternate clients written in Rust, Bash, and…
 ahxr/ghost
Lightweight RAT providing silent remote command-line access, hidden file download/execution, and persistence mechanisms for Windows systems.…
 r00ts3c/ddos-rootsec
Explore RootSec's DDOS Archive, featuring top-tier scanners, powerful botnets (Mirai & QBot) and other variants, high-impact exploits, advanced…
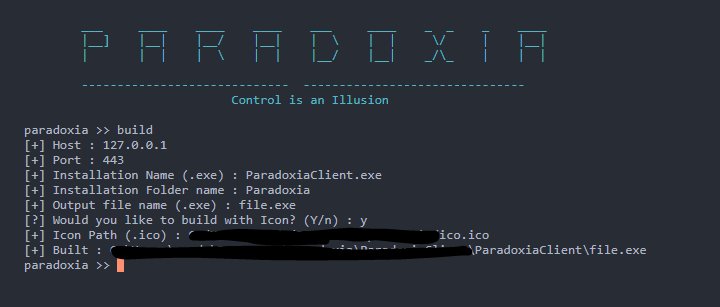 quantumcore/paradoxiarat
ParadoxiaRat : Native Windows Remote access Tool.
 androvirus/blacknet
Free advanced and modern Windows botnet with a nice and secure PHP panel developed using VB.NET.
 alienwithin/owasp-mth3l3m3nt-framework
OWASP Mth3l3m3nt Framework is a penetration testing aiding tool and exploitation framework. It fosters a principle of attack the web using the web as…
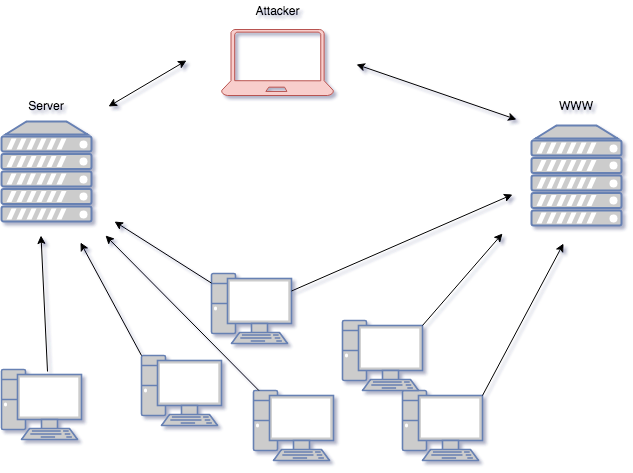 m507/m-botnet
A C2 project that controls a self-propagating MS17-010 worm.
 correcthorsebatterystaple-sudo/orwell-rat-and-botnet
Orwell is a RAT and Botnet designed as a trio of programs.
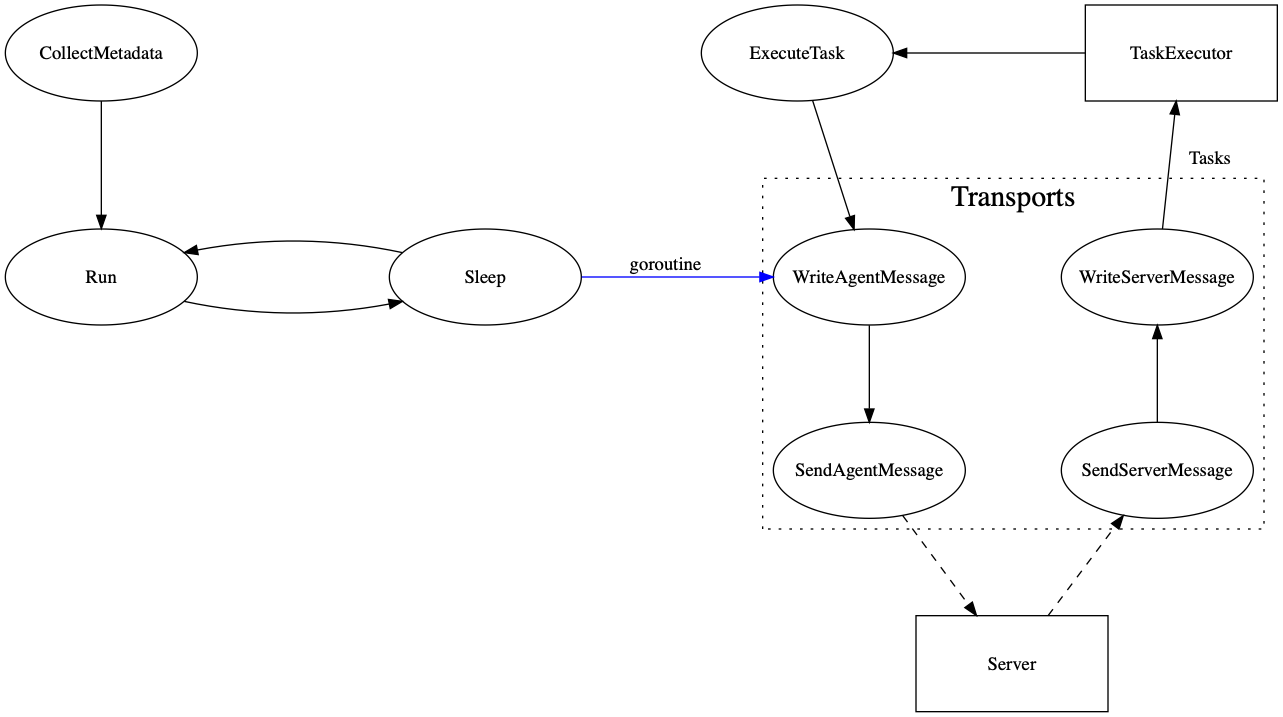 kcarretto/paragon
Red Team engagement platform with the goal of unifying offensive tools behind a simple UI
 flags-alt/abyss-c2
Full-stack C2 framework for IoT exploitation (CVE-2020-25078) with real-time web panel, multi-source target acquisition, vulnerability scanning,…
 sweetsoftware/ares
Python botnet and backdoor
 treehacks/botnet-hackpack
Build a basic Command & Control botnet in C
 saintly2k/katana
Katana Botnet used for DDoS attacks based on the Mirai Botnet. TEACHING PURPOSES ONLY! I CANNOT BE HELD RESPONSIBLE FOR ANYTHING YOU DO WITH IT! I…
 smaash/quasibot
complex webshell manager, quasi-http botnet.