

ScreenshotBOF
 codextf2/screenshotbof
An alternative screenshot capability for Cobalt Strike that uses WinAPI and does not perform a fork & run. Screenshot downloaded in memory.
command-and-controlpayload-developmentpenetration-testing+2
508
codextf2/screenshotbofAn alternative screenshot capability for Cobalt Strike that uses WinAPI and does not perform a fork & run. Screenshot downloaded in memory.
 xlinshan/coldroot
Mac OS Trojan (RAT) made with love <3
 paranoidninja/brute-ratel-c4-community-kit
This repository contains scripts, configurations and deprecated payload loaders for Brute Ratel C4 (https://bruteratel.com/)
 anhkgg/pyrat
PyRat,a rat by python xmlrpc
 ekomssavior/airborne-poc
poc for CVE-2025-24252 & CVE-2025-24132
 kira2040k/avbypass
golang script for bypass AV and work only in windows platform
 zibility/remote
参考Gh0st源码,实现的一款PC远程协助软件,拥有远程Shell、文件管理、桌面管理、消息发送等功能。
 yuvrajshad/freepbx-cve-2025-57819
Unauthenticated SQL Injection to Remote Code Execution in FreePBX — CVE-2025-57819
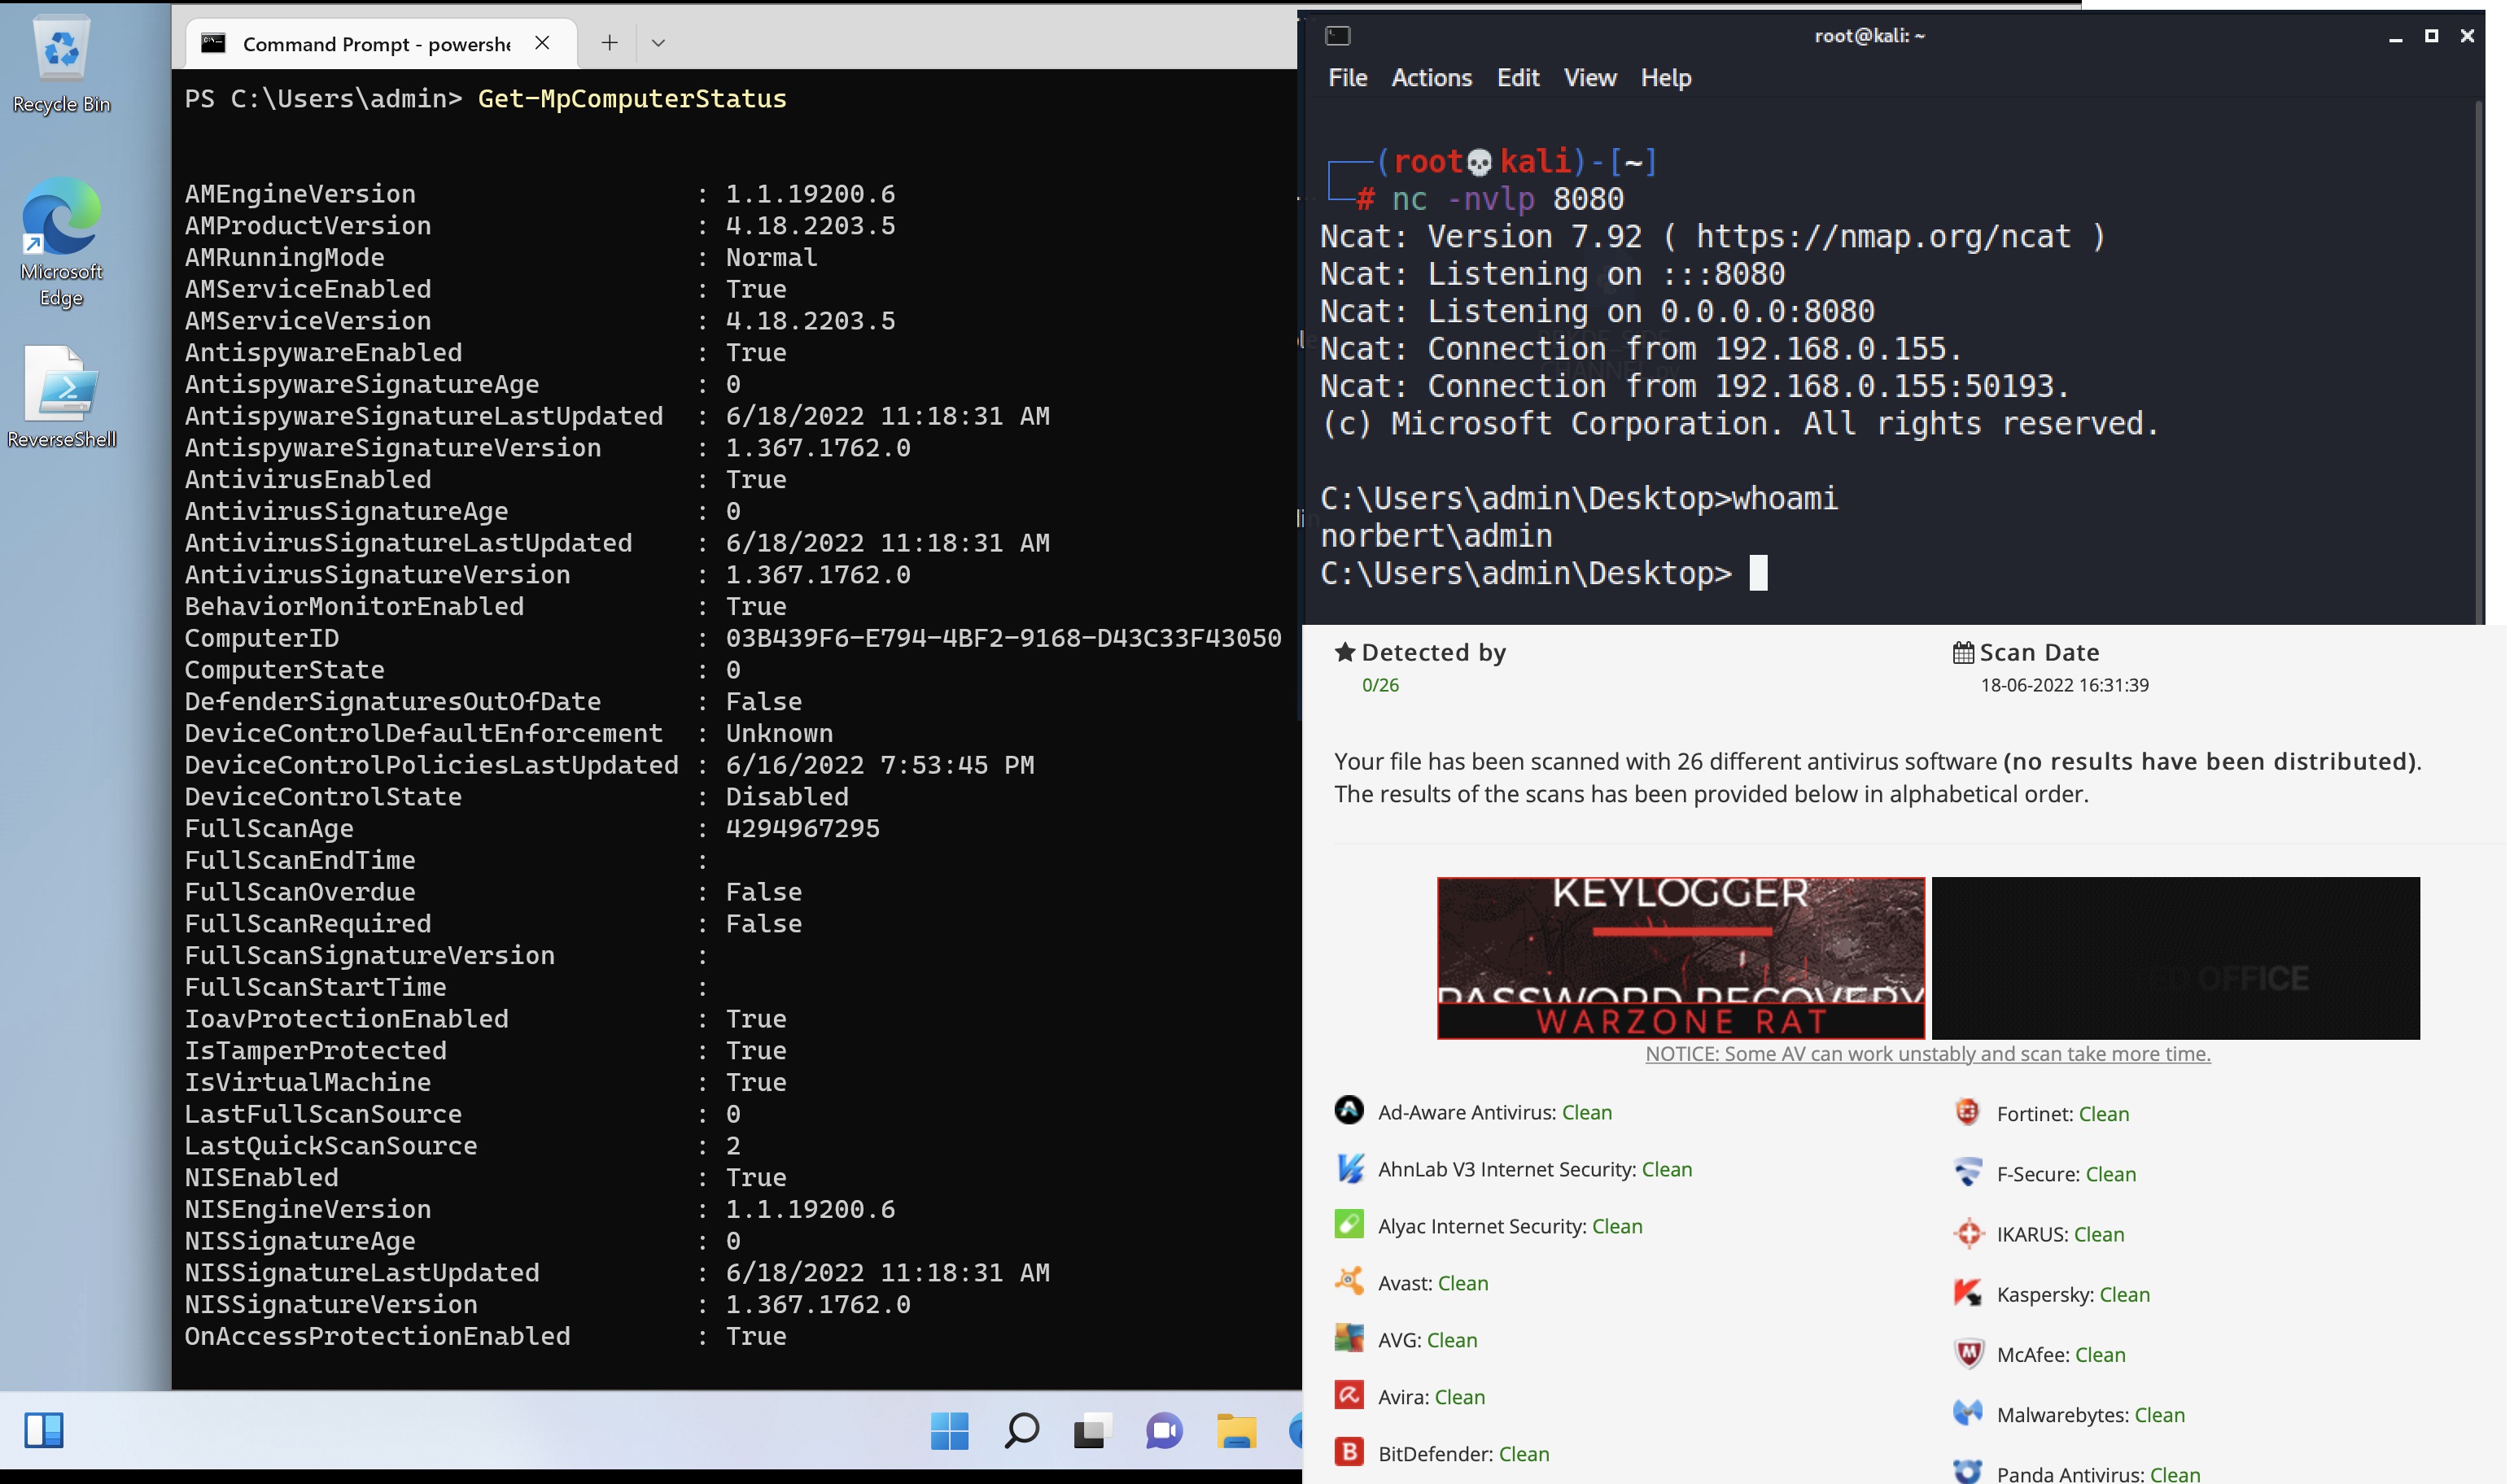 tihanyin/pssw100avb
A list of useful Powershell scripts with 100% AV bypass (At the time of publication).
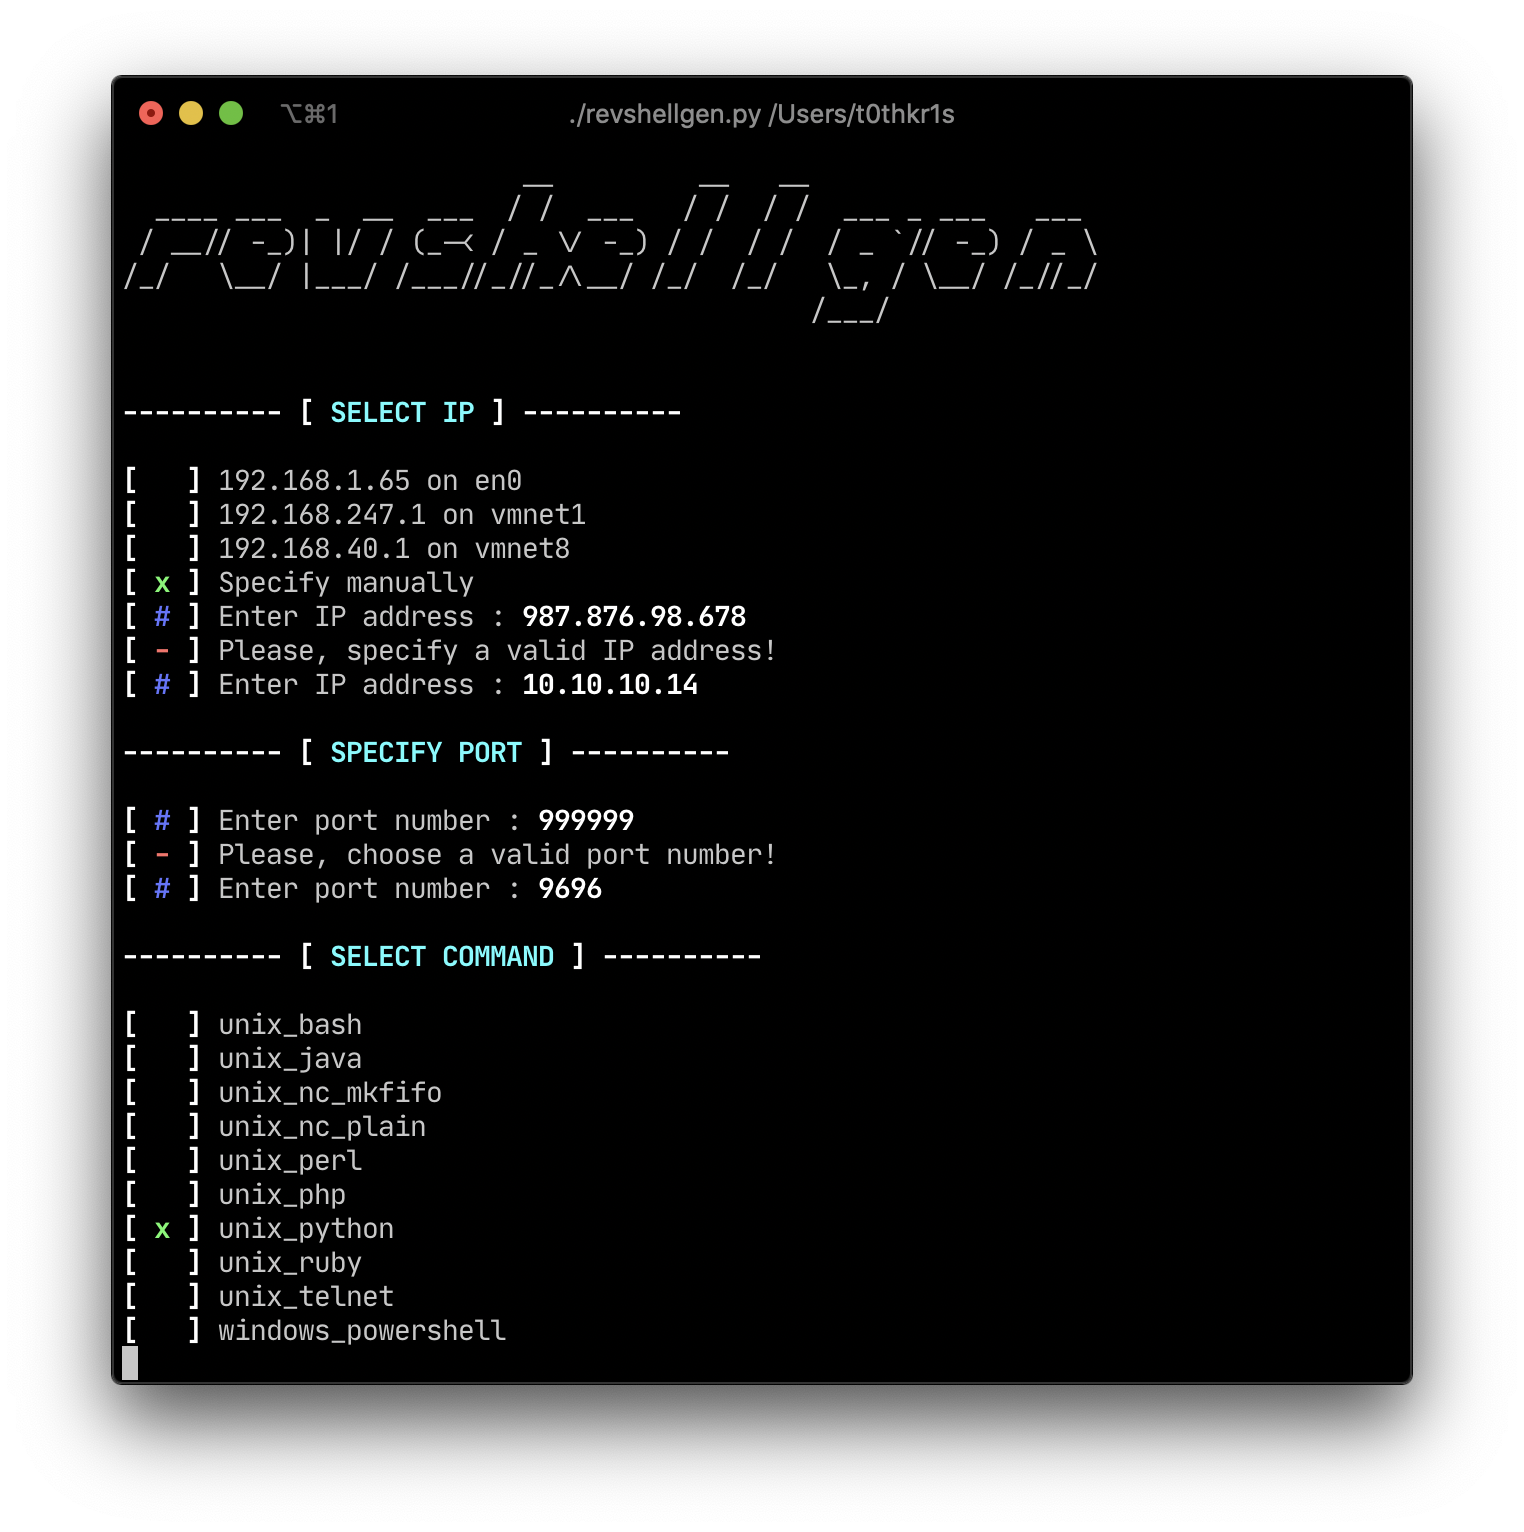 t0thkr1s/revshellgen
Reverse shell generator written in Python 3.
 d00mfist/mystikal
macOS Initial Access Payload Generator
 mttaggart/offensivenotion
Notion as a platform for offensive operations

 idov31/nidhogg
Windows rootkit for Intel x64 with 25+ features, demonstrating rootkit techniques compatible with all Windows 10 and Windows 11 versions.
 paulsec/twittor
A fully featured backdoor that uses Twitter as a C&C server
 m4rm0k/talkingben
UEFI rootkit under development focusing on privilege escalation, C2 integration, and anti-EDR/AV evasion for real-world malware deployment.
 tsuyoken/imgbackdoor
Hide your payload into .jpg file
 zarkones/bloodfangc2
Modern PIC implant for Windows (64 & 32 bit)