
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
355 results
BEAR-C2 preview

BEAR-C2

GitHubs3n4t0r-0x0/bear-c2

The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…

adversarial-attackcommand-and-controldata-exfiltration+8
679
4 days ago
cplt preview

cplt

GitHubnavikt/cplt

Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…

ai-securitycommand-and-controlconfiguration-auditing+7
1213 days ago
sliver preview

sliver

GitHubbishopfox/sliver

Adversary Emulation Framework
adversarial-attackcommand-and-controldata-exfiltration+16
11.9k5 days ago
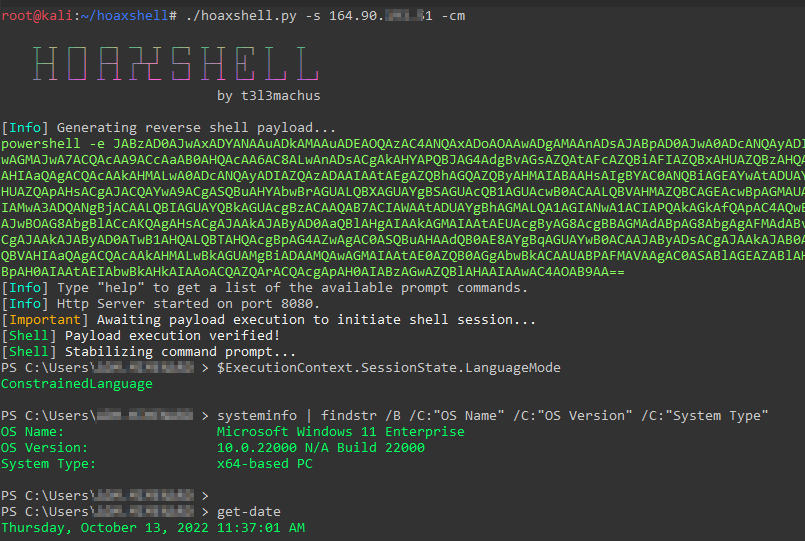
hoaxshell preview

hoaxshell

GitHubt3l3machus/hoaxshell

A Windows reverse shell payload generator and handler that abuses the http(s) protocol to establish a beacon-like reverse shell.

command-and-controlexploitationpayload-generation+5
3.5k1 year ago
CVE-2021-40444 preview

CVE-2021-40444

GitHubklezvirus/cve-2021-40444

CVE-2021-40444 - Fully Weaponized Microsoft Office Word RCE Exploit
command-and-controleducationexploitation+4
8332 years ago
chisel preview

chisel

GitHubjpillora/chisel

Fast TCP/UDP tunnel over HTTP with SSH encryption, supporting reverse port forwarding, SOCKS5 proxy, and client authentication for secure network…

command-and-controldata-exfiltrationgeneral-purpose-utilities+8
16.6k24 days ago
Empire preview

Empire

GitHubbc-security/empire

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
adversarial-attackcommand-and-controldata-exfiltration+16
5.3k17 days ago
MrRAT preview

MrRAT

GitHubuser696/mrrat

:mouse: This is a cross-platform Python 2.x Remote Access Trojan (RAT)

command-and-controlencryption-decryption-toolspayload-development+3
149 years ago
yakit preview

yakit

GitHubyaklang/yakit

All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
command-and-controlexploit-frameworksfuzzing+9
7.8k1 day ago
pybeacon preview

pybeacon

GitHubnccgroup/pybeacon

A collection of scripts for dealing with Cobalt Strike beacons in Python
command-and-controlencryption-decryption-toolsexploitation+3
1685 years ago
notionterm preview

notionterm

GitHubariary/notionterm

Embed a reverse shell in Notion pages using the Notion API as a proxy, enabling stealthy remote shell sessions with encrypted and authenticated…
command-and-controlexploitationpayload-generation+3
1383 years ago
TelegramRAT preview

TelegramRAT

GitHubmachine1337/telegramrat

Cross Platform Telegram based RAT that communicates via telegram to evade network restrictions
command-and-controlinformation-gatheringpost-exploitation+3
4511 year ago
Girsh preview

Girsh

GitHubnodauf/girsh

Automatically spawn a reverse shell fully interactive for Linux or Windows victim

command-and-controlexploitationpayload-generation+5
3593 years ago
Tourmaline preview

Tourmaline

GitHubv-pun215/tourmaline

Reverse engineering notes, deobfuscated source, IOCs, and YARA rules for the Tourmaline ClickFix Python RAT, covering its DNS tunnel and blockchain…

command-and-controlcryptographydigital-forensics+7
1014 days ago
stratum-c2 preview

stratum-c2

GitHublame-projects/stratum-c2

Cloud dead-drop C2 framework — RSA-4096 + AES-256-GCM, 5 cloud providers, Rust-only agents, P2P mesh, persistence engine, credential harvesting
cloud-securitycommand-and-controlencryption-decryption-tools+6
4216 days ago
APT-Individual-Combat-Guide preview

APT-Individual-Combat-Guide

GitHubghostwolflab/apt-individual-combat-guide

Educational guide and code repository for understanding APT attack techniques, covering reconnaissance, web and service exploitation, trojans, C2,…
command-and-controleducationexploitation+7
11010 months ago
SliverMirage preview

SliverMirage

GitHubdaniomass/slivermirage

Crystal Palace PICO loader for Sliver C2 dual-layer AMSI bypass, ETW silencing, AES-256-CBC encrypted payloads, 6 delivery variants
binary-analysiscommand-and-controlexploitation+4
441 month ago
Mythic preview

Mythic

GitHubits-a-feature/mythic

A collaborative, multi-platform, red teaming framework

command-and-controldata-exfiltrationexploitation+9
4.8k18 days ago
Previous12…20Next