-LogicSentry-AI
 vighnesh91/-logicsentry-ai
Offline SAST/DAST triage engine that parses source code and replays HAR traffic to detect business-logic flaws, BOLA, race conditions, and privilege…
ai-securityapi-security-testingcode-analysis+9
1
vighnesh91/-logicsentry-aiOffline SAST/DAST triage engine that parses source code and replays HAR traffic to detect business-logic flaws, BOLA, race conditions, and privilege…
 shoucheng3/x-stream__xstream_cve-2021-21345_1-4-15
Java XML serialization library with a focus on CVE-2021-21345 exploit analysis and deserialization vulnerability testing for web applications.
 cloudflare/security-audit-skill
A coding-agent skill for multi-phase security audits with independently verified, machine-readable findings
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 lolcaken/javascript-deobfuscator
Deobfuscator for javascript-obfuscator 5.x output (string arrays, control-flow flattening, self-defending, RC4/base64)
 tomnomnom/gf
A wrapper around grep, to help you grep for things
 byt3bl33d3r/offensivedlr
Toolbox containing research notes & PoC code for weaponizing .NET's DLR
 smackers/smack
Modular software verification toolchain that translates LLVM IR into Boogie intermediate verification language for bounded and experimental unbounded…
 lifting-bits/sleigh
CMake build of Ghidra's SLEIGH processor specification library, providing standalone disassembly and p-code lifting engines for reverse engineering…
 we5ter/flerken
A Solution For Cross-Platform Obfuscated Commands Detection presented on CIS2019 China. 动静态Bash/CMD/PowerShell命令混淆检测框架 - CIS 2019大会
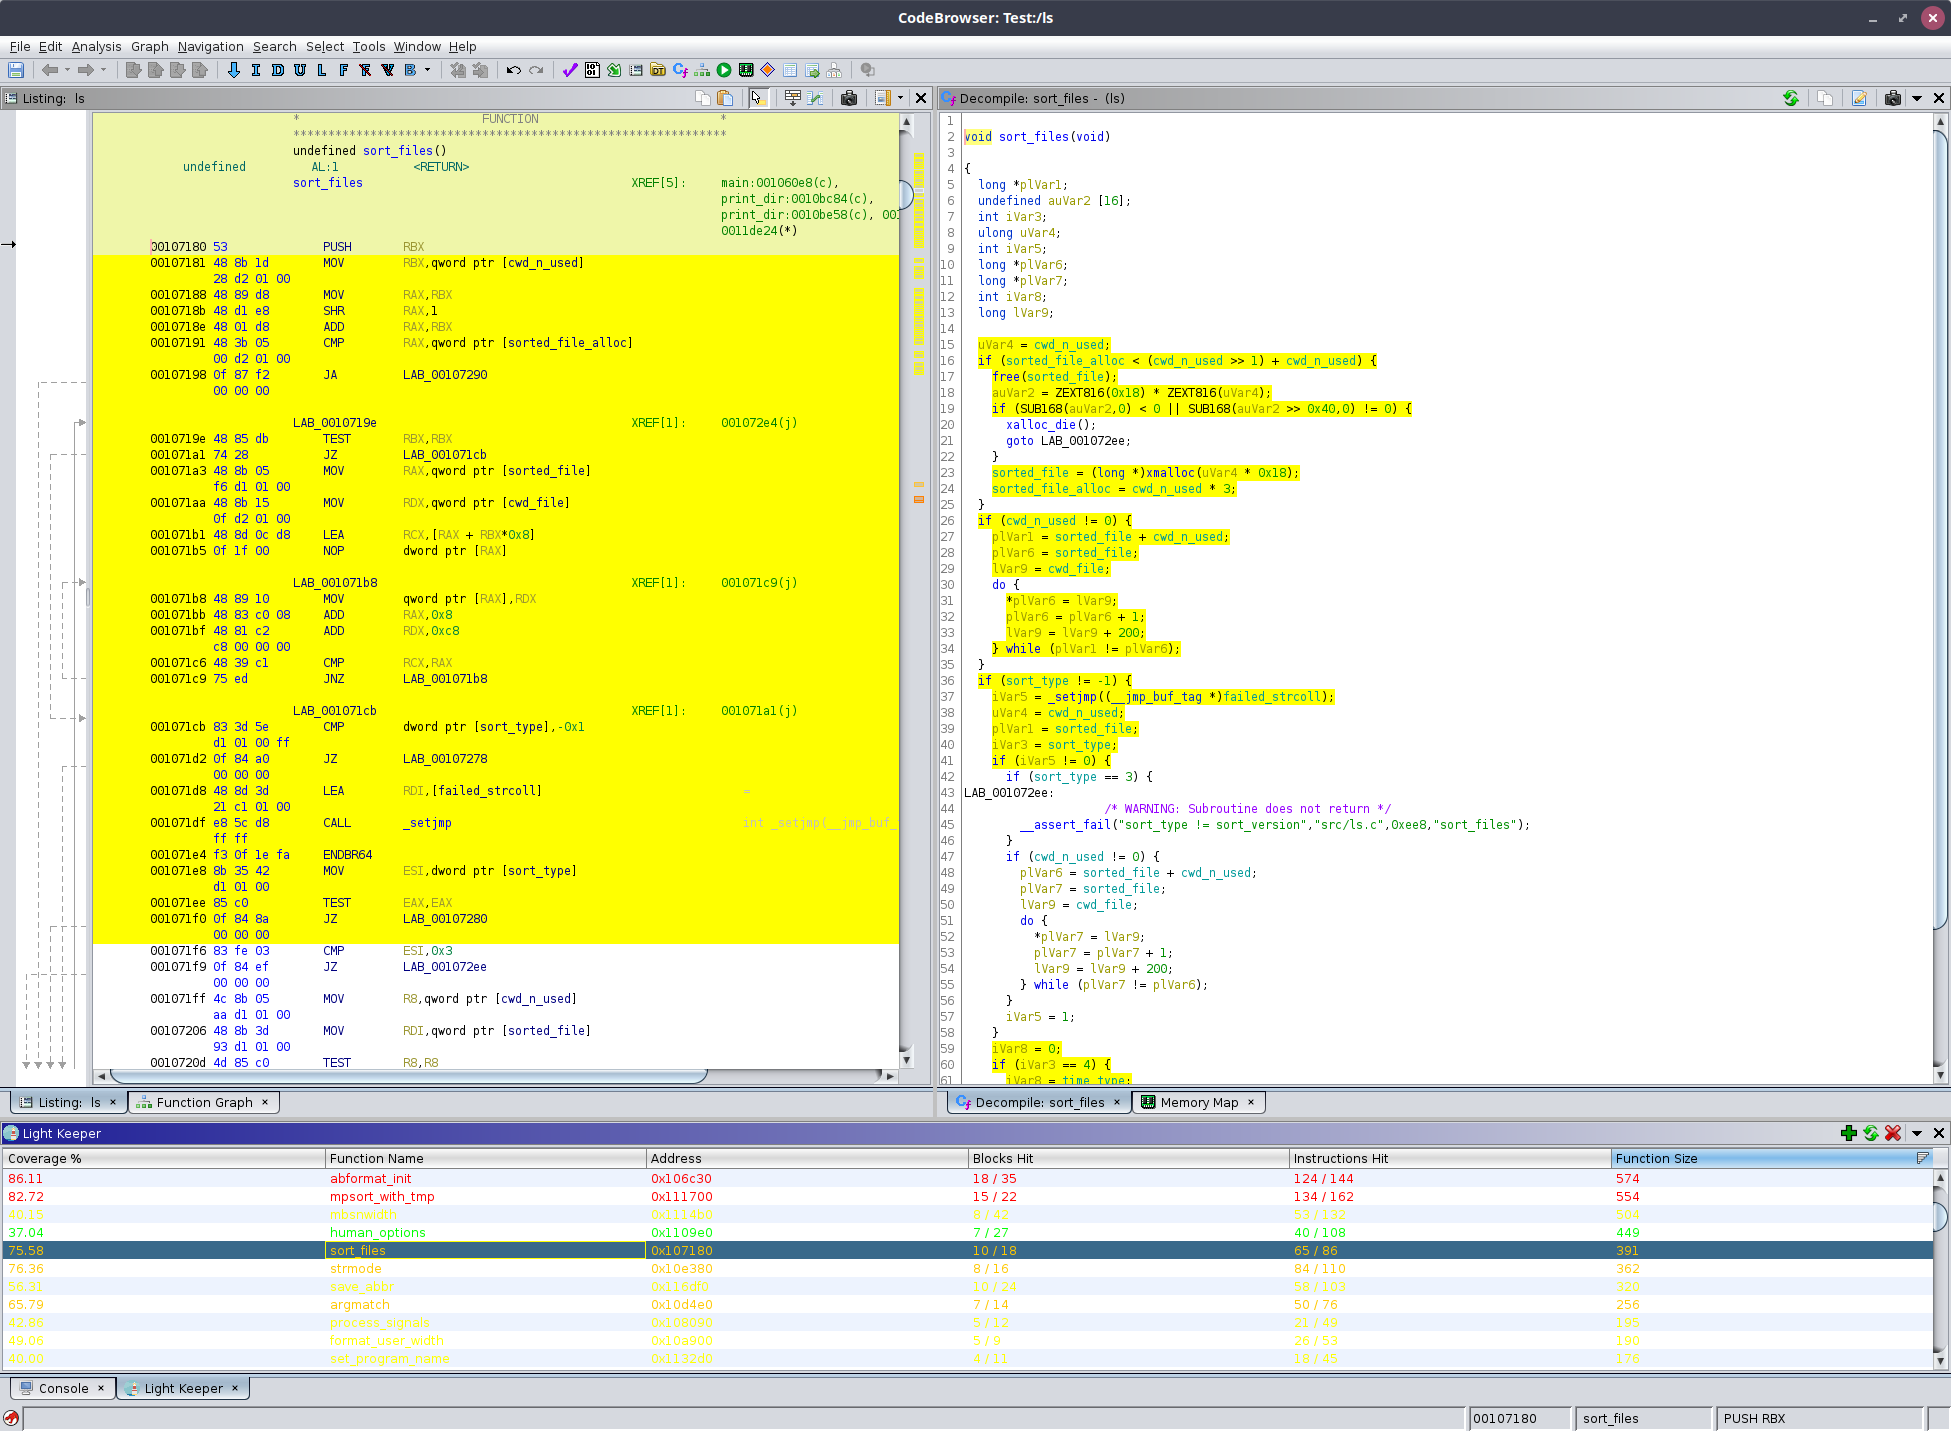 worksbutnottested/lightkeeper
Maps execution-coverage data onto Ghidra disassembly to highlight visited code paths and accelerate reverse-engineering workflows.
 r00tkitsmm/pishi
Pishi is a code coverage tool like kcov for macOS.
 jpiechowka/jenkins-cve-2016-0792
Exploit for Jenkins serialization vulnerability - CVE-2016-0792
 binsec/xyntia
Xyntia, the black-box deobfuscator
 ejfkdev/jscd
Reverse bytenode .jsc (V8 code cache) to JavaScript — static, pure Rust, no patched V8/Node. Node 8→26 / V8 5.8–14.6; 25k .jsc tested, 0 fail.
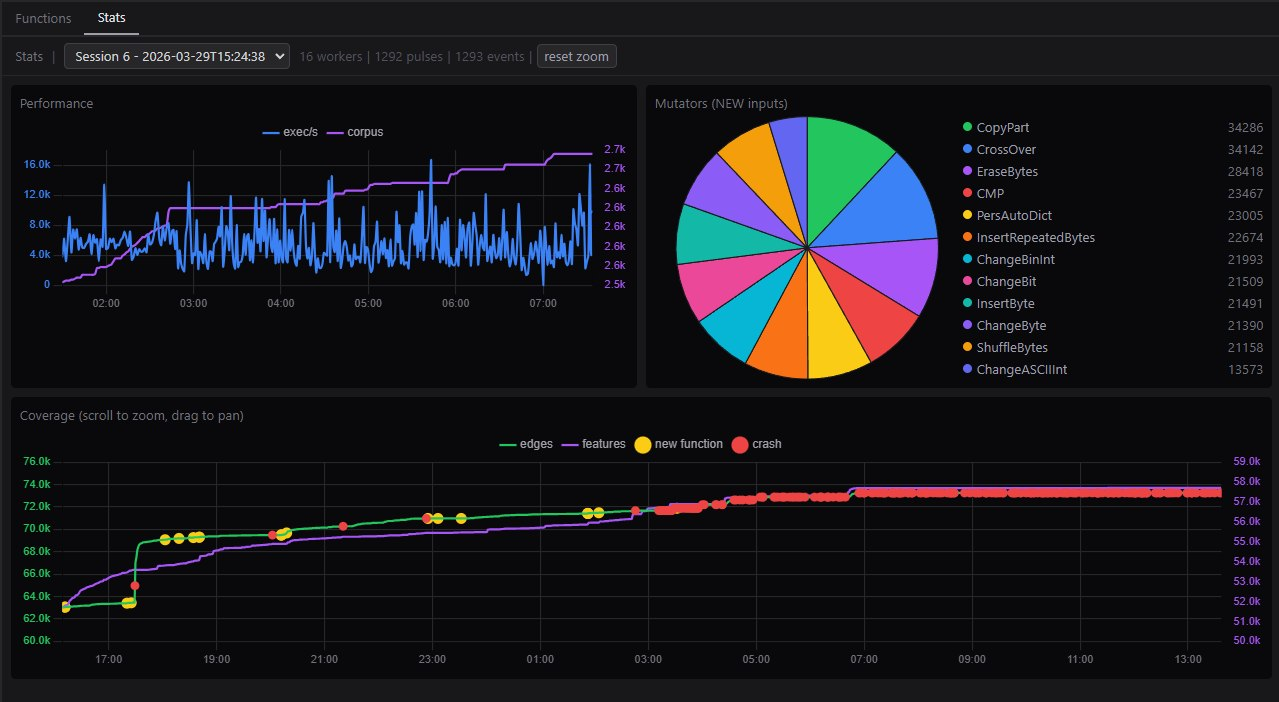 0xbigshaq/apatchy
Fuzzing Framework for Modules in Apache HTTPD Server
 hupe1980/cve-2021-3129
Laravel debug mode - Remote Code Execution (RCE)