EXPLOIT-CVE-2026-8832-

Automated RCE exploit for WordPress WPCode Lite v2.3.5. Executes 6-step exploitation chain via XML-RPC bypass with 8 built-in PHP payloads, including…

Automated RCE exploit for WordPress WPCode Lite v2.3.5. Executes 6-step exploitation chain via XML-RPC bypass with 8 built-in PHP payloads, including…

Exploit for CVE-2025-28915: WordPress ThemeEgg ToolKit arbitrary file upload vulnerability allowing remote Web Shell deployment. Includes…

Proof-of-concept for authenticated remote code execution in ClipBucket via PHP code injection in update_launch.php. Includes web shell deployment and…

Unauthenticated 0-click RCE exploit for CVE-2024-9932. Exploits an arbitrary file upload vulnerability in the Wux Blog Editor WordPress plugin to…

Proof-of-concept exploit for authenticated PHP code injection in ISPConfig <= 3.2.11, enabling remote code execution via unsanitized language file…

Pluck v4.7.18 - Remote Code Execution (RCE)

Proof-of-Concept exploit for Apache Struts S2-052 (CVE-2017-9805) XML Deserialization Remote Code Execution. Created while solving the INE eWPTX…

Shell scripts to clone and mirror Git repositories, compute deltas, and run gitleaks to detect secrets hidden in deleted or reset commits.

Jenkins POC of Arbitrary file read vulnerability through the CLI can lead to RCE

Automated RCE exploit for WordPress WPCode Lite v2.3.5 (CVE-2026-8832) with 8 built-in PHP payloads, XML-RPC bypass, and web-based interactive shell…

CVE-2023-30253 — Dolibarr ERP/CRM 17.0.0 RCE via PHP code injection (exploit educativo)

Proof-of-concept exploit for unauthenticated remote code execution in SPIP < 4.2.1 via PHP object injection in the password reset form. Provides…

Exploit script for CVE-2021-22204, an ExifTool RCE via malicious DjVu files, with manual exploitation steps and reverse shell payloads.

CVE-2026-48909 - Unauthenticated PHP Object Injection to RCE exploit for Joomla SP LMS extension versions <= 4.1.3. Exploits lmsOrders cookie…

Authenticated remote code execution exploit for Roundcube Webmail (CVE-2025-49113) via insecure deserialization. Includes session injection, gadget…

Python-based RCE exploit for CVE-2026-42588 targeting Apache ActiveMQ Jolokia. Features check-only mode, malicious XML generation, and support for…

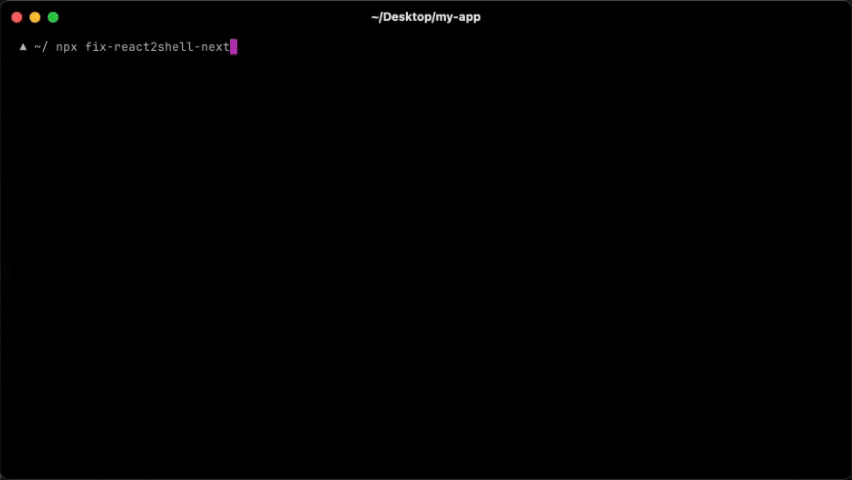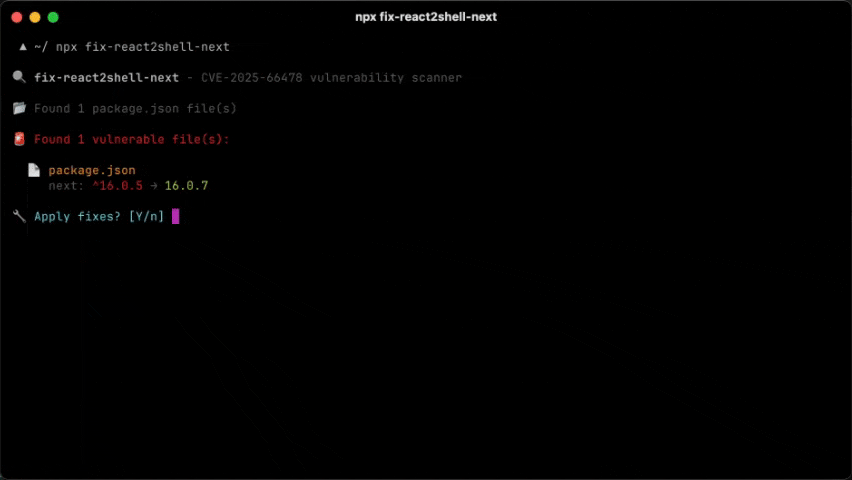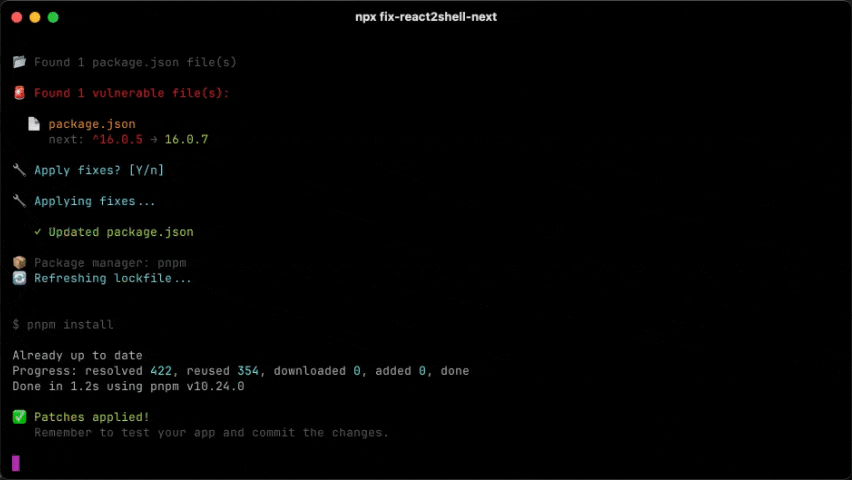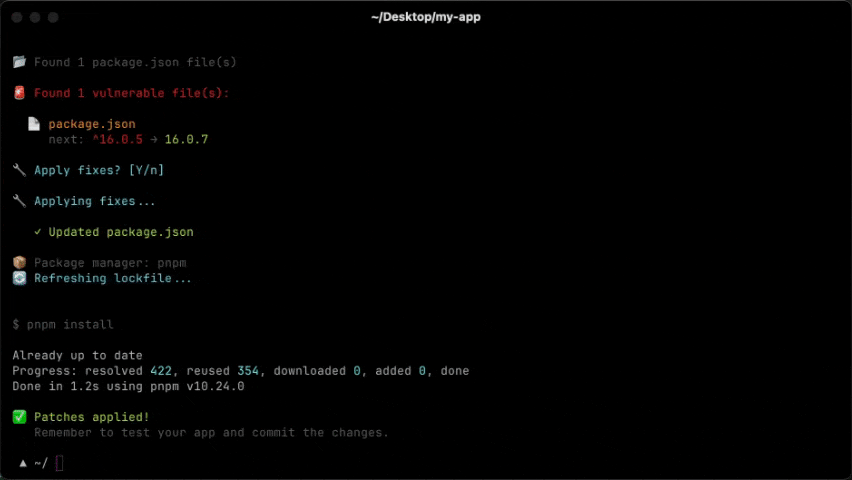
One command to fix CVE-2025-66478 (React 2 Shell RCE) in your Next.js / React RSC app.

A lightweight security auditor and sandbox for shell scripts. Oversight combines a Static Analysis engine (Rust) with Dynamic Enforcement (Linux…