
CVE-2026-2964-Lab
 thegenetic/cve-2026-2964-lab
Educational lab demonstrating CVE-2026-2964, a prototype pollution vulnerability in web-audio-recorder-js leading to RCE. Includes vulnerable and…
code-analysiseducationexploitation+4
thegenetic/cve-2026-2964-labEducational lab demonstrating CVE-2026-2964, a prototype pollution vulnerability in web-audio-recorder-js leading to RCE. Includes vulnerable and…
 whgojp/javaseclab
Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
 paolorabbito/internet-security-project---cve-2021-26814
Educational exploit demonstration for CVE-2021-26814 targeting Wazuh v4.0.3, with step-by-step exploitation and remediation code for university-level…
 masahiro331/cve-2020-8277
Proof-of-concept exploit for CVE-2020-8277, a Node.js DNS resolver denial-of-service vulnerability triggered by large record responses, with…
 sakib570/cve-2018-1263-demo
Educational exploit demo for CVE-2018-1263 (phpMyAdmin RCE/LFI). Includes vulnerable environment setup via Docker and step-by-step attack walkthrough…
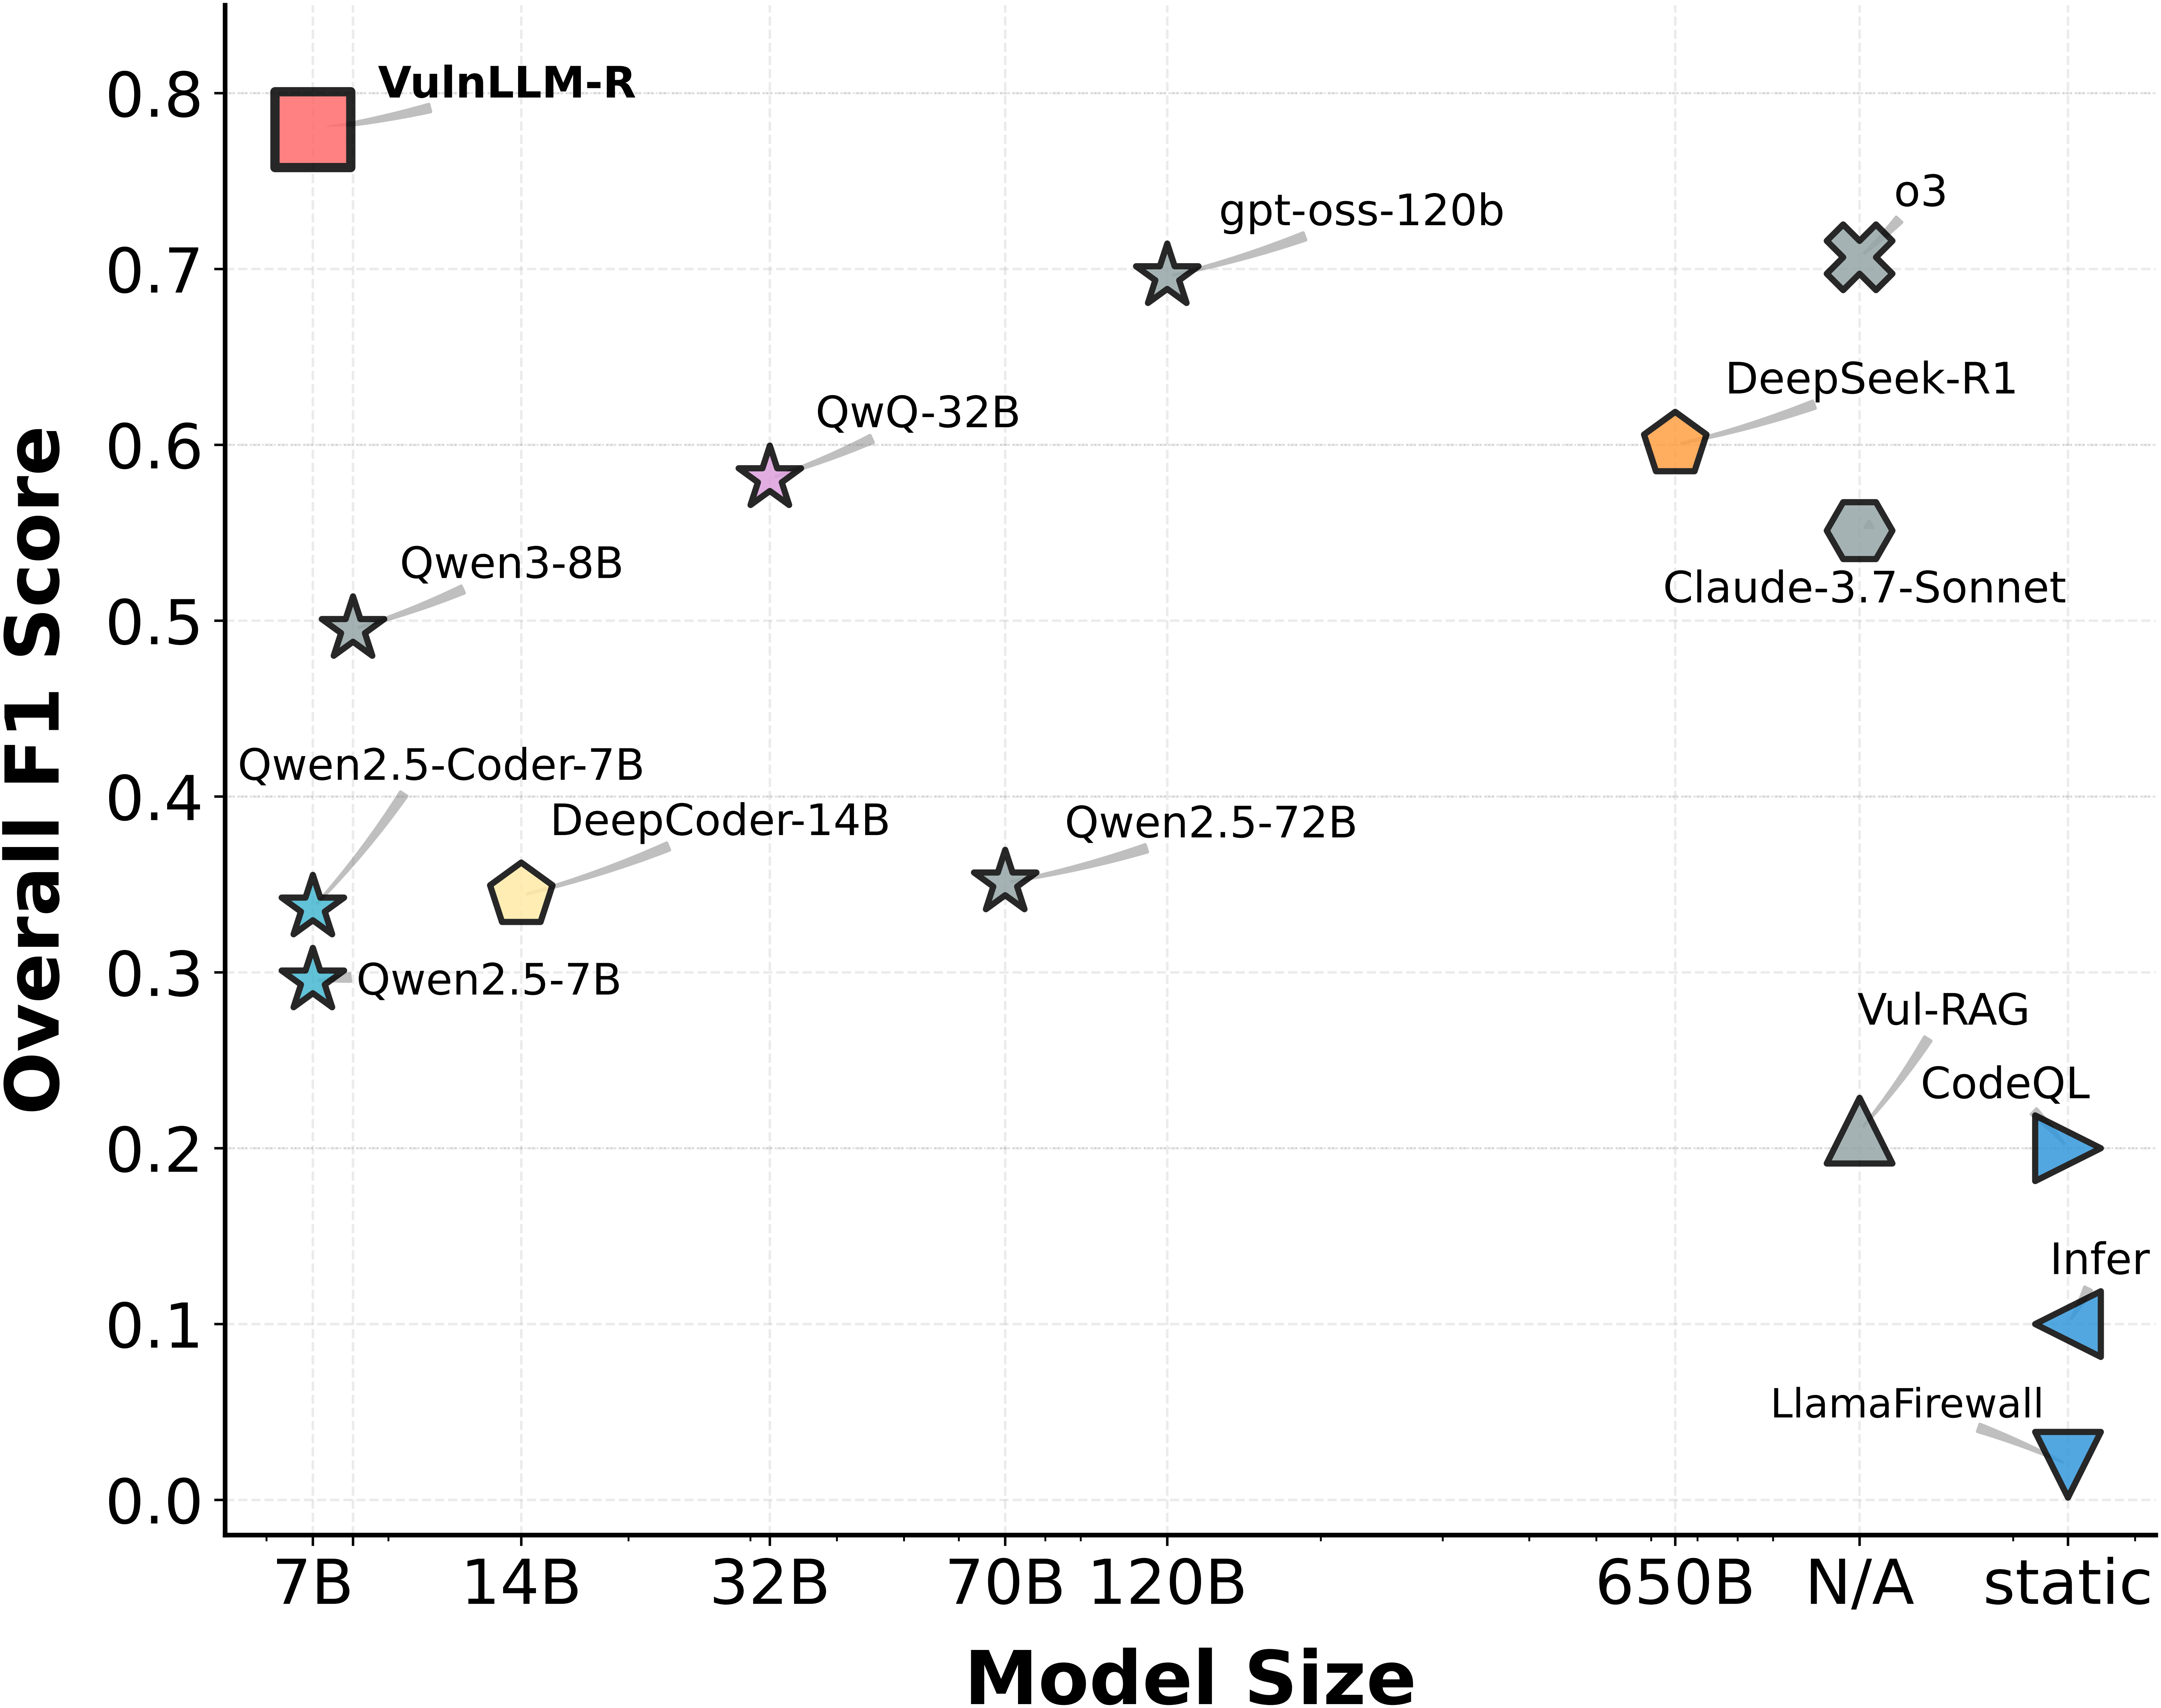 ucsb-mlsec/vulnllm-r
Specialized reasoning LLM for source-code vulnerability detection in C/C++ and Python, with dataset construction, SFT/DPO training, and…
 li8u99/spring-data-mongodb-demo
Demo environment for CVE-2022-22980 (Spring Data MongoDB SpEL injection RCE) with vulnerable application code for security testing and education.
 jaytarr-geo/nextjs-lodash-cve-2025-13465-repro
Reproduction environment for CVE-2025-13465, demonstrating a vulnerability in Next.js applications using Lodash. Provides a minimal setup to test and…
 gitguardian/ggshield
Detect and validate 500+ types of hardcoded secrets with advanced checks. Use it as a pre-commit hook, GitHub Action, or CLI for proactive secret…
 fairyming/cve-2020-8840
PoC exploit for CVE-2020-8840: JNDI injection leading to remote code execution in FasterXML jackson-databind. Includes environment setup, exploit…
 cookiengineer/exocomp
Self-hosted multi-agent environment for Go with LLM-powered pentesting agents (exploiter, reverser, threathunter, webscanner) that automate…
 kuron3k0/spring-data-mongodb-example
Dockerized PoC environment for CVE-2022-22980 (Spring Data MongoDB SpEL injection) with a working exploit demonstrating remote code execution via…
 nyamort/cve-2024-52301
Proof-of-concept exploit for CVE-2024-52301 demonstrating environment manipulation in Laravel via injected URL parameters, with detailed code…
 ztcoalson/if-guide
[NeurIPS '25] Code for Paper "IF-Guide: Influence Function-Guided Suppression of Harmful Training Data for Reducing LLM Toxicity"
 nyamort/cve-2024-50340
Proof-of-concept exploit for CVE-2024-50340 demonstrating Symfony ArgvInput environment variable injection via crafted URL query parameters, enabling…
 cckuailong/cve-2021-2471
Maven-based reproduction environment for CVE-2021-2471, demonstrating JDBC SQLXML XXE exploitation with step-by-step guide and reference code.
 khidottrivi/cve-2022-22965
In-depth technical analysis of CVE-2022-22965 (Spring4Shell) with environment setup, debug walkthrough, and exploit chain breakdown for educational…
 endusdksla/xwiki-cve-2025-24893
Unauthenticated remote code execution exploit for XWiki SolrSearch (CVE-2025-24893) via Groovy injection in the text parameter, with Docker-based lab…