
cwe-tool
 owasp/cwe-tool
A command line CWE discovery tool based on OWASP / CAPSEC database of Common Weakness Enumeration.
code-analysiscurated-resourceseducation+3
owasp/cwe-toolA command line CWE discovery tool based on OWASP / CAPSEC database of Common Weakness Enumeration.
 owasp/cwe-sdk-javascript
A Common Weakness Enumeration (CWE) Node.js SDK compliant with MITRE / CAPEC
 0x00phantom-hat/cve-2026-5029-exploit
Proof-of-concept exploit for CVE-2026-5029, delivering unauthenticated remote code execution via the run-code MCP tool on exposed HTTP endpoints.…
 cerberusmrxi/cve-2026-44680-mikroorm-sql-injection-exploit-framework
PoC tool for CVE-2026-44680 affecting MikroORM ≤7.0.13. Exploits JSON path injection to extract database contents via UNION-based attacks. Features…
 jjk96/javaclasspathenum
Java classpath enumeration, focussed on CVE-2014-0043 for Apache Wicket 6.x
 cycodelabs/raven
Scans GitHub Actions CI/CD workflows for security vulnerabilities, indexes findings into a Neo4j graph database, and provides a query library for…
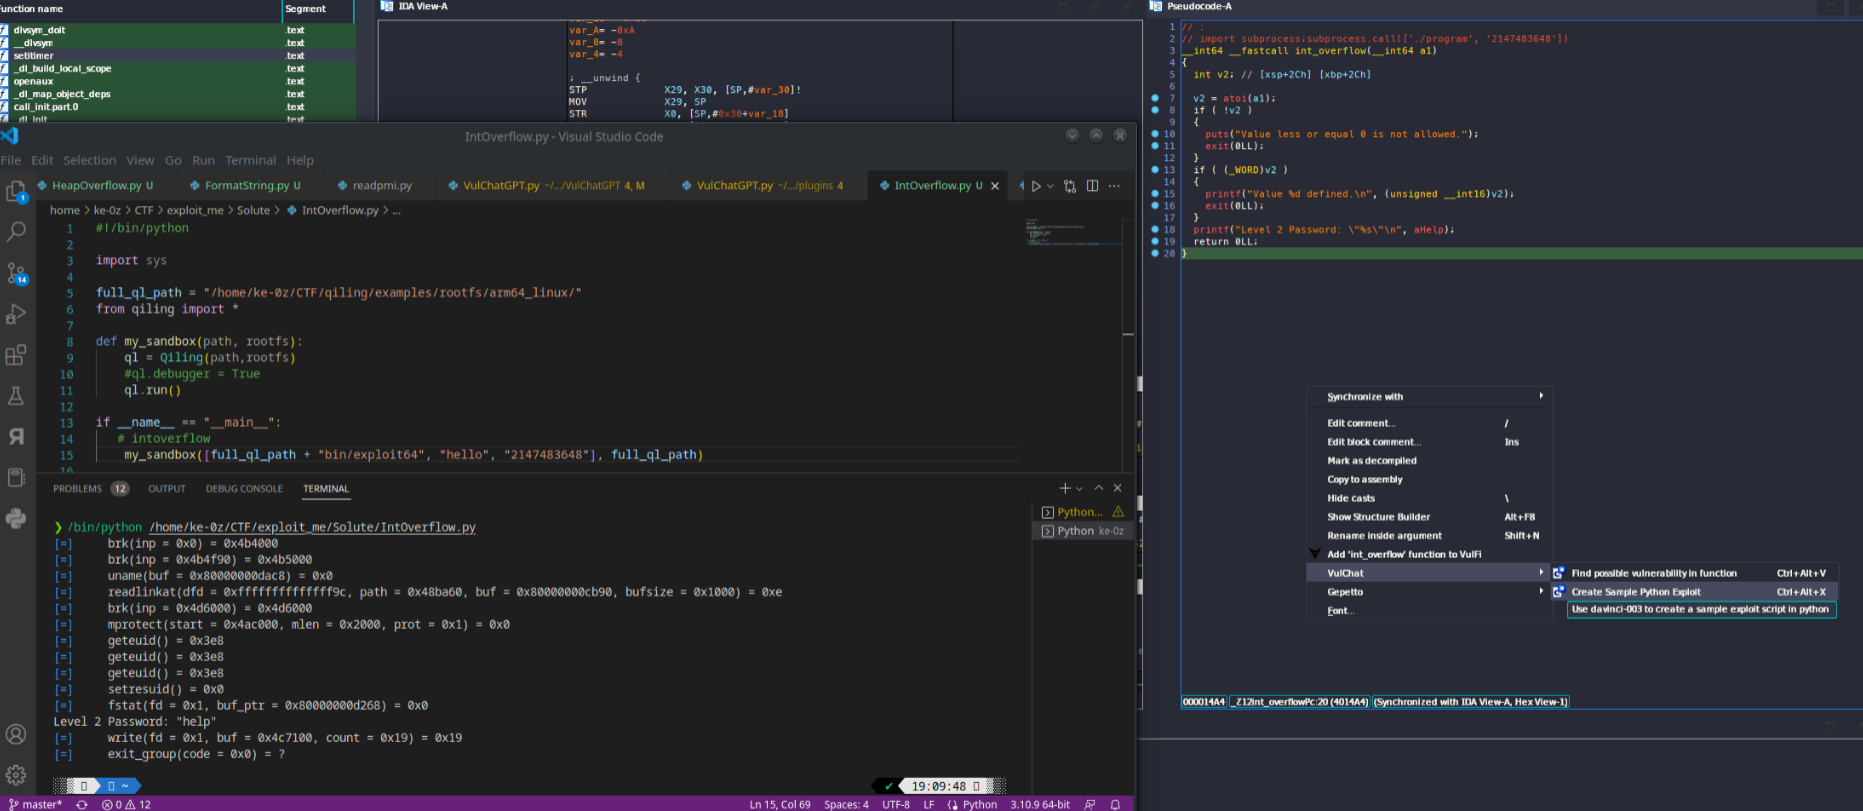 ke0z/binaivulhunter
Use IDA PRO HexRays decompiler with OpenAI(ChatGPT) to find possible vulnerabilities in binaries
 bishopfox/jsluice
Extract URLs, paths, secrets, and other interesting bits from JavaScript
 josehelps/git-wild-hunt
A tool to hunt for credentials in github wild AKA git*hunt
 soxoj/gitcolombo
🧬 Extract and analyze contributors info from git repos
 nightwatchcybersecurity/gitbleed_tools
Shell scripts to clone and mirror Git repositories, compute deltas, and run gitleaks to detect secrets hidden in deleted or reset commits.
 unkl4b/gitminer3
Tool for advanced mining for content on Github
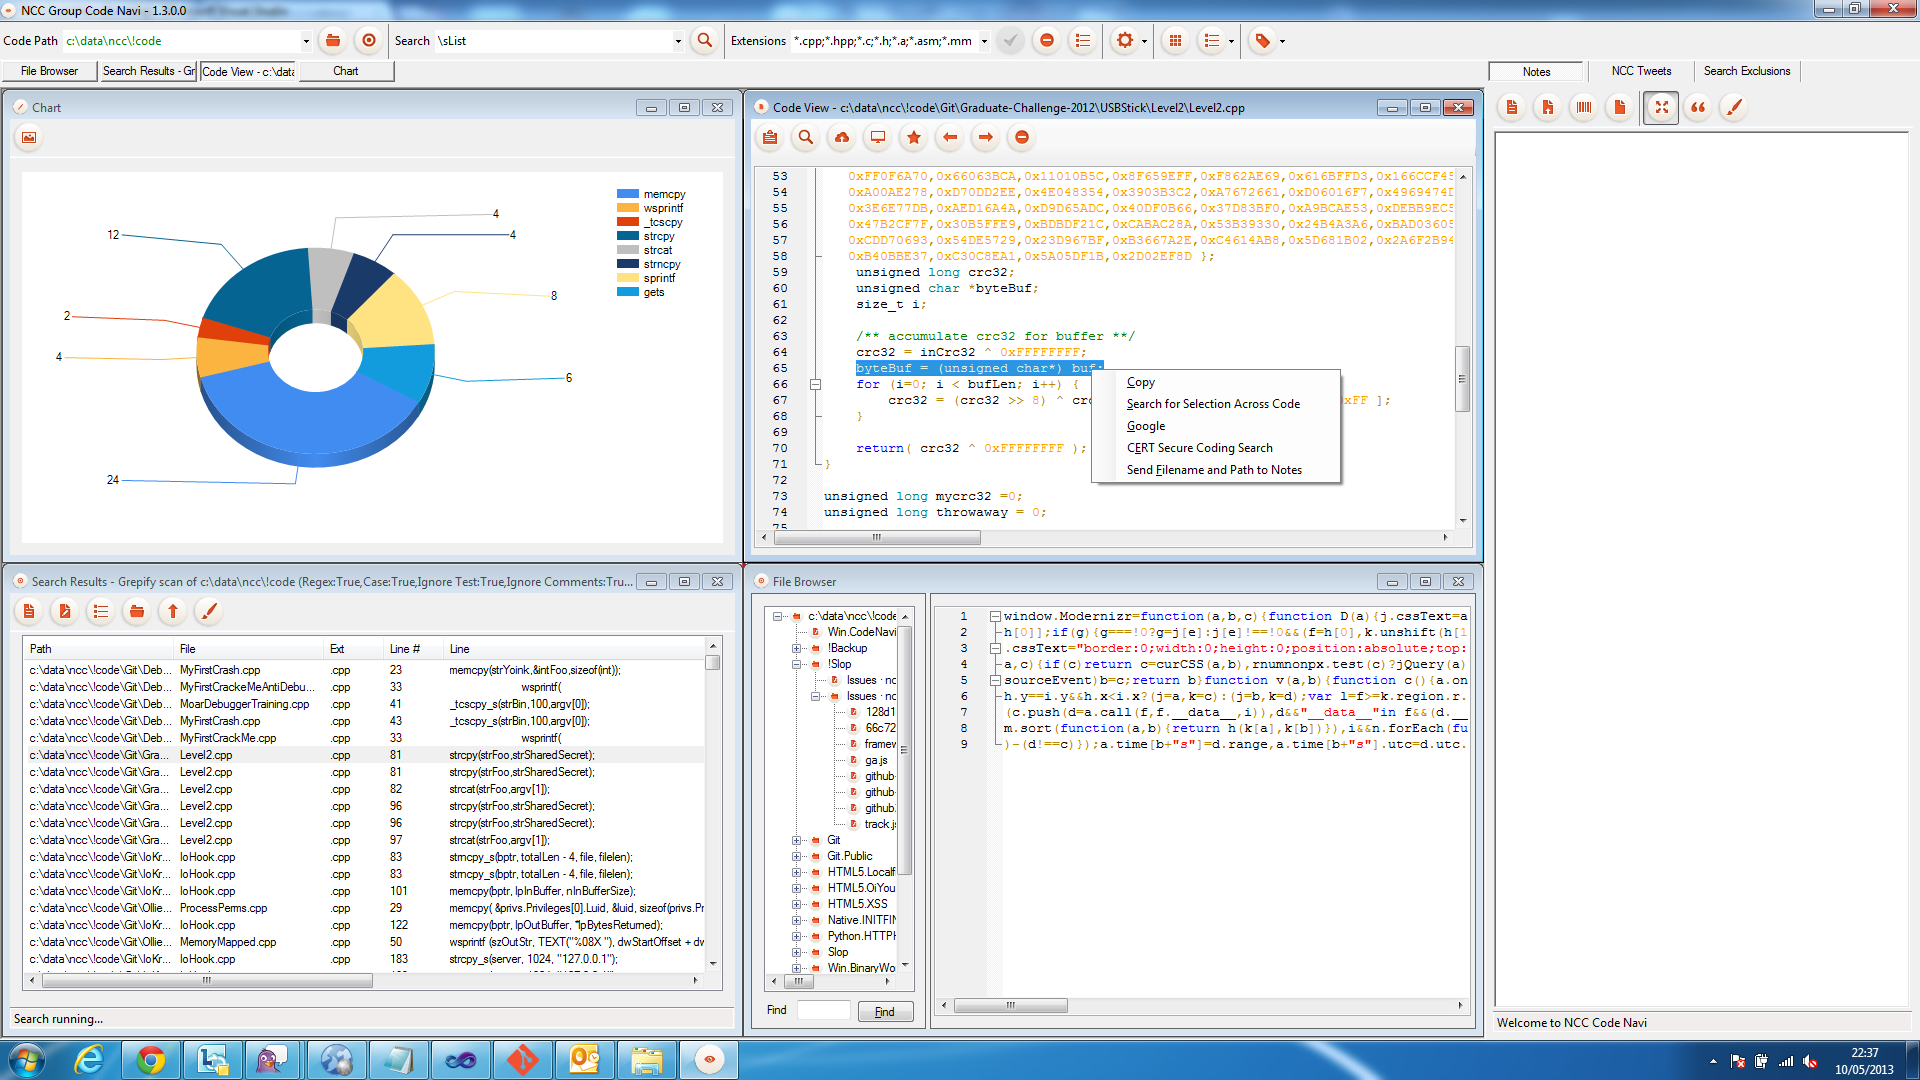 nccgroup/ncccodenavi
NCC Code Navigator
 atmoner/githubfind3r
Command-line tool for fast searching of GitHub repositories, users, and commits to gather open-source intelligence and code-related information.
 josue87/givemesecrets
Use regular expressions to get sensitive information from a given repository (GitHub, pip or npm).
 raoufmaklouf/jsecret
Fast Go-based static scanner for detecting sensitive data (API keys, tokens, passwords) in JavaScript files and source code using regex patterns.
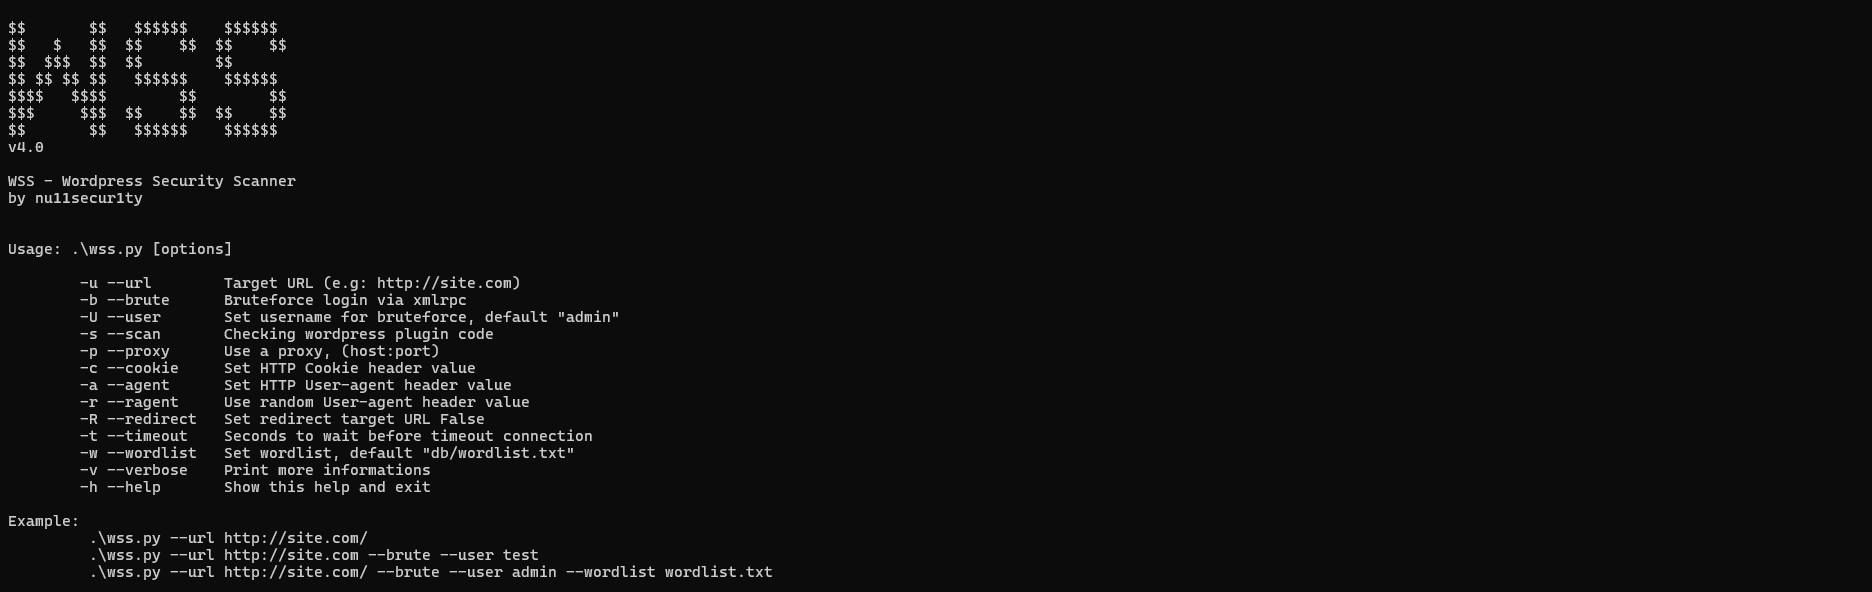 nu11secur1ty/wss
Black-box WordPress vulnerability scanner that detects security issues, enumerates users, brute-forces logins via XMLRPC, and performs static PHP…
 nurjaman2004/jspdf-bulk-detector-cve-2025-68428-
Asset-wide detection tool for identifying jsPDF usage related to CVE-2025-68428 Detection only — no exploitation