

PurpleLlama
 meta-llama/purplellama
Set of tools to assess and improve LLM security.
adversarial-attackai-securitycode-analysis+4
4.4k18h 46m ago
meta-llama/purplellamaSet of tools to assess and improve LLM security.
 timtimxs/cve-2026-51947-advisory
Pivotal CRM's patch for an initial deserialization vulnerability was incomplete. The fix switched from BinaryFormatter to JSON.NET but left…
 mkway/cve-2025-57833
We've set up an environment to test CVE-2025-57833. This environment was built using AI, so it's subject to ongoing modification.
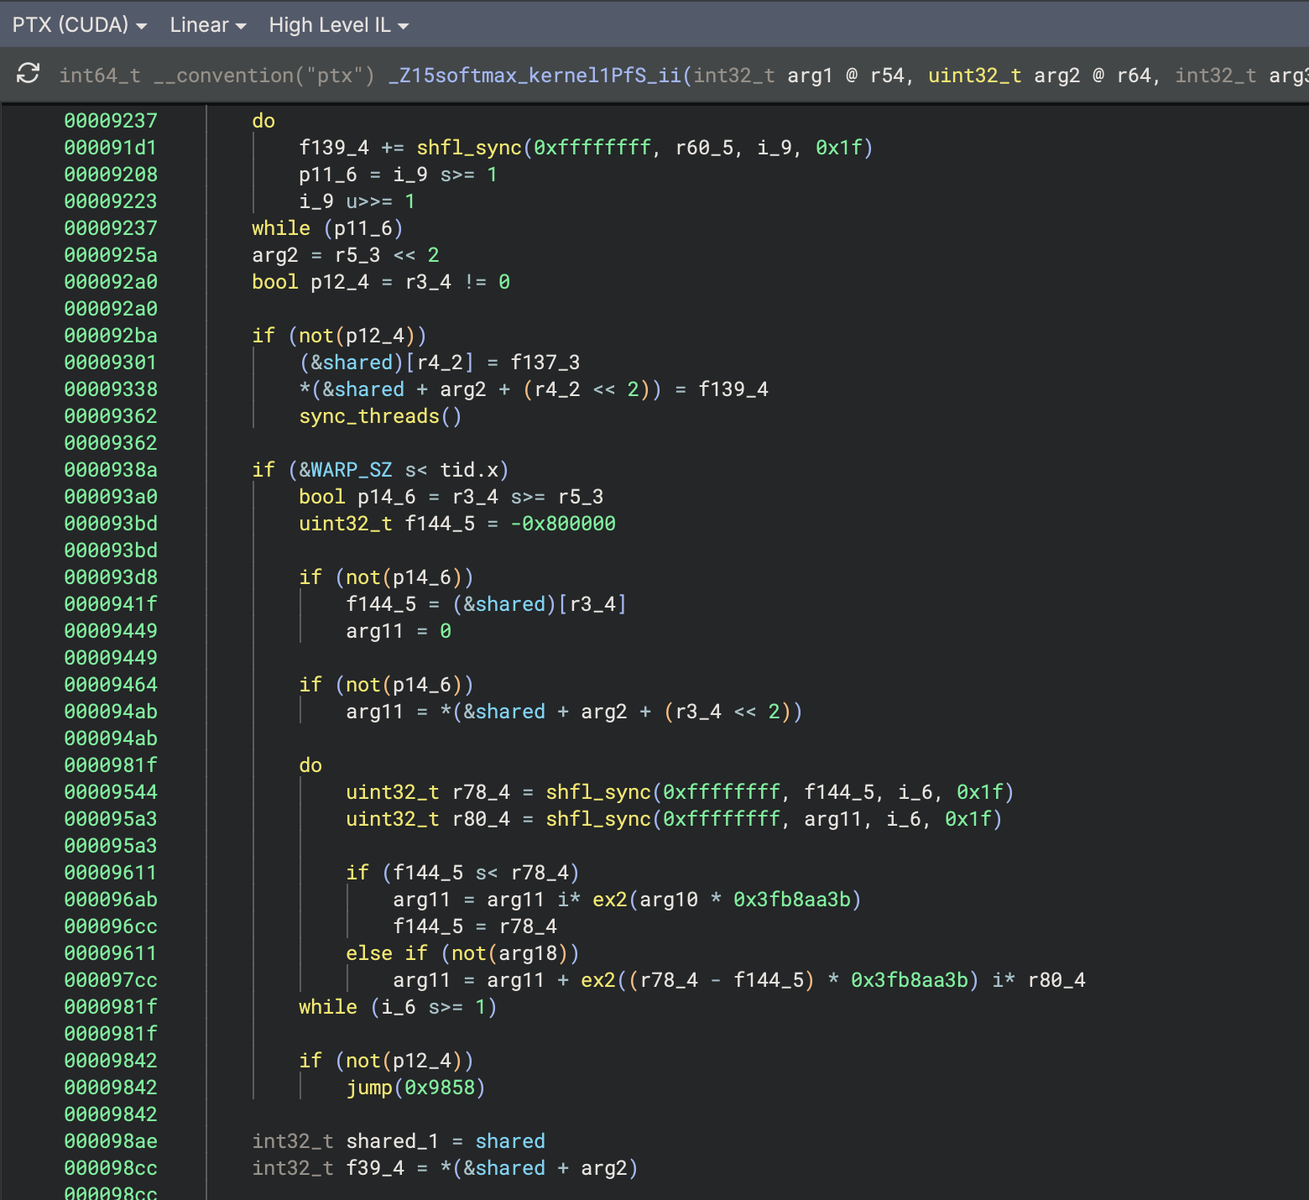 seekbytes/ptxninja
Binary Ninja plugin for reverse engineering PTX -- the virtual instruction set architecture of CUDA-based GPUs.
 cmatthewbrooks/r2kit
A set of scripts for a radare-based malware code analysis workflow
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
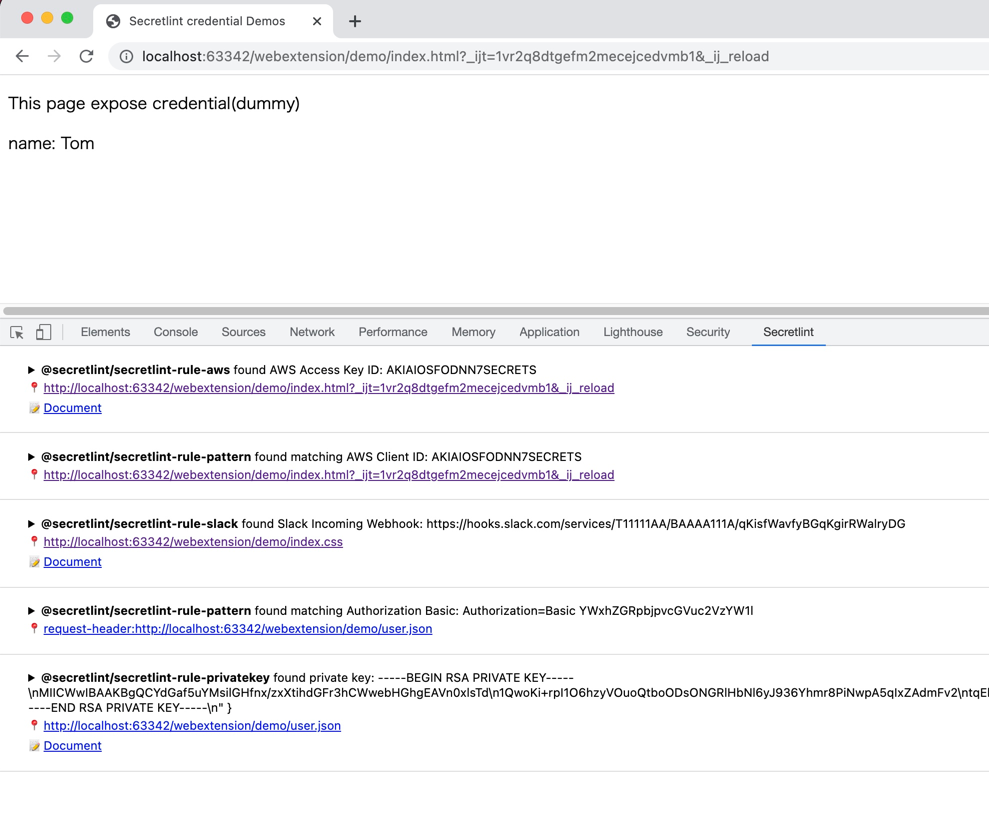 secretlint/secretlint
Pluggable linting tool to prevent committing credential.
 mistymntncop/cve-2023-4863
Proof-of-concept for CVE-2023-4863, a heap buffer overflow in WebP image decoding. Demonstrates the code_lengths trigger mechanism discovered by…
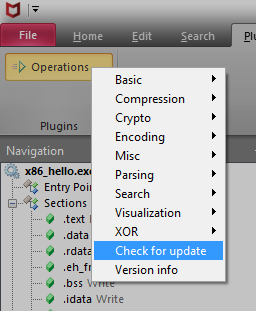 nmantani/fileinsight-plugins
FileInsight-plugins: decoding toolbox of McAfee FileInsight hex editor for malware analysis
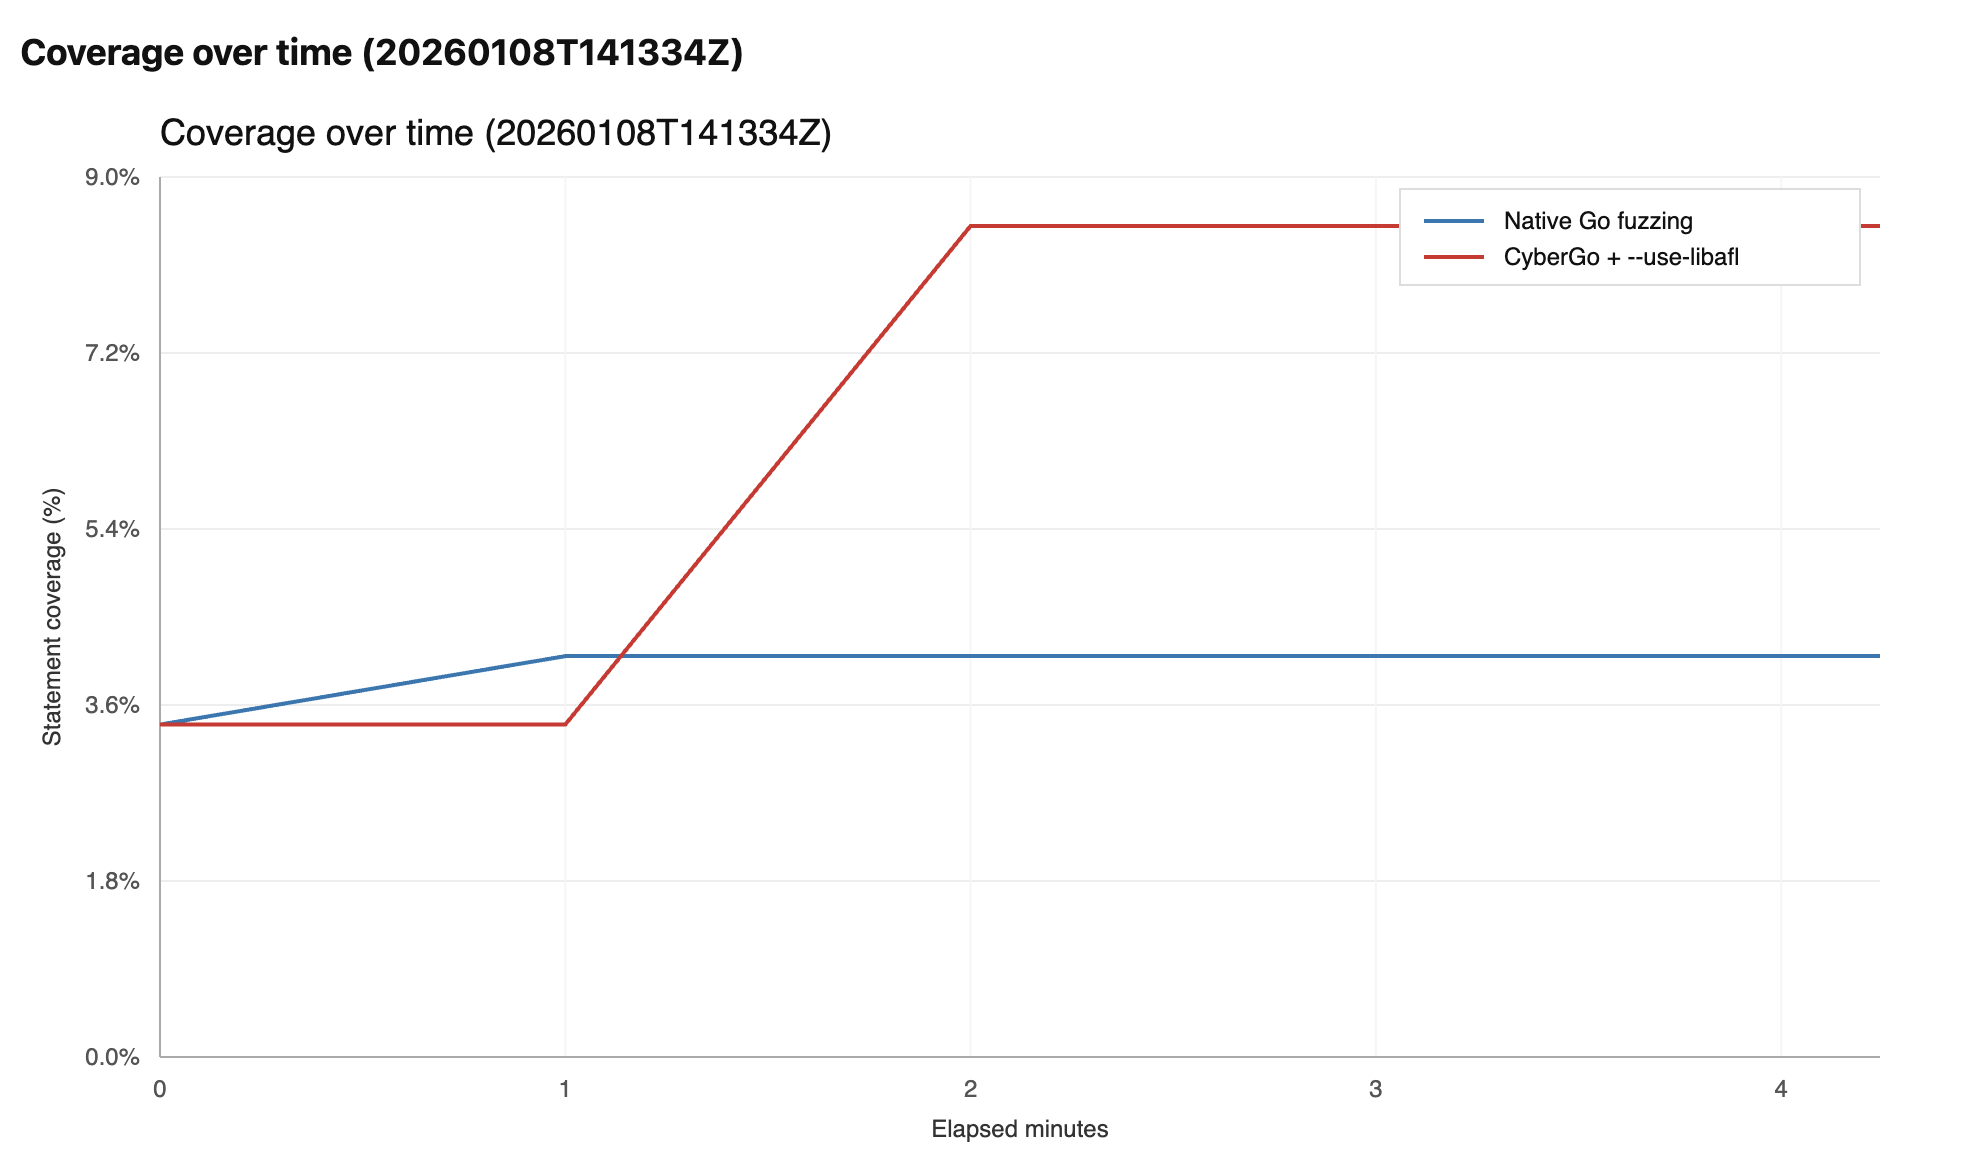 trailofbits/gosentry
Security-oriented Go toolchain, focused on state-of-the-art fuzzing capabilities.
 wolfssl/wolfcose
A fast, portable, and lightweight COSE + CBOR implementation for embedded systems. Supports PQC, FIPS 140-3, DO-178, and MISRA C. Powered by wolfSSL.
 owasp/tcasvs
OWASP Thick Client Application Security Verification Standard
 grantzile/poc-cve-2024-33883
PoC of CVE-2024-33883, RCE vulnerability of ejs.
 nanda-rani/safe
A contextual security auditing system for research artifacts
 kevinbackhouse/djvulibre-poc-cve-2025-53367
Proof-of-concept exploit for CVE-2025-53367, a vulnerability in the DjVuLibre library. Demonstrates exploitation of a memory corruption bug in DjVu…
 shoucheng3/joniles__mpxj_cve-2020-35460_8-3-4
Exploit for CVE-2020-35460 targeting MPXJ project management library, enabling arbitrary code execution via crafted project files in Java, .Net, and…
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)