

CVE-2020-26259
 jas502n/cve-2020-26259
CVE-2020-26259: XStream is vulnerable to an Arbitrary File Deletion on the local host when unmarshalling as long as the executing process has…
code-analysisexploitationpenetration-testing+2
25
jas502n/cve-2020-26259CVE-2020-26259: XStream is vulnerable to an Arbitrary File Deletion on the local host when unmarshalling as long as the executing process has…
 shoucheng3/apache__uima-uimaj_cve-2022-32287_3-3-0
Java SDK for building analytics pipelines that process and enrich unstructured text data with annotations, type systems, and modular analysis engines.
 google/enjarify
Translates Dalvik bytecode (DEX/APK) to equivalent Java bytecode, enabling Java analysis tools to process Android applications with high correctness…
 gmh5225/iat-hook
C++ DLL that performs Import Address Table hooking by parsing PE headers and redirecting imported function addresses to a custom hook inside a target…
 byt3bl33d3r/offensivenim
My experiments in weaponizing Nim (https://nim-lang.org/)
 googleprojectzero/tinyinst
A lightweight dynamic instrumentation library
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 santhreal/keyhog
Open-source secret scanner in Rust
 coffeeandsecurity/dakshscra
Framework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…
 sadopc/machscope
All-in-one macOS binary analysis: Mach-O parsing, ARM64 disassembly, code signatures, and debugging.
 mr-xn/cve-2022-24086
CVE-2022-24086 about Magento RCE
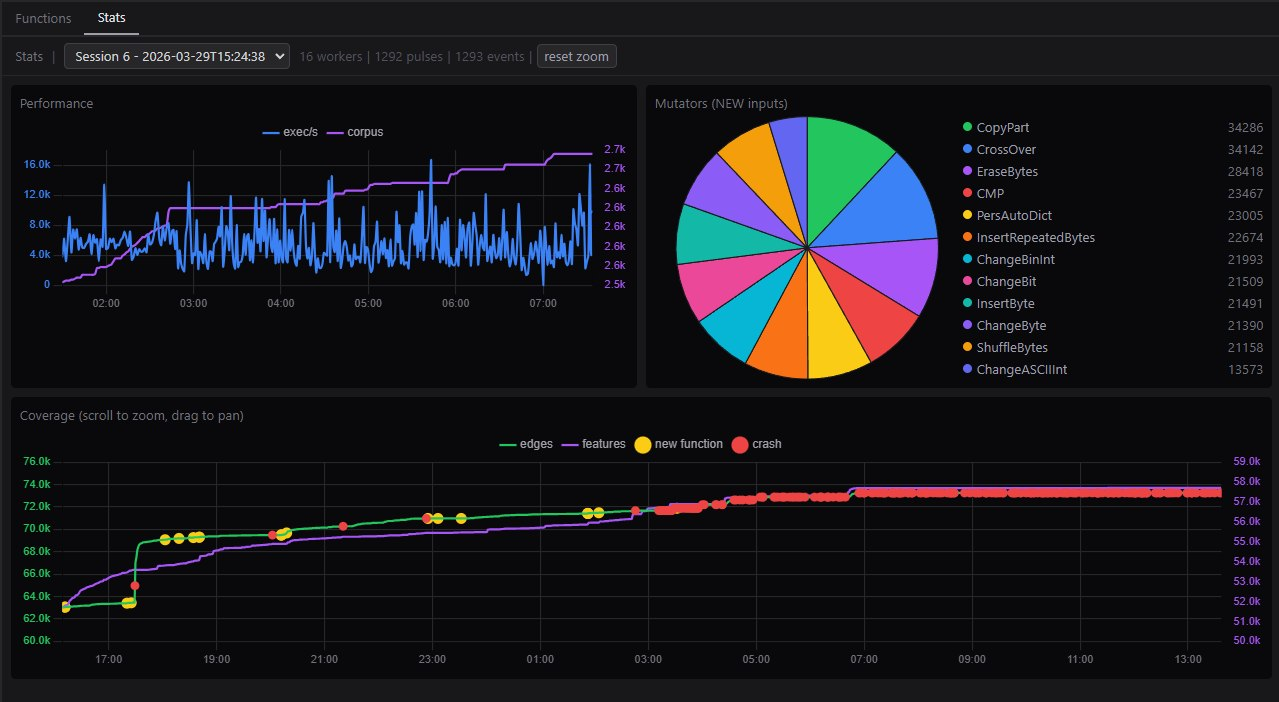 0xbigshaq/apatchy
Fuzzing Framework for Modules in Apache HTTPD Server
 murphysecurity/libwebp-checker
A tool for finding vulnerable libwebp(CVE-2023-4863)
 theopaid/cve-2026-66749-unchecked-room-lookup-leads-to-server-crash-let-s-chat-
Security Advisory: Unchecked Room Lookup Leads to Server Crash (Let's Chat)
 gmh5225/0xguard
Simple Anti-cheat library for applications that use C++ on windows. #PastedProtection
 al1ex/cve-2020-26259
CVE-2020-26259 &&XStream Arbitrary File Delete
 ducducuc111/cve-2025-55182-poc
Proof-of-concept exploit for CVE-2025-55182, demonstrating remote code execution via prototype chain vulnerability in React Server Components.…
 kov404/cve-2025-52385
Studio 3T v.2025.1.0