
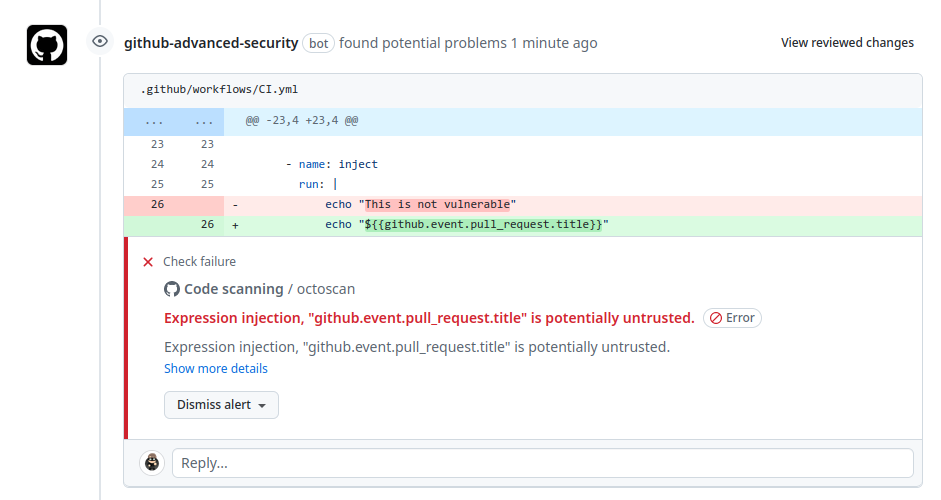
octoscan
 synacktiv/octoscan
Octoscan is a static vulnerability scanner for GitHub action workflows.
code-analysisconfiguration-auditingdevsecops+5
synacktiv/octoscanOctoscan is a static vulnerability scanner for GitHub action workflows.
 olacabs/jackhammer
Jackhammer - One Security vulnerability assessment/management tool to solve all the security team problems.
 faloker/purify
All-in-one tool for managing vulnerability reports from AppSec pipelines
 smxlabs/lamma-beta
Vulnerability Assessment and Auditing Framework for all the Crypto Implementations.
 dpomnean/log4j_scanner_wrapper
log4j vulnerability wrapper scanner for CVE-2021-44228
 ekamsinghwalia/openssl-vulnerability-detection-script
This is an OpenSSL Vulnerability Detection Script for CVE-2022-2274
 tlwebdesign/joomla-3.10.12-languagehelper-hotfix
Plugin to fix security vulnerability CVE-2023-40626 in Joomla 3.10.12
 rashedhasan090/aegisjava
I have created AegisJava, a tool to fix (detect and mitigate) CVE-2025-30749.
 sh00bx/cve-2025-4615
cve-2025-4615 poc & deep dive
 0sec-labs/foxguard
A fast universal code security scanner, written in Rust. Batteries included: supports 14 languages, TUI for triage, secrets, post-quantum audits,…
 intrinsec/comission
White-box CMS security scanner that audits core, plugin, and theme versions, detects unauthorized modifications, and cross-references known…
 0xcyberstan/cve-2026-42533-config-scanner
Static config scanner that flags nginx configs vulnerable to the complex_value two-pass capture-clobbering bug (regex map + regex capture → heap…
 nationwide-group-oss/cryptoptic
CodeQL-based scanner that inventories cryptographic function calls across repositories and GitHub organizations, producing a Cryptographic Bill of…
 califio/ngxray
ngxray — nginx config security scanner
 kriskimmerle/wheelaudit
Python Wheel File Security Scanner — scan .whl files for security issues before installation. Detects path traversal (CVE-2026-24049), RECORD…
 simota/nginx-rift-scanner
Detect-only scanner for CVE-2026-42945 (NGINX Rift), a heap overflow in ngx_http_rewrite_module. Version detection + nginx.conf pattern analysis.…
 gagaltotal/cve-2026-42533-nginx
CVE-2026-42533 Nginx