
sast-scan
 shiftleftsecurity/sast-scan
Scan is a free & Open Source DevSecOps tool for performing static analysis based security testing of your applications and its dependencies. CI and…
cloud-securitycode-analysisconfiguration-auditing+6
883
shiftleftsecurity/sast-scanScan is a free & Open Source DevSecOps tool for performing static analysis based security testing of your applications and its dependencies. CI and…
 owasp/secure-agent-playbook
OWASP Secure Agent Playbook Project
 owasp/asst
OWASP ASST (Automated Software Security Toolkit) | A Novel Open Source Web Security Scanner.
 github/codeql
CodeQL: the libraries and queries that power security researchers around the world, as well as code scanning in GitHub Advanced Security
 traceforce/mcp-xray
Unified security scanner for MCP servers with config, pentest, and repo-scan modes. Generates SARIF reports for CI/CD integration, detects secrets,…
 oxsecurity/codetotal
Analyze any snippet, file, or repository to detect possible security flaws such as secret in code, open source vulnerability, code security,…
 ntanwir10/guardscan
100% Free & Open Source • Privacy-First Security Scanning and AI Code Review CLI
 ossf/scorecard
OpenSSF Scorecard - Security health metrics for Open Source
 anthropics/oss-scanner
Service that builds enrolled open-source repositories in isolated offline VMs and scans them for security vulnerabilities, emailing findings with…
 hxsecurity/dongtai
Open-source Interactive Application Security Testing (IAST) tool that passively instruments Java applications to detect vulnerabilities and…
 nuguardai/nuguard
opensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis
 mandiant/route-sixty-sink
Link sources to sinks in C# applications.
 soheilkhodayari/jaw
JAW: A Graph-based Security Analysis Framework for Client-side JavaScript
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
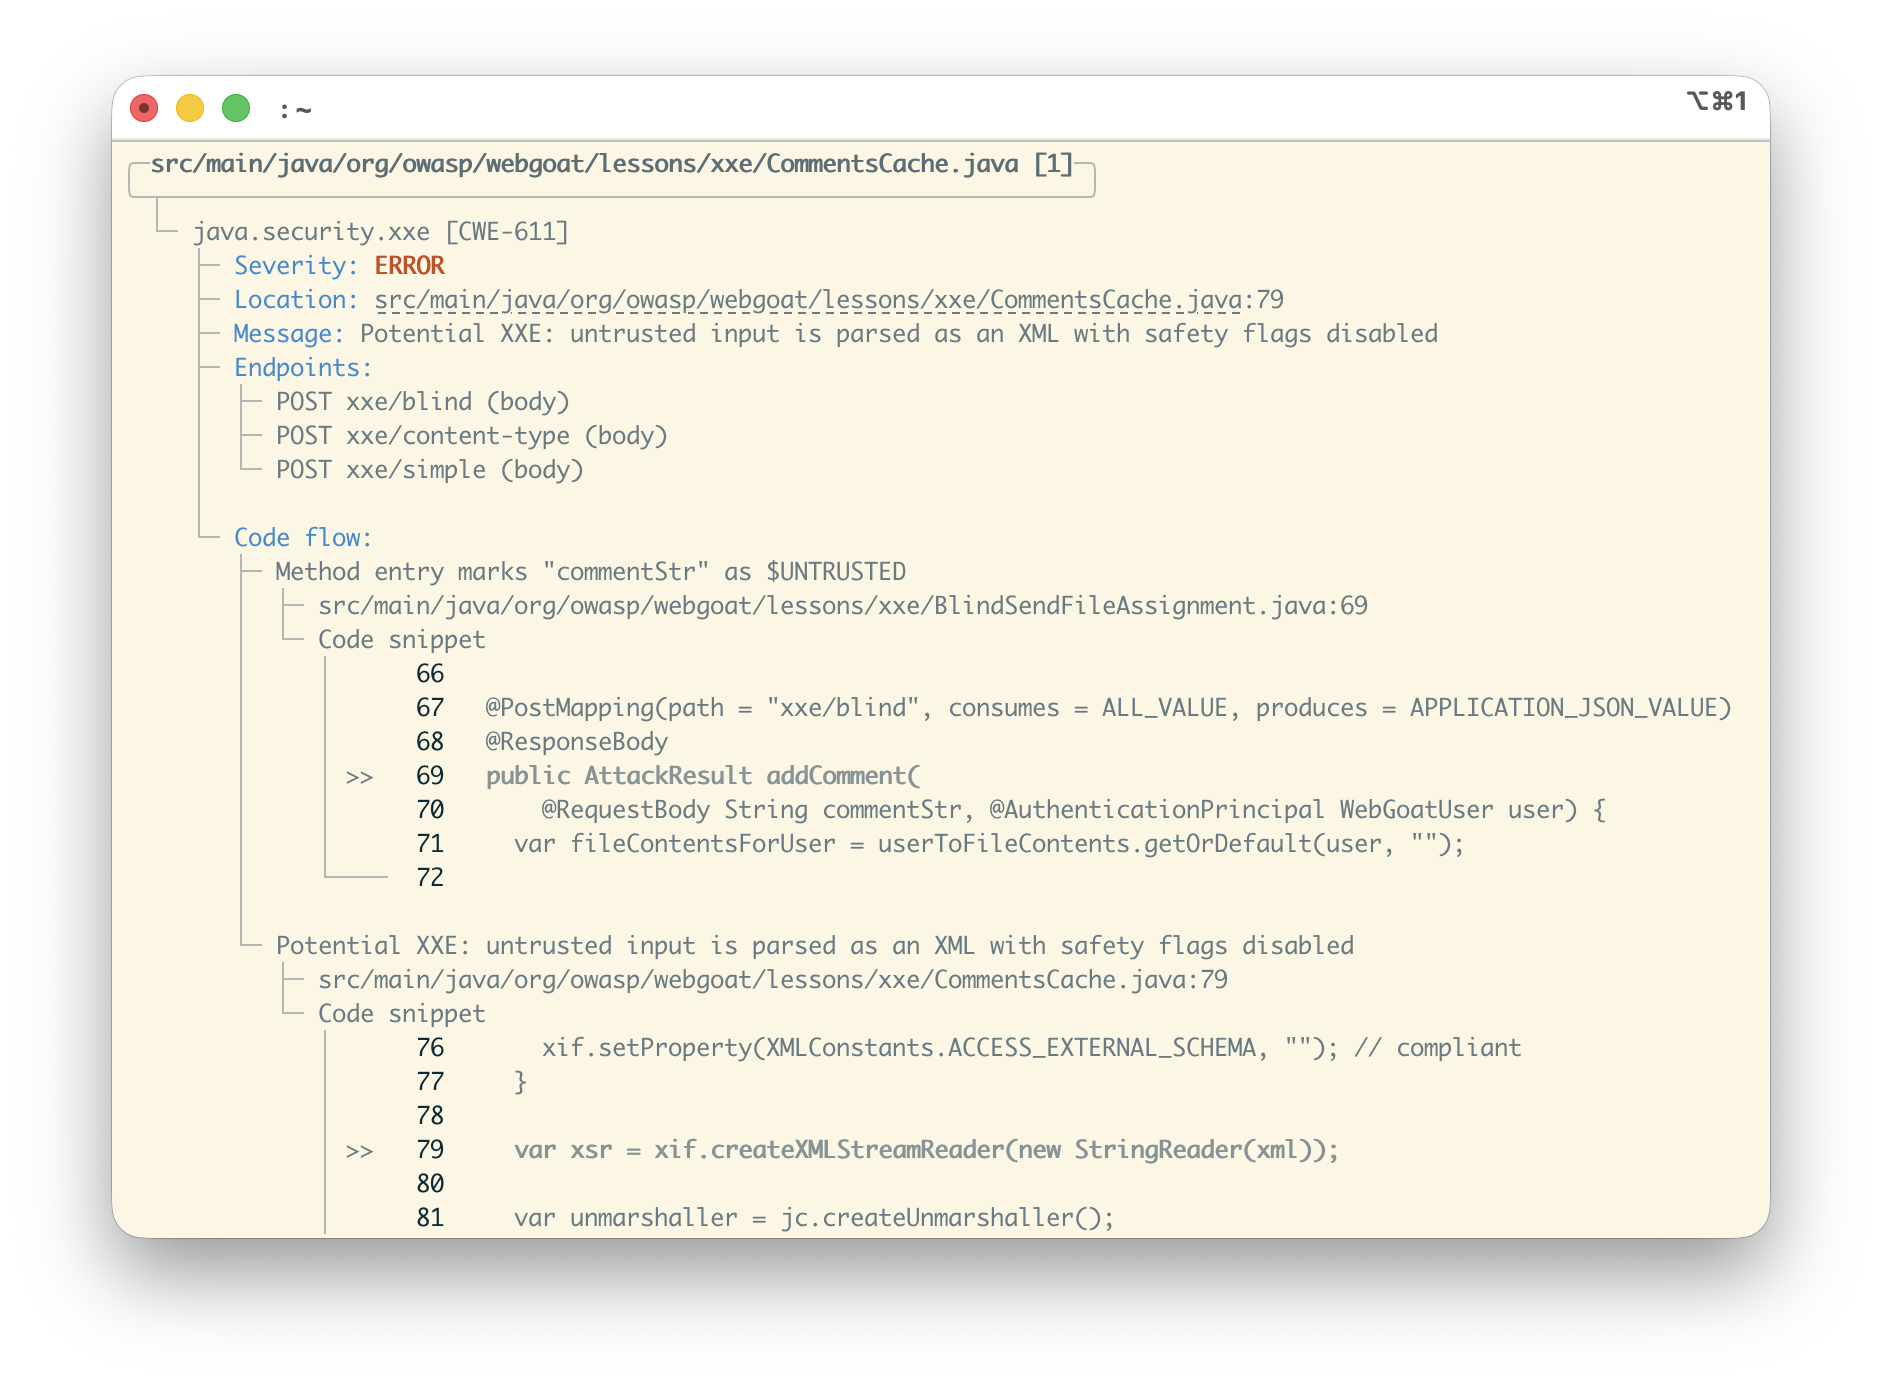 seqra/opentaint
Formal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…
 abhi-r3v0/adhrit
Android Security Suite for in-depth reconnaissance and static bytecode analysis based on Ghera benchmarks.
 rvermeulen/apache-struts-cve-2017-9805
Exploit for Apache Struts CVE-2017-9805, a remote code execution vulnerability in the REST plugin. Enables penetration testing and security…
 safedep/vet
Protect against malicious open source packages 🤖