

oletools
 decalage2/oletools
Python toolkit for analyzing MS OLE2 and Office documents, extracting VBA macros, detecting exploits, and performing forensic analysis of structured…
code-analysisdigital-forensicsforensics+3
3.4k
decalage2/oletoolsPython toolkit for analyzing MS OLE2 and Office documents, extracting VBA macros, detecting exploits, and performing forensic analysis of structured…
 certcc/cve-2021-44228_scanner
Scanners for Jar files that may be vulnerable to CVE-2021-44228
 dbzoo/log4j_scanner
Filesystem scanner for Log4Shell (CVE-2021-44228) and related CVEs. Detects vulnerable JAR files via hash matching and class presence. Runs…
 respondiq/jsp-webshell-scanner
🔍 A simple Bash script to detect malicious JSP webshells, including those used in exploits of SAP NetWeaver CVE-2025-31324.
 jvr2022/cve-2026-29786
Proof-of-concept demonstrating a hardlink path traversal in the tar npm package, allowing overwrite of files outside the extraction directory via…
 chiefyoru/cve-2026-48939_poc
iCagenda extension for Joomla allows the upload of arbitrary files in the file attachment feature, ultimately resulting in PHP code upload and…
 jjyg/metasm
This is the main repository for metasm, a free assembler / disassembler / compiler written in ruby
 mallo-m/cve-2024-47051
Mautic < 5.2.3 Authenticated RCE
 nthuong95/cve-2018-11235
Proof-of-concept exploit for CVE-2018-11235, a remote code execution vulnerability in Git submodules. Demonstrates exploitation of malicious…
 maweil/bidi_char_detector
Checks your files for existence of Unicode BIDI characters which can be misused for supply chain attacks. See CVE-2021-42574
 ejfkdev/ddc
DEX → Java decompiler in Rust — fast, progressive analysis, bilingual CLI
 alexpena5635/cve-2021-44228_scanner-main-modified-
Scans jar, war, and ear files for the presence of JndiLookup.class to detect applications vulnerable to CVE-2021-44228 (Log4Shell).
 mo200909/office-malware-forensics-lab-remnux-static-analysis
Static analysis of 2 malicious Office documents on REMnux using oletools; identified CVE-2017-11882 and obfuscated macros.
 ally-petitt/cve-2024-29399
CVE-2024-29399 reference
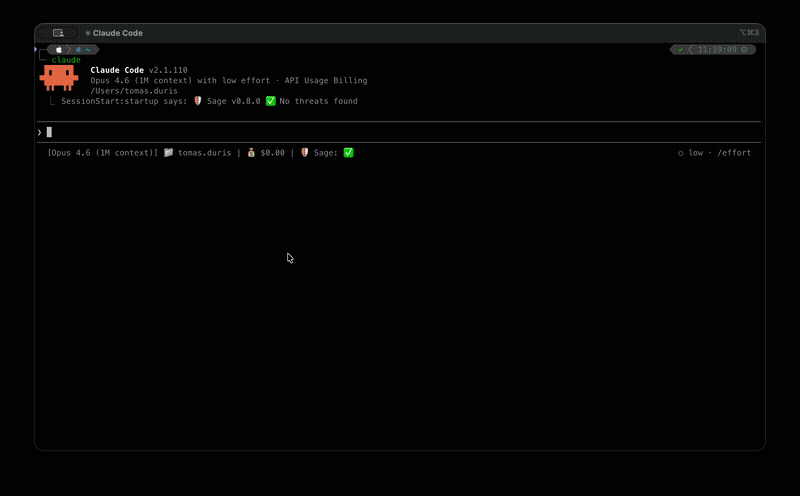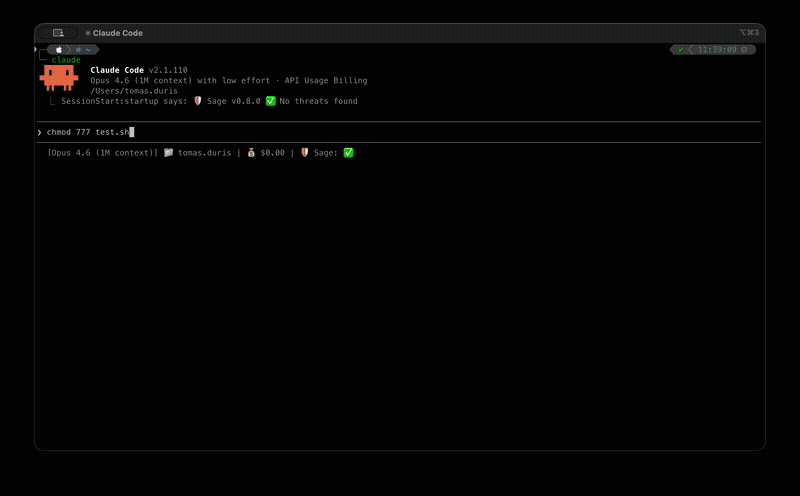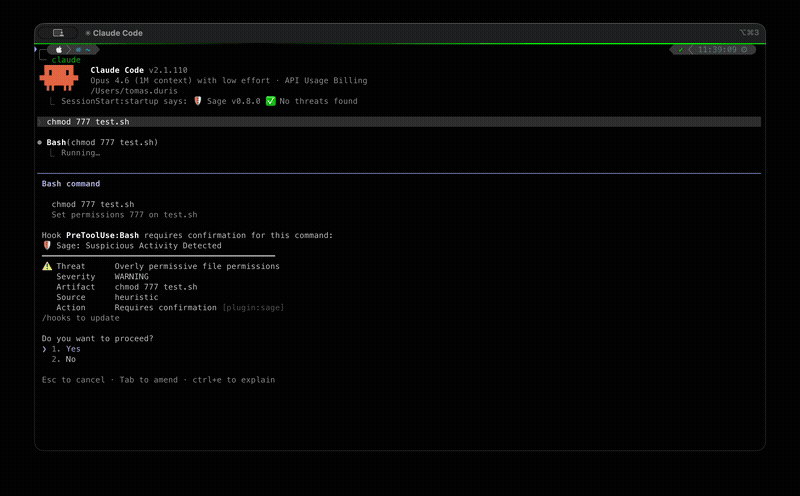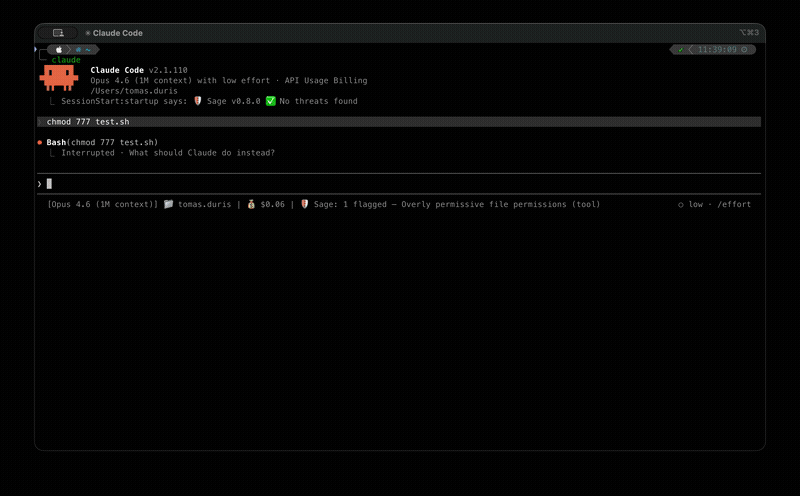 gendigitalinc/sage
Lightweight Agent Detection & Response (ADR) layer for AI agents — guards commands, files, and web requests. Part of Gen Agent Trust Hub.
 mebibite/springhound
Created after the disclosure of CVE-2022-22965 and CVE-2022-22963. Bash script that detects Spring Framework occurrences in your projects and…
 d0n601/cve-2025-5961
Migration, Backup, Staging – WPvivid Backup & Migration <= 0.9.116 - Authenticated (Administrator+) Arbitrary File Upload
 hozyx/log4shell
Applications that are vulnerable to the log4j CVE-2021-44228/45046 issue may be detectable by scanning jar, war, ear, zip files to search for the…