CVE-2019-9978-Social-Warfare-WordPress-RCE

A complete walkthrough and exploit for CVE-2019-9978 - Unauthenticated Remote Code Execution in Social Warfare WordPress plugin ≤ 3.5.2. Includes…

A complete walkthrough and exploit for CVE-2019-9978 - Unauthenticated Remote Code Execution in Social Warfare WordPress plugin ≤ 3.5.2. Includes…

Educational lab demonstrating CVE-2020-7598 prototype pollution in minimist with a vulnerable Node.js/Express app, exploit payload, and…

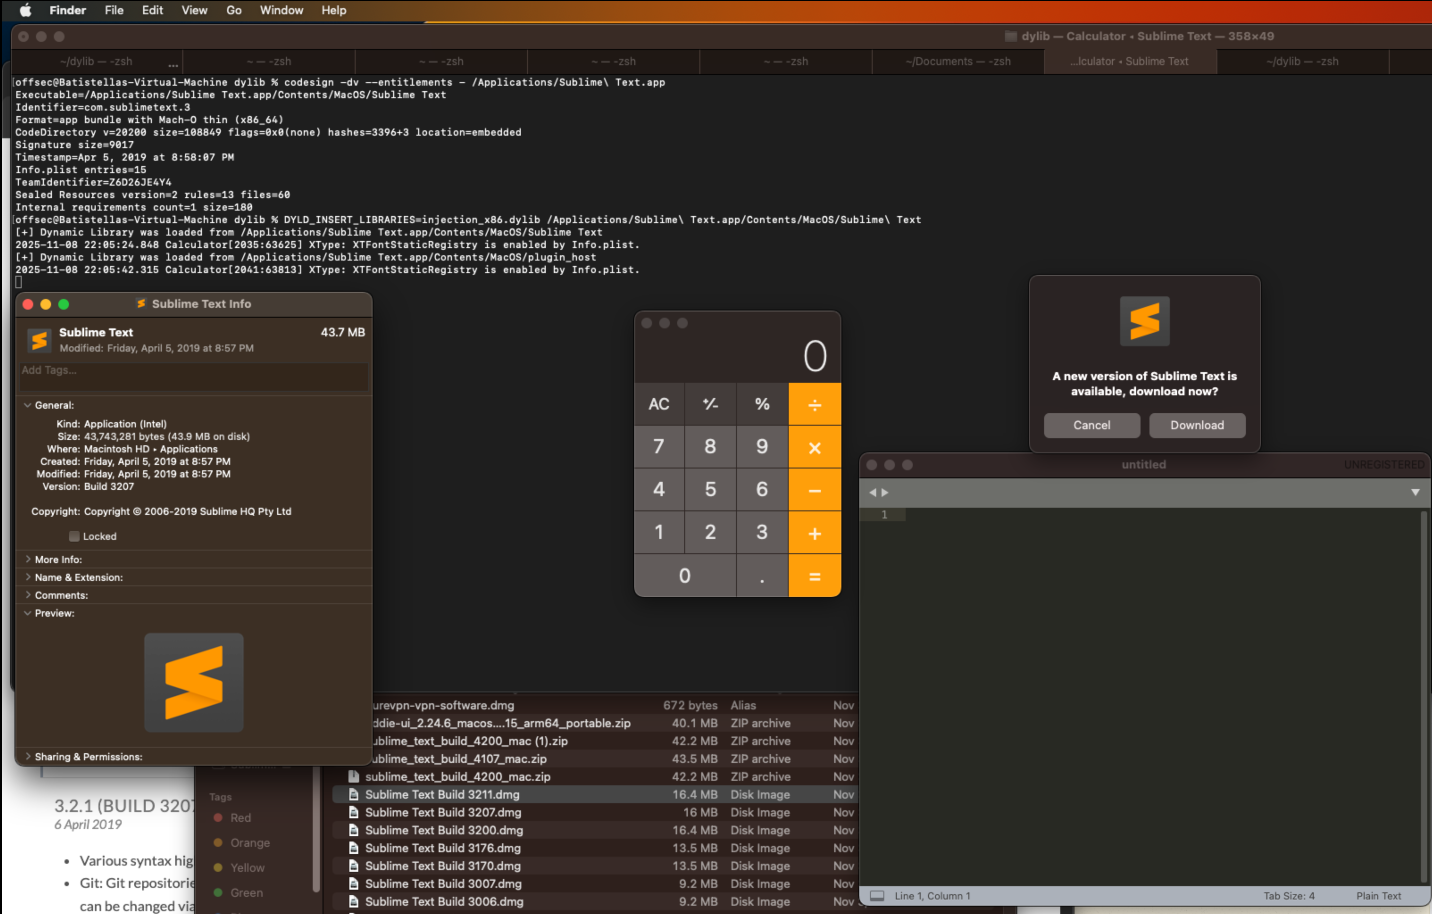
Proof-of-concept for CVE-2025-65741 demonstrating dylib injection in Sublime Text 3 on macOS via unsigned code, with a compiled .dylib payload and…

Demonstrates exploitation of CVE-2017-8046 in a Spring Boot application, including a SpEL injection payload and dependency-check verification for…

Pre-authentication remote code execution exploit for Oracle WebLogic ADF Faces (CVE-2022-21445, CVSS 9.8). Includes detailed environment setup,…

PoC repository for CVE-2025-68147: Stored Cross-Site Scripting (XSS) in OpenSourcePOS. Vulnerability allows privilege escalation via malicious…

Proof-of-concept exploit for CVE-2026-58116 demonstrating remote code execution in LLaMA-Factory WebUI via trust_remote_code model path injection.…

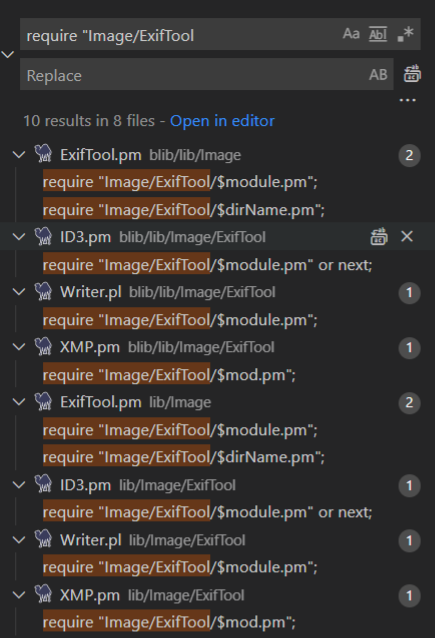
In-depth technical analysis of CVE-2021-22204 (ExifTool RCE) with PoC reproduction, payload construction, and Perl code review of the vulnerable DjVu…

Self-contained Docker lab demonstrating CVE-2007-4559 (TarSlip) directory traversal via Python's tarfile module. Includes vulnerable and fixed APIs,…

Proof-of-concept exploit for CVE-2021-43503, a Laravel deserialization RCE vulnerability. Includes PHP POP chain generation and HTTP-based payload…

Exploit tool for CVE-2026-22785, a critical code injection in orval < 7.18.0. Provides shell command execution and file scanning to demonstrate the…

Proof-of-concept exploit for CVE-2022-24434 targeting the Dicer npm package v0.3.1. Demonstrates server-side vulnerability exploitation with a…

Step-by-step analysis and exploitation guide for CVE-2019-3396, a critical SSTI vulnerability in Confluence Server & Data Center, including debugging…

Proof-of-concept exploit demonstrating the Zip Slip vulnerability (CVE-2019-10743) in mholt/archiver, with a vulnerable server and Python payload for…

Step-by-step walkthrough for exploiting Apache Struts CVE-2024-53677 RCE via file upload manipulation, including OGNL injection, payload embedding,…

Research repository documenting failed exploitation attempts for CVE-2025-24813, a deserialization vulnerability in Apache Tomcat, with tested…

Exploit for CVE-2018-6574, a Go command injection vulnerability. Provides a targeted payload for testing and validating the flaw in affected systems.

A prompt injection in a code‑review bot that executes AI‑generated fixes in a sandbox. The sandbox uses a blacklist to prevent dangerous commands,…