
log4jhound
 mebibite/log4jhound
Created after the disclosure of CVE-2021-44228. Bash script that detects Log4j occurrences in your projects and systems, allowing you to get insight…
code-analysisdevsecopsstatic-analysis+2
mebibite/log4jhoundCreated after the disclosure of CVE-2021-44228. Bash script that detects Log4j occurrences in your projects and systems, allowing you to get insight…
 mebibite/springhound
Created after the disclosure of CVE-2022-22965 and CVE-2022-22963. Bash script that detects Spring Framework occurrences in your projects and…
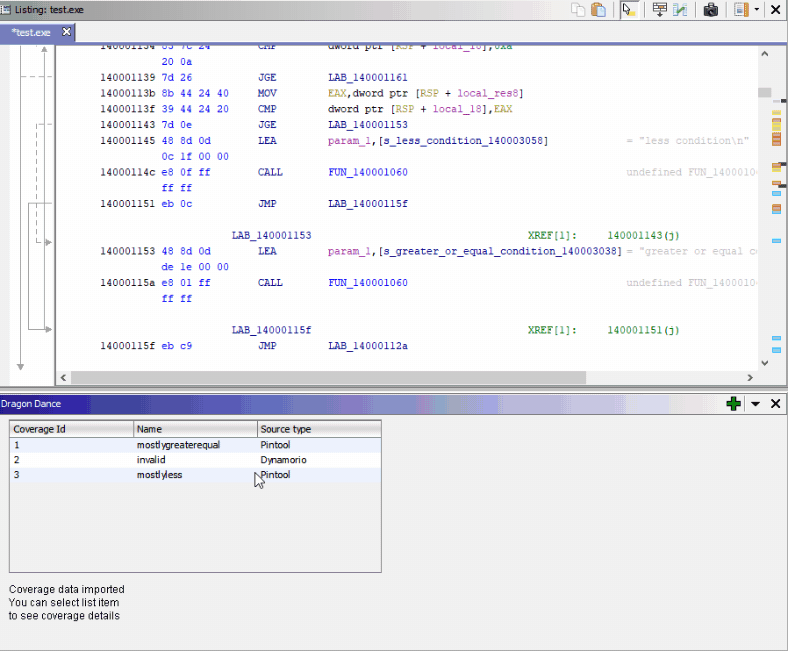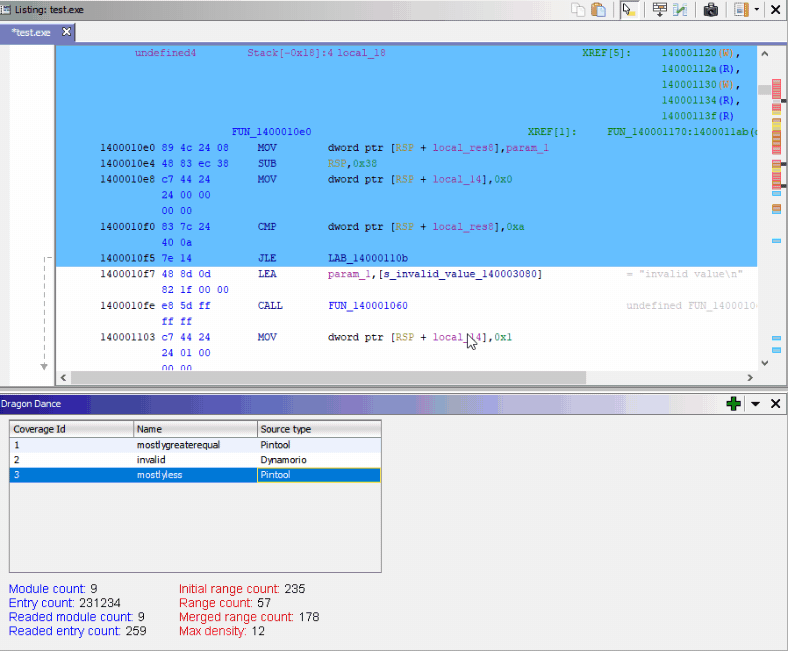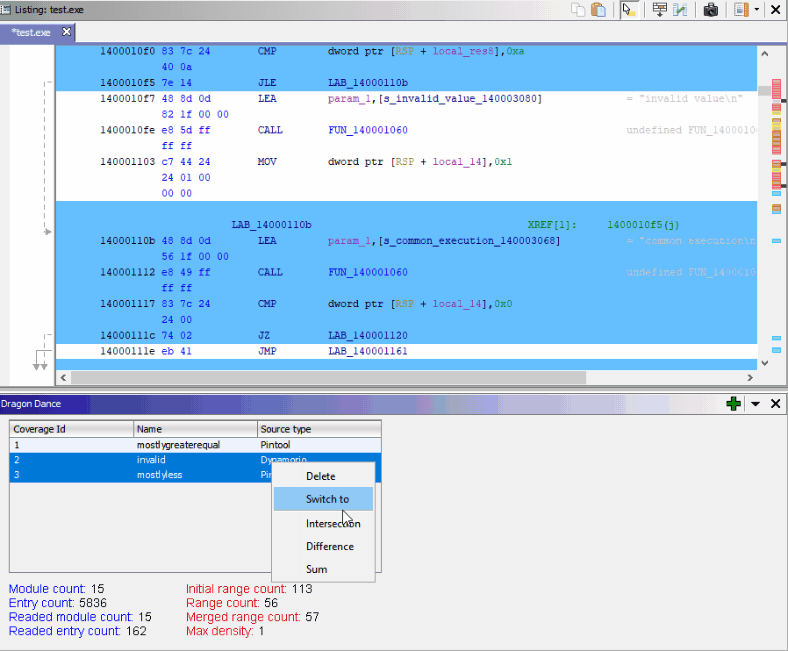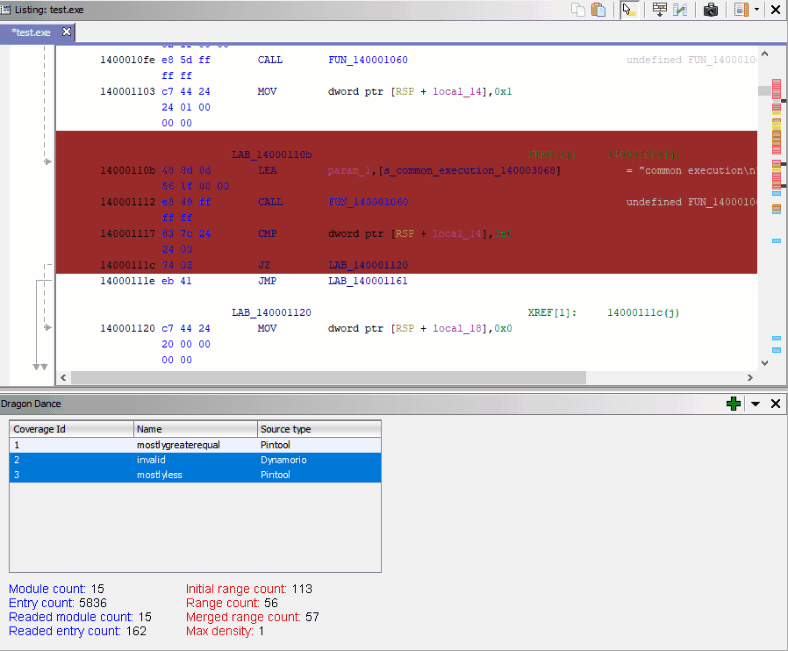 0ffffffffh/dragondance
Binary code coverage visualizer plugin for Ghidra
 arzaan789/keyguard
Scan codebases and GCP projects for exposed API credentials
 intelxed/xed
Low-level library for encoding and decoding IA32/Intel64 x86 instructions, exposing APIs for instruction length, operands, categories, control-flow…
 the-valluvarsploit/cve-2018-6574
Proof-of-concept exploit for CVE-2018-6574, a remote code execution vulnerability in Go's 'go get' command, demonstrating exploitation via malicious…
 mekhalleh/cve-2018-6574
Proof-of-concept exploit for CVE-2018-6574, a remote code execution vulnerability in Go's 'go get' command. Demonstrates exploitation via malicious…
 faqihudin13/cve-2018-6574
Proof-of-concept exploit for CVE-2018-6574, a remote code execution vulnerability in Go's 'go get' command. Demonstrates exploitation via malicious…
 duckzsc2/cve-2018-6574-poc
Proof-of-concept exploit for CVE-2018-6574, a remote code execution vulnerability in Go's 'go get' command. Demonstrates exploitation via malicious…
 jftierno/cve-2018-6574-2
Proof-of-concept exploit for CVE-2018-6574, a remote code execution vulnerability in Go's 'go get' command. Demonstrates exploitation via malicious…
 noobtest1122/cve-2018-6574
Proof-of-concept exploit for CVE-2018-6574, a remote code execution vulnerability in Go's 'go get' command, demonstrating exploitation via malicious…
 20matan/cve-2018-6574-poc
Proof-of-concept exploit for CVE-2018-6574, demonstrating arbitrary command execution via crafted import paths in Go's go get command.
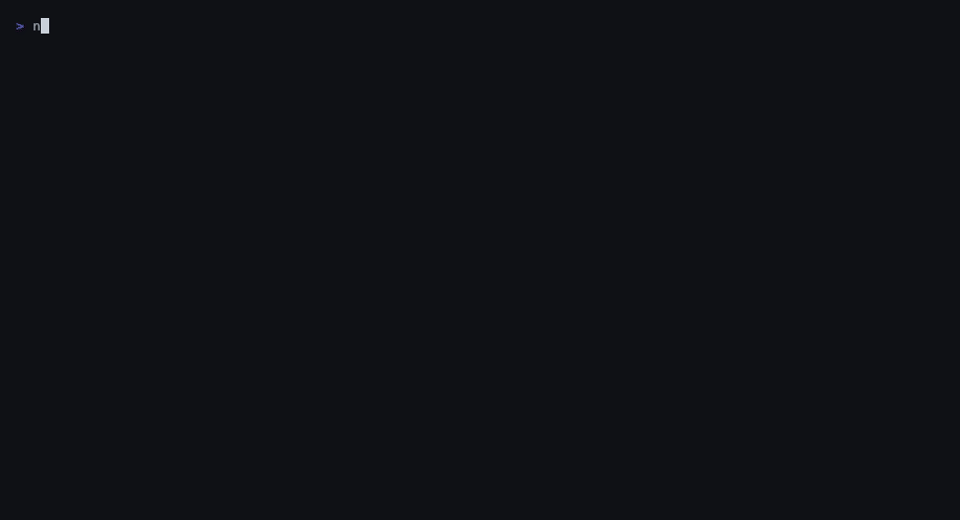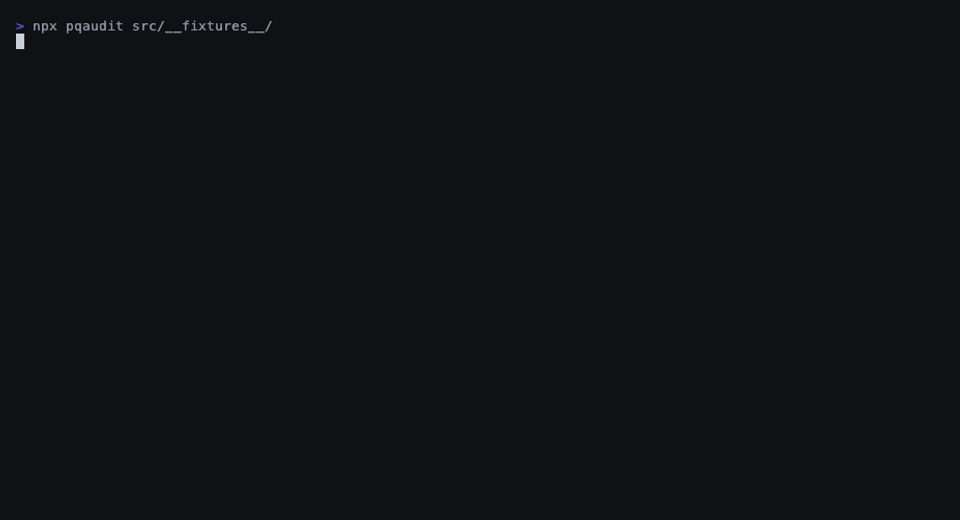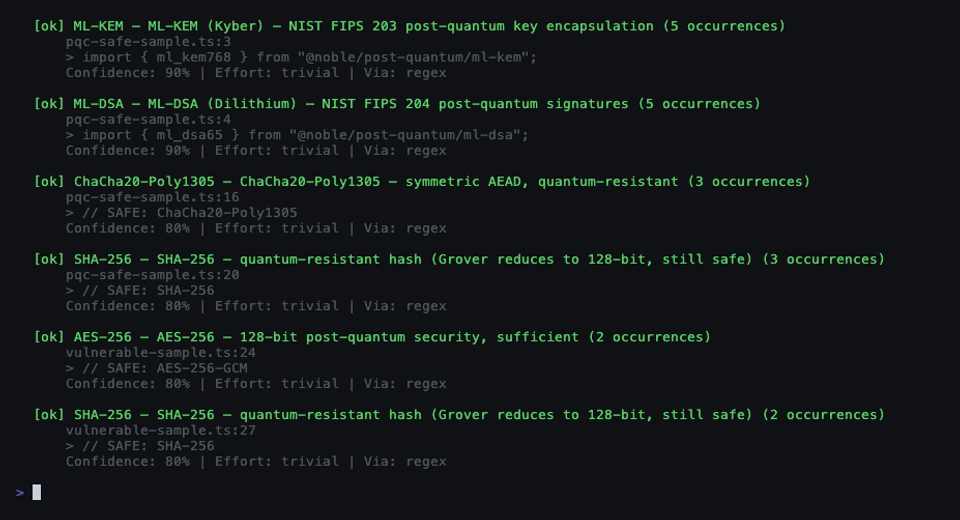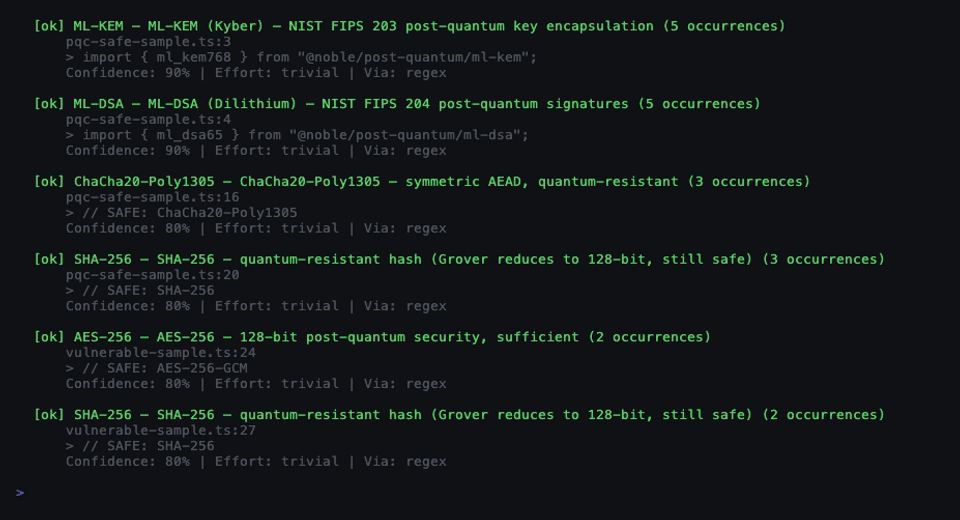 pqcworld/pqaudit
Scan codebases for quantum-vulnerable cryptography. Detect RSA, ECDSA, Ed25519, ECDH before Q-Day. CycloneDX CBOM + SARIF output.
 yomisana/are-you-get-tanstack-attack
Are you get Tanstack Supply chain attack attack of 5/11? CVE-2026-45321 / GHSA-g7cv-rxg3-hmpx
 glasses618/cve-2020-15169
Ruby-based exploit for CVE-2020-15169, demonstrating a specific web application vulnerability with proof-of-concept code for security testing and…
 tamaloa/avo-cve-2024-22411
Proof-of-concept exploit for CVE-2024-22411 targeting the Avo admin panel. Demonstrates vulnerability exploitation in Ruby-based web applications.
 crazycatmyopic/cve
Reproducible example demonstrating CVE-2024-26308 vulnerability detection during Docker builds, with Maven dependency tree analysis and remediation…
 honeynet/apkinspector
APKinspector is a powerful GUI tool for analysts to analyze the Android applications.