

ddc
 ejfkdev/ddc
DEX → Java decompiler in Rust — fast, progressive analysis, bilingual CLI
android-securitybinary-analysiscode-analysis+6
ejfkdev/ddcDEX → Java decompiler in Rust — fast, progressive analysis, bilingual CLI
 newliver666/apk-reverse
Agent skill for Android APK reverse engineering: dex patching, unpacking, repacking, ad and paywall removal, native .so analysis, and runtime…
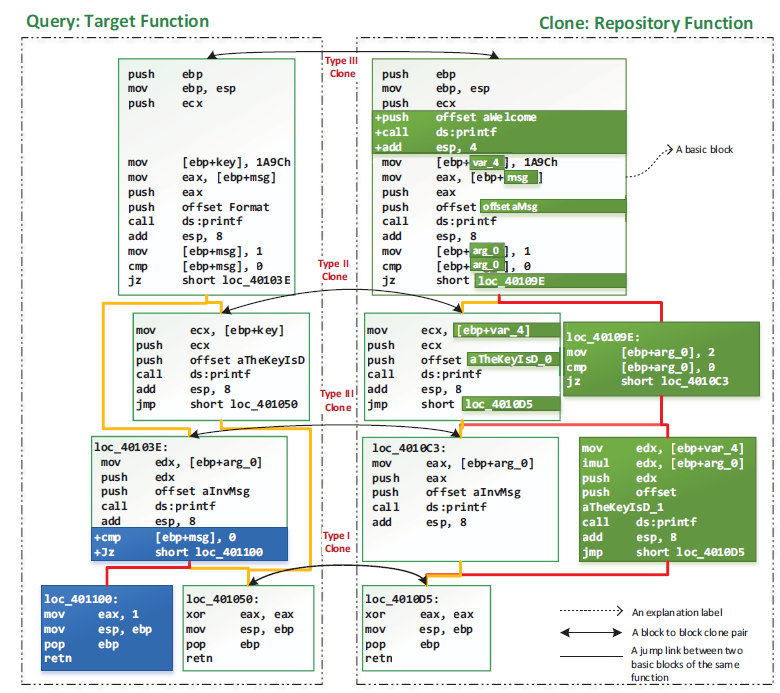 mcgill-dmas/kam1n0-community
Scalable assembly analysis platform for indexing, clone search, and executable classification using static, dynamic, and machine-learning techniques…
 felixber/findfunc
IDA Pro plugin for filtering functions by assembly patterns, byte sequences, string/name references, and size constraints, with rule-based search and…
 quarkslab/quokka
Quokka: A Fast and Accurate Binary Exporter
 ch0pin/rdx
A native APK and DEX decompiler written in Rust
 prophetcraft/jarhunter
JAR analysis tool for exploring, searching, and extracting specific classes from large JAR files with bytecode search, multi-selection extraction,…
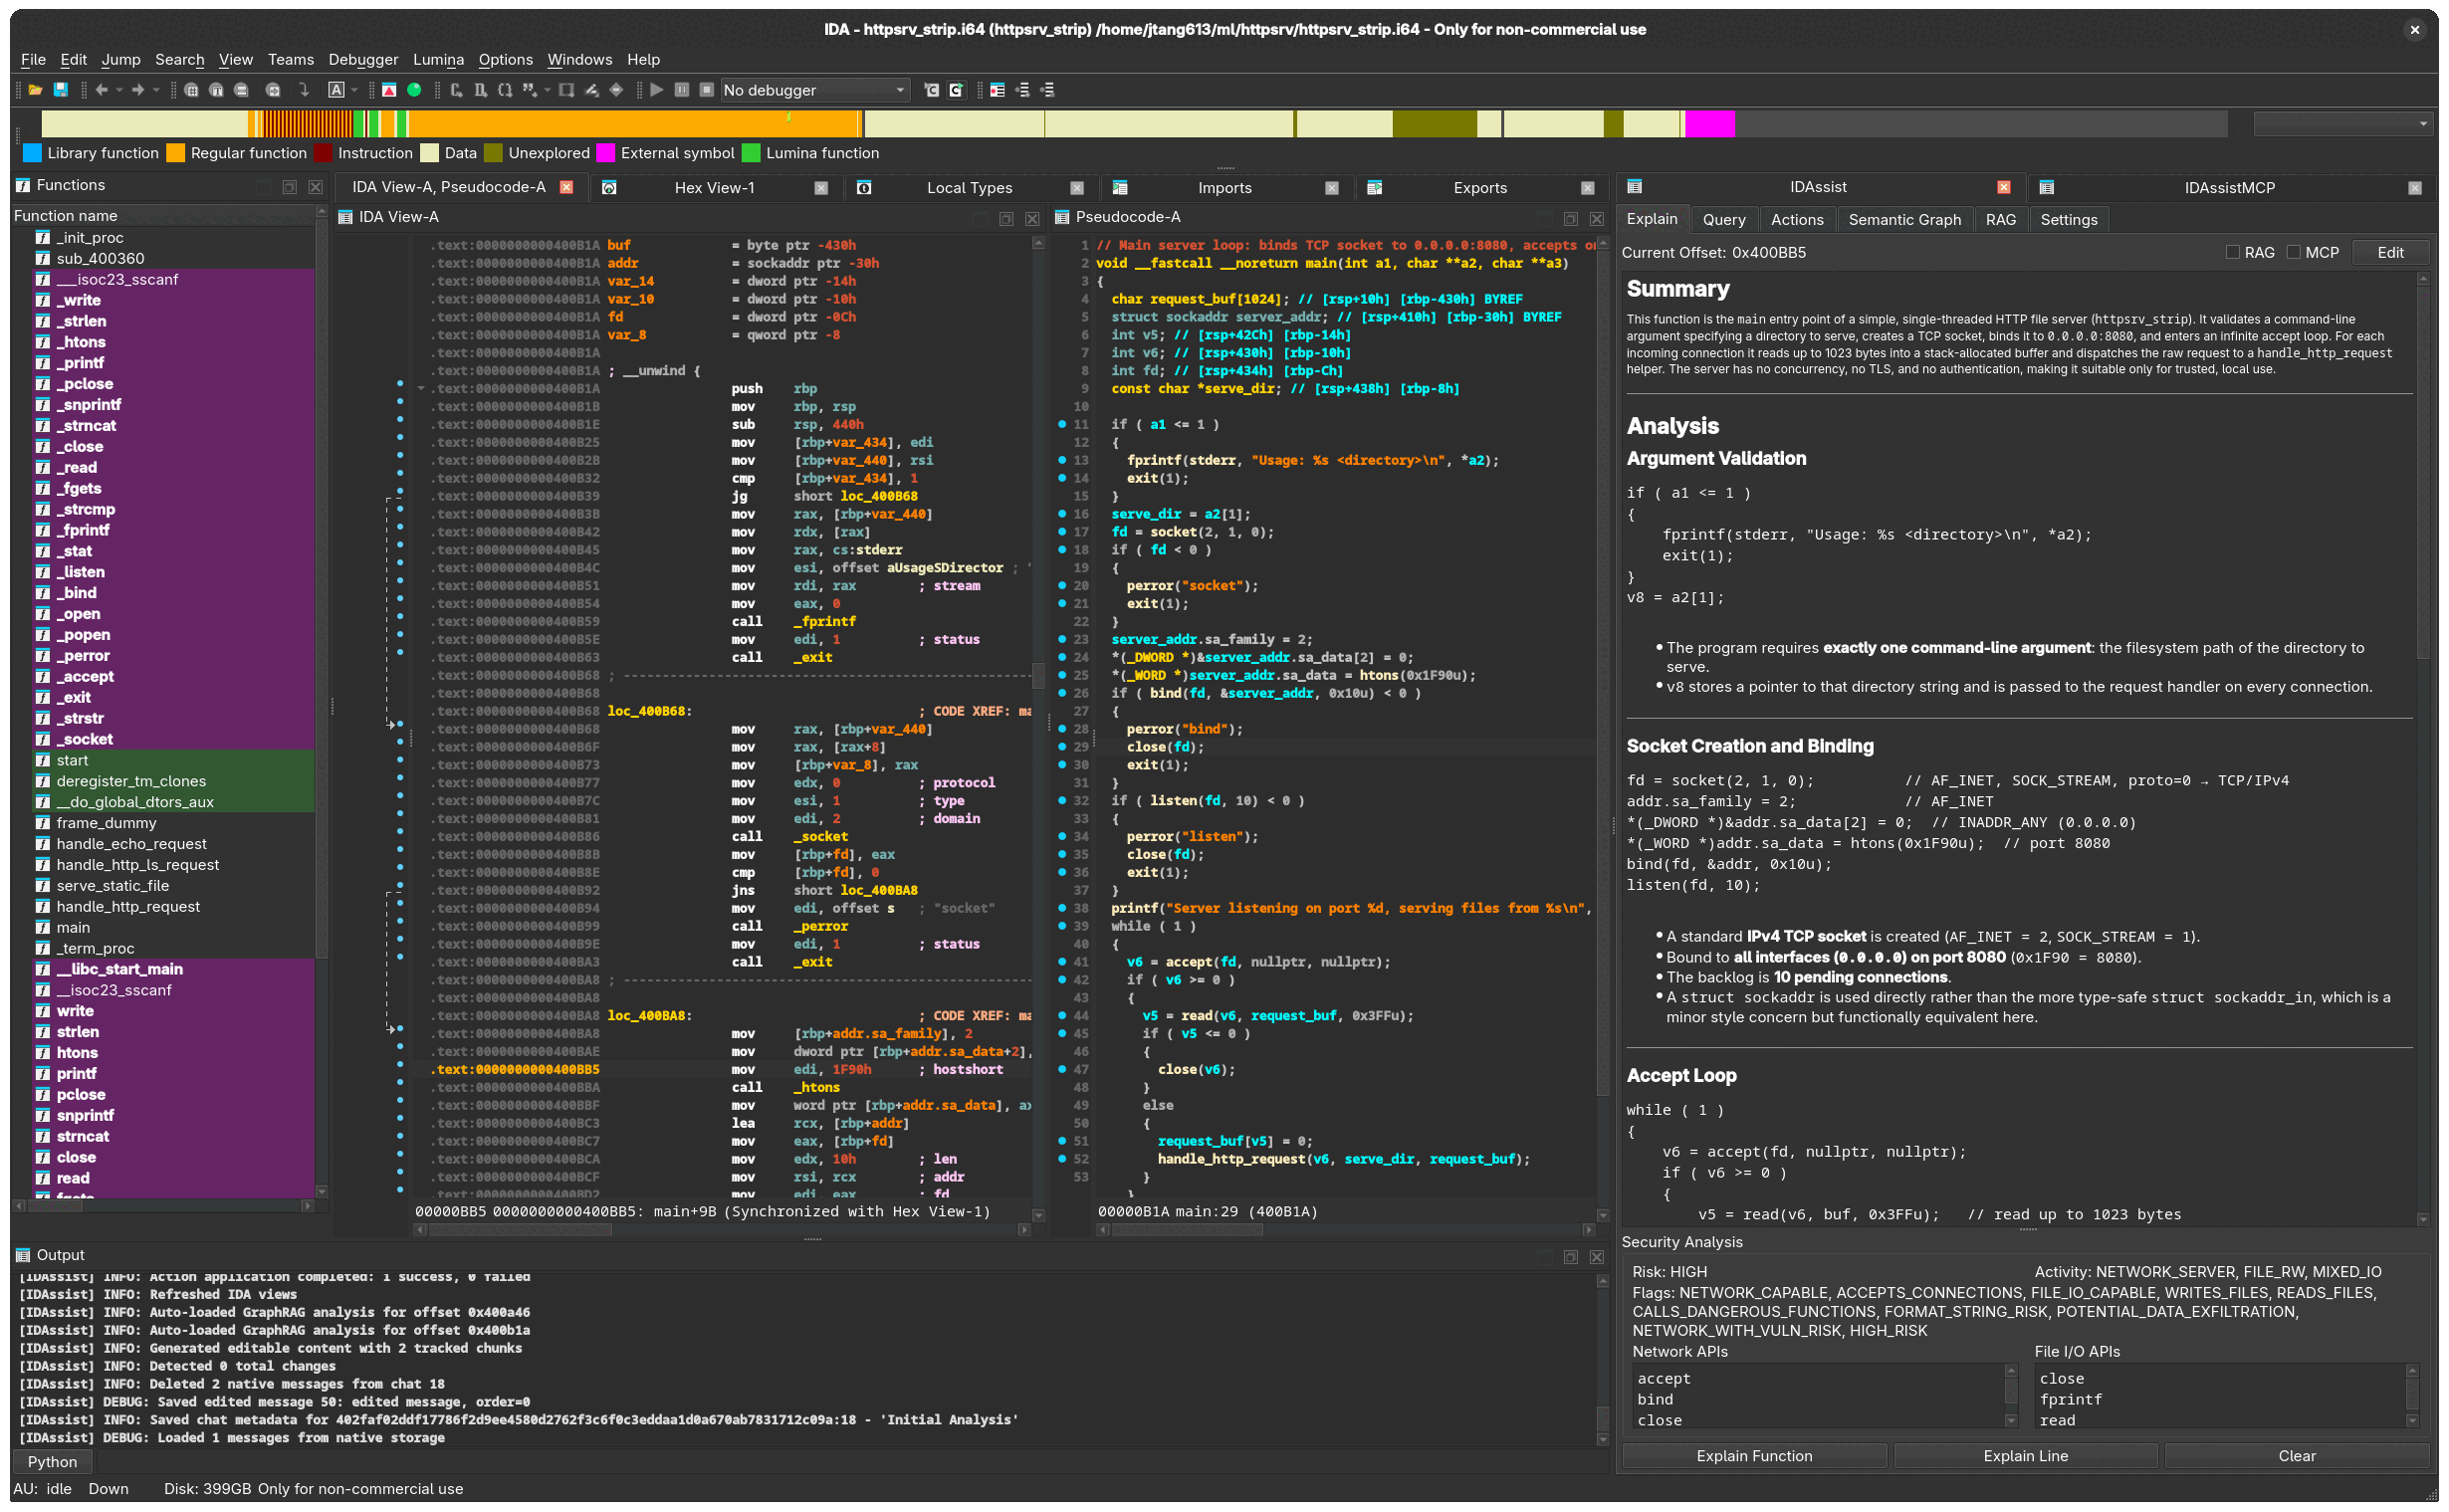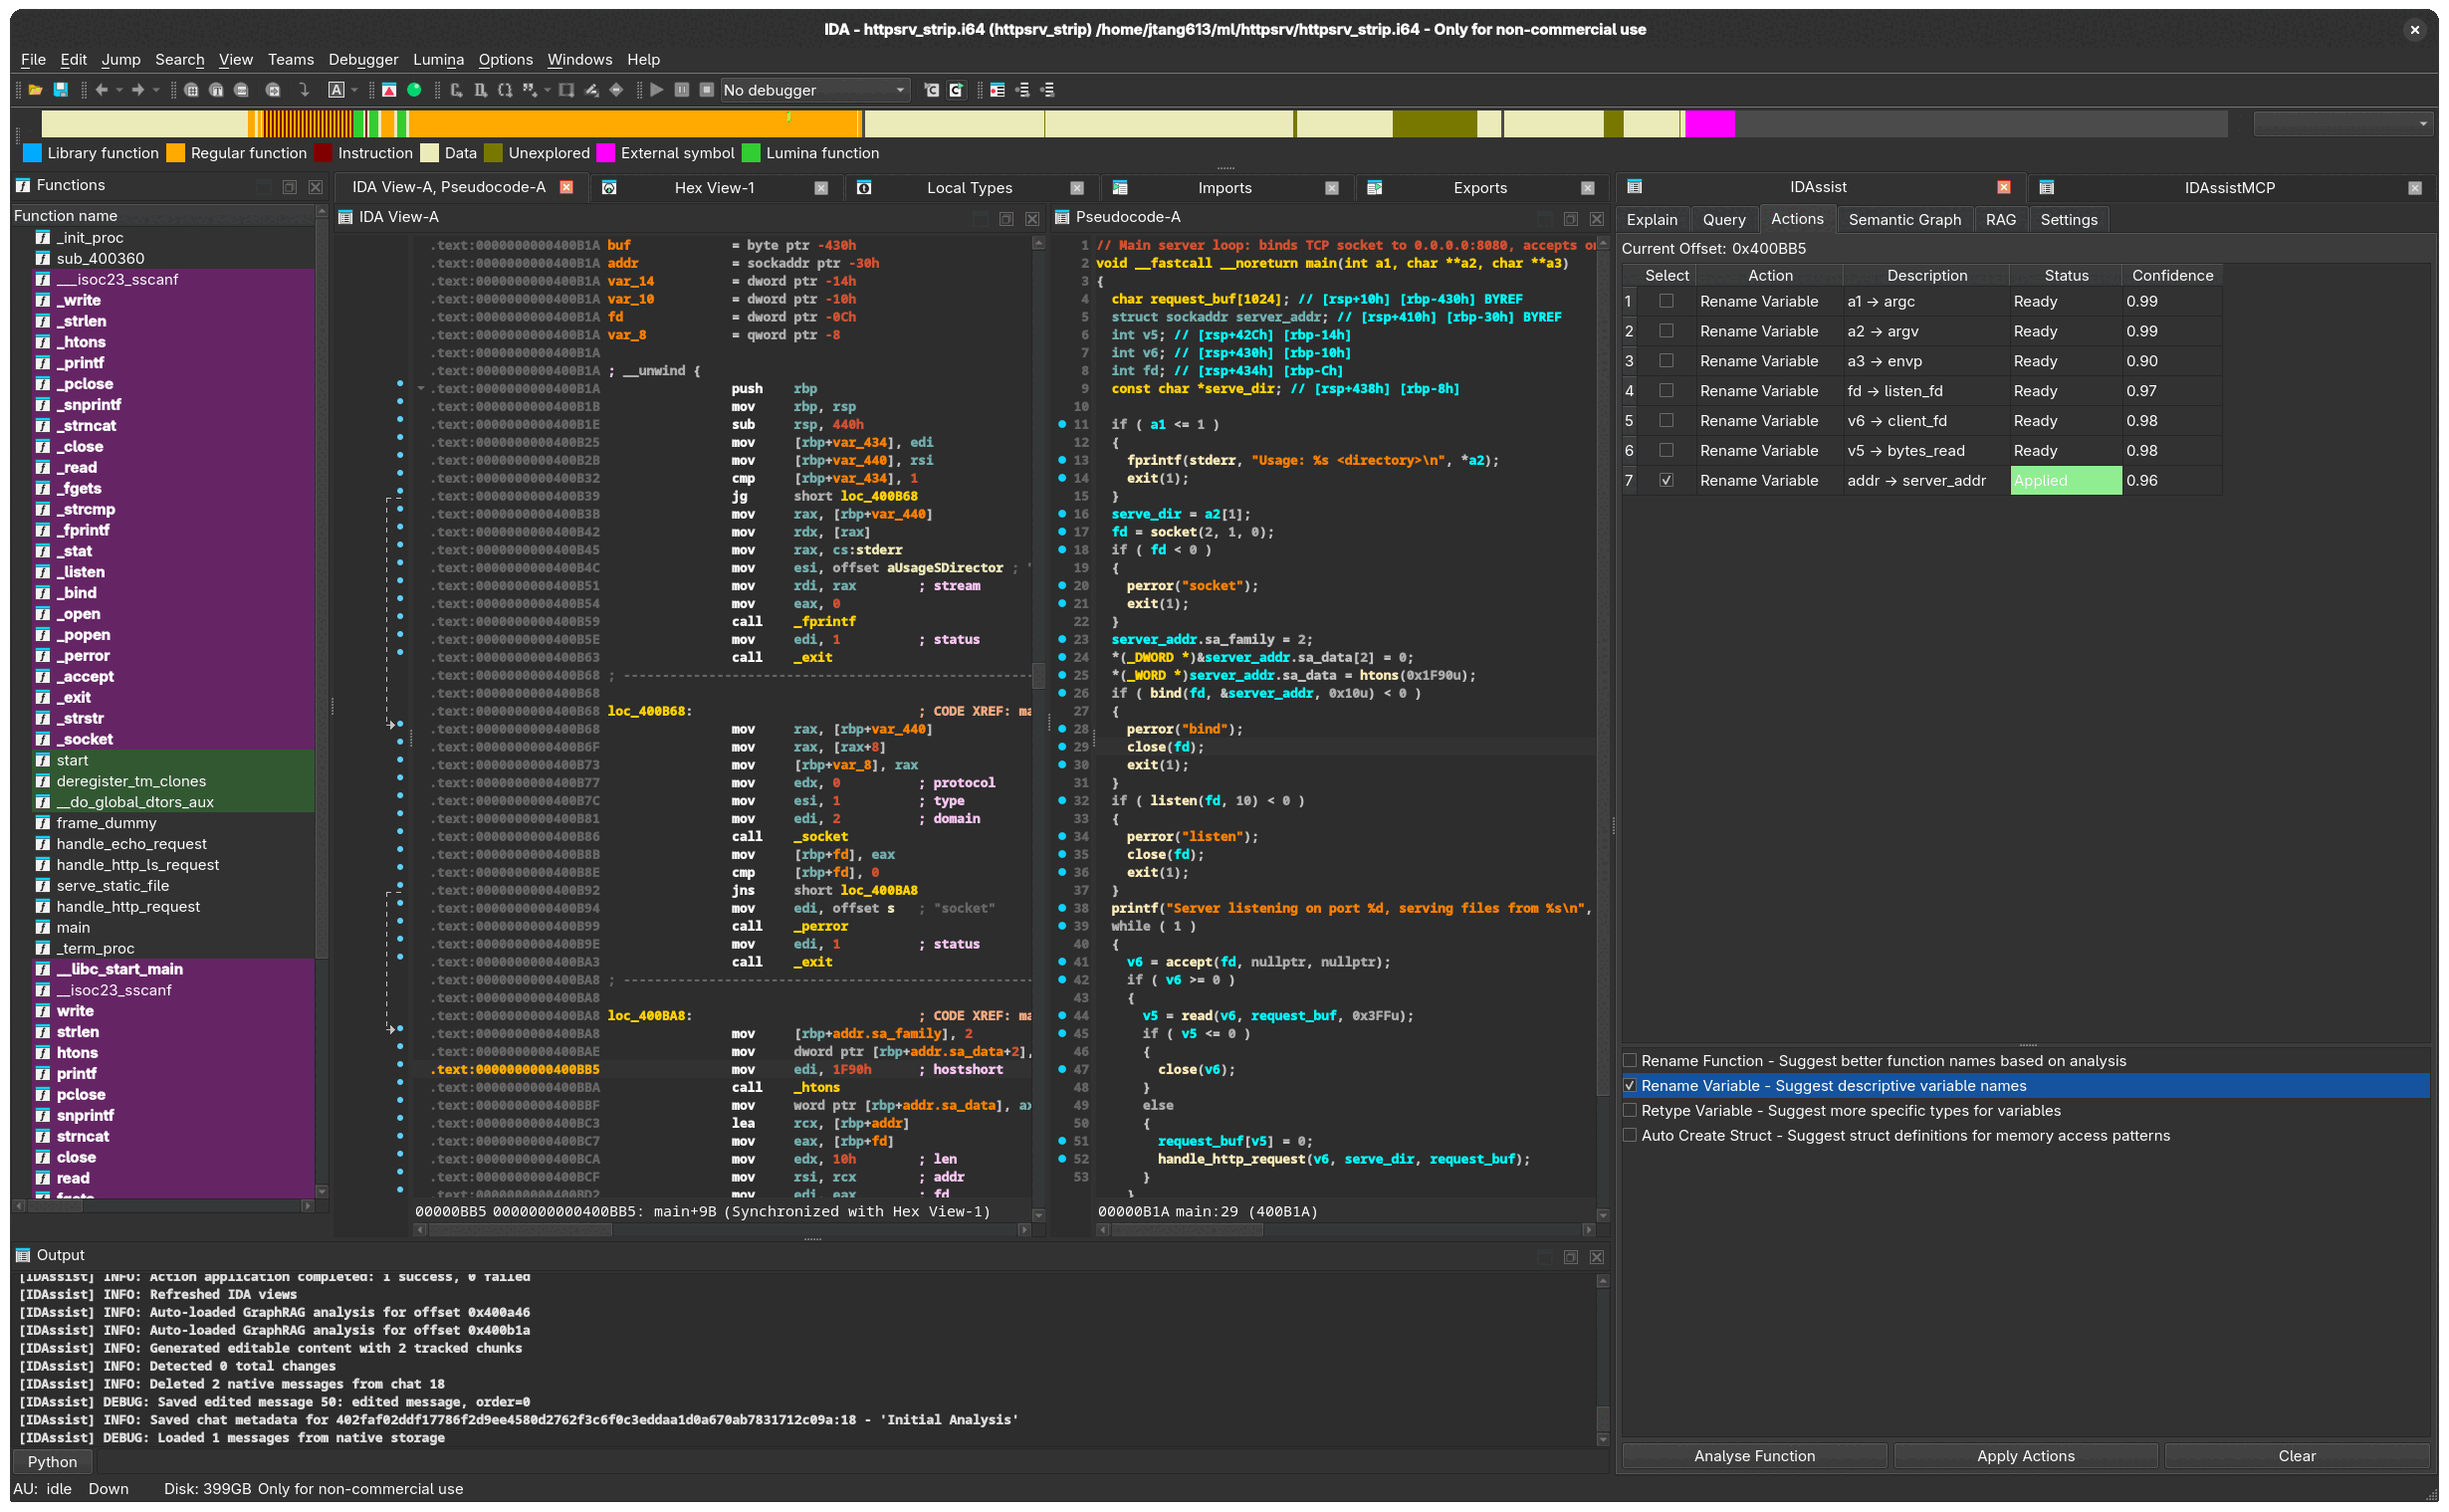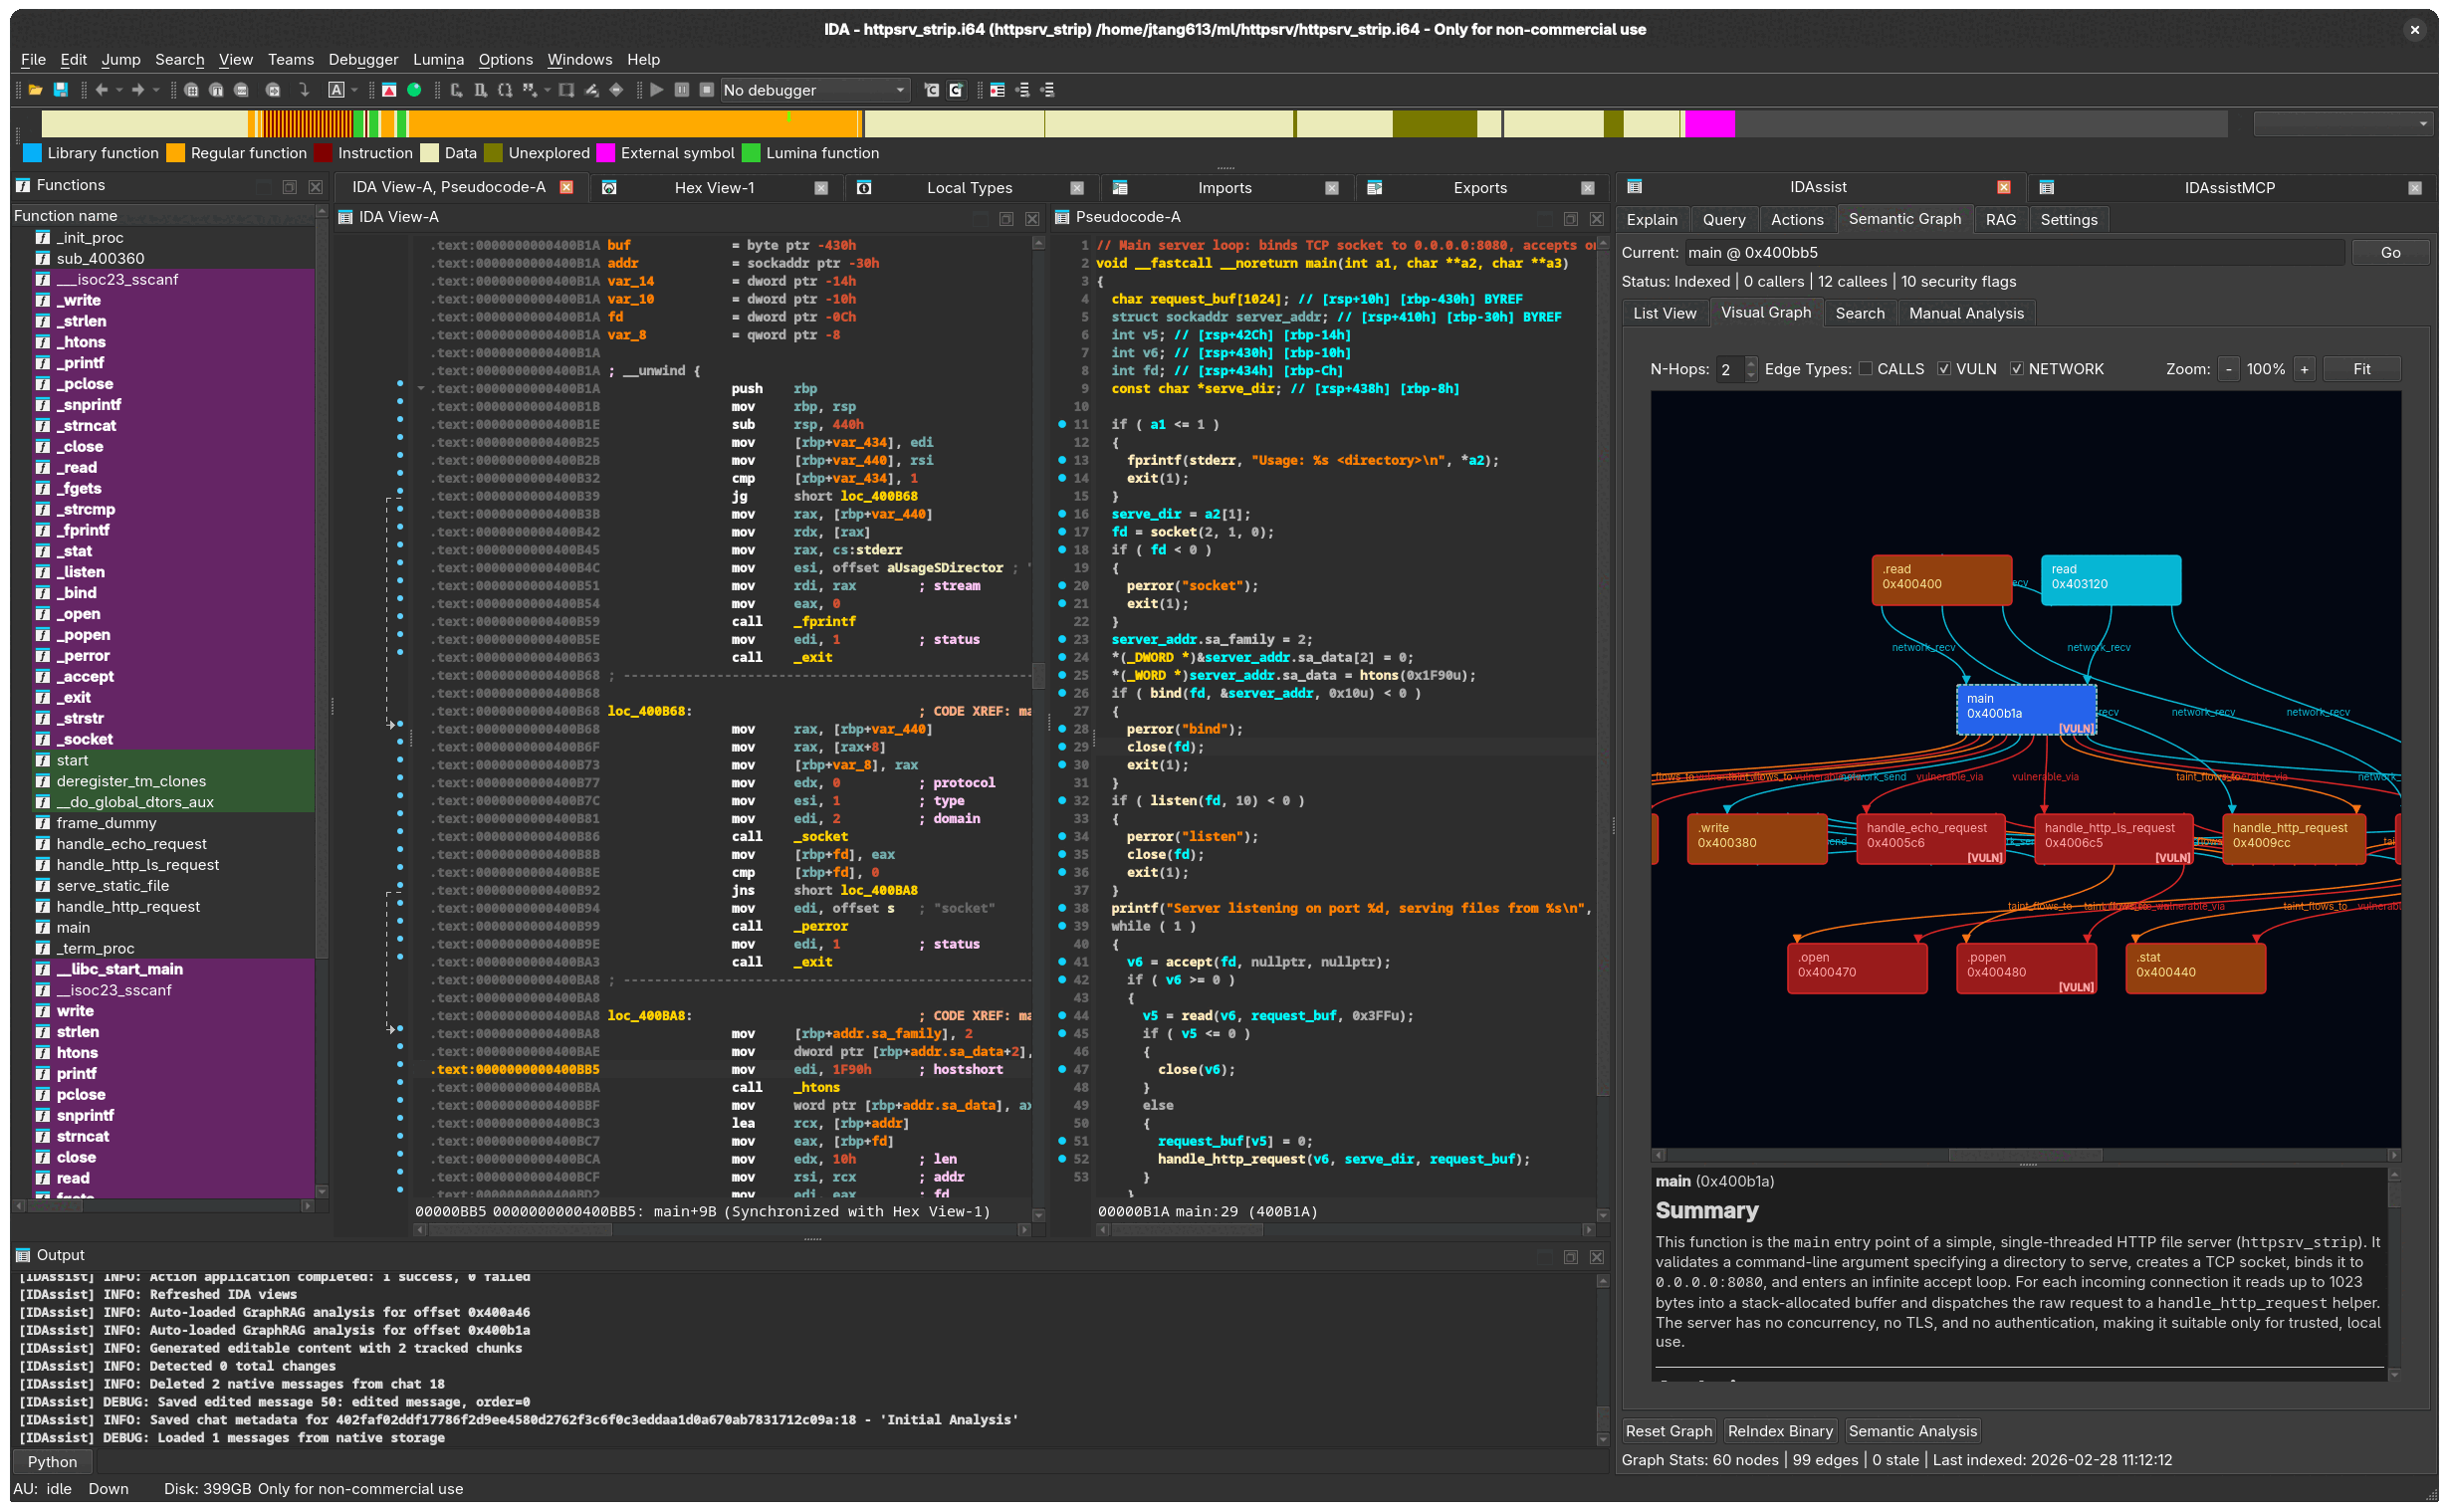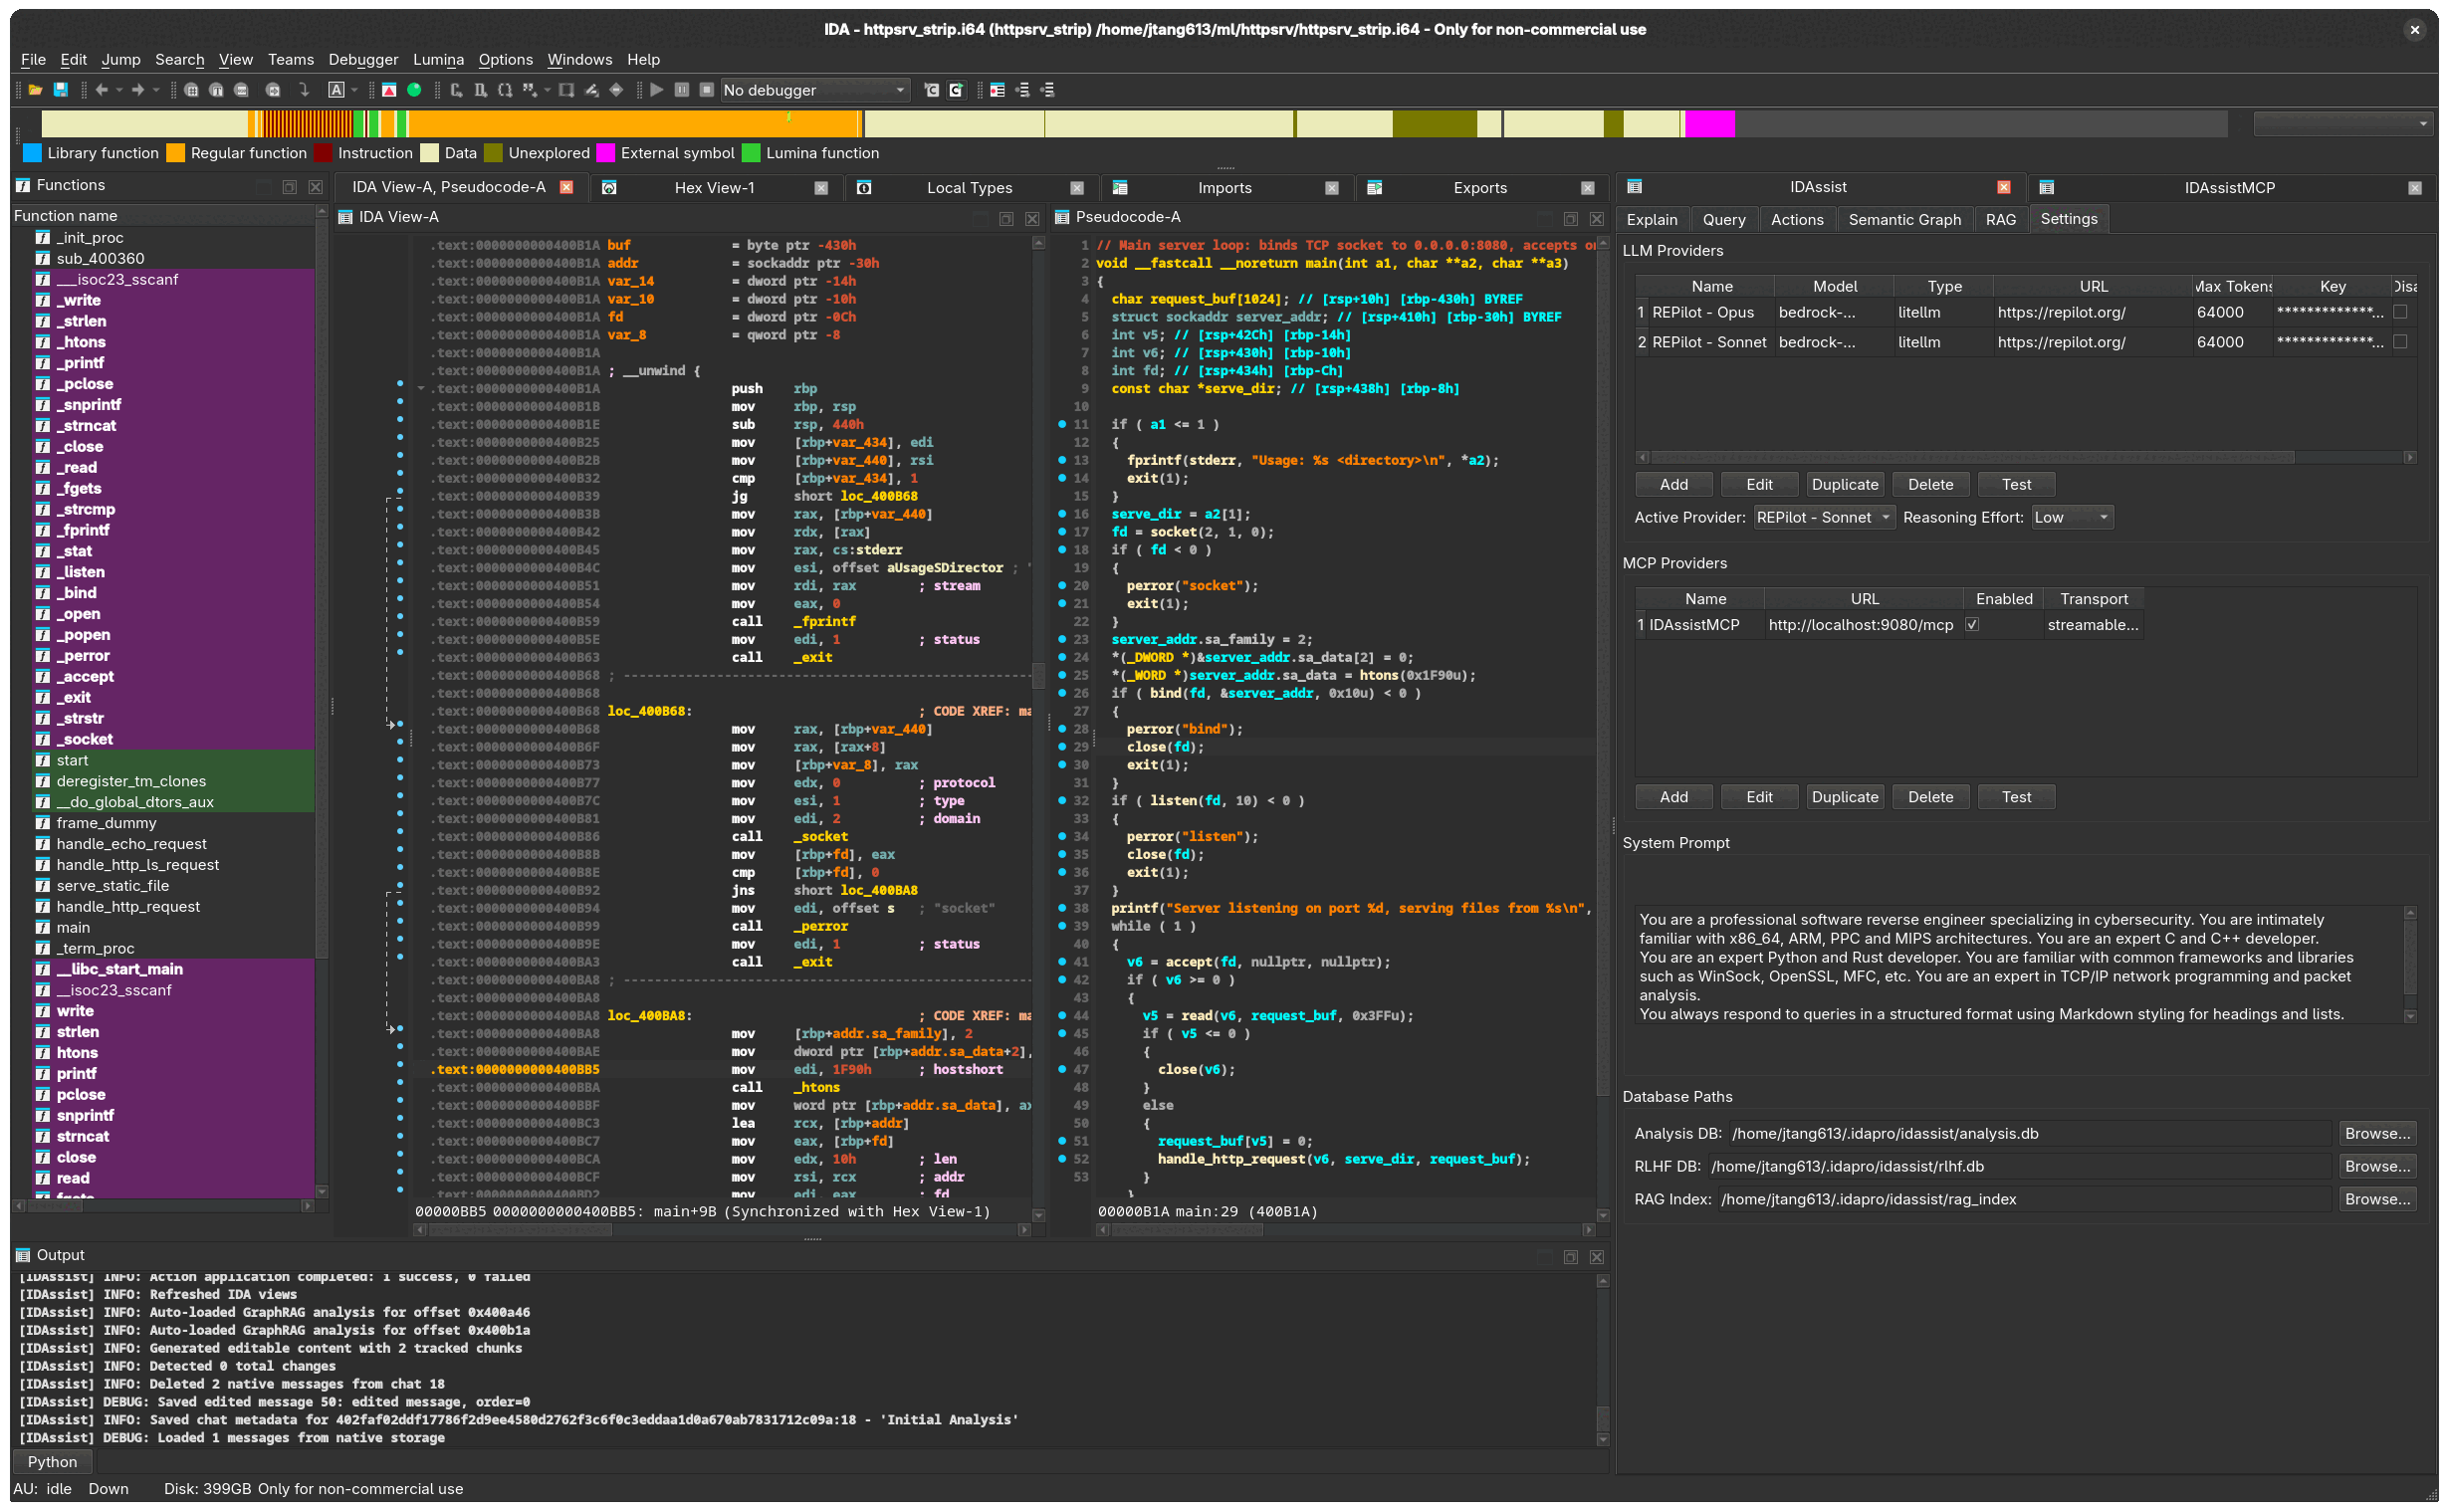 symgraph/idassist
AI-Powered Reverse Engineering Plugin for IDA Pro
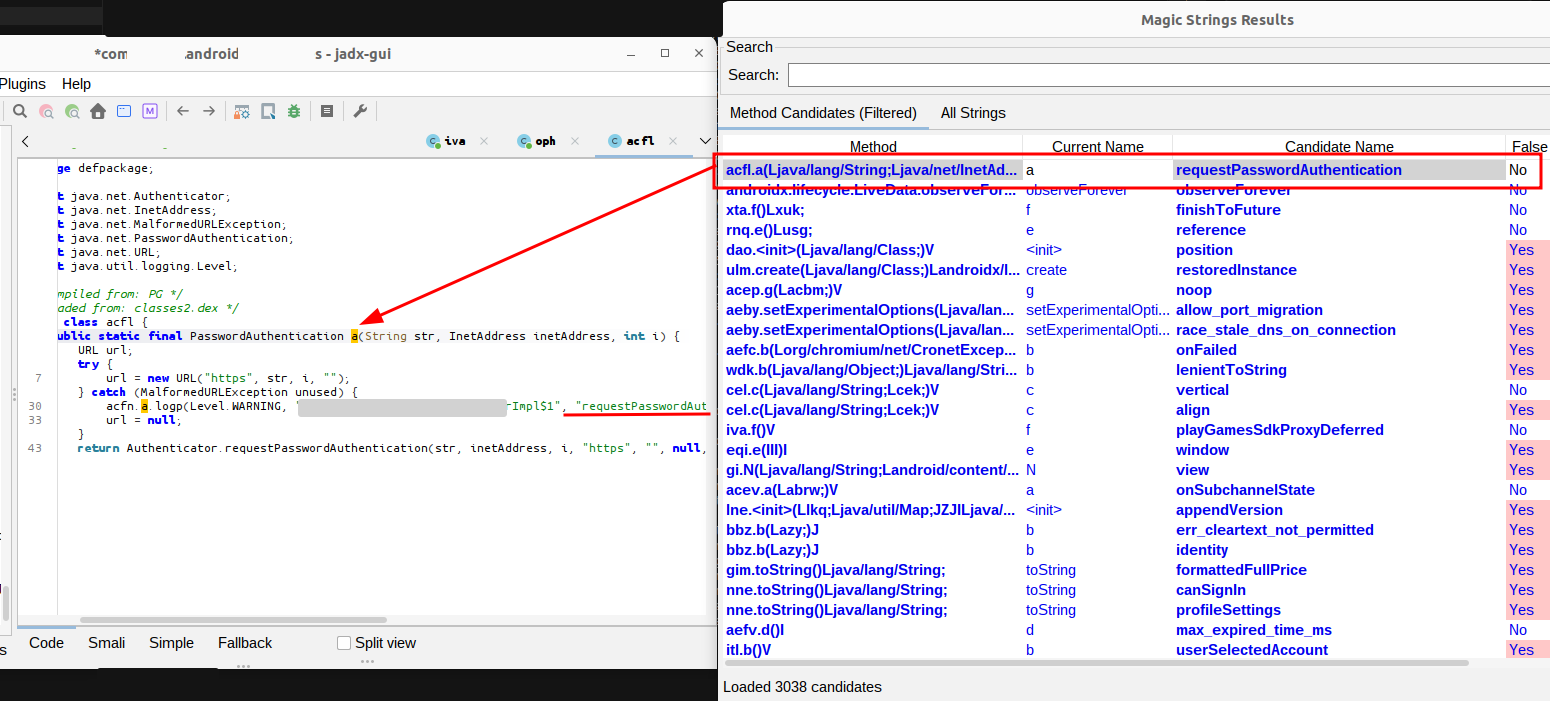 0rshemesh/jadx-magic-strings
JADX plugin that extracts method names, class references, and source file paths from string constants found in DEX files and decompiled Android code.
 superandroidanalyzer/super
Secure, Unified, Powerful and Extensible Rust Android Analyzer
 antonin-deniau/cave_miner
Search for code cave in all binaries
 google/kernel-sanitizers
Linux Kernel Sanitizers, fast bug-detectors for the Linux kernel
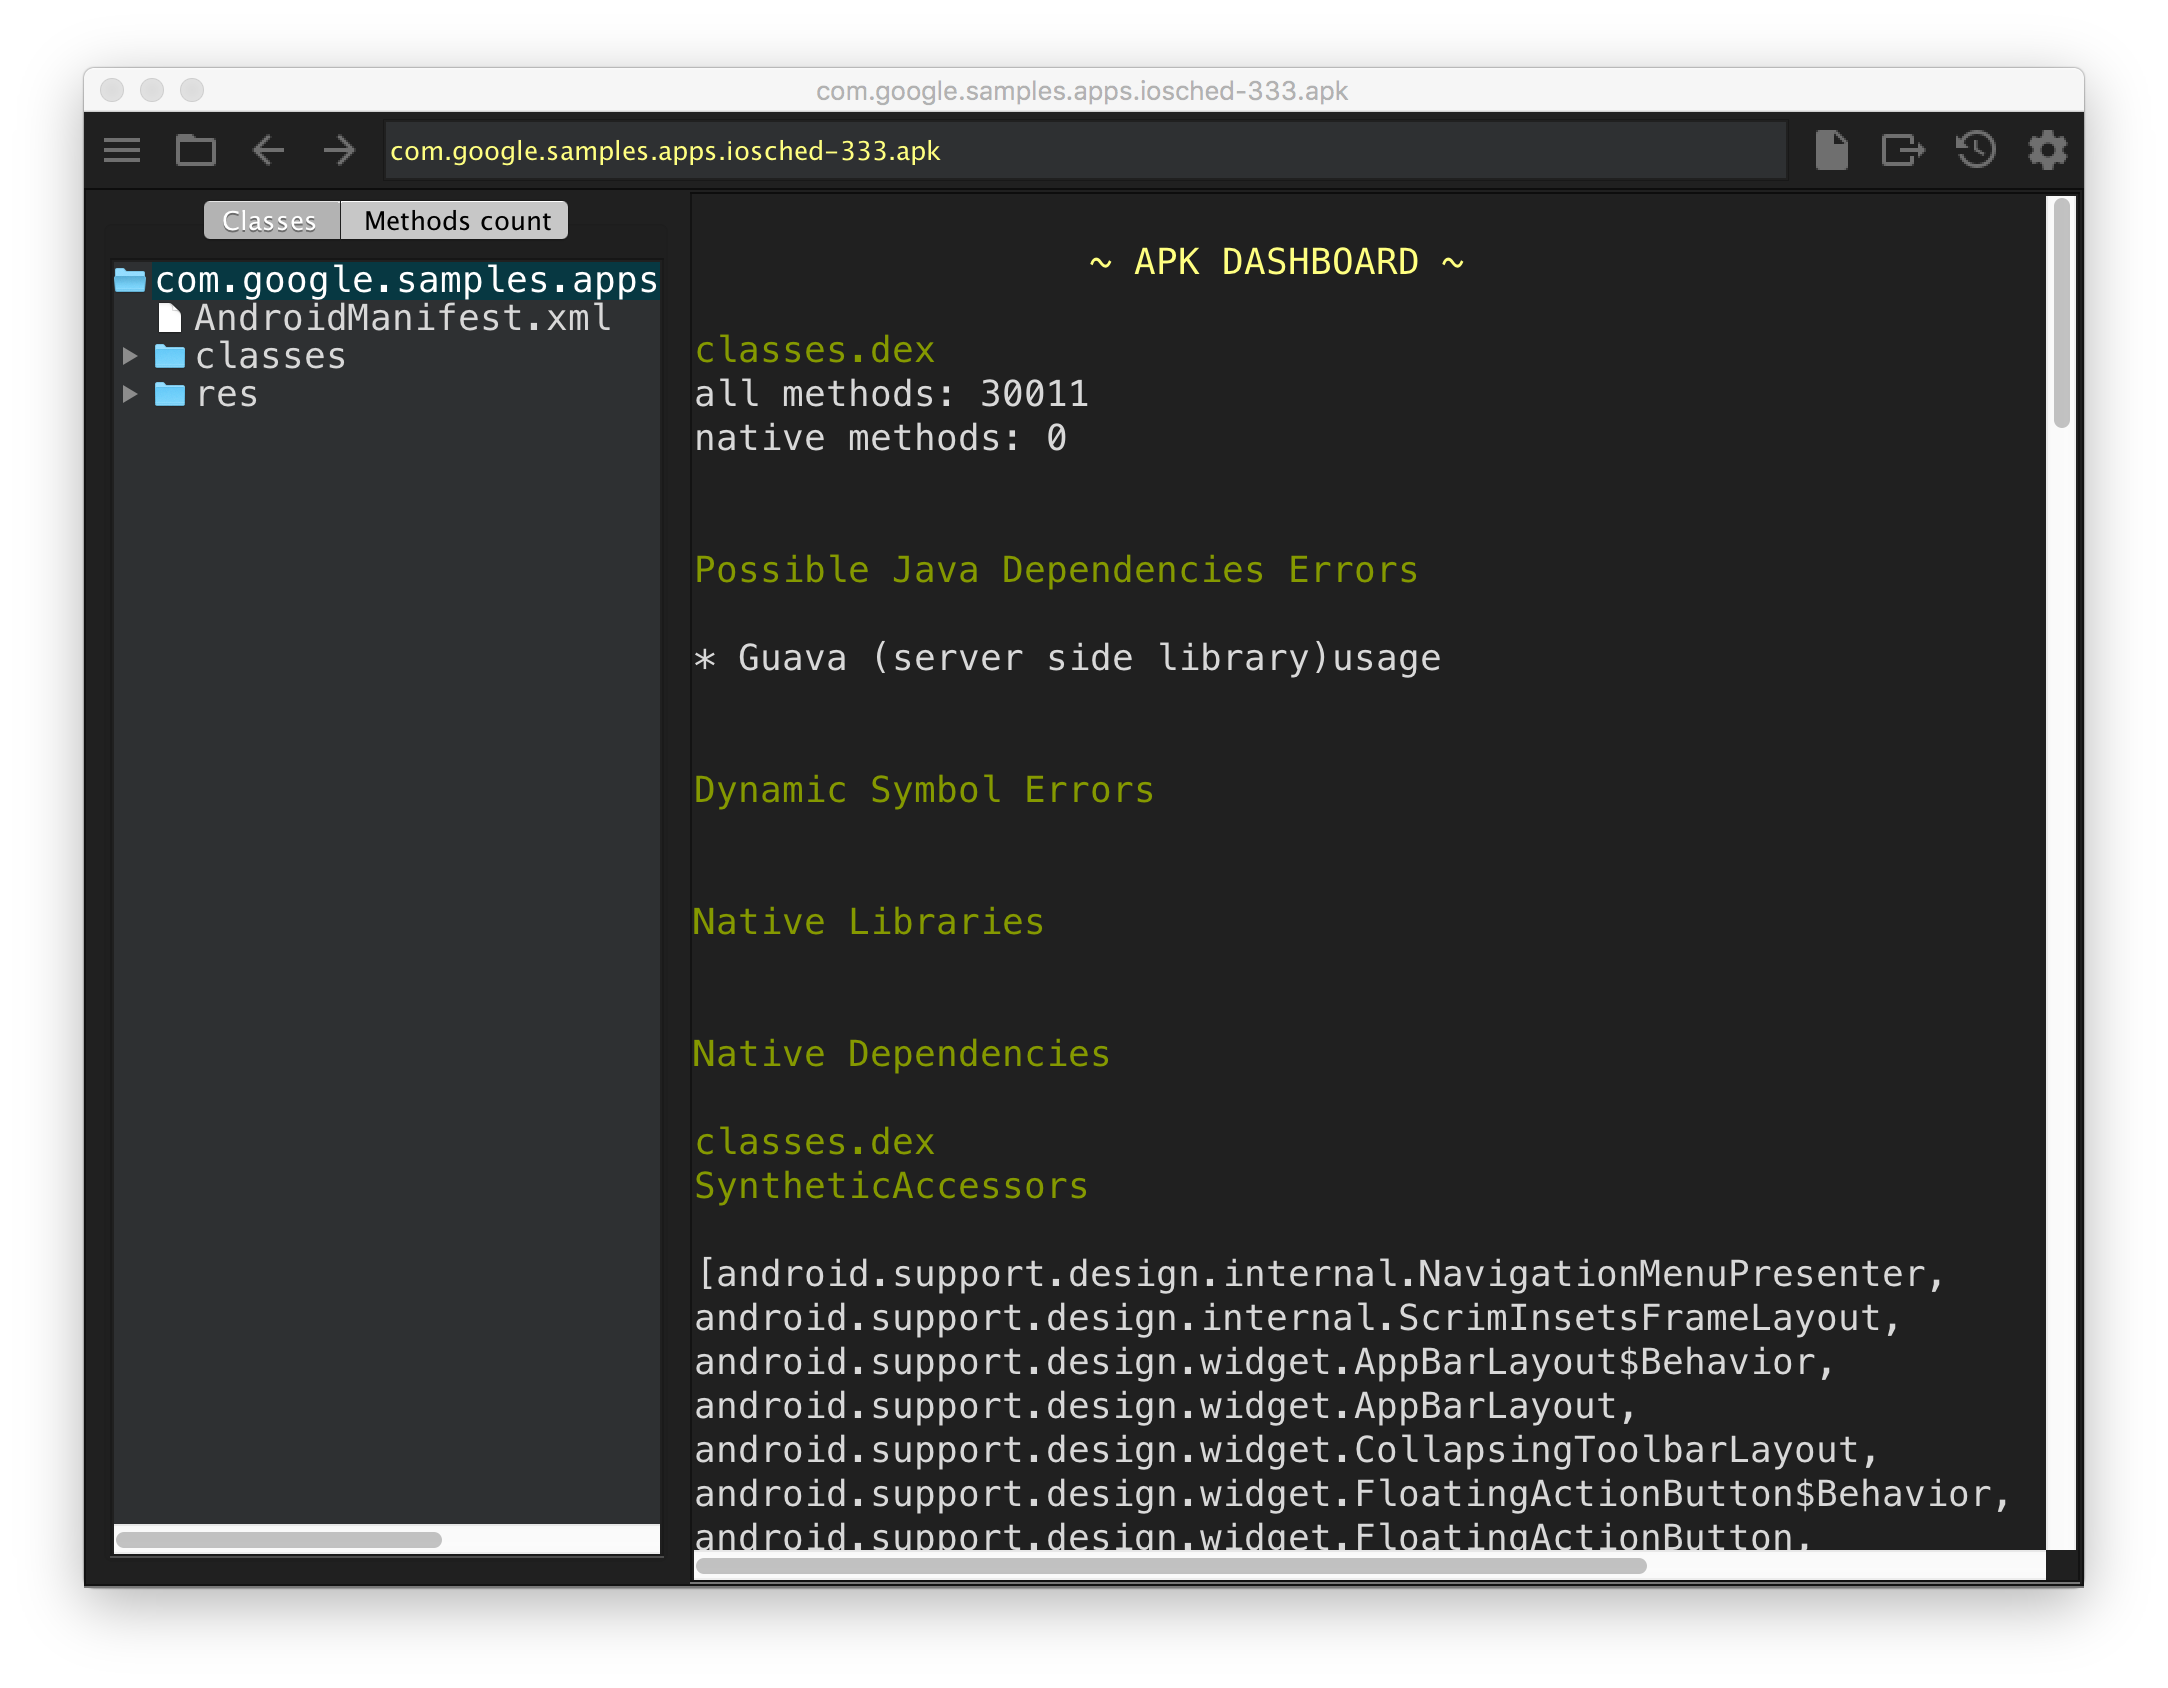 google/android-classyshark
Android and Java bytecode viewer
 abhi-r3v0/adhrit
Android Security Suite for in-depth reconnaissance and static bytecode analysis based on Ghera benchmarks.
 synacktiv/captainhook
Traces user inputs to detect injection vulnerabilities in Java methods via JDWP and Frida, identifying potential command and SQL injection points.
 veridiff/veridiff
Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.
 sensepost/dotnethookertoolkit
Frida-based .NET Framework injector and managed method hooking toolkit for runtime tracing, native entrypoint resolution, and dynamic analysis of…
 frida/frida
Main repo for hosting release binaries