

web2py-e94946d-CVE-2016-3957
 sj/web2py-e94946d-cve-2016-3957
web2py/web2py @ e94946d
authenticationcode-analysisdatabase-security+3
sj/web2py-e94946d-cve-2016-3957web2py/web2py @ e94946d

 nyamort/cve-2024-52301
Proof-of-concept exploit for CVE-2024-52301 demonstrating environment manipulation in Laravel via injected URL parameters, with detailed code…
 nccgroup/android_demystification_toolbox
ADT is a toolset designed to help model application behavior, research and test security vulnerabilities, and facilitate reversing hostile code.
 matesz44/cve-2025-64512
CVE-2025-64512: pdfminer.six pickle deserialization rce; .pickle.gz + pdf generator w/ custom payloads
 inferiorak/cve-2025-55182-react2shell-async-scanner
Async RCE scanner for CVE-2025-55182 / CVE-2025-66478 — prototype-pollution → code execution via React Server Actions.
 kx00007/cve-2026-39938
Detailed CVE-2026-39938 vulnerability report for Cacti ≤1.2.30, demonstrating unauthenticated LFI chained to OS command injection RCE with PoC, root…
 barroqueiro/cve-2023-37941
Exploit on the default cache of superset by using pickle
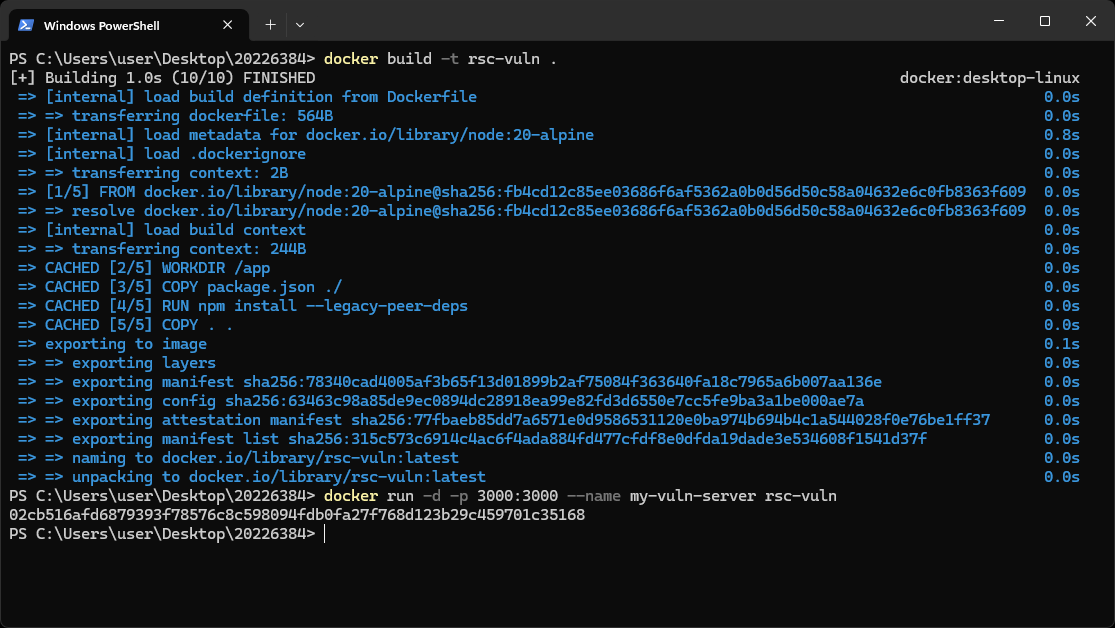
 mahaveer-choudhary/cve-2025-55182
A Python-based security scanner for detecting and exploiting **React Server Components (RSC)** vulnerabilities in Next.js applications. This tool…
 ill-deed/langflow-cve-2025-3248-multi-target
Langflow versions prior to 1.3.0 are susceptible to code injection in the /api/v1/validate/code endpoint. A remote and unauthenticated attacker can…

 benedridge/cve-2021-46703
Simple payload builder