
CVE-2024-39306
 apena-ba/cve-2024-39306
Proof-of-concept exploit for CVE-2024-39306, a SQL injection vulnerability in ChurchCRM <= 5.8.0 that allows authenticated remote code execution.…
code-analysisexploitationpenetration-testing+2
1
apena-ba/cve-2024-39306Proof-of-concept exploit for CVE-2024-39306, a SQL injection vulnerability in ChurchCRM <= 5.8.0 that allows authenticated remote code execution.…
 apena-ba/cve-2024-39304
Proof-of-concept exploit for CVE-2024-39304, a SQL injection vulnerability in ChurchCRM, allowing authenticated attackers to execute arbitrary SQL…
 bi-zone/cve-2024-7965
This repository contains PoC for CVE-2024-7965. This is the vulnerability in the V8 that occurs only within ARM64.
 rat-c/cve-2024-1512
PoC for CVE-2024-1512 in MasterStudy LMS WordPress Plugin.
 eqstlab/cve-2024-23998
PoC for CVE-2024-23998
 nollium/cve-2024-9264
Exploit for Grafana arbitrary file-read and RCE (CVE-2024-9264)
 ianthinus/cve-2024-4577
Proof-of-concept exploit for CVE-2024-4577, a PHP CGI argument injection vulnerability enabling remote code execution via crafted HTTP requests.
 itzsh4dowxz/cve-2024-37032-poc
CVE-2024-37032 (Probllama) PoC for Ollama ≤0.1.33: path traversal and arbitrary file write via model digest handling, leading to automated privilege…
 jacklosingheart/ghsa-4cx5-89vm-833x-poc
GHSA-4cx5-89vm-833x/CVE-2024-52800
 jacklosingheart/cve-2024-55875
CVE-2024-55875 | GHSA-7mj5-hjjj-8rgw | http4k first CVE
 ptrstr/cve-2024-32830-poc
PoC code to download files with CVE-2024-32830
 funcid/cve-2024-38828
PoC and fix for CVE-2024-38828: Spring Framework DoS via Content-Length manipulation in ByteArrayHttpMessageConverter. Includes load testing,…
 canyie/magiskeop
Exploit and writeup for installed app to root privilege escalation through CVE-2024-48336 (Magisk Bug #8279), Privileges Escalation / Arbitrary Code…
 p33d/cve-2024-43363
Python exploit script to test Cacti instances for CVE-2024-43363 RCE via log poisoning. Checks version, injects PHP payload into device names, and…
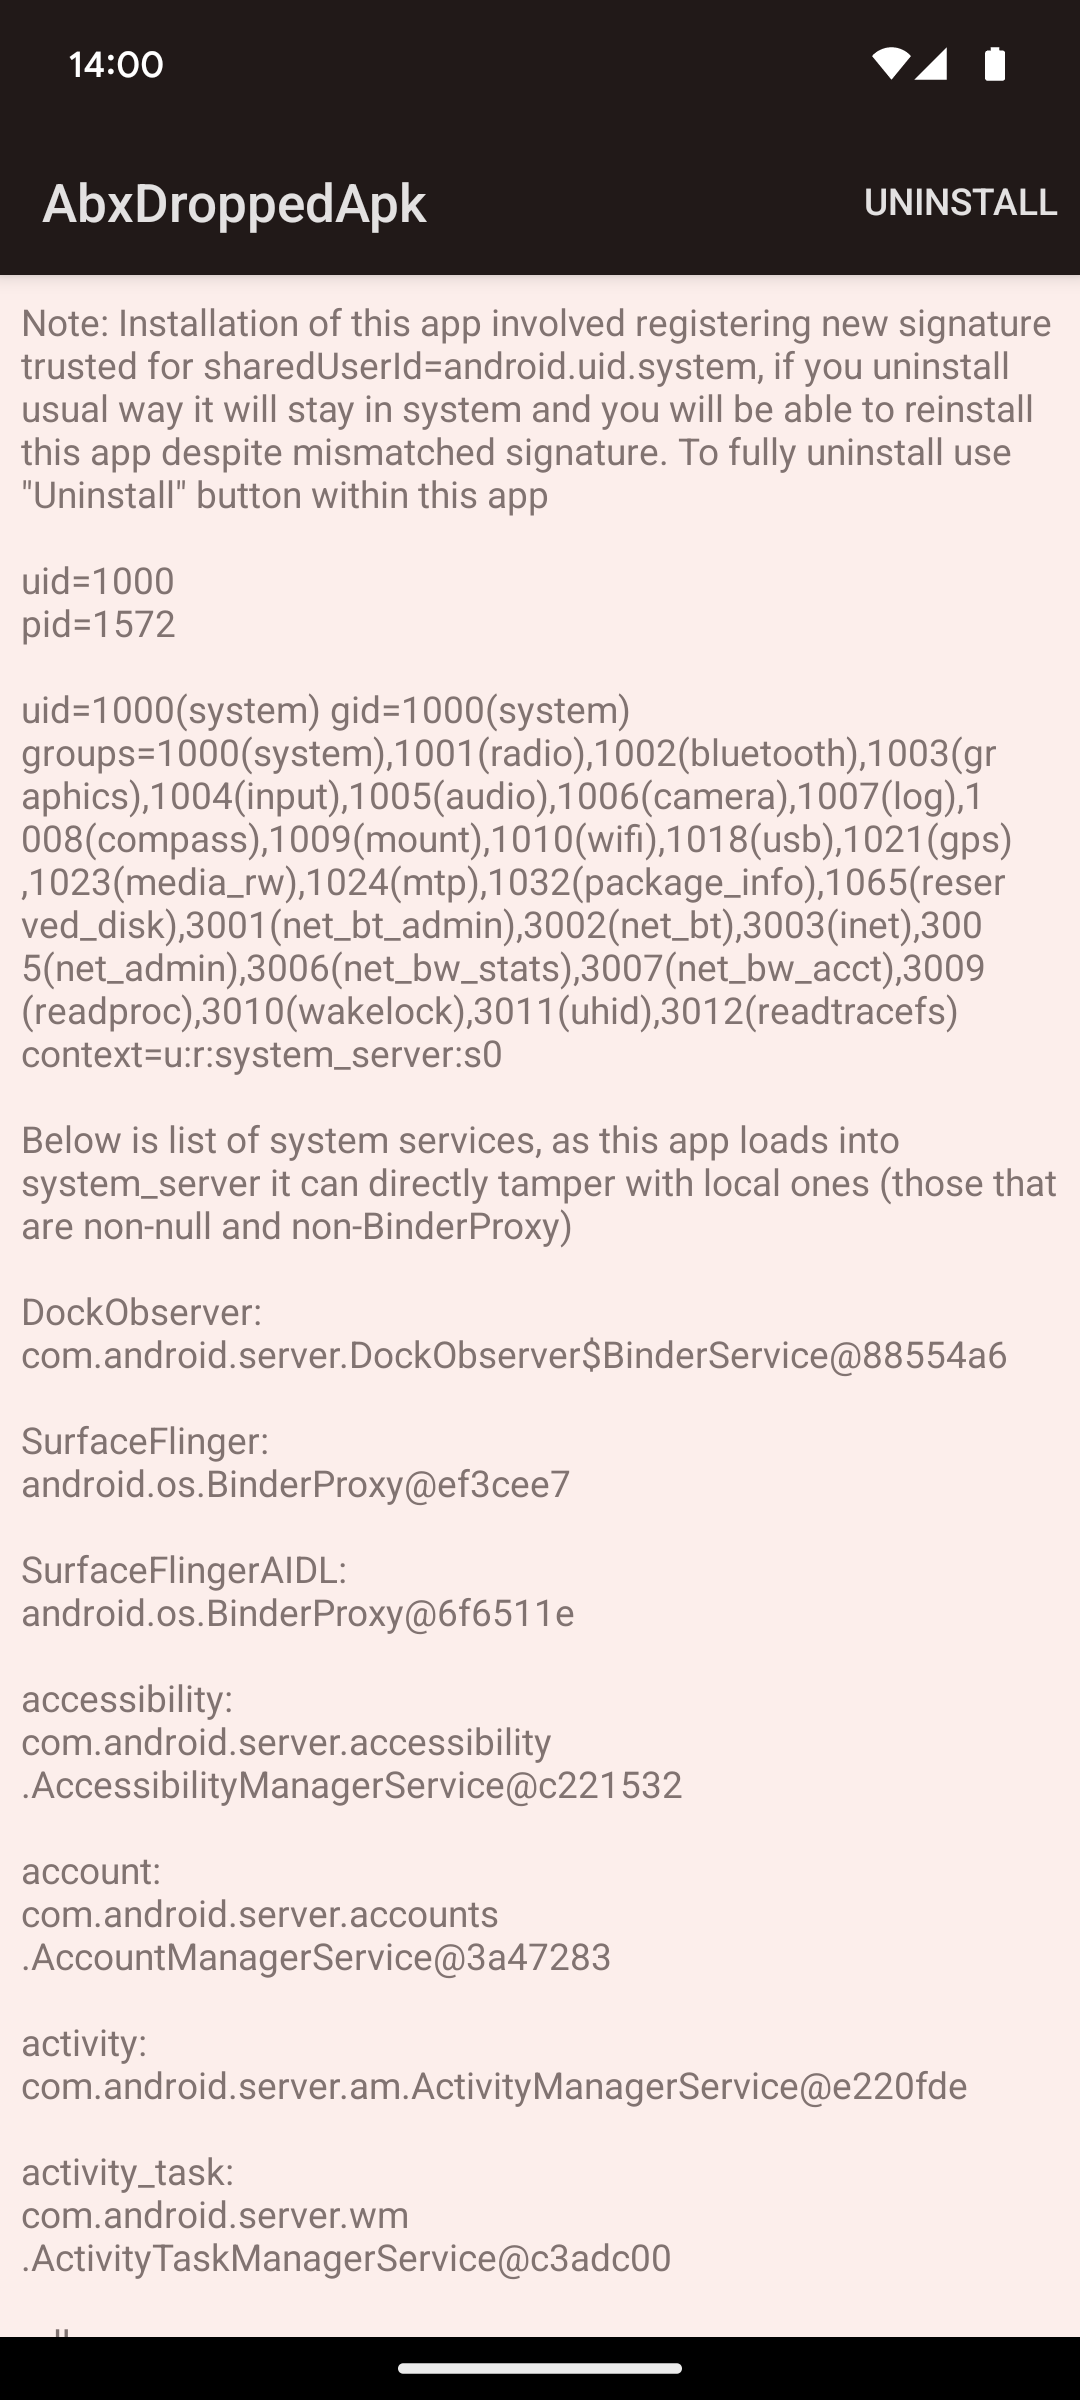 michalbednarski/abxoverflow
Writeup and exploit for CVE-2024-34740, integer overflow in Android's BinaryXmlSerializer to system_server file write and then to system_server code…
 savagesanta11/reproduce-cve-2024-21513
Demonstrates CVE-2024-21513 in langchain-experimental, showing arbitrary code execution via VectorSQLDatabaseChain's eval() on retrieved values.…
 taiyou-tw/cve-2024-40445_cve-2024-40446
This repository serves as the public reference for CVE-2024-40445 and CVE-2024-40446. Both vulnerabilities impact MimeTeX, an open-source software…