
CVE-2026-25747
 oscerd/cve-2026-25747
CVE-2026-25747 - Camel LevelDB Deserialization Vulnerability
code-analysiseducationexploitation+3
oscerd/cve-2026-25747CVE-2026-25747 - Camel LevelDB Deserialization Vulnerability
 hopsypopsy8/cve-2024-53677-exploitation
Step-by-step walkthrough for exploiting Apache Struts CVE-2024-53677 RCE via file upload manipulation, including OGNL injection, payload embedding,…
 p33d/cve-2024-43363
Python exploit script to test Cacti instances for CVE-2024-43363 RCE via log poisoning. Checks version, injects PHP payload into device names, and…
 canyie/magiskeop
Exploit and writeup for installed app to root privilege escalation through CVE-2024-48336 (Magisk Bug #8279), Privileges Escalation / Arbitrary Code…
 nollium/cve-2024-9264
Exploit for Grafana arbitrary file-read and RCE (CVE-2024-9264)
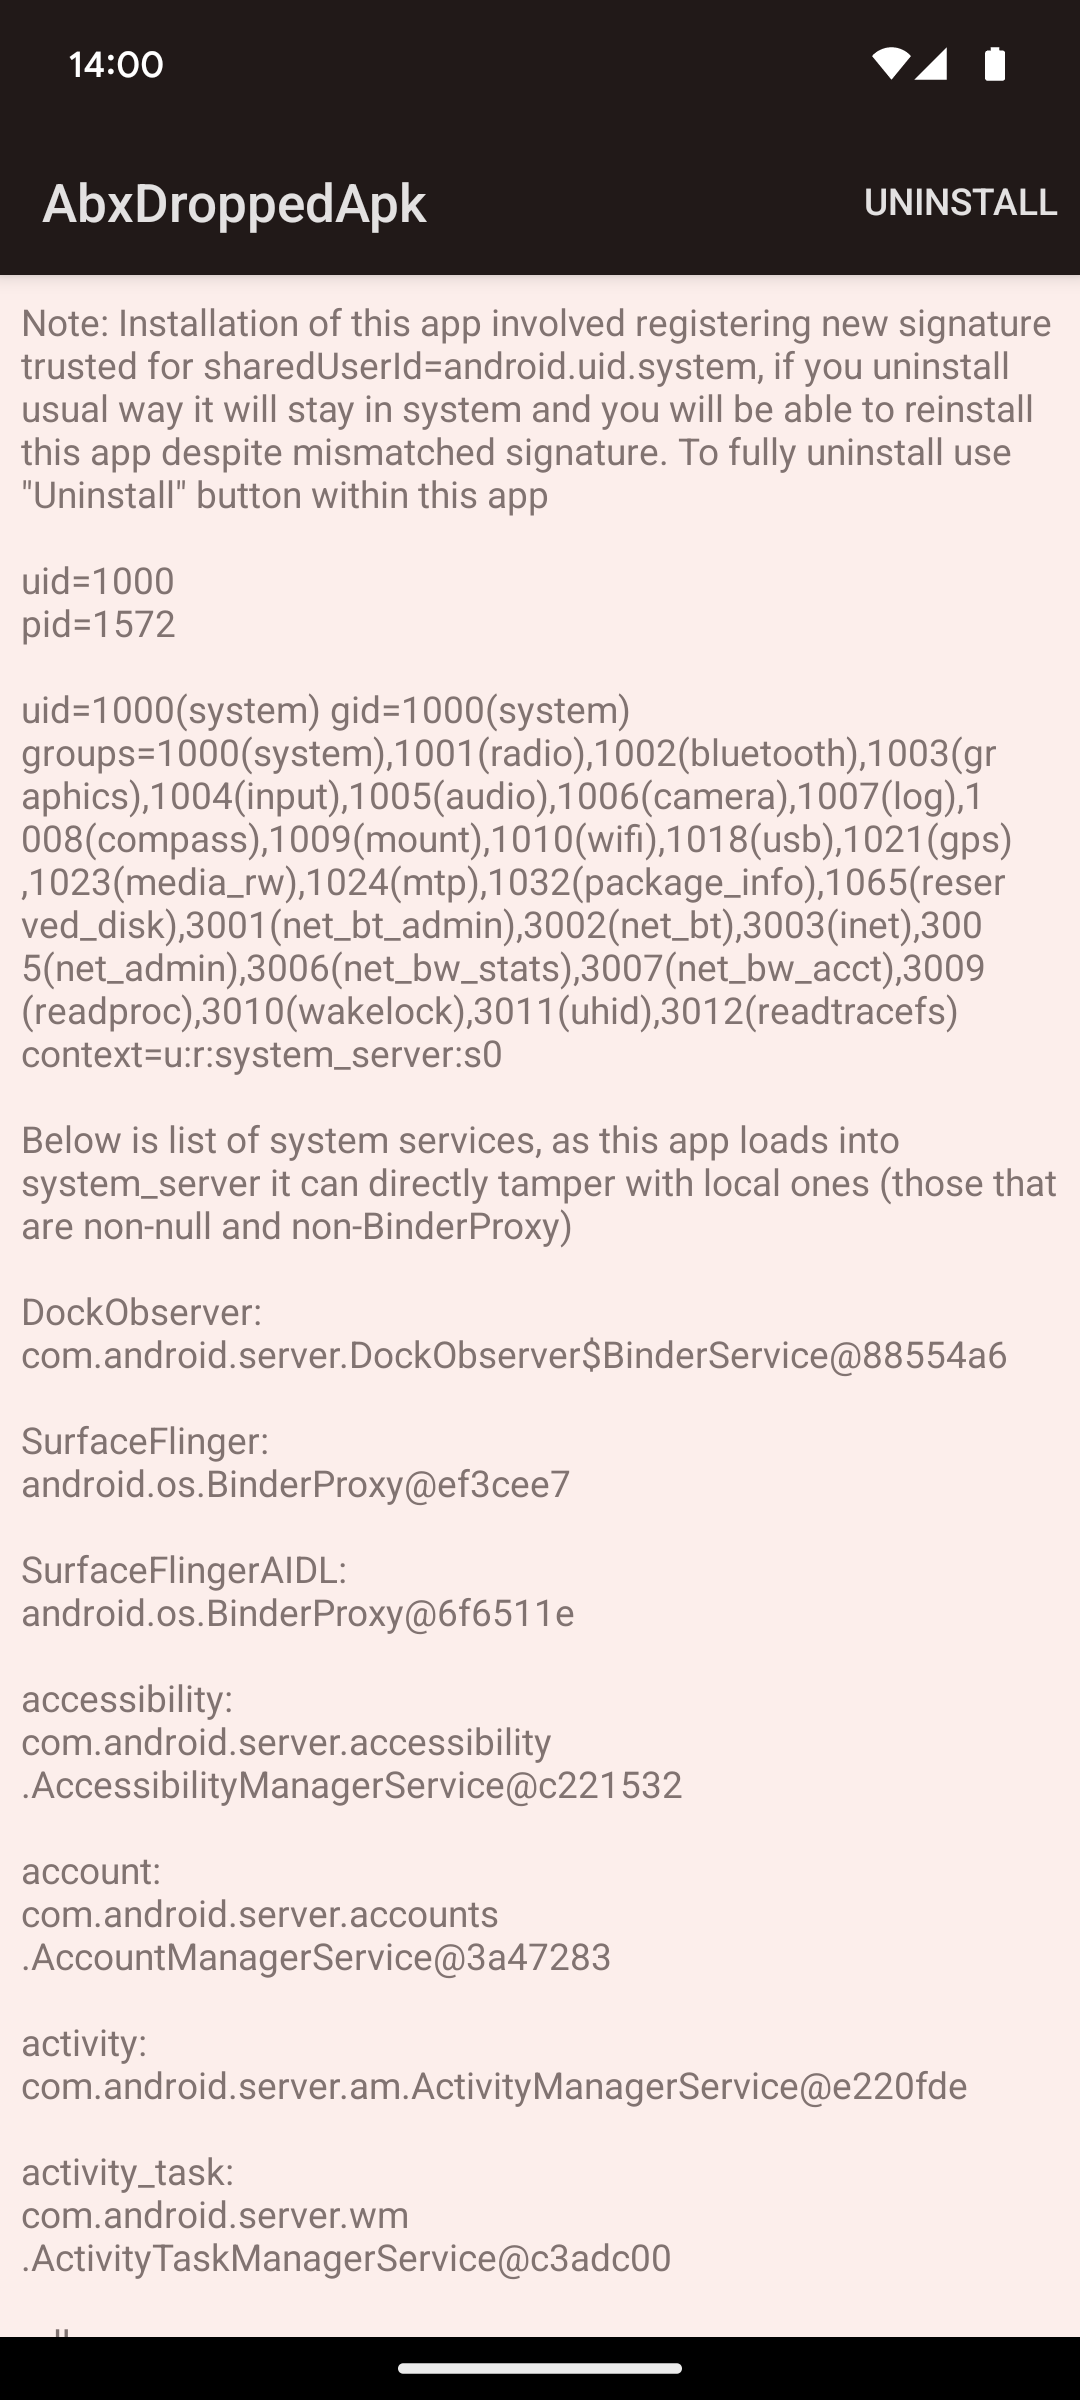 michalbednarski/abxoverflow
Writeup and exploit for CVE-2024-34740, integer overflow in Android's BinaryXmlSerializer to system_server file write and then to system_server code…
 nyamort/cve-2024-52301
Proof-of-concept exploit for CVE-2024-52301 demonstrating environment manipulation in Laravel via injected URL parameters, with detailed code…
 aelmokhtar/cve-2024-34716
Proof-of-concept exploit for CVE-2024-34716, a PNG-driven XSS to RCE chain in PrestaShop 8.1.5, enabling remote code execution via crafted image…
 vesjolyjd/kaspersky_cve-2024-3094
Security review of CVE-2024-3094 (XZ Utils backdoor) including threat modeling, static/dynamic code analysis, fuzzing with AFL++, and a…
 apena-ba/cve-2024-39306
Proof-of-concept exploit for CVE-2024-39306, a SQL injection vulnerability in ChurchCRM <= 5.8.0 that allows authenticated remote code execution.…
 bohemianhacks/cve-2024-21534-poc
Proof-of-concept exploit for CVE-2024-21534, a critical RCE in jsonpath-plus, demonstrating arbitrary code execution via the VM module and providing…
 ronf98/cve-2024-11972-poc
CVE-2024-11972 in Hunk Companion <1.9.0 allows unauthenticated attackers to exploit insecure REST API endpoints and install vulnerable plugins,…
 ltranquility/cve-2024-21644-poc
Proof-of-concept exploit for CVE-2024-21644, demonstrating remote code execution vulnerability with Python-based automation and colored output.
 apena-ba/cve-2024-39304
Proof-of-concept exploit for CVE-2024-39304, a SQL injection vulnerability in ChurchCRM, allowing authenticated attackers to execute arbitrary SQL…
 kadamnayan/poc-cve-2024-38820
Proof-of-concept exploit for CVE-2024-38820, demonstrating locale-dependent case conversion bypass of Spring Framework DataBinder disallowedFields…
 ianthinus/cve-2024-4577
Proof-of-concept exploit for CVE-2024-4577, a PHP CGI argument injection vulnerability enabling remote code execution via crafted HTTP requests.
 h4ckr4v3n/cve-2024-46209
Security research repository detailing CVE-2024-46209 (authenticated RCE) and CVE-2024-46210 (stored XSS via file upload) in Redaxo CMS v5.17.1, with…
 savagesanta11/reproduce-cve-2024-21513
Demonstrates CVE-2024-21513 in langchain-experimental, showing arbitrary code execution via VectorSQLDatabaseChain's eval() on retrieved values.…