
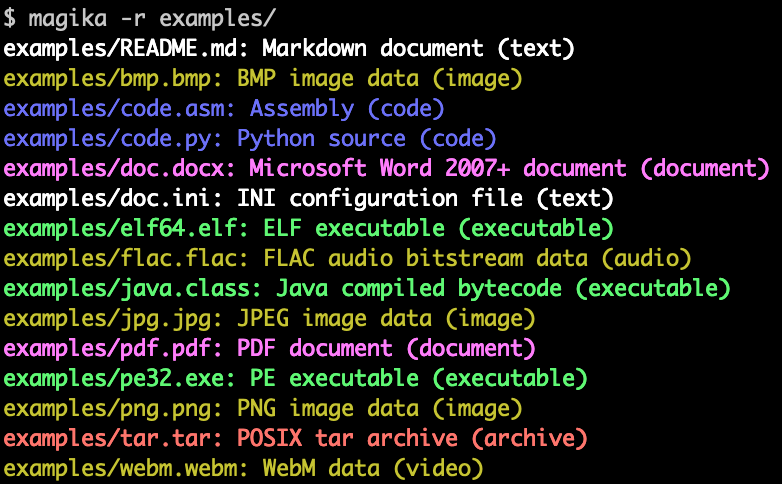
magika
 google/magika
Fast and accurate AI powered file content types detection
code-analysisforensicsgeneral-purpose-utilities+3
google/magikaFast and accurate AI powered file content types detection
 ewenquim/entropy
CLI tool that scans codebases for high-entropy lines to detect potential secrets, with customizable file extension and top-N filtering.
 firelock-ai/kin
Semantic graph-based version control for AI-written code. Tracks entities and relations instead of file diffs, enabling blast radius analysis, shadow…
 luelueking/cve-2022-25845-in-spring
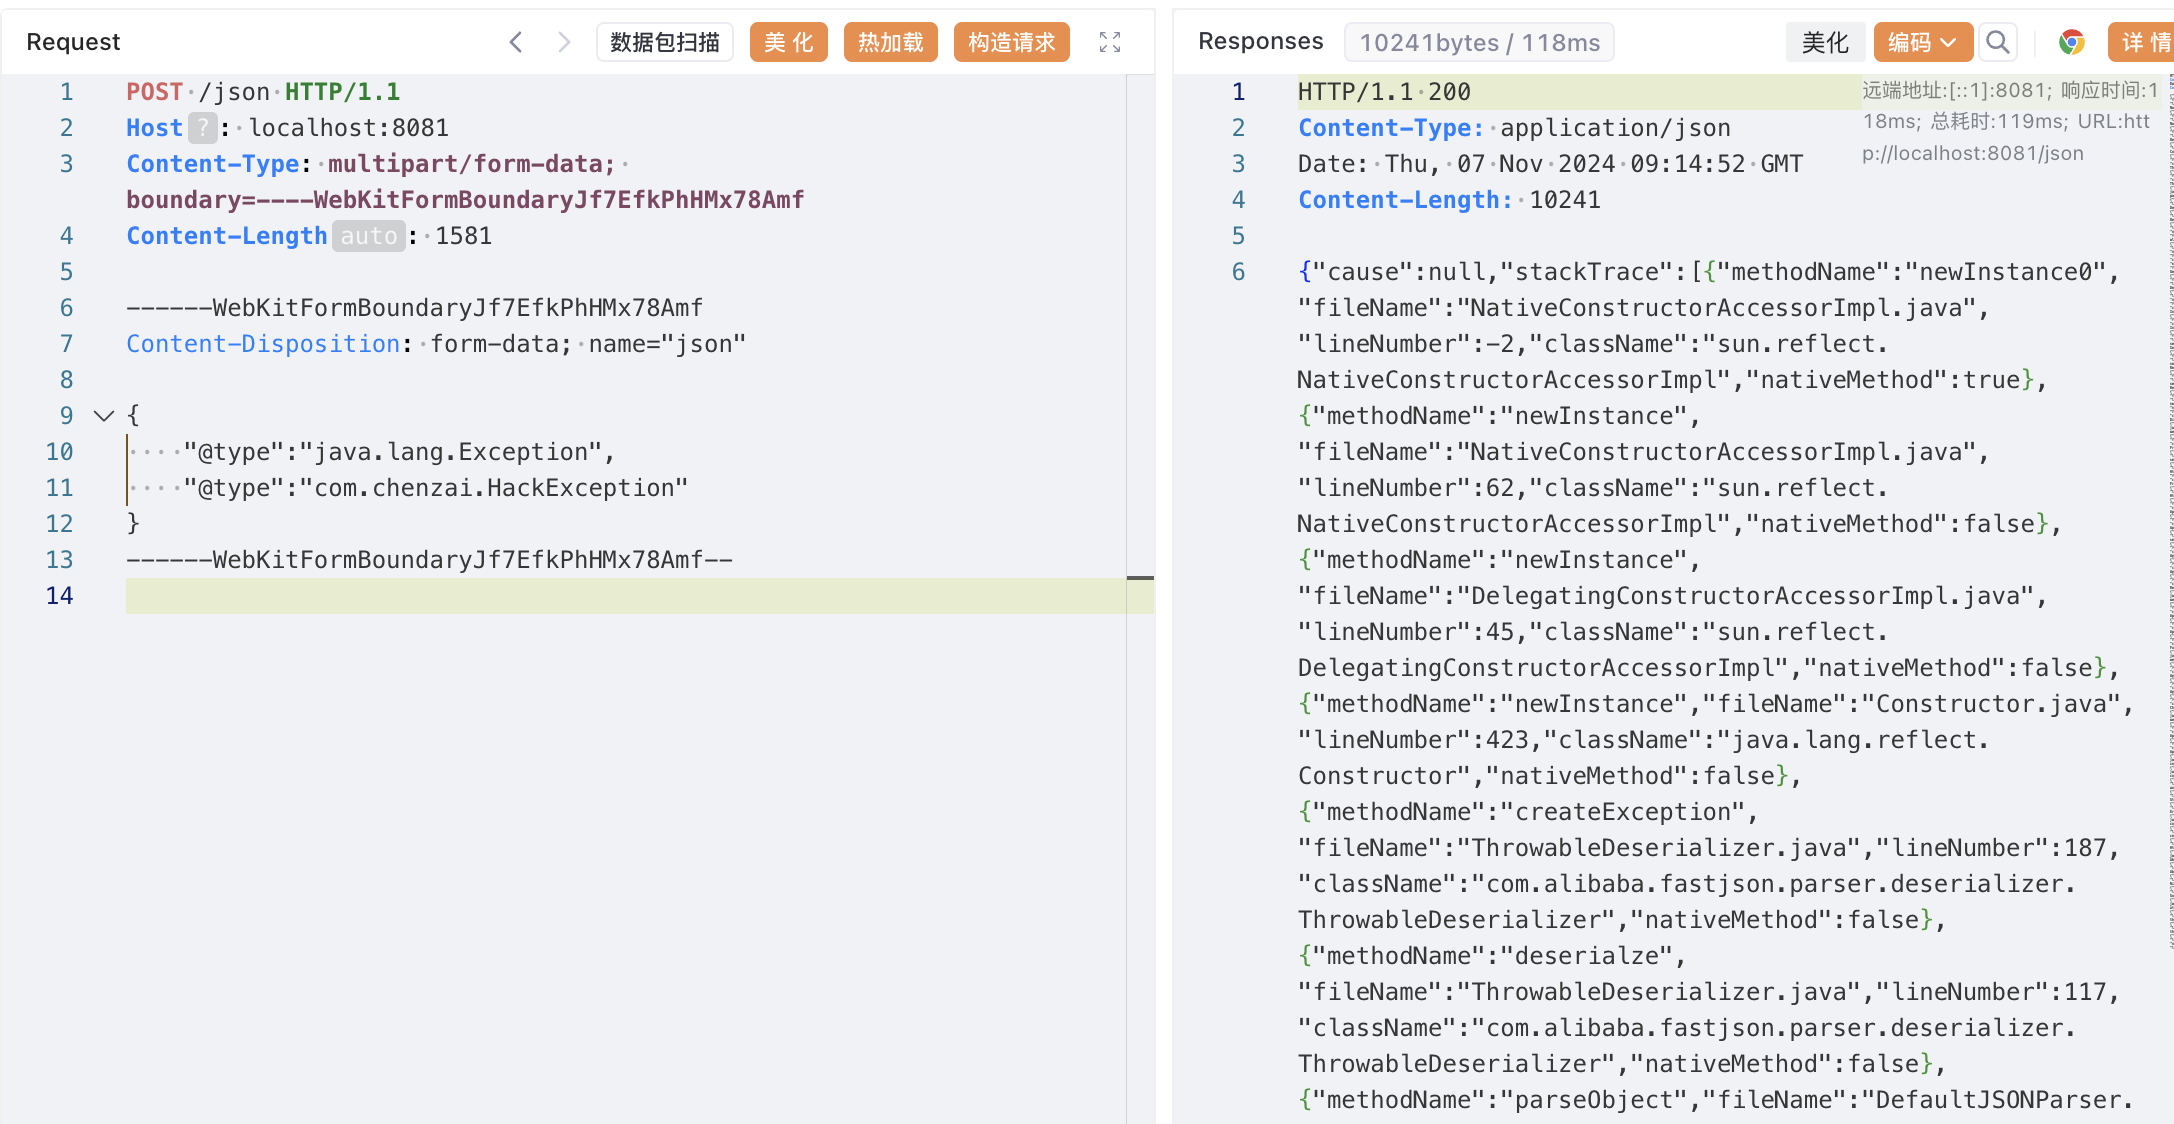
CVE-2022-25845 (fastjson 1.2.80) exploit for Spring environments with step-by-step PoC, file read, and arbitrary file write via Jackson/commons-io…
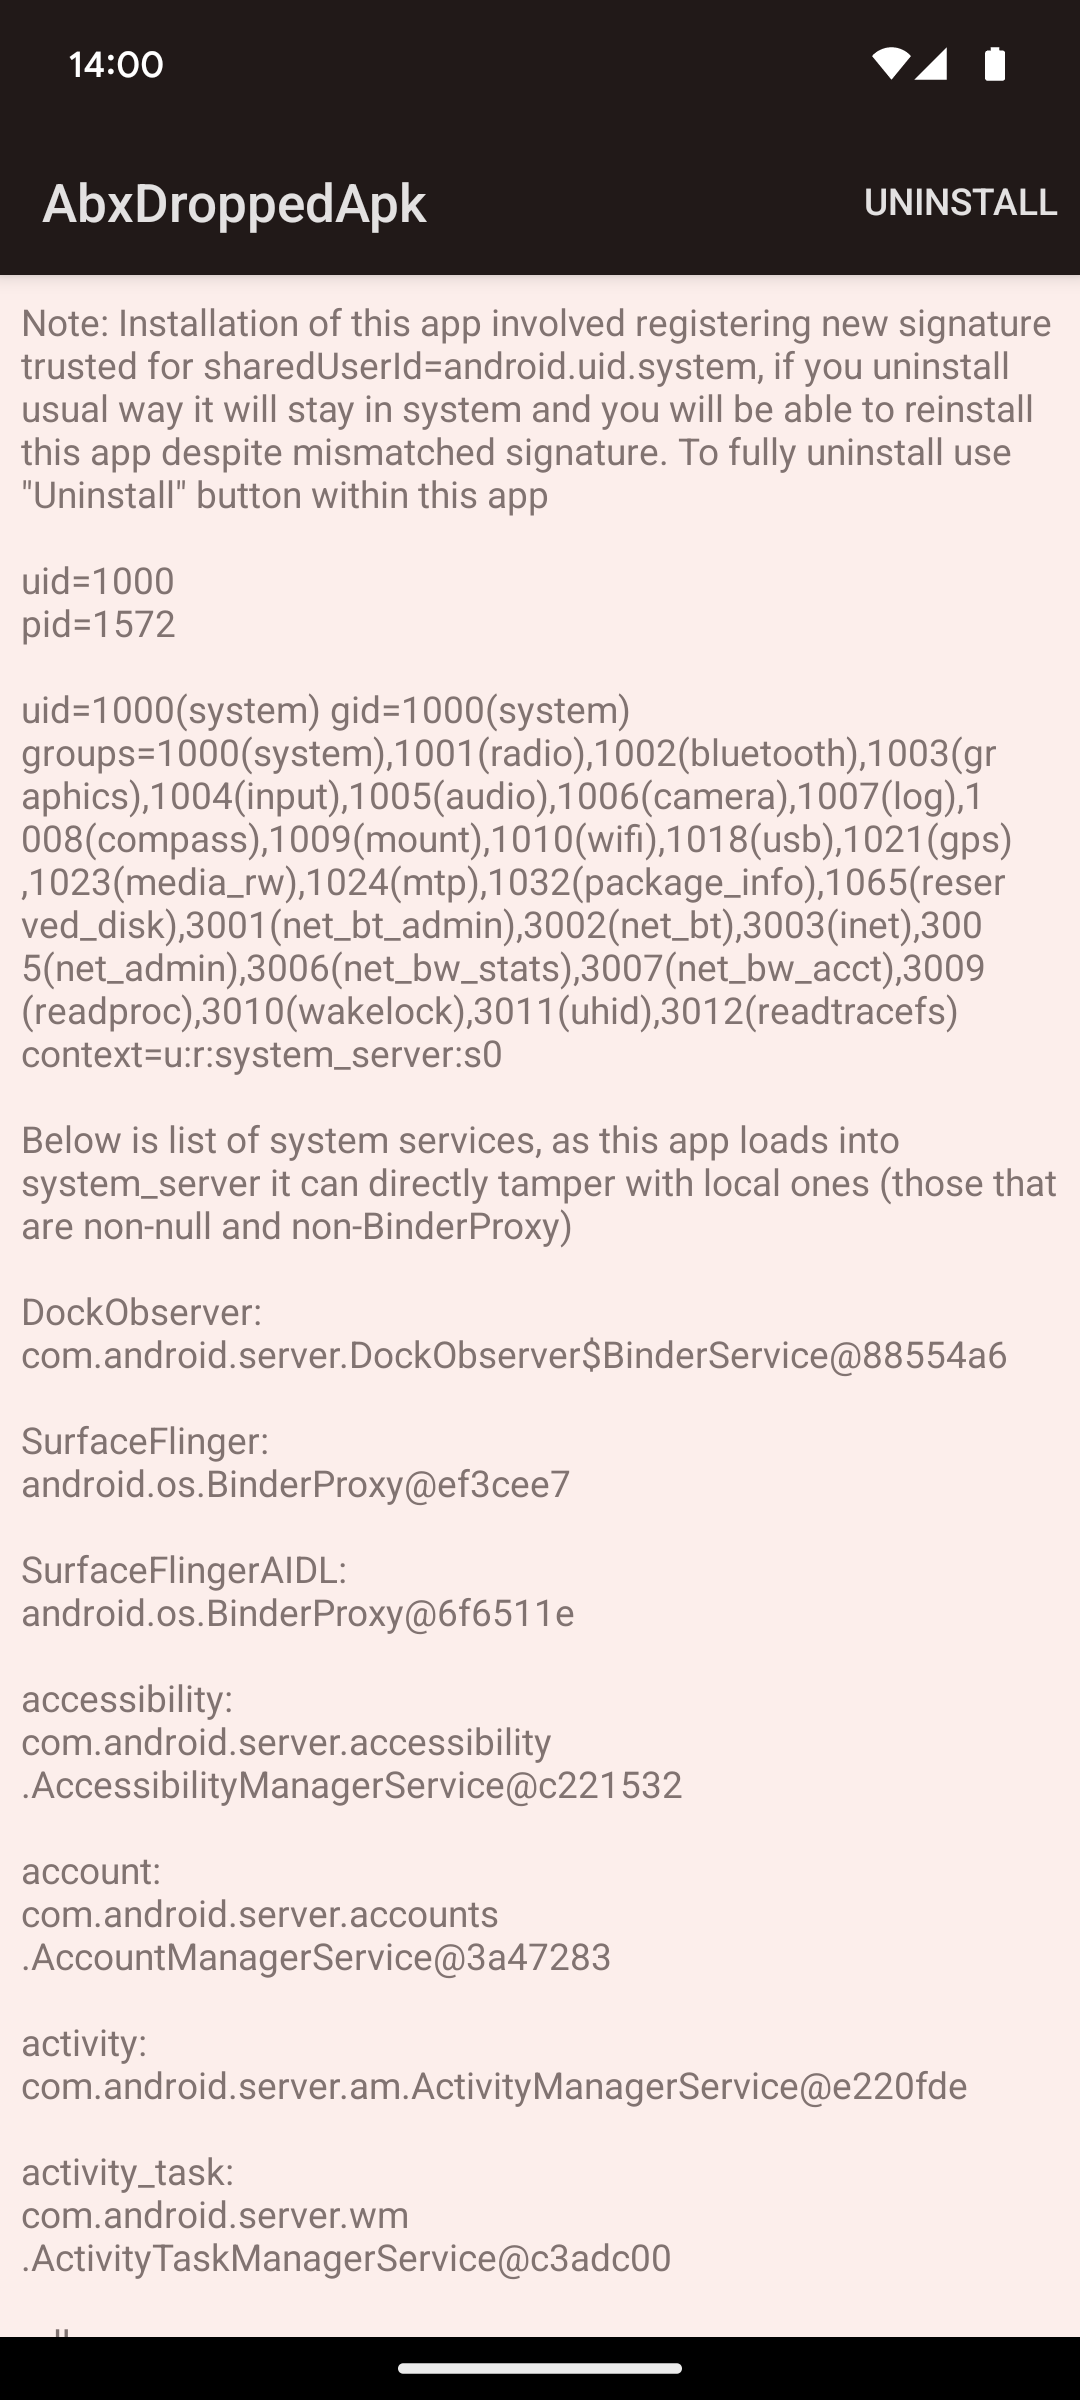 michalbednarski/abxoverflow
Writeup and exploit for CVE-2024-34740, integer overflow in Android's BinaryXmlSerializer to system_server file write and then to system_server code…
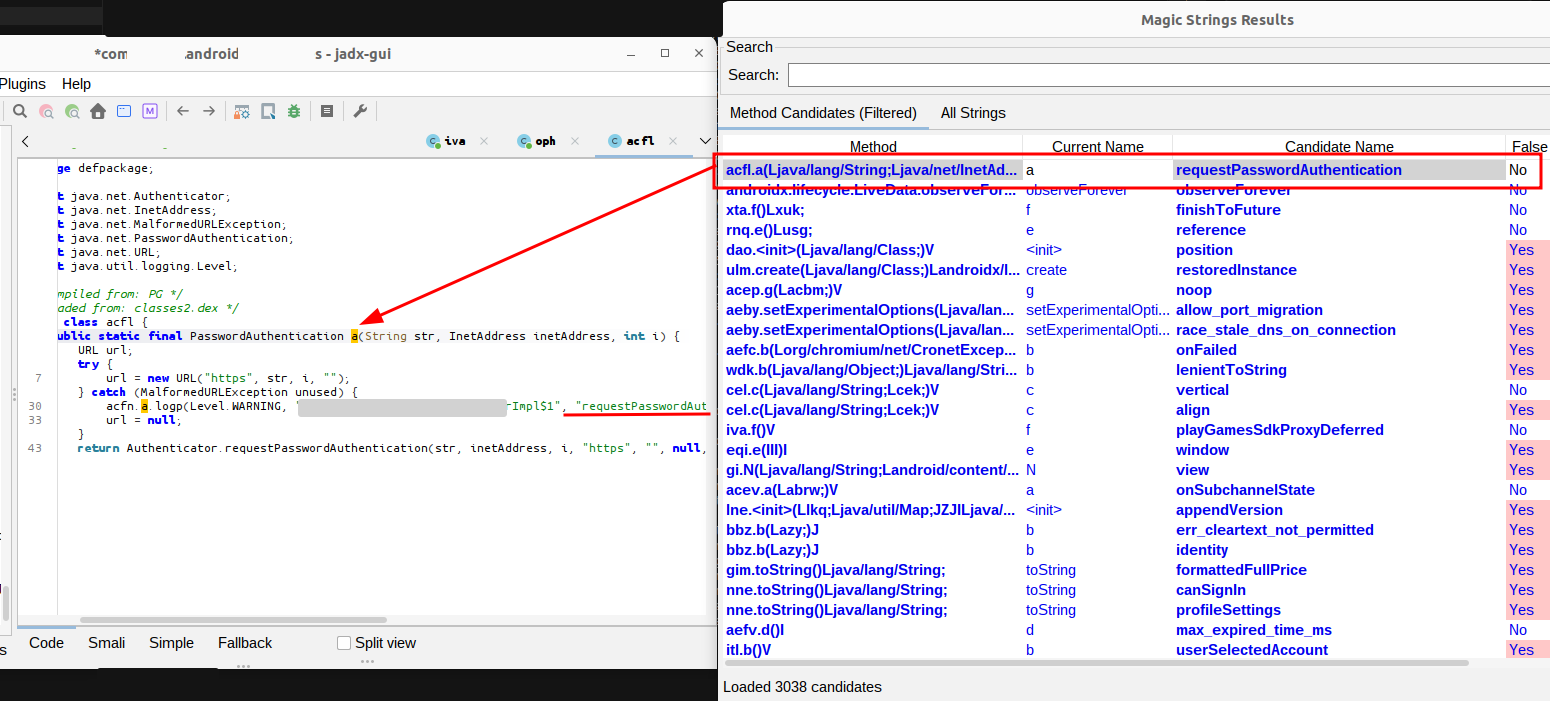 0rshemesh/jadx-magic-strings
JADX plugin that extracts method names, class references, and source file paths from string constants found in DEX files and decompiled Android code.
 oxsecurity/codetotal
Analyze any snippet, file, or repository to detect possible security flaws such as secret in code, open source vulnerability, code security,…
 jra89/cve-2019-19634
This is a filter bypass exploit that results in arbitrary file upload and remote code execution in class.upload.php <= 2.0.4
 m4sh-wacker/cve-2026-3891-pix-for-woocommerce-plugin-exploit
PoC for CVE-2026-3891 — Unauthenticated Arbitrary File Upload leading to Remote Code Execution in Pix for WooCommerce <= 1.5.0
 alfarom256/cve-2022-45451
PoC for Acronis Arbitrary File Read - CVE-2022-45451
 jas502n/cve-2020-26259
CVE-2020-26259: XStream is vulnerable to an Arbitrary File Deletion on the local host when unmarshalling as long as the executing process has…
 papageo75/cve-2026-48908-poc
Unauthenticated RCE PoC for CVE-2026-48908 — SP Page Builder for Joomla (≤ 6.6.1): arbitrary file upload via asset.uploadCustomIcon. Self-cleaning,…
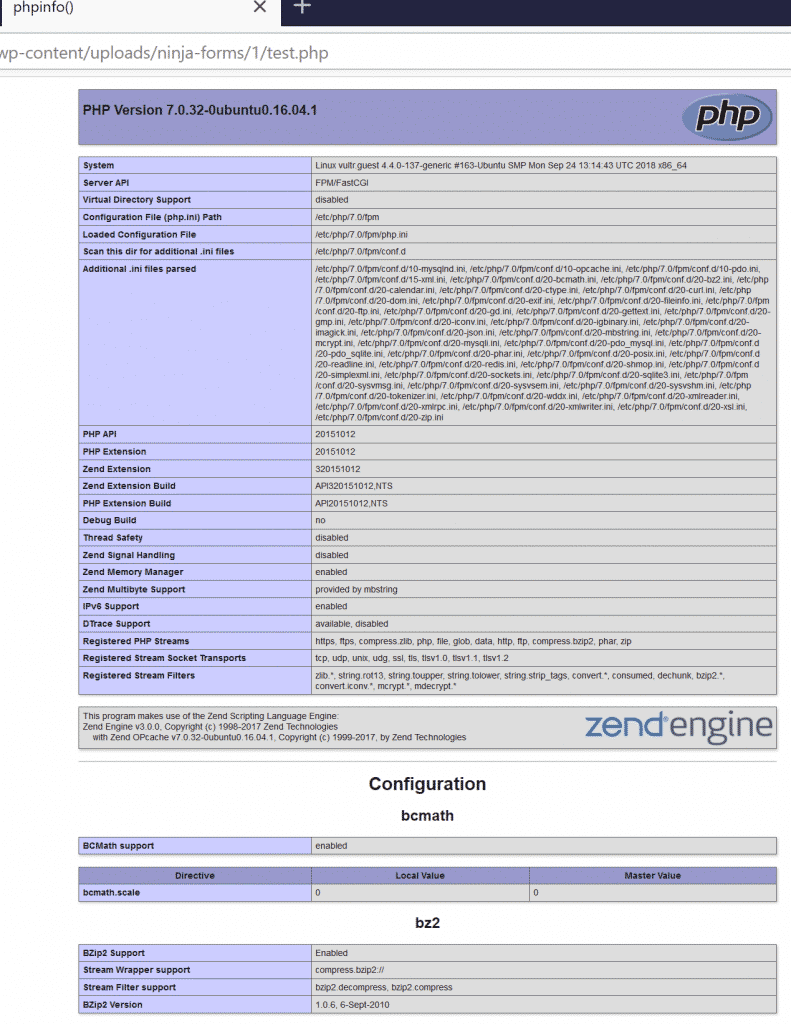 ktn1990/cve-2019-10869
(Wordpress) Ninja Forms File Uploads Extension <= 3.0.22 – Unauthenticated Arbitrary File Upload
 jra89/cve-2019-19576
This is a filter bypass exploit that results in arbitrary file upload and remote code execution in class.upload.php <= 2.0.3
 hunntr/cve-2023-46818
An issue was discovered in ISPConfig before 3.2.11p1. PHP code injection can be achieved in the language file editor by an admin if…
 itzsh4dowxz/cve-2024-37032-poc
CVE-2024-37032 (Probllama) PoC for Ollama ≤0.1.33: path traversal and arbitrary file write via model digest handling, leading to automated privilege…
 0x240x23elu/cve-2020-28948-and-cve-2020-28949
Proof-of-concept demonstration for CVE-2020-28948 and CVE-2020-28949, PHP Archive_Tar path traversal and arbitrary file write vulnerabilities.
 romain-deperne/cve-2026-77262
Proof-of-concept exploit for arbitrary file read in mcp-atlassian via path traversal in confluence_upload_attachment, with analysis and reproduction…