

githubFind3r
 atmoner/githubfind3r
Command-line tool for fast searching of GitHub repositories, users, and commits to gather open-source intelligence and code-related information.
code-analysisinformation-gatheringosint+1
29
atmoner/githubfind3rCommand-line tool for fast searching of GitHub repositories, users, and commits to gather open-source intelligence and code-related information.
 josue87/givemesecrets
Use regular expressions to get sensitive information from a given repository (GitHub, pip or npm).
 jacklosingheart/cve-2024-51132-poc
Proof-of-concept exploit for CVE-2024-51132, an XML External Entity (XXE) injection vulnerability in HAPI FHIR core libraries, enabling SSRF and…
 unicorn-hyh/cve-2026-31156
There is a path injection vulnerability in OpenPLC-v3, which arises from the program not performing any validity checks on the file path parameters…
 joaosilva21/cve-2024-43018
Proof-of-concept for CVE-2024-43018: SQL injection in Piwigo 13.8.0 via unsanitized max_level and min_register parameters, enabling information…
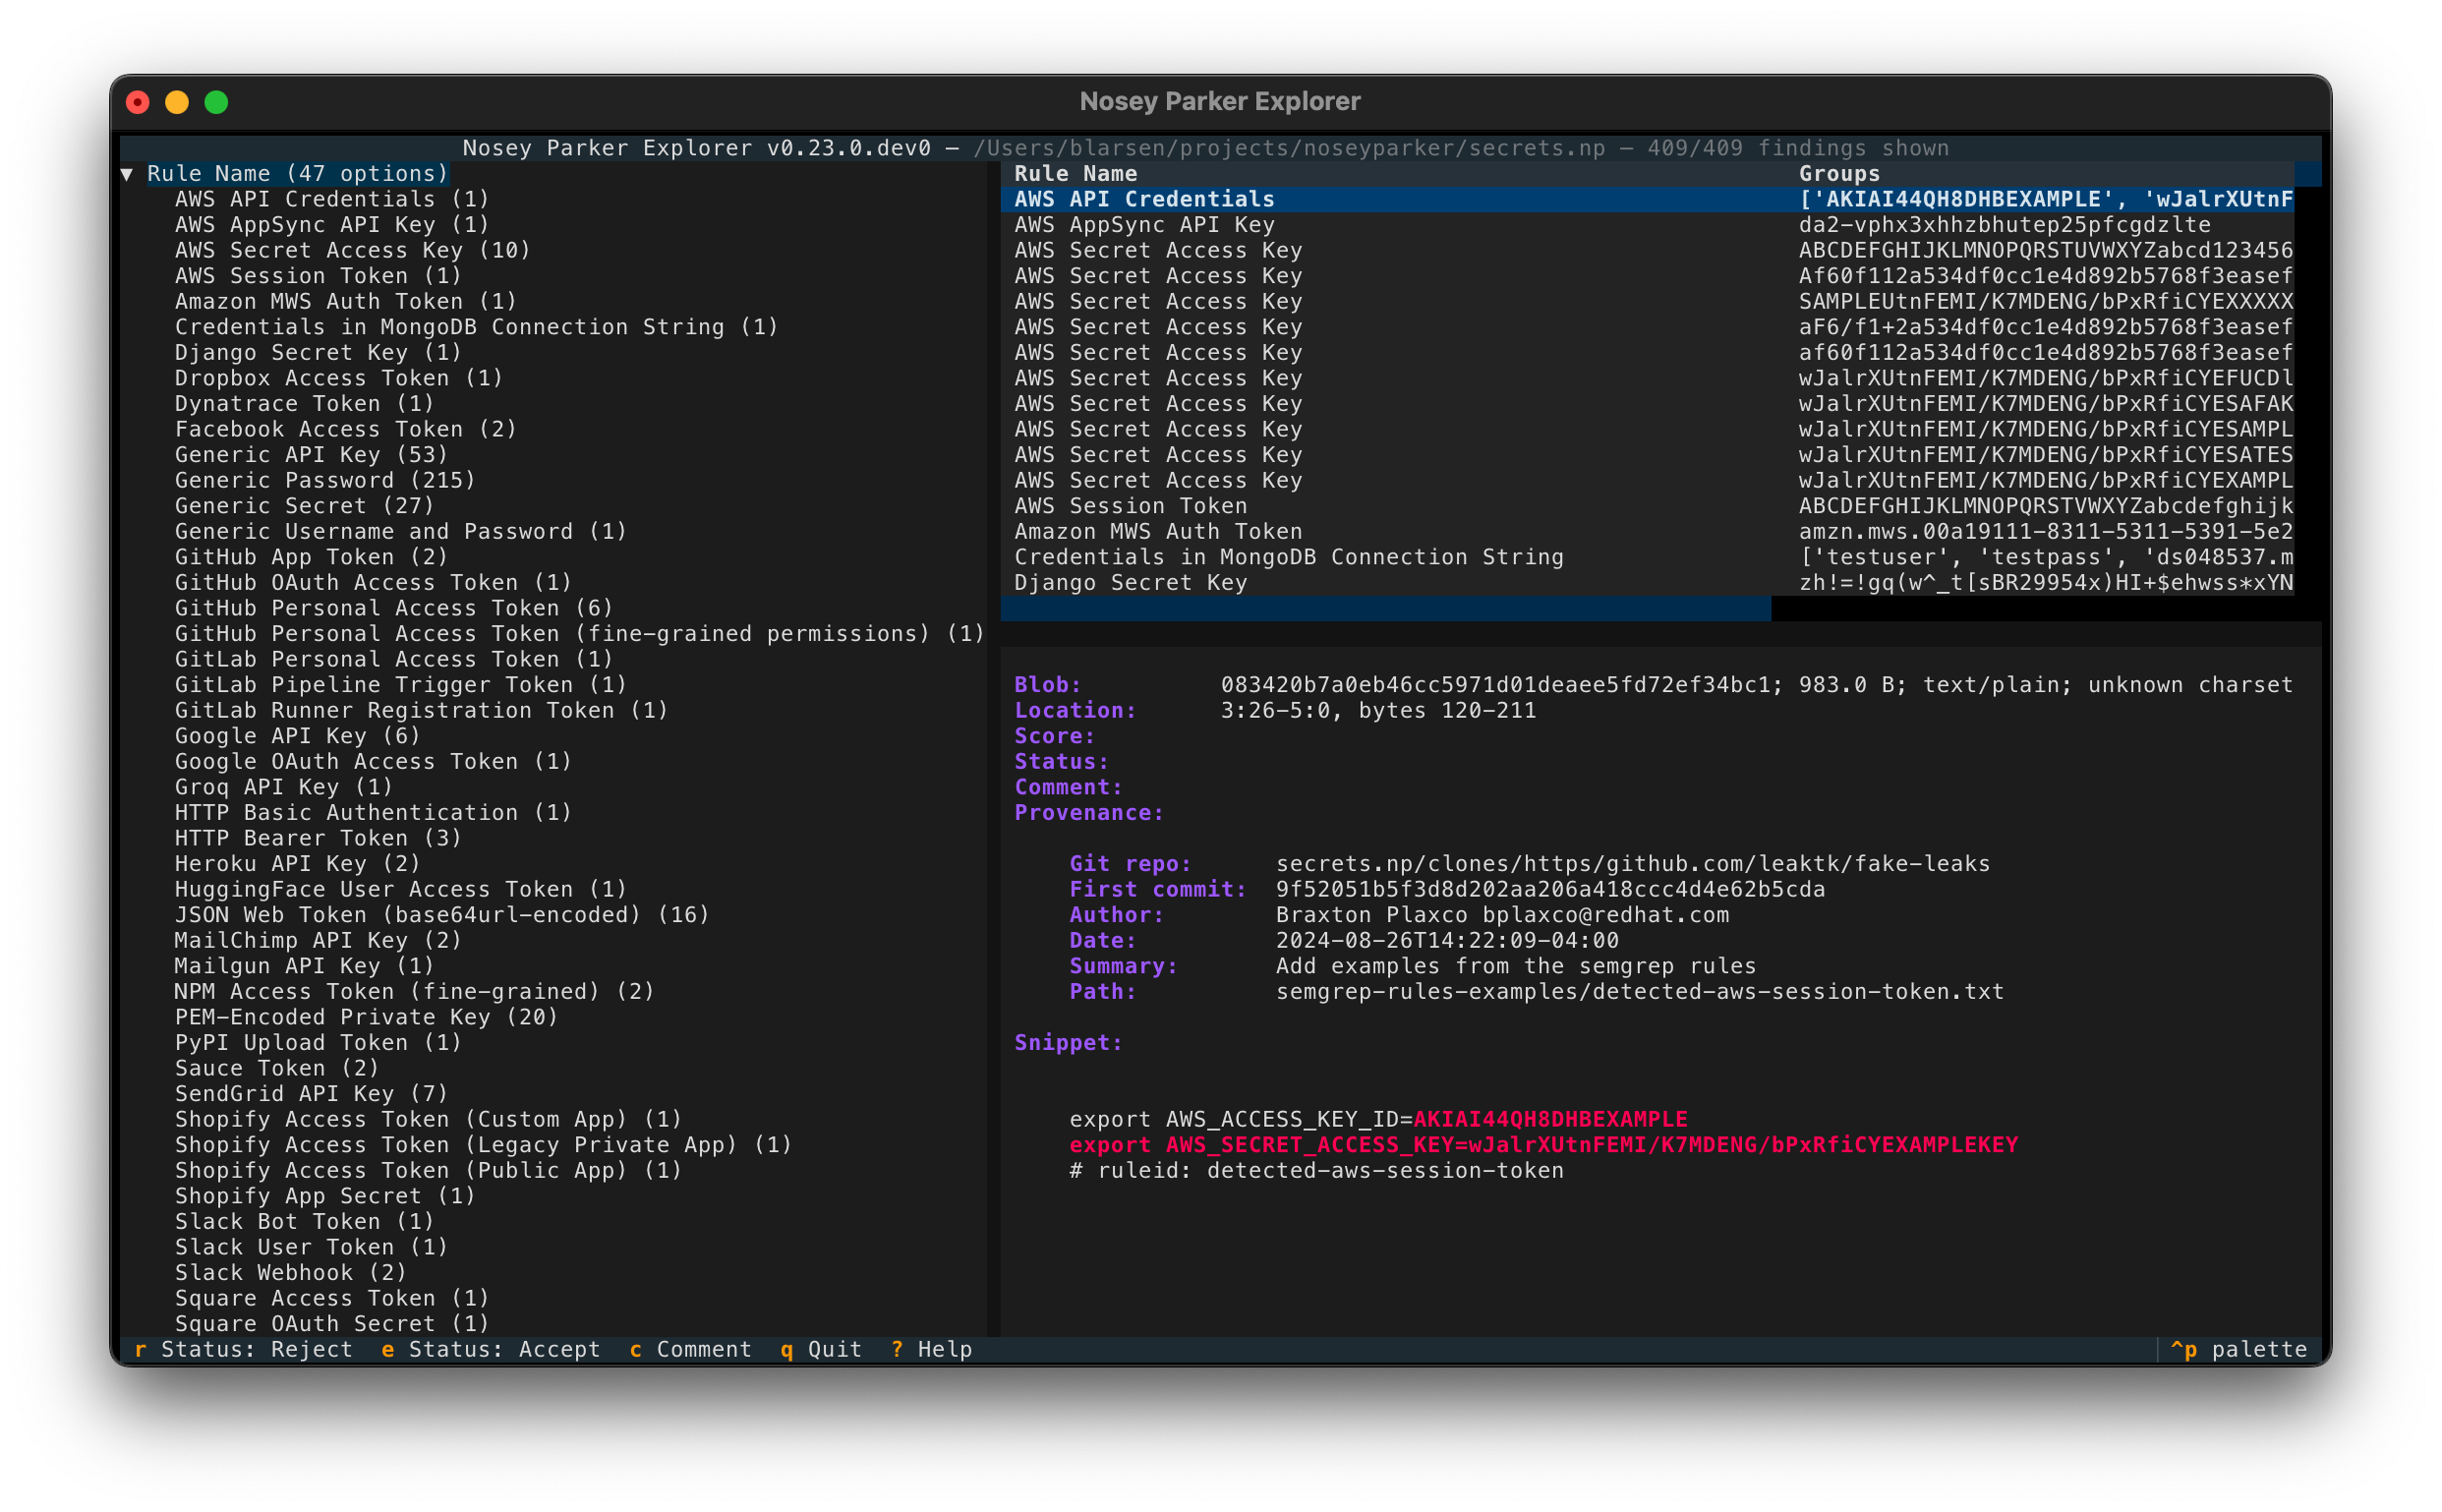 praetorian-inc/noseyparker
Nosey Parker is a command-line tool that finds secrets and sensitive information in textual data and Git history.
 owasp/cheatsheetseries
The OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.
 burrowers/garble
Obfuscates Go builds by wrapping the Go toolchain, replacing identifiers, package paths, and position data with hashes and stripping debug and build…
 dor-tumarkin/cve-2019-17564-fastjson-gadget
Basic code for creating the Alibaba FastJson + Spring gadget chain, as used to exploit Apache Dubbo in CVE-2019-17564 - more information available at…
 ernos/browser-xpi-malware-scanner
A comprehensive browser extension (.xpi) malware scanner which checks for many common malware tricks like:, credential-stealers obfuscation tactics,…
 password123456/py_certificate_extractor
Extracts and exports certificate information from digitally signed PE files using Python and pefile, enabling forensic analysis of code-signing…
 bde574786/sequelize-1day-cve-2023-25813
Proof-of-concept and technical analysis of CVE-2023-25813, a SQL injection vulnerability in Sequelize ORM versions prior to 6.19.1, including…
 unkl4b/gitminer3
Tool for advanced mining for content on Github
 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
 awslabs/git-secrets
Prevents you from committing secrets and credentials into git repositories
 crytic/caracal
Static Analyzer for Starknet smart contracts
 ethiack/cve-2023-29007
Proof-of-concept exploit for CVE-2023-29007, a Git arbitrary configuration injection vulnerability. Demonstrates exploitation via crafted repository…
 airbus-cert/ditto
Obfuscates PowerShell and JavaScript scripts using tree-sitter-based parsing with multiple configurable impostor profiles for stealth, size, and…