
PolinRider
 opensourcemalware/polinrider
Technical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…
code-analysiscurated-resourceseducation+8
opensourcemalware/polinriderTechnical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…
 afine-com/glassworm-hunter
Detects GlassWorm supply chain attack payloads by scanning VS Code extensions, npm/PyPI packages, and git repos for invisible Unicode payloads,…
 byt3bl33d3r/offensivenim
My experiments in weaponizing Nim (https://nim-lang.org/)
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 byt3bl33d3r/offensivedlr
Toolbox containing research notes & PoC code for weaponizing .NET's DLR
 manuelschipper/nah
a guard that blocks catastrophic agent actions
 linuztx/alter-zero
RAM efficient terminal agent harness for coding, cybersecurity, and automation.
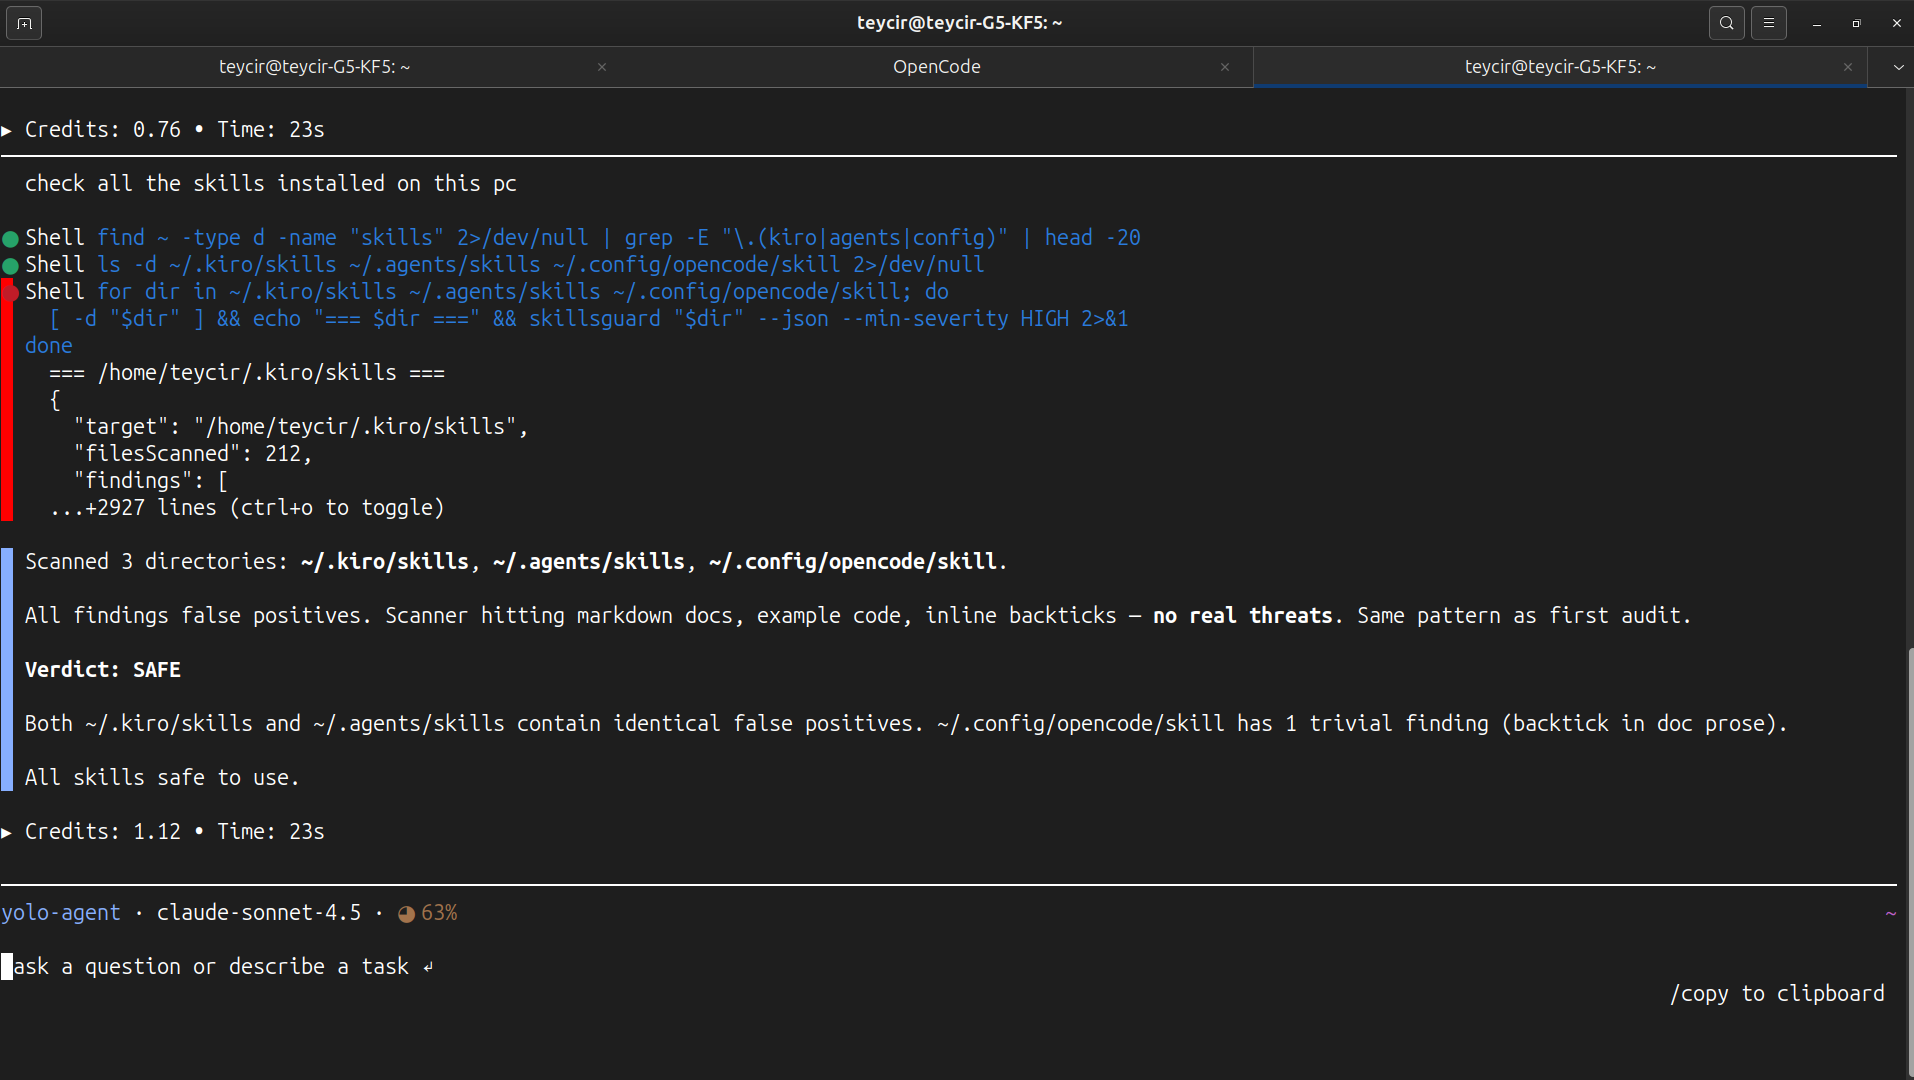 teycir/skillsguard
Static security scanner for AI agent skill packages. Detects malicious SKILL.md files and bundled scripts before they run.
 randomrobbiebf/cve-2024-9593
Time Clock <= 1.2.2 & Time Clock Pro <= 1.1.4 - Unauthenticated (Limited) Remote Code Execution
 zhzyker/cve-2018-7600-drupal-poc-exp
CVE-2018-7600 Drupal Drupalgeddon 2 远程代码执行漏洞利用脚本
 louiselalanne/cve-2023-49314
Proof-of-concept exploit for CVE-2023-49314 demonstrating code injection in Asana Desktop on macOS via Electron Fuses, with automated vulnerability…
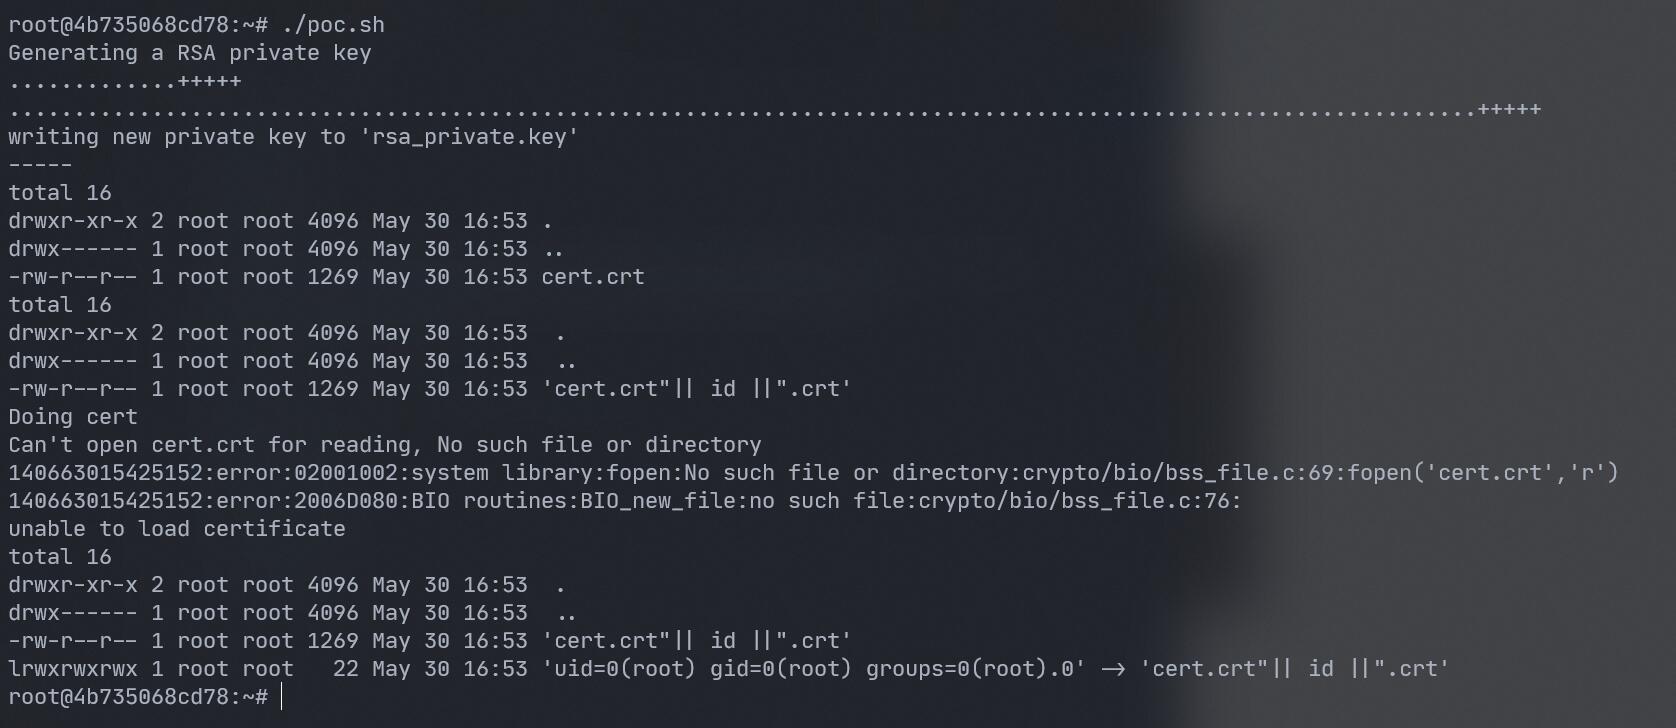 rama291041610/cve-2022-1292
CVE-2022-1292 OpenSSL c_rehash Vulnerability
 mhtsec/cve-2026-84645
Jenkins PersistenceRoot Deserialization RCE (SECURITY-3972) — PoC & analysis. Requires Item/Configure; affects weekly <= 2.579 / LTS <= 2.568.2
 huseyinstif/cve-2025-24016-nuclei-template
Nuclei template to detect CVE-2025-24016 unsafe deserialization RCE in Wazuh servers via a crafted JSON payload that triggers a NameError.
 cerberusmrxi/cve-2026-48909-joomla-sp-exploit
CVE-2026-48909 - Unauthenticated PHP Object Injection to RCE exploit for Joomla SP LMS extension versions <= 4.1.3. Exploits lmsOrders cookie…
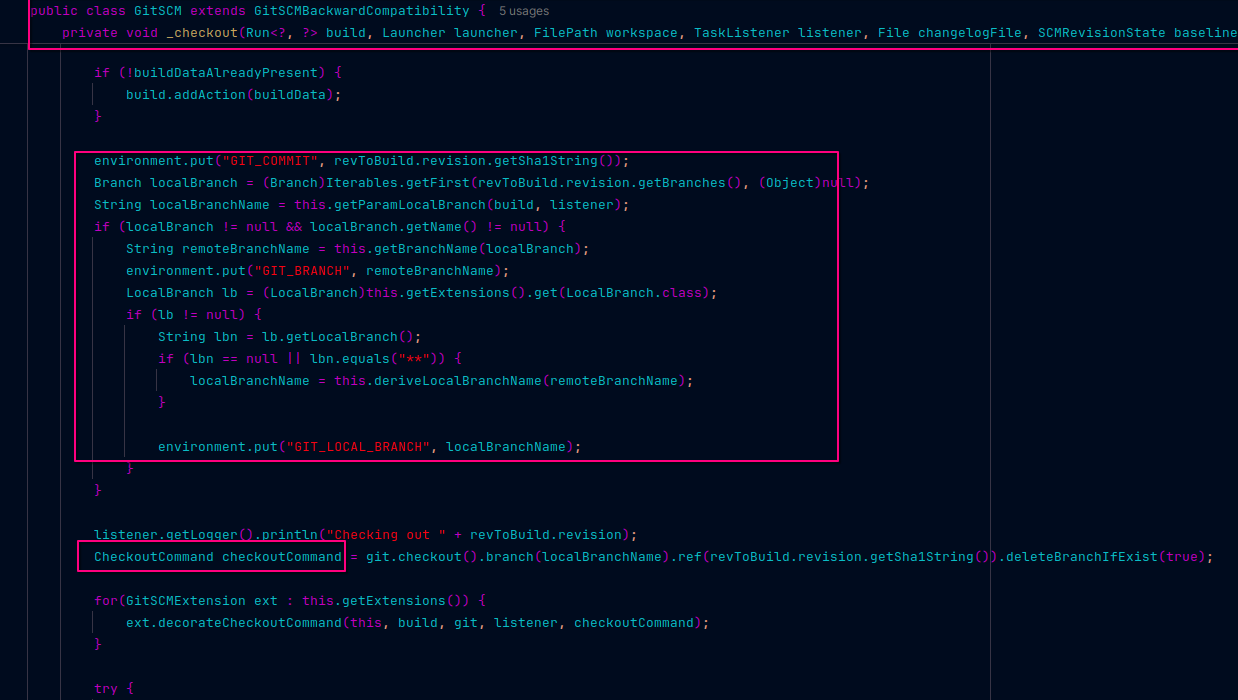 pl4tyz/cve-2025-53652-jenkins-git-parameter-analysis
CVE-2025-53652: Jenkins Git Parameter Analysis
 hnytgl/cve-2026-42588
Python-based RCE exploit for CVE-2026-42588 targeting Apache ActiveMQ Jolokia. Features check-only mode, malicious XML generation, and support for…
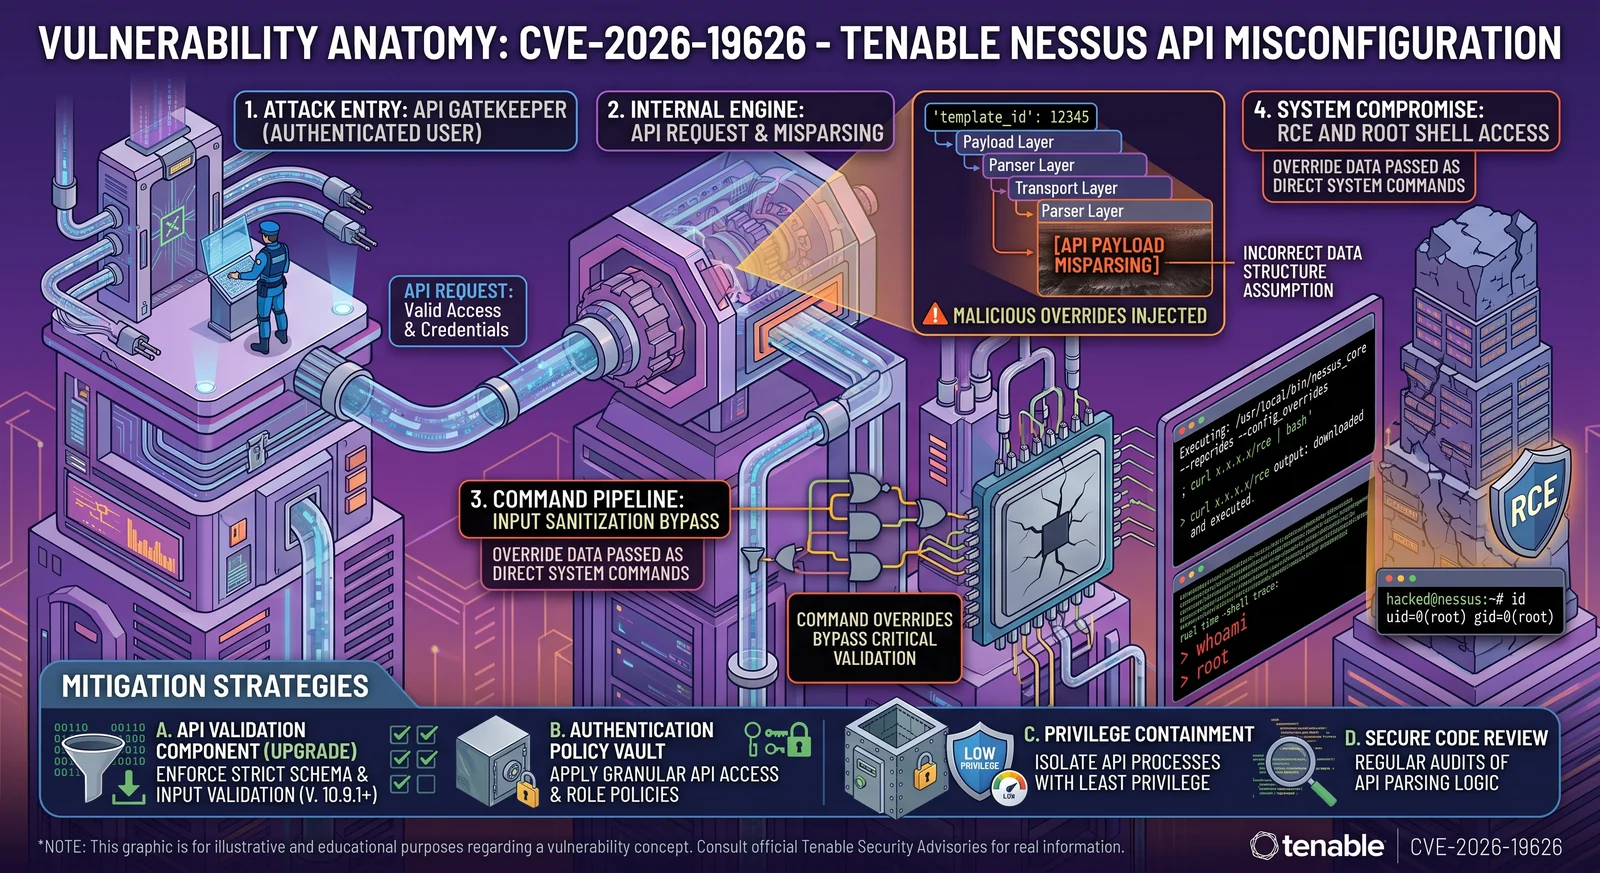 h00die/poc-cve-2026-19626
Proof-of-concept exploit for CVE-2026-19626, an authenticated remote code execution in SecurityCenter report generation, demonstrating a non-admin…