
glasgo
 nccgroup/glasgo
Go static analysis tool that checks for security issues using an AST.
code-analysisstatic-code-analysisvulnerability-analysis
nccgroup/glasgoGo static analysis tool that checks for security issues using an AST.
 otsmane-ahmed/ci-supplychain-guard
Static analysis tool that detects malicious dependencies in CI/CD pipelines using pattern matching and AST analysis, with a traffic-light risk…
 seifreed/yaraast
A powerful Python library and CLI tool for parsing, analyzing, and manipulating YARA rules through Abstract Syntax Tree (AST) representation
 studiomeyer-io/mcp-stdio-shellguard
Defense-in-depth bundle for MCP stdio servers: drop-in guardExec/guardSpawn wrappers, AST audit CLI, reference MCP server. Closes the Ox-Security…
 trailofbits/multiplier
Indexes C/C++ build artifacts into a queryable whole-program database, exposing AST, token, and IR-level APIs for code auditing and vulnerability…
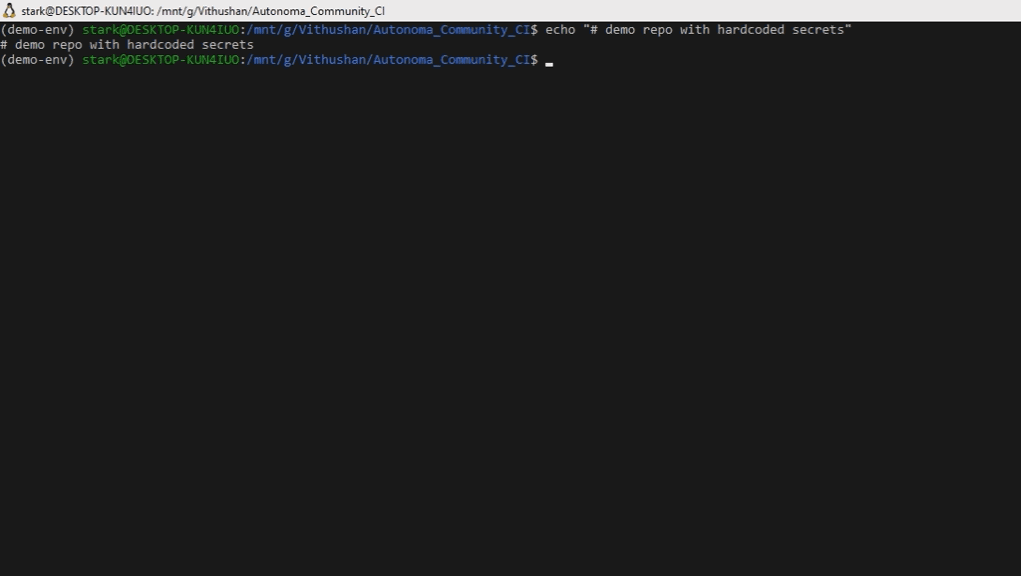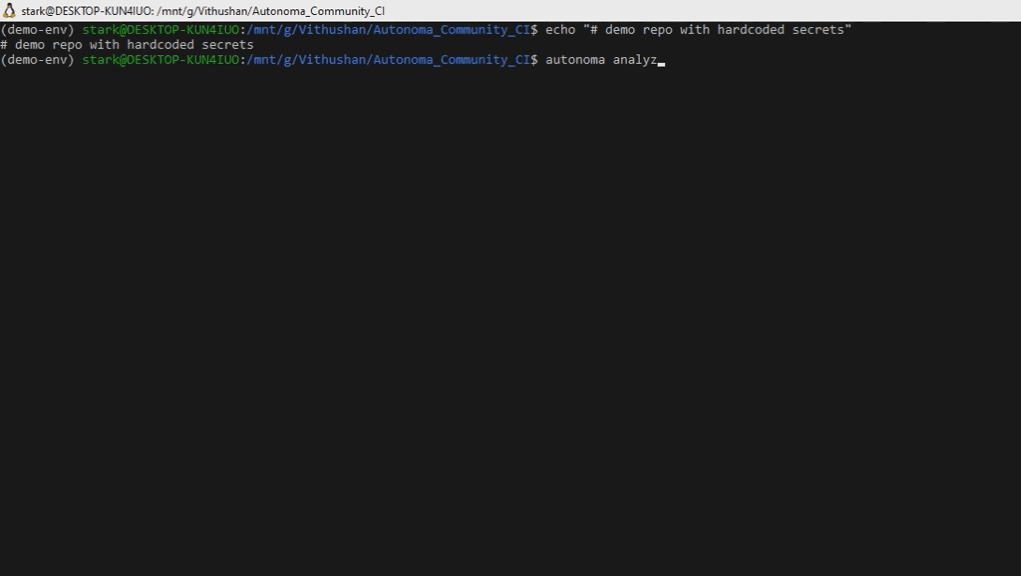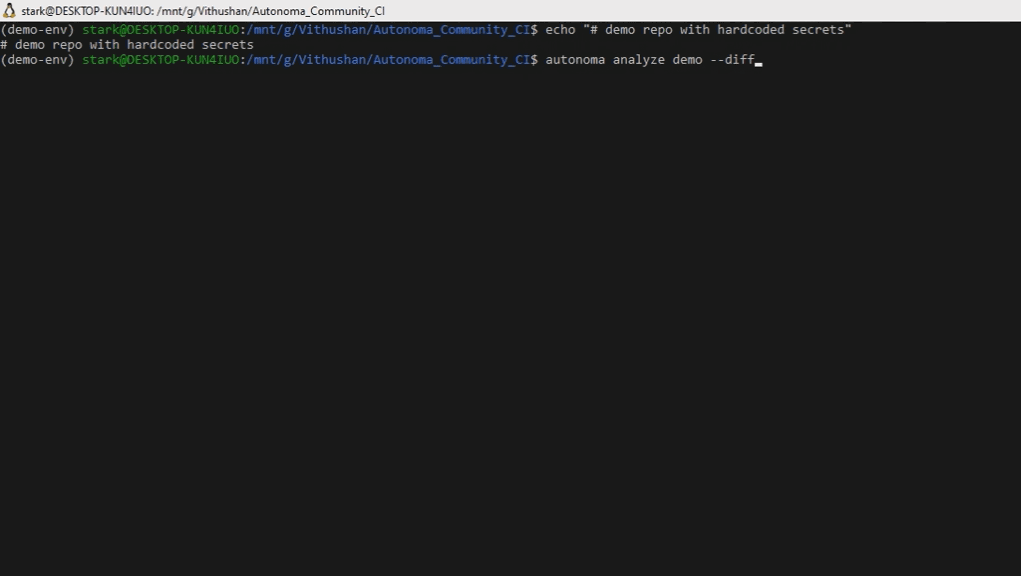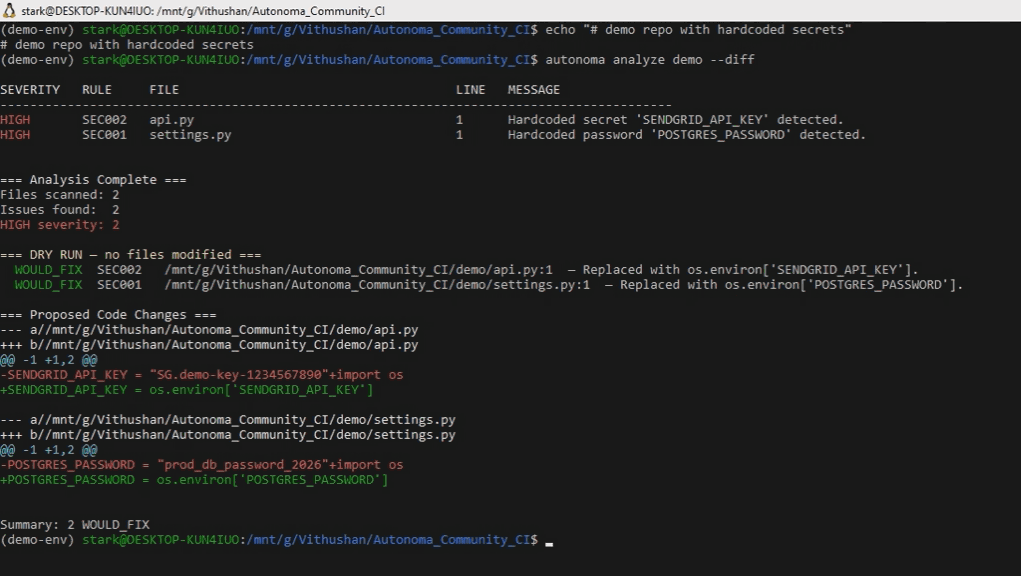 vihaaninnovations/autonoma
Detects and auto-fixes hardcoded secrets in Python repos — refuses when the fix could break your code
 corgea/sighthound
Tree-sitter based static vulnerability scanner with pattern matching and taint-flow analysis for multi-language source code. Outputs findings as…
 dnszlsk/muad-dib
Real-time npm/PyPI supply-chain threat detection. Behavioral chain analysis, AST scanning, IOC feeds, and compound scoring engine.
 raytran54/cve-2018-7600
Step-by-step analysis and exploitation lab for Drupal CVE-2018-7600 remote code execution vulnerability, including debugging, exploit code, and…
 dinhvaren/cve-2026-33937
Proof-of-concept exploit for CVE-2026-33937, a Handlebars AST injection vulnerability leading to remote code execution in Node.js. Demonstrates…
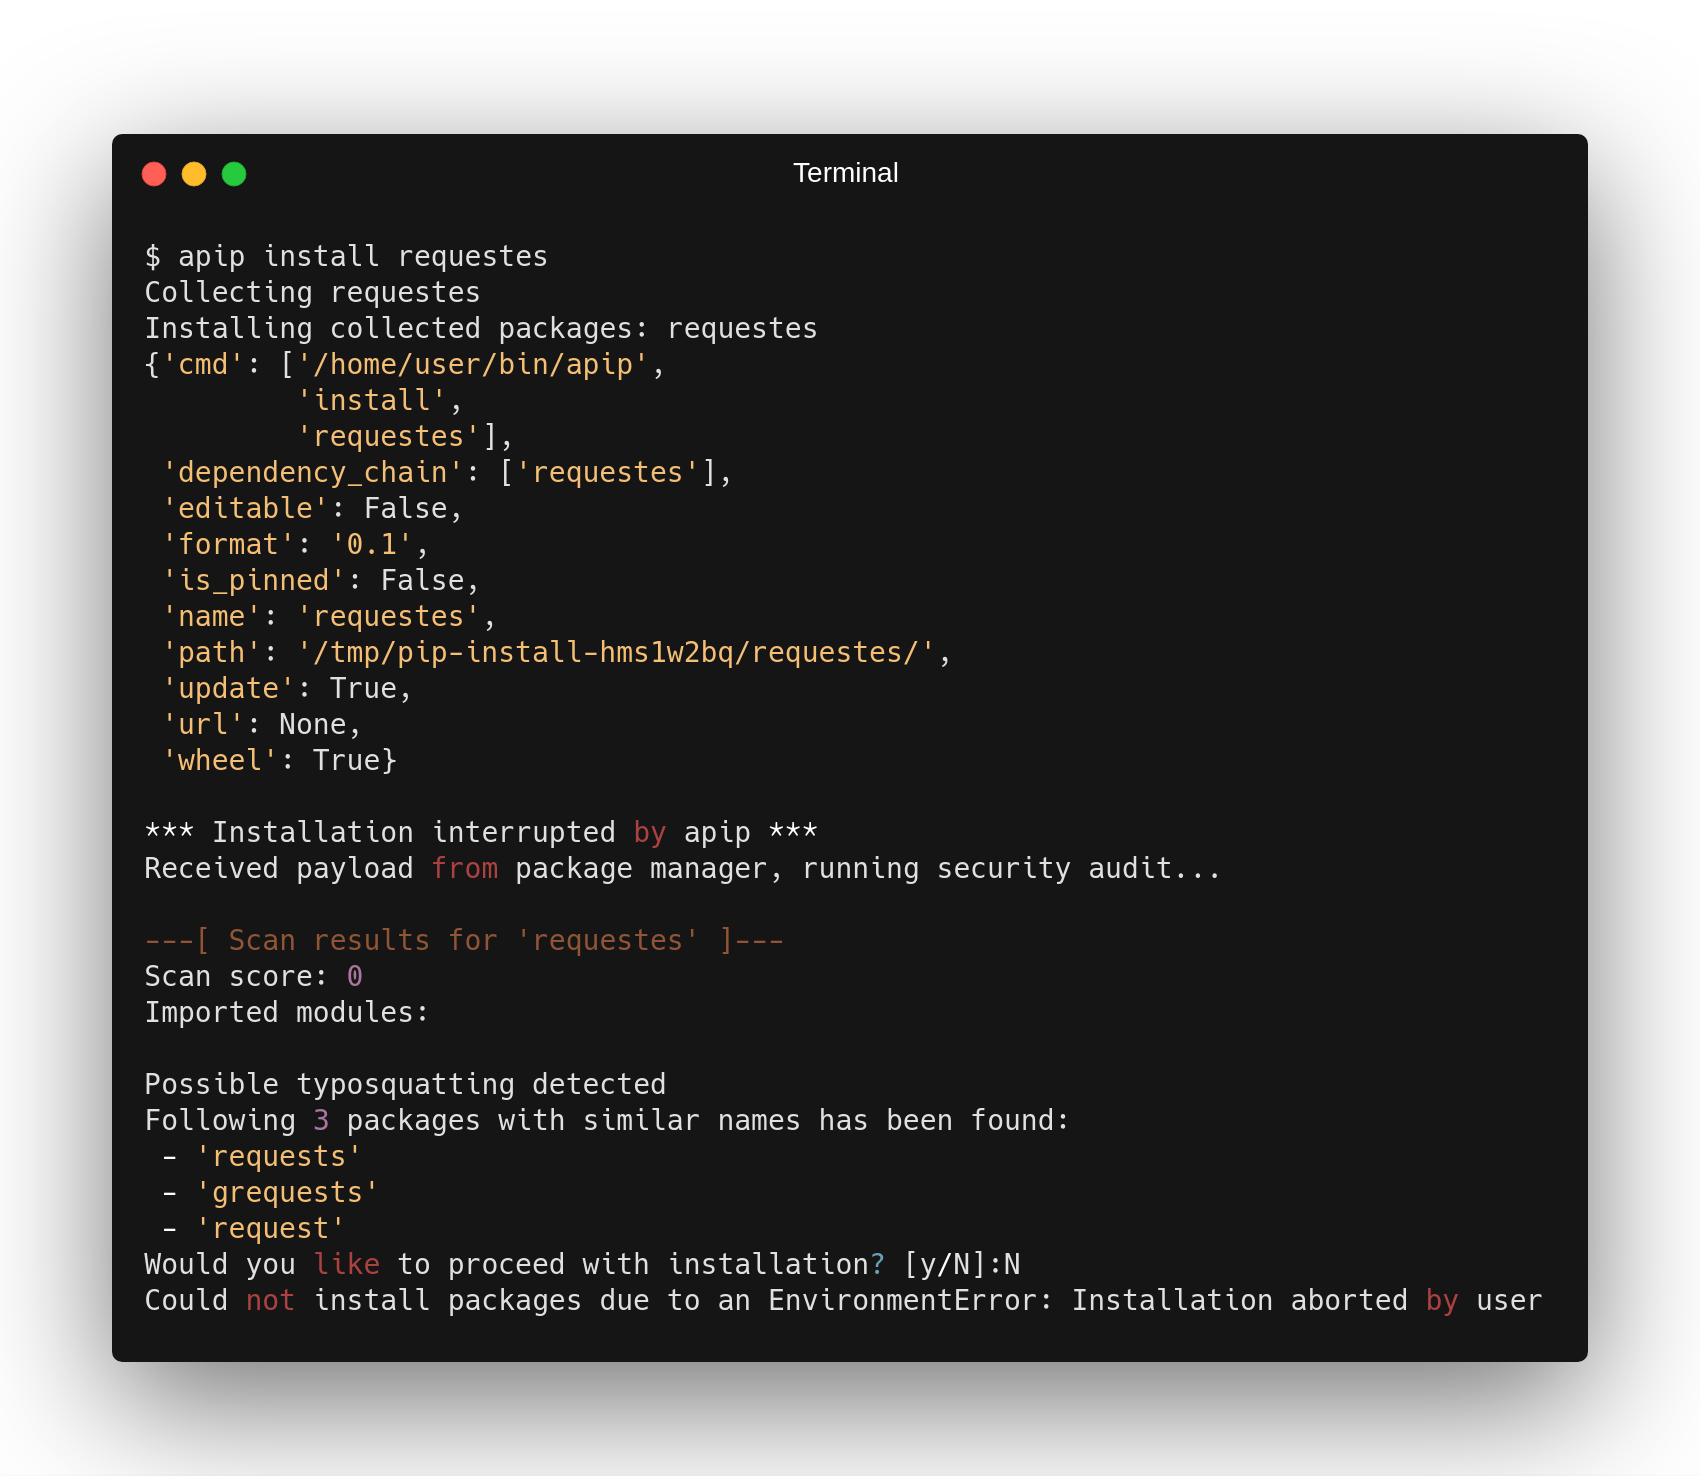 rootlug/aura
Project Aura: Security auditing and code introspection
 nodesecure/js-x-ray
JavaScript & Node.js open-source SAST scanner. A static analyser for detecting most common malicious patterns 🔬.
 0p4n1k/noctyra
AST-based Python code transformation & deobfuscation framework
 oscar-collado/langflow-cve-2026-17633-poc
PoC for CVE-2026-17633 — Authenticated RCE in IBM Langflow OSS 1.0.0–1.10.3 via custom_component endpoint. Includes CVE-2026-17632 AST scanner bypass…
 use-tusk/tusk-cli
Automated testing suite with live traffic record and replay
 owasp/vulnreach
Runtime-aware SCA — proves which CVEs are actually reachable, not just installed.
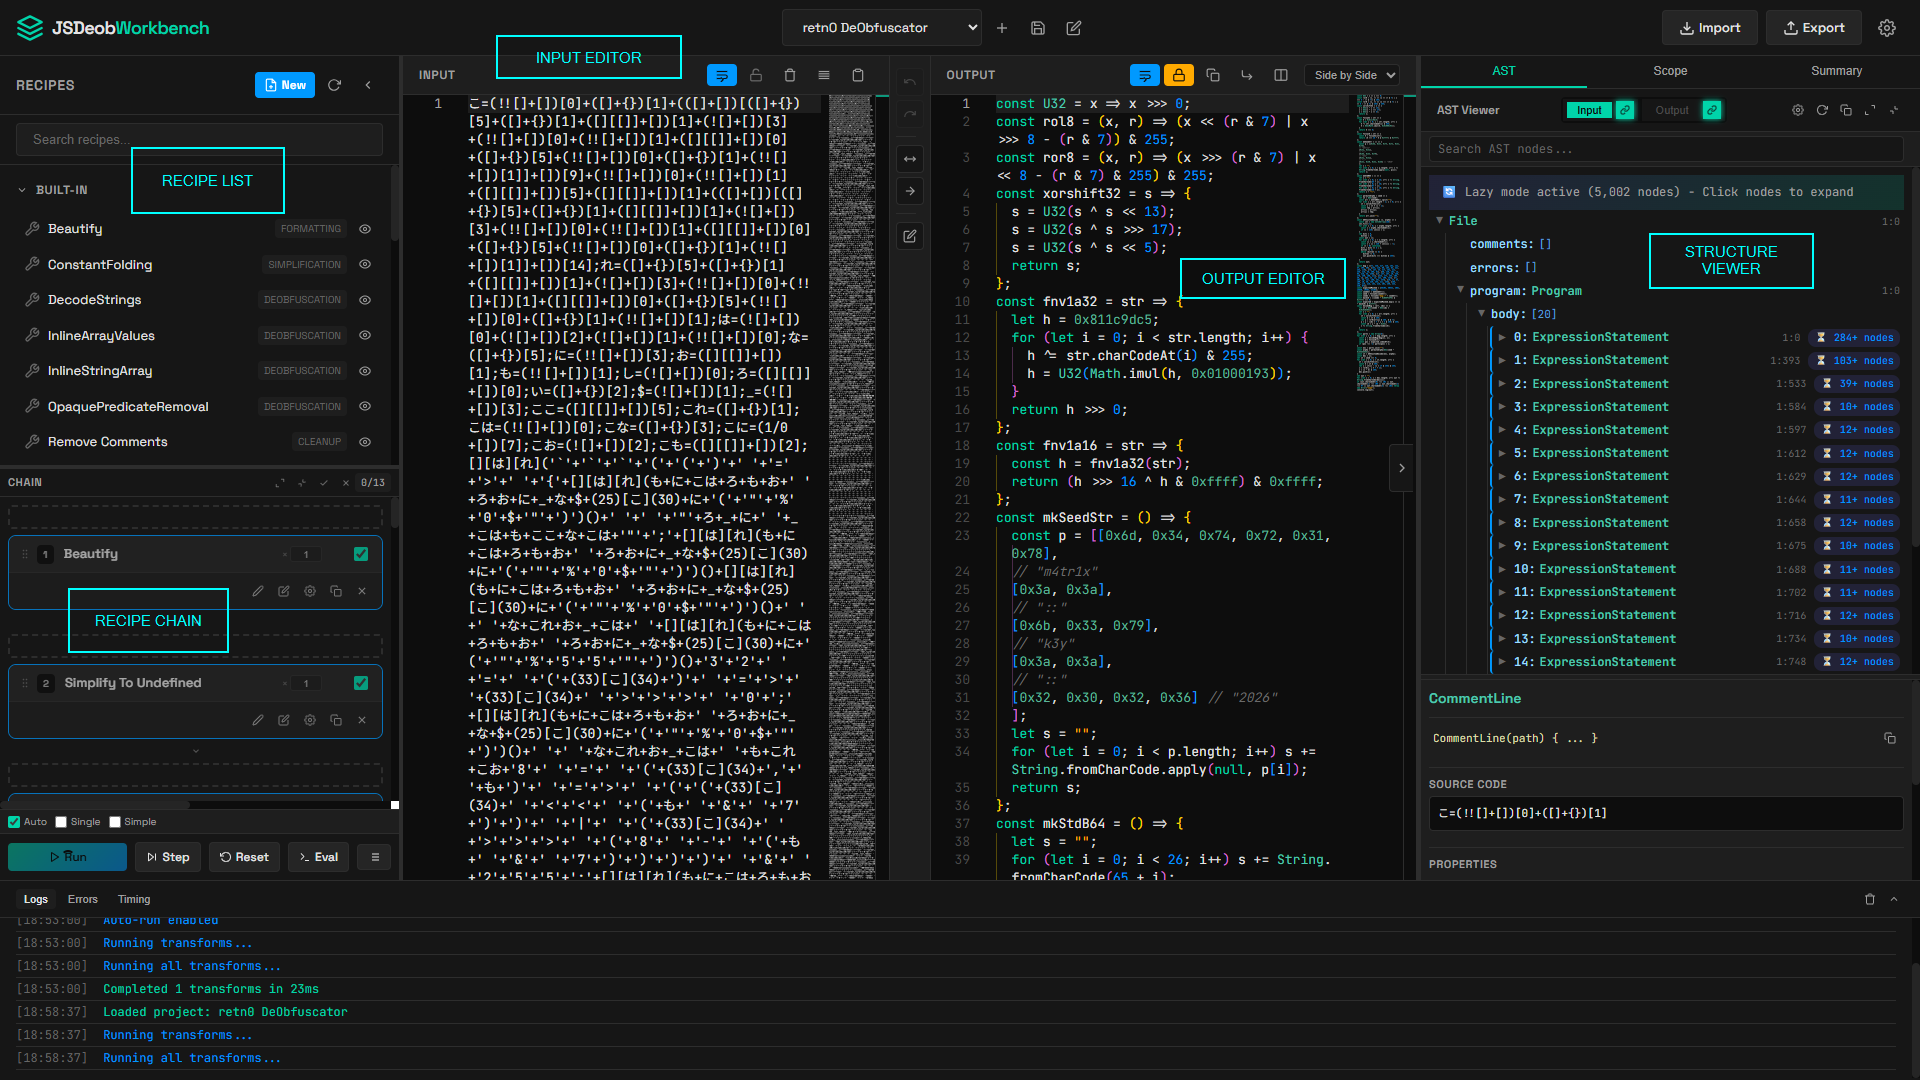 owl4444/jsdeob-workbench
Reverse engineer obfuscated JavaScript visually. Chain transforms, inspect AST changes, write reusable deobfuscation plugins.
 biitts/cve-2026-53753-crawl4ai-rce
CVE-2026-53753 — Crawl4AI <0.8.7 unauthenticated RCE (AST sandbox escape via gi_frame.f_back). Lab + PoC, verified e2e.