
Confluence-CVE-2021-26084
 30579096/confluence-cve-2021-26084
OGNL Injection in Confluence server version < 7.12.5
code-analysisexploitationpenetration-testing+2
30579096/confluence-cve-2021-26084OGNL Injection in Confluence server version < 7.12.5
 rooootdev/cve-2019-5784-poc
a proof of concept for CVE-2019-5784
 shan0ar/cve-2025-32756
Proof-of-concept exploit for CVE-2025-32756, demonstrating the vulnerability and providing a basis for security testing and remediation validation.
 shoucheng3/apache__sling-org-apache-sling-xss_cve-2016-5394_1-0-8
Java library providing XSS escaping and filtering services (XSSAPI, XSSFilter) to sanitize user-submitted content and prevent cross-site scripting…
 r2c-cse/multer-sca-rule-test_cve-2025-7338
Test to validate CVE-2025-7338 https://semgrep.dev/orgs/-/advisories?f=CAAQGRoTCg1jdmUtMjAyNS03MzM4GgAiAA%3D%3D
 shoucheng3/dspace__dspace_cve-2022-31194_5-10
Security patch for DSpace repository software addressing CVE-2022-31194, a vulnerability in the Java-based digital asset management platform.

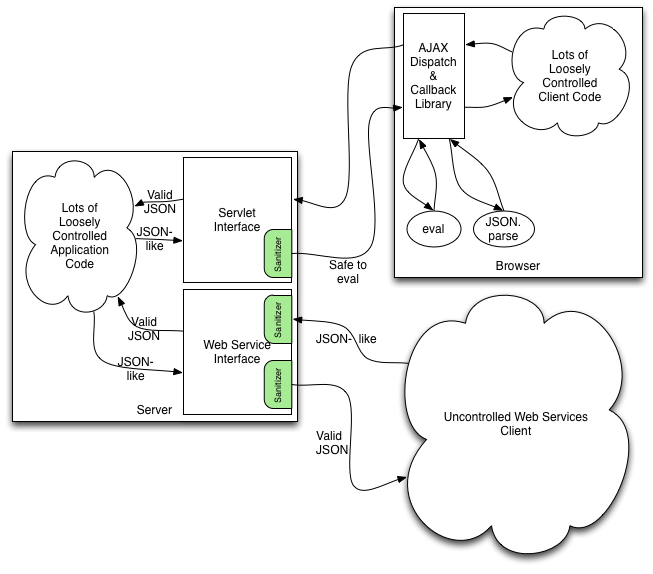 shoucheng3/owasp__json-sanitizer_cve-2020-13973_1-2-0
Java library that converts malformed JSON-like content into standards-compliant, safe JSON, preventing code injection and ensuring embeddability in…
 r3dkn33-zz/cve-2013-0156
Arbitrary deserialization that can be used to trigger SQL injection and even Code execution
 satheesh575555/packages_apps_settings_aosp10_r33_cve-2021-0506
 shoucheng3/dspace__dspace_cve-2022-31195_5-10
Patched version of DSpace repository addressing CVE-2022-31195, providing a secure digital asset management platform with enhanced vulnerability…
 phzietsman/batchoverflow
A fix for the batchOverflow bug https://medium.com/@peckshield/alert-new-batchoverflow-bug-in-multiple-erc20-smart-contracts-cve-2018-10299-511067db65…
 nanopathi/external_expat_aosp10_r33_cve-2022-22822tocve-2022-22827
Patched version of the Expat XML parser library addressing multiple CVEs (CVE-2022-22822 through CVE-2022-22827) for AOSP 10 r33, providing…
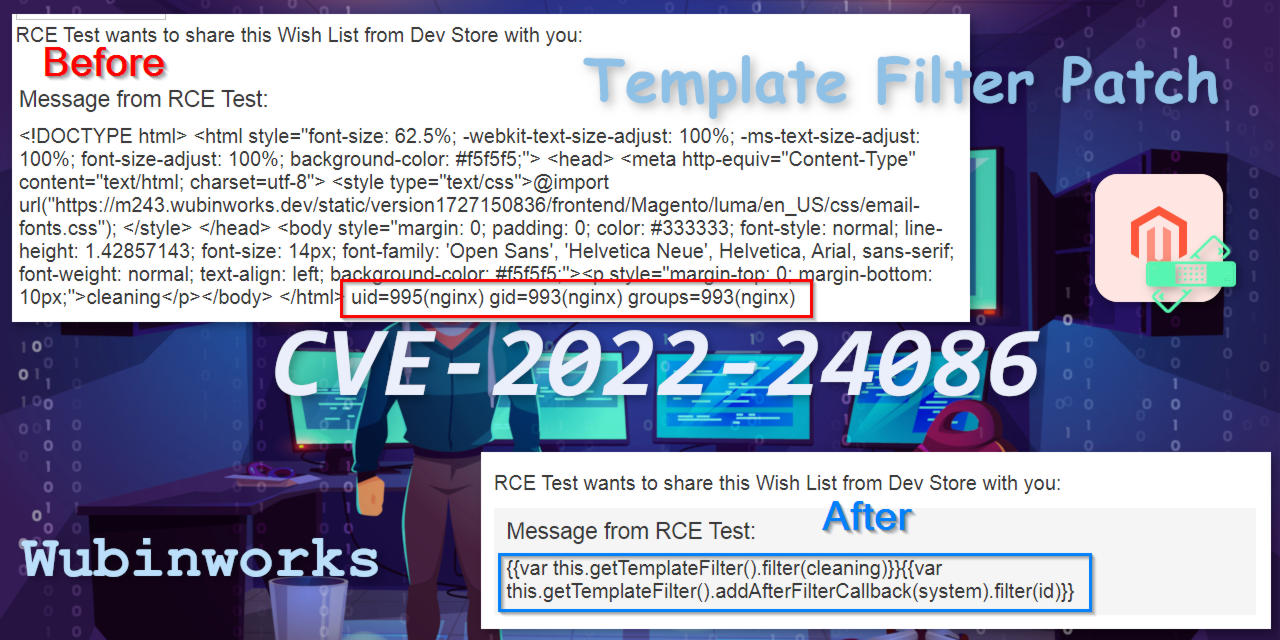 wubinworks/magento2-template-filter-patch
Magento 2 patch for CVE-2022-24086, CVE-2022-24087. Fix the RCE vulnerability and related bugs by performing deep template variable escaping. If you…
 arsalanraja987/gradle-cve-2021-29427-demo
gradle cve
 shoucheng3/asf__tapestry-5_cve-2019-0207_5-4-4
Proof-of-concept exploit for CVE-2019-0207 in Apache Tapestry 5.4.4, demonstrating remote code execution via deserialization vulnerability.
 q1uf3ng/cve-2025-51458-exp
CVE-2025-51458 - DB-GPT Pre-Auth SQL Injection PoC