

CVE-2019-11043
 ianxtianxt/cve-2019-11043
Remote code execution exploit for CVE-2019-11043 targeting Nginx with php-fpm. Includes Go and pre-compiled exploit binaries for testing vulnerable…
code-analysisexploitationpayload-generation+3
ianxtianxt/cve-2019-11043Remote code execution exploit for CVE-2019-11043 targeting Nginx with php-fpm. Includes Go and pre-compiled exploit binaries for testing vulnerable…
 w2xim3/cve-2023-6933
Introduction to CVE-2023-6933 Vulnerability
 subc0ol/cve-2015-0235
Ruby-based exploit for CVE-2015-0235 (Ghost) targeting glibc gethostbyname buffer overflow for remote code execution on vulnerable systems.
 rxerium/cve-2025-4427-cve-2025-4428
Detection for CVE-2025-4427 and CVE-2025-4428
 shoucheng3/esapi__esapi-java-legacy_cve-2022-24891_2-2-3-1
OWASP Enterprise Security API library providing security controls for Java web applications, including authentication, access control, input…
 nayankadamm/cve-2022-24434_poc
Proof-of-concept exploit for CVE-2022-24434 targeting the Dicer npm package v0.3.1. Demonstrates server-side vulnerability exploitation with a…
 shoucheng3/nahsra__antisamy_cve-2016-10006_1-5-3
Fast, configurable HTML sanitization library for preventing XSS and malicious code injection from untrusted user input. Provides a policy-driven API…
 kaylertee/computer-security-equifax-2017
A hands-on simulation of CVE-2017-5638 (Apache Struts2 RCE), showcasing exploit reproduction, OS-level command execution, and mitigations such as…
 r00t4dm/jenkins-cve-2015-8103
Exploit for Jenkins CVE-2015-8103, a remote code execution vulnerability in the Jenkins CLI. Enables authenticated attackers to execute arbitrary…
 uriyahav/tough-cookie-2.5.0-cve-2023-26136-fix
ecurity patch for CVE-2023-26136 in tough-cookie 2.5.0 - Prototype pollution vulnerability fix with backward compatibility
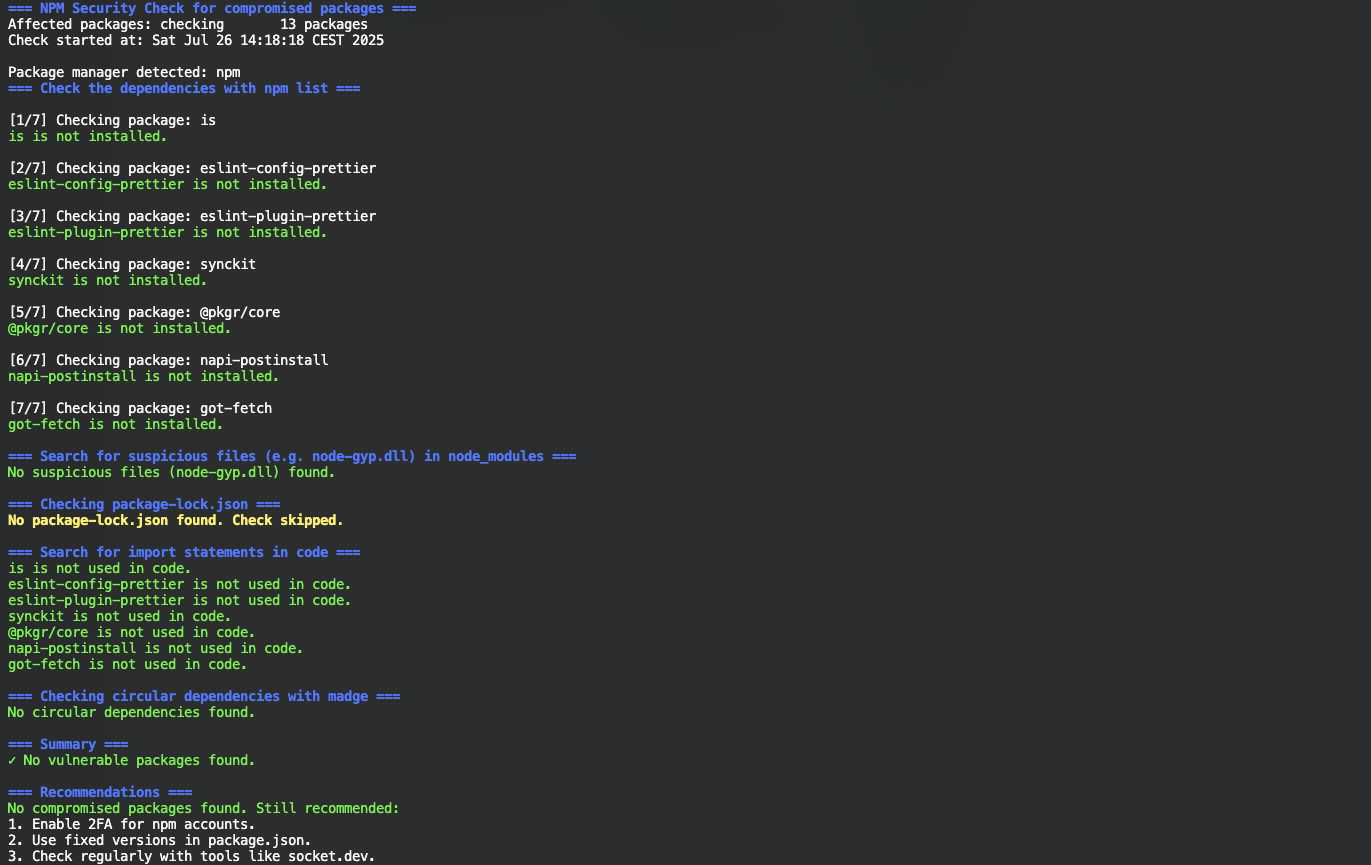 nihilor/cve-2025-54313
Checks projects for compromised packages, suspicious files, and import statements.
 s0/rsyslog-librelp-cve-2018-1000140-fixed
Patch for CVE-2018-1000140 in rsyslog's librelp library, fixing a remote code execution vulnerability in the reliable event logging protocol…
 iris-sast/zip4j
CWE-Bench-Java CVE-2018-1002202 versions 1.3.2, 1.3.3
 pierdipi/unicode-control-characters-action
A GitHub Action to find Unicode control characters using the Red Hat diagnostic tool https://access.redhat.com/security/vulnerabilities/RHSB-2021-007…
 gmh5225/malicious-code-detection-bugu
AI-based malicious code detection and obfuscation system with microservices for detection, packing, and code confusion, plus user and admin services.
 njawalkar/apache-commons-lang2
Apache's commons-lang2 v2.6 with a backported fix for CVE-2025-48924
 f41k0n/rce-nodejs
Exploit Title: Node.JS - 'node-serialize' Remote Code Execution (2), Version: 0.0.4, CVE: CVE-2017-5941
 lirantal/cve-2024-21533-poc-ggit
Proof-of-concept exploit for CVE-2024-21533, an argument injection vulnerability in the ggit npm package that allows arbitrary command execution via…