evmbench-certora-agent-harness

Iterative agent harness that uses LLMs and Certora Prover to generate and refine smart-contract CVL specs, feeding verifier output back until success…

Iterative agent harness that uses LLMs and Certora Prover to generate and refine smart-contract CVL specs, feeding verifier output back until success…

Proof-of-concept exploit for CVE-2025-51482, demonstrating remote code execution via unsafe exec() usage and sandbox bypass in the Letta AI agent…

CAWODOG is a proof-of-concept project demonstrating how to protect Python-based AI models deployed on offline industrial machines. Across three…

Proof-of-concept for CVE-2025-60787, demonstrating remote code execution in MotionEye <= 0.43.1b4 via client-side validation bypass and command…

AI-based malicious code detection and obfuscation system with microservices for detection, packing, and code confusion, plus user and admin services.

Langflow versions prior to 1.3.0 are susceptible to code injection in the /api/v1/validate/code endpoint. A remote and unauthenticated attacker can…

Anticipator is an open-source threat detection platform for multi-agent AI systems.

AI Code Security — four agents that catch what SAST misses in AI-generated code. Built on GitLab Duo Agent Platform.

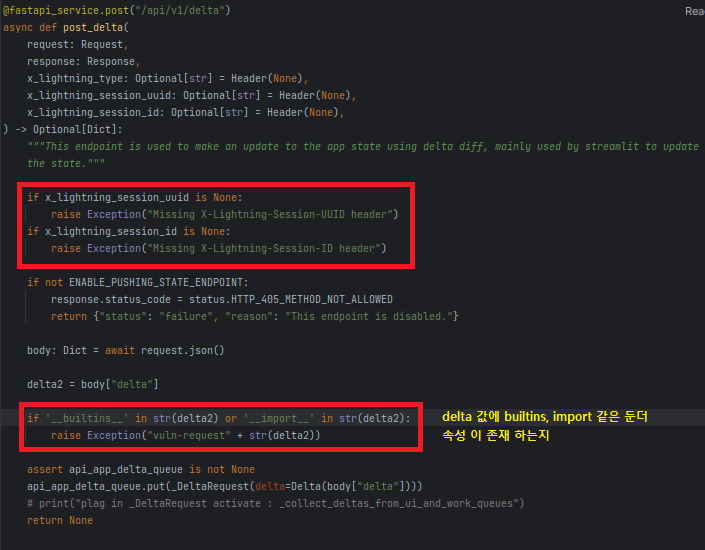
Detailed technical analysis of CVE-2024-5452, a remote code execution vulnerability in PyTorch Lightning via DeepDiff delta property pollution, with…

Exploit for Apache Struts CVE-2017-9805, a remote code execution vulnerability in the REST plugin. Enables penetration testing and security…

Proof-of-concept exploit for CVE-2020-0601 (CurveBall) demonstrating ECC certificate validation bypass to spoof trusted CA and sign arbitrary…

Proof-of-concept exploit for CVE-2024-0195, a critical code injection vulnerability in SpiderFlow 0.4.3 enabling remote code execution via the…

The Security Toolkit for LLM Interactions

High-performance open-source security scanner combining SAST, SCA, Secret Detection, and IaC analysis, built for developers and CI/CD pipelines,…

Public vulnerability advisories with root-cause write-ups and reproducible PoCs for coordinated-disclosure findings in Psono Server and Microsoft…

Scans WordPress plugins for missing-guard vulnerabilities using ripgrep signatures, Semgrep rules, attack-surface mapping, and an LLM review cascade…